

bifrost
 bifrost-proxy/bifrost
High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
api-security-testingnetwork-securitypacket-sniffing-analysis+6
166
bifrost-proxy/bifrostHigh-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
 d4vinci/scrapling
Adaptive web scraping framework with anti-bot bypass, automatic element relocation, concurrent crawling, proxy rotation, and browser automation for…
 zaproxy/zap-hud
The ZAP Heads Up Display (HUD)
 hxsecurity/dongtai
Open-source Interactive Application Security Testing (IAST) tool that passively instruments Java applications to detect vulnerabilities and…
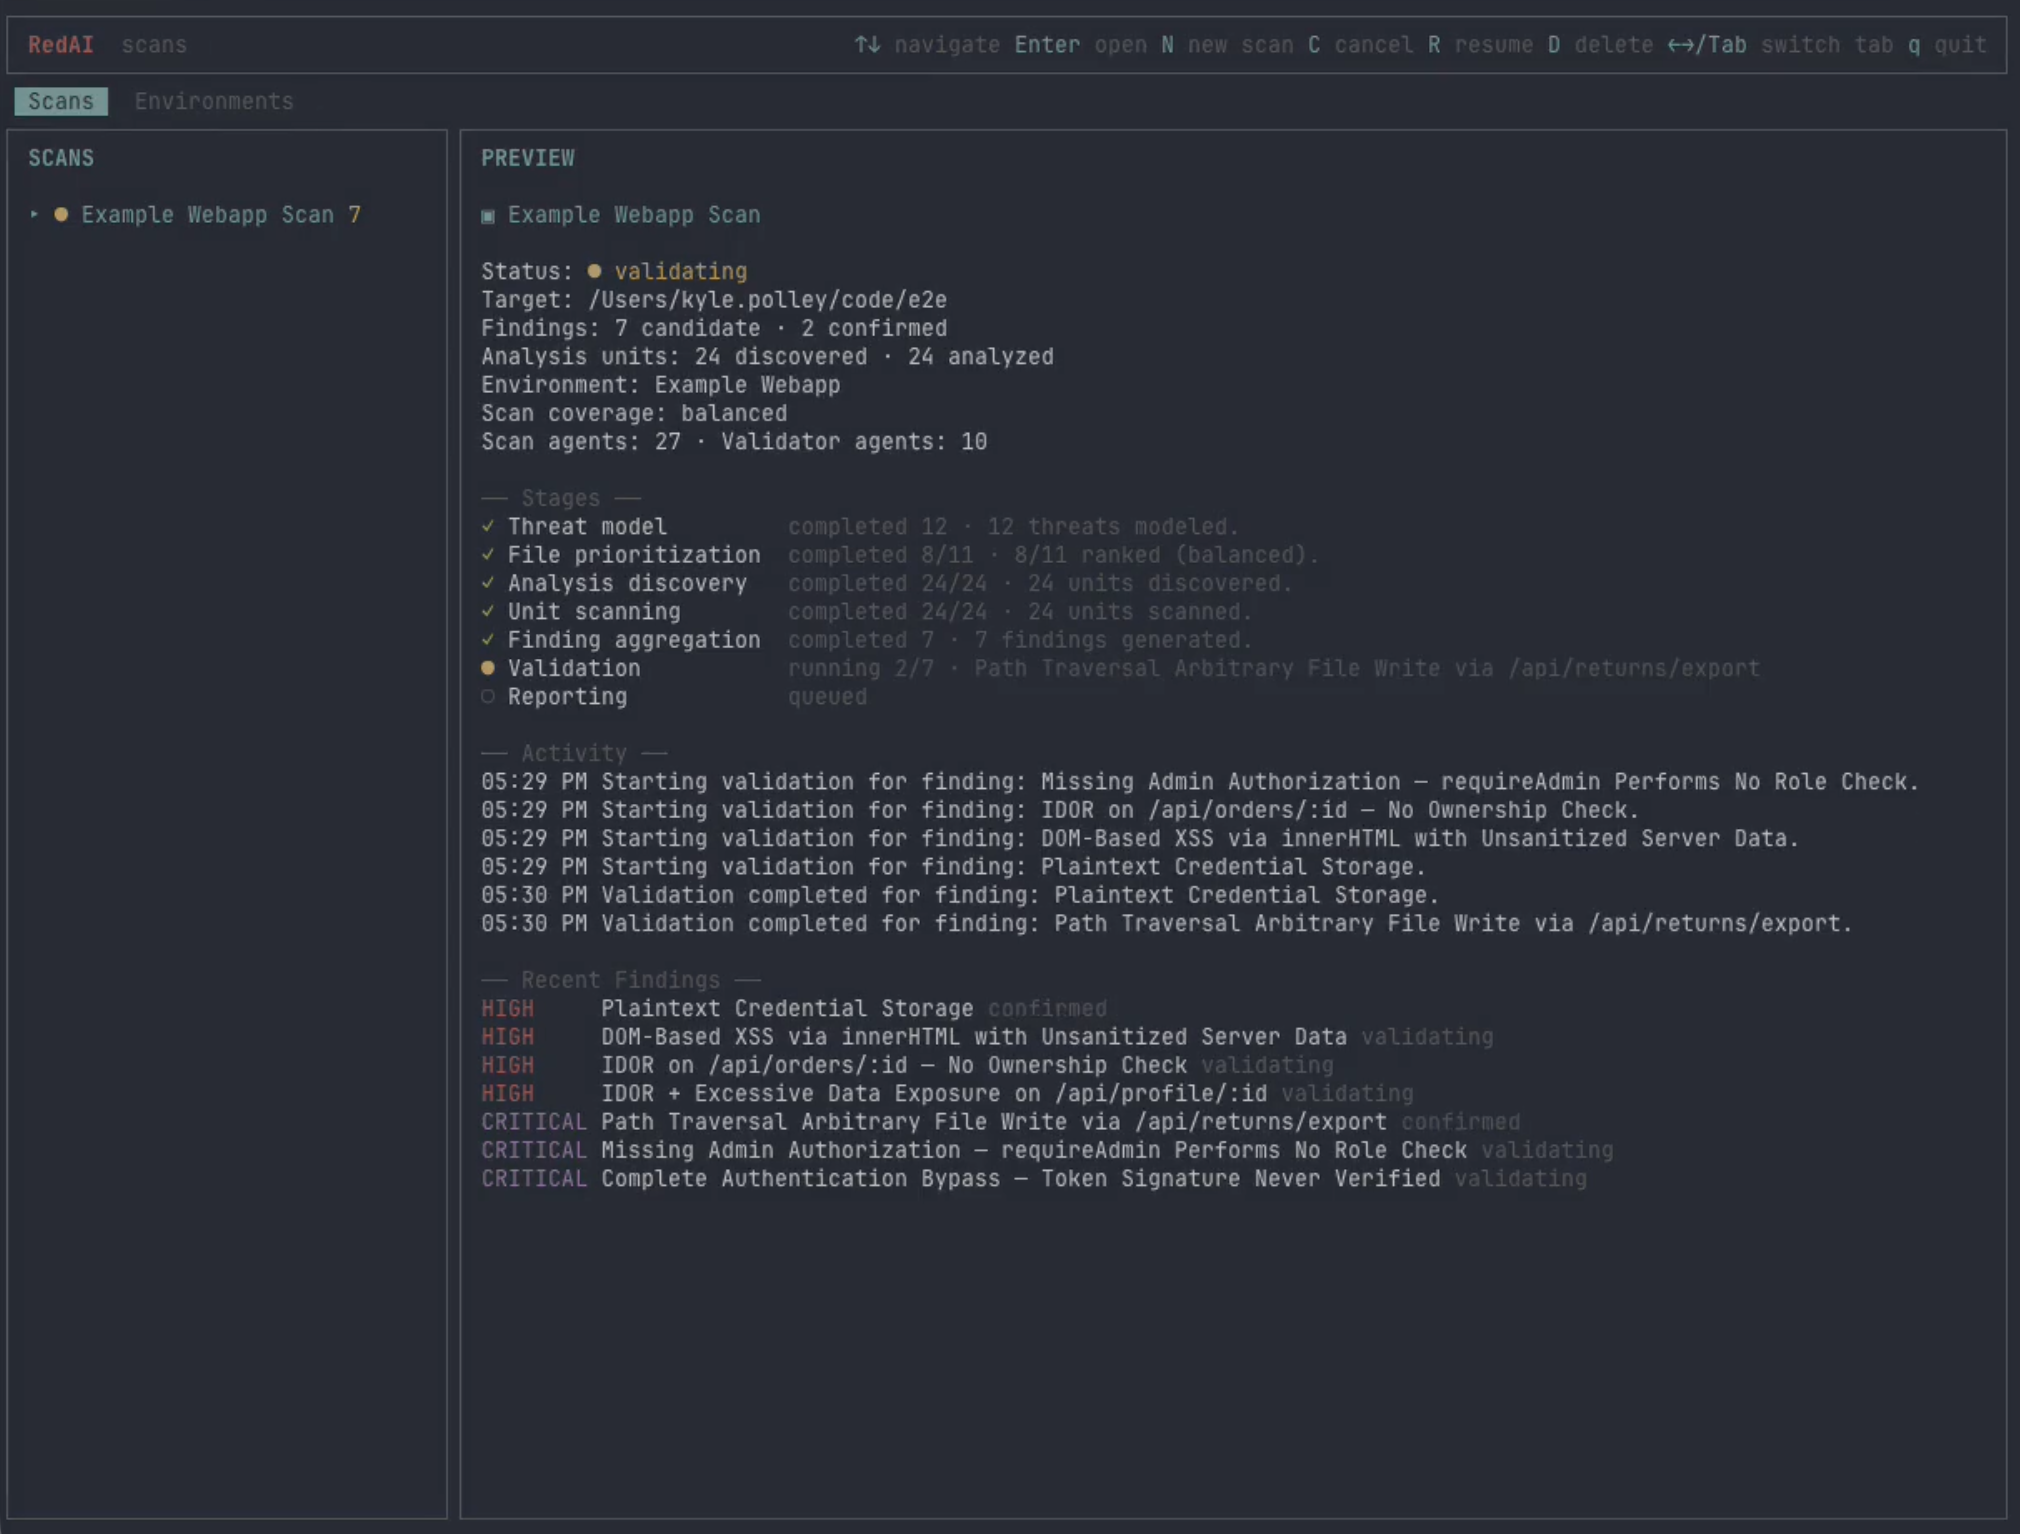 kpolley/redai
AI-driven vulnerability discovery and live validation
 xalgord/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
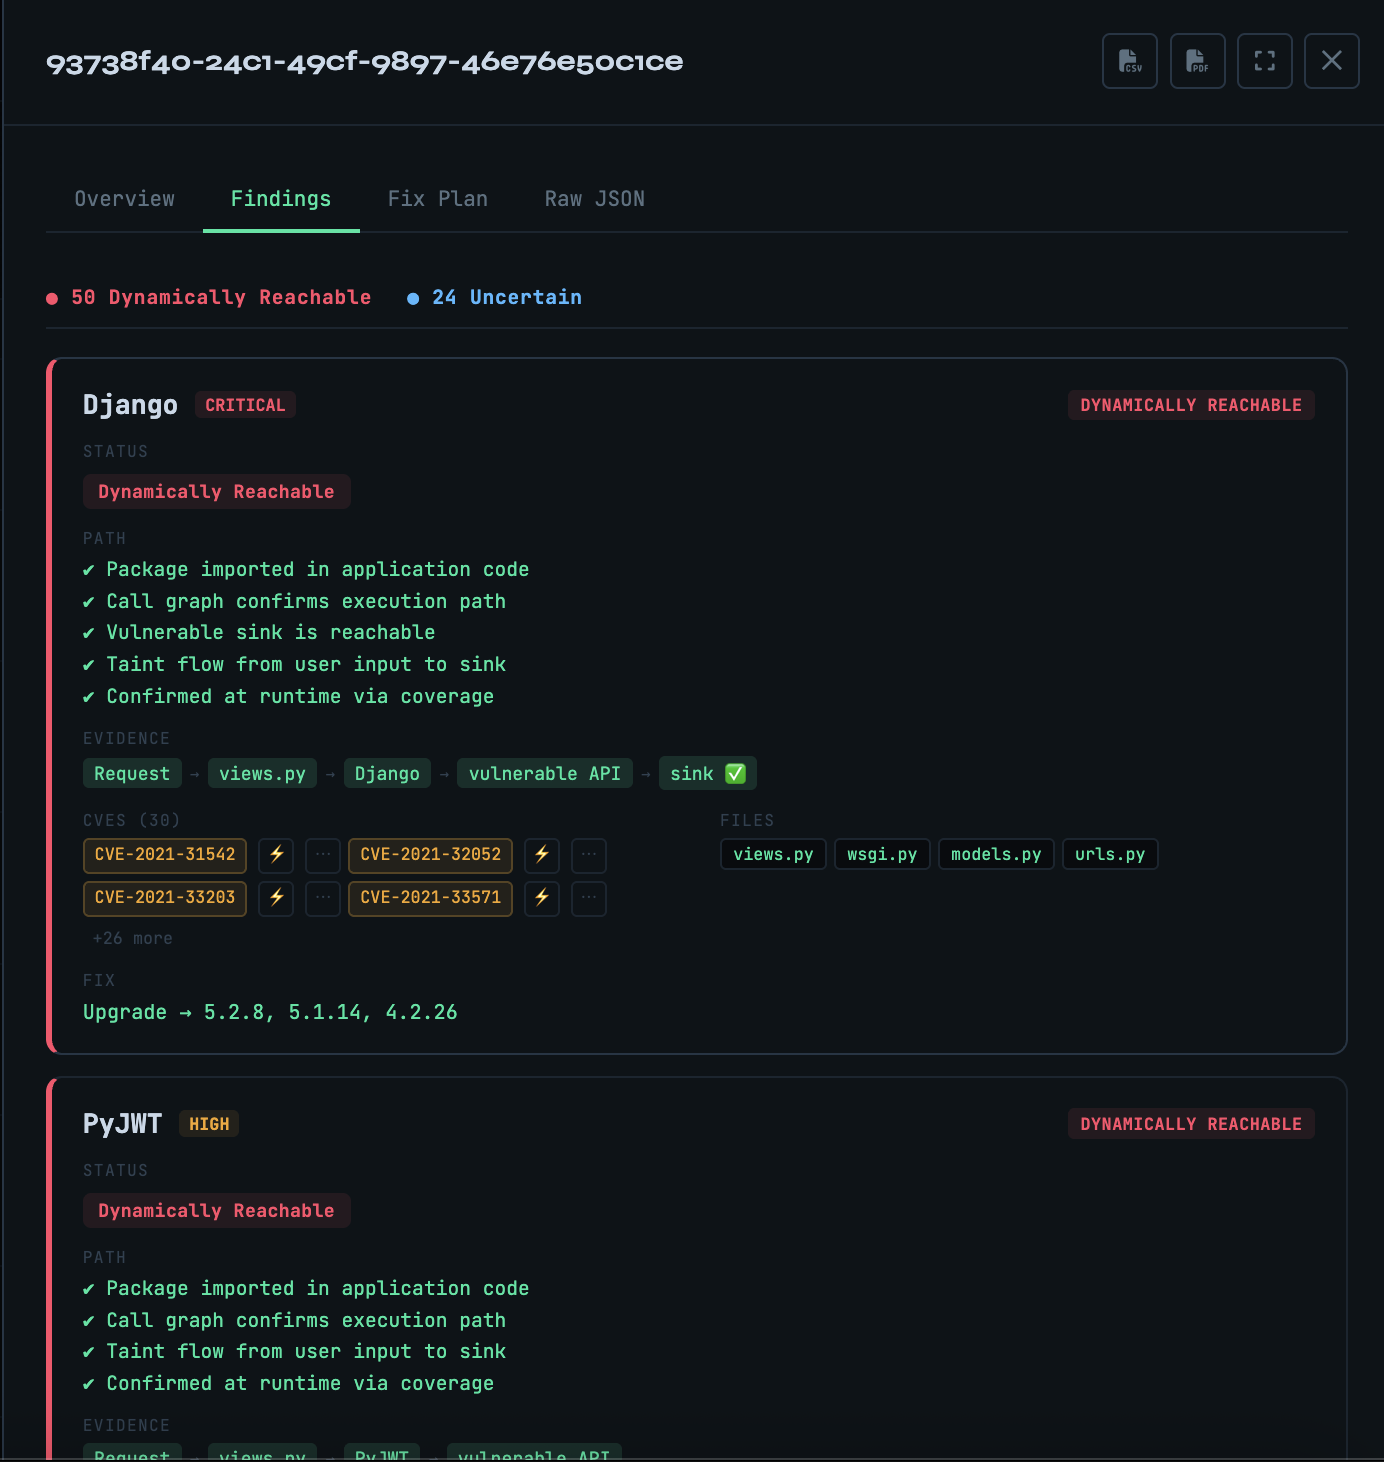 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
 sneakynachos/cve-2026-2796-escape-wasm-by-using-wasm
PoC exploit chain for CVE-2026-2796: SpiderMonkey WebAssembly sandbox escape (signature type confusion -> arbitrary R/W -> RCE)
 spinkham/skipfish
Web application security scanner created by lcamtuf for google - Unofficial Mirror
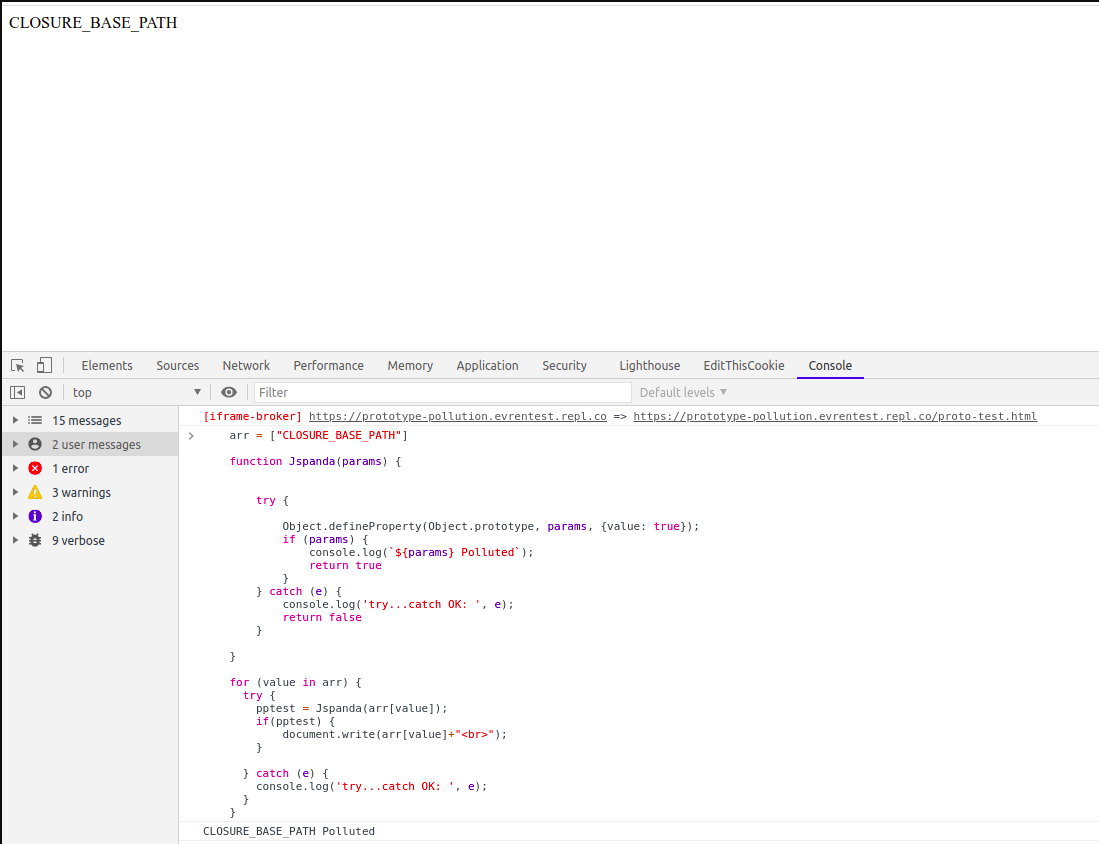 redsection/jspanda
client-side prototype pullution vulnerability scanner
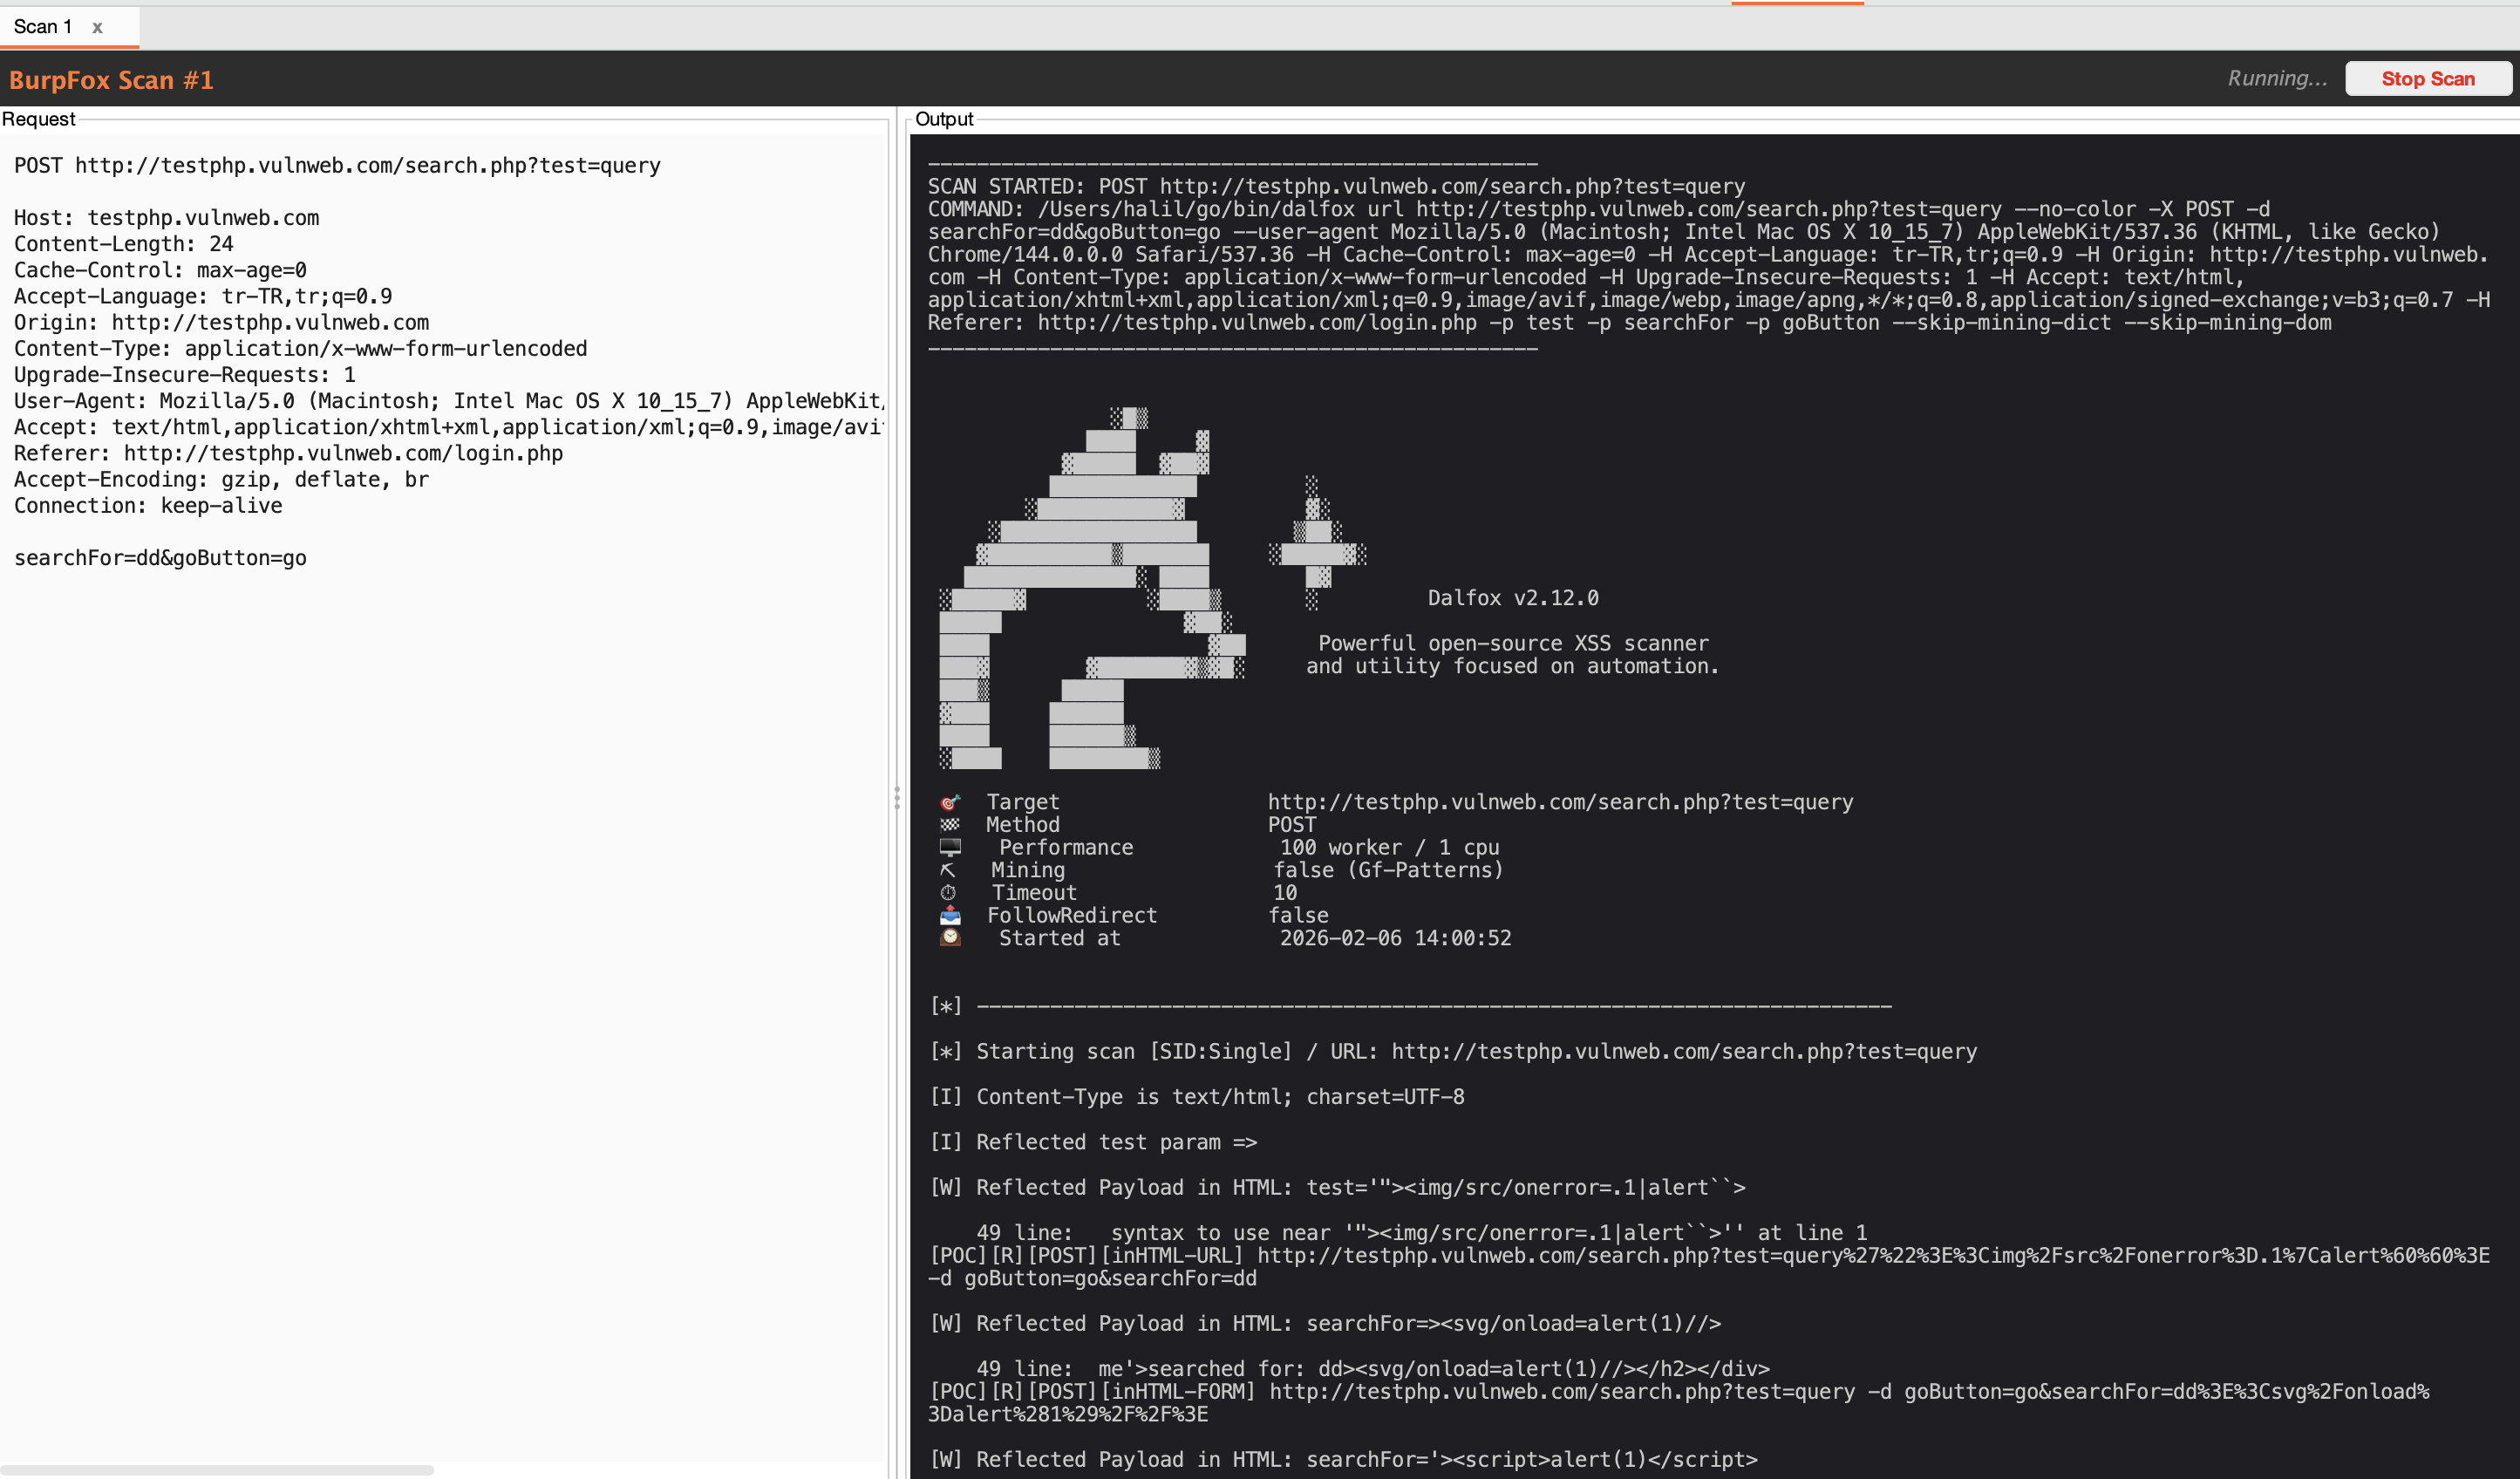 halilkirazkaya/burpfox
A Burp Suite extension that integrates Dalfox XSS scanner directly into your workflow.
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
 hackinglz/svg_phishing_tools
SVG Analysis and generation tools for commonly seen SVG attachment phishing
 arachni/arachni
Web Application Security Scanner Framework
 portswigger/http-request-smuggler
Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…
 pr0v3rbs/firmae
Towards Large-Scale Emulation of IoT Firmware for Dynamic Analysis
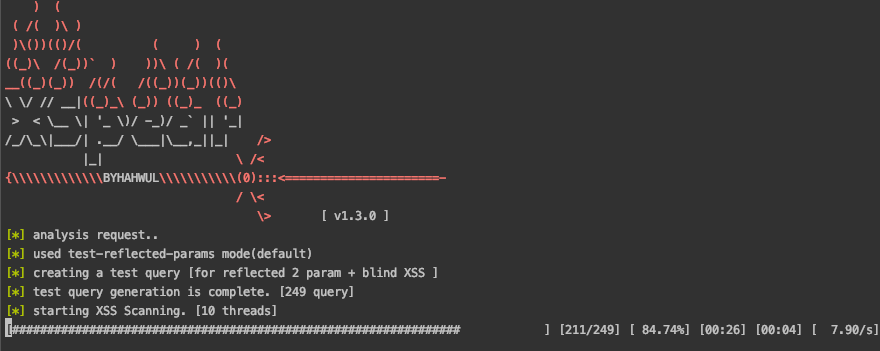 hahwul/xspear
🔱 Powerfull XSS Scanning and Parameter analysis tool&gem
 perplext/echteeteepee
Go tool and Nuclei template for testing James Kettle's (CVE-2025-32094) HTTP/1.1 must die: the desync endgame