
ntlmscout
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
authenticationdns-analysisinformation-gathering+8
18
boydhacks/ntlmscoutUnauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 mda1r/cve-2026-31278
CVE write-up for Active Directory credential exposure vulnerability in Suprema BioStar 2
 gquere/cve-2018-16987
Technical disclosure of CVE-2018-16987: cleartext storage of external service passwords in Squash TM administration panel, with CVSS 4.1 scoring and…
 xiaoqimikko/jetty-line-check
CVE-2026-2332 and 4 more 2026 Jetty CVEs: which does your Jetty (or Spring Boot) build hit, and does the fixed version Jetty names even exist on…
 hessandrew/cve-2020-3766_apsb20-12
Proof-of-concept exploit for CVE-2020-3766, an Adobe Integrity Service vulnerability. Provides technical details and advisory references for security…
 xmyronn/cve-2026-10288-auth-bypass
Proof-of-concept exploit for an authentication bypass in Hotel and Tourism Reservation System 1.0, allowing unauthenticated admin access via inverted…
 brinhosa/cve-2009-3036
Repository documenting CVE-2009-3036, an HTML injection vulnerability in Symantec IM Manager, including details and exploit references.
 halildeniz/pathfinder
Python-based web reconnaissance tool that extracts site metadata, DNS records, subdomains, firewall names, technologies, and certificate details for…
 mehrzad1994/cve-2021-21193
Educational presentation analyzing CVE-2021-21193, a use-after-free vulnerability in Google Chrome's Blink engine, including exploitation details and…
 oscerd/cve-2026-66907
Proof-of-concept reproducers for Apache Camel camel-google-storage path traversal (CVE-2026-66907), demonstrating arbitrary file write via…
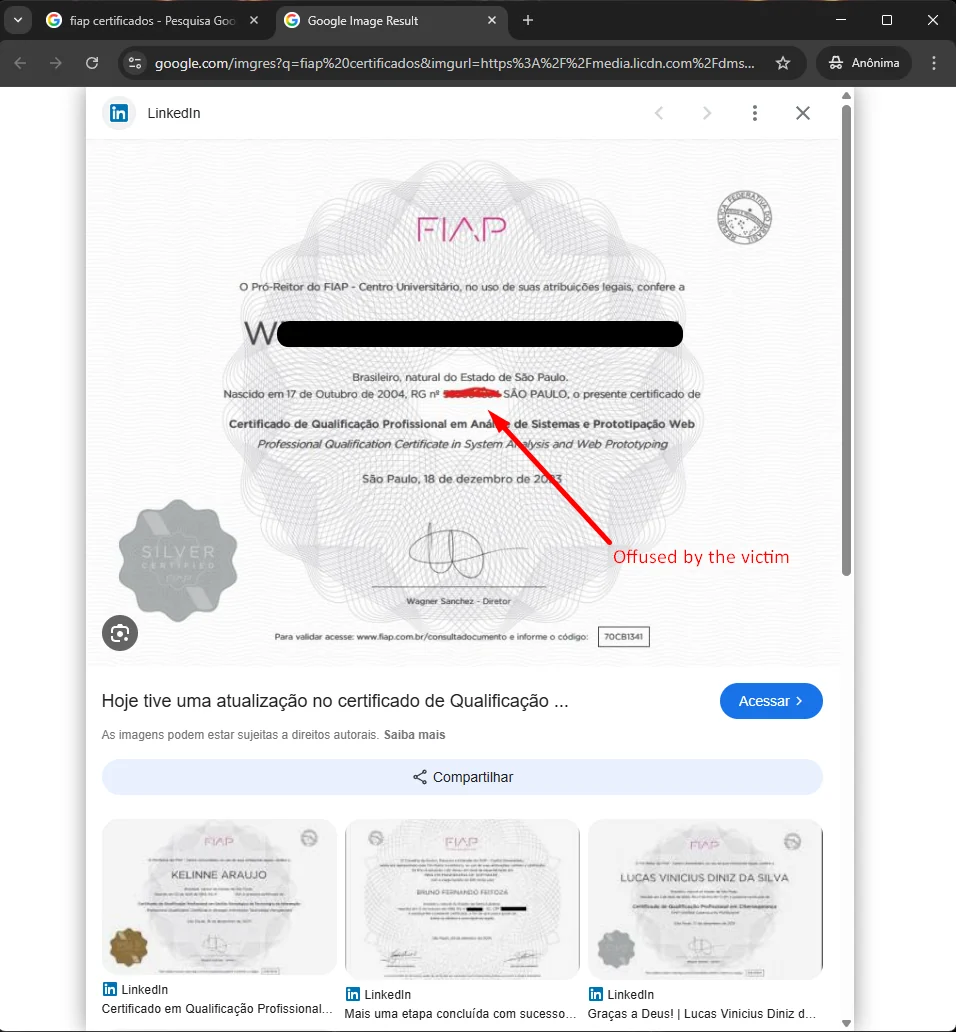 rrespxwnss/cve-2026-36374
Demonstrates an unauthenticated enumeration vulnerability in a public certificate lookup endpoint, exposing personal data such as CPF and RG.…
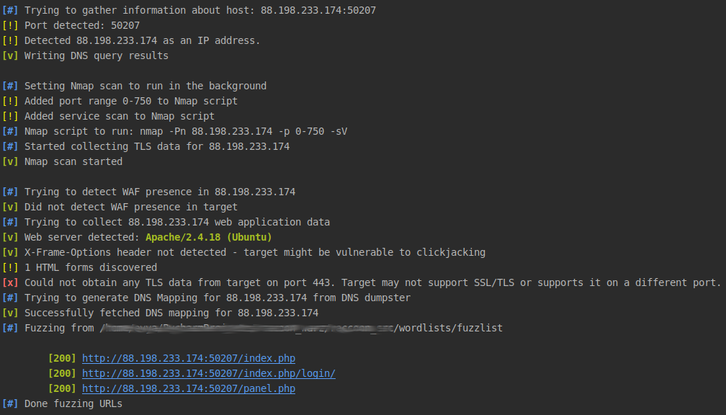 evyatarmeged/raccoon
A high performance offensive security tool for reconnaissance and vulnerability scanning
 chaitanyagarware/cve-2026-54520
Public advisory landing page documenting CVE-2026-54520, a high-severity path traversal vulnerability in ai-agent-automation's workflow executor,…
 4ybrick/cve-2026-79303
Proof-of-concept for CVE-2026-79303, a critical boolean-blind SQL injection in Kaiten affecting order_by and order_direction parameters, with…
 h4zaz/cve-2026-8793
esponsible disclosure write-ups for CVE-2026-8793 - PaperCut NG 25.0.11
 xmyronn/cve-2026-11518-xss
Proof-of-concept for unauthenticated stored XSS in SourceCodester Inventory System, demonstrating admin session hijacking via crafted registration…
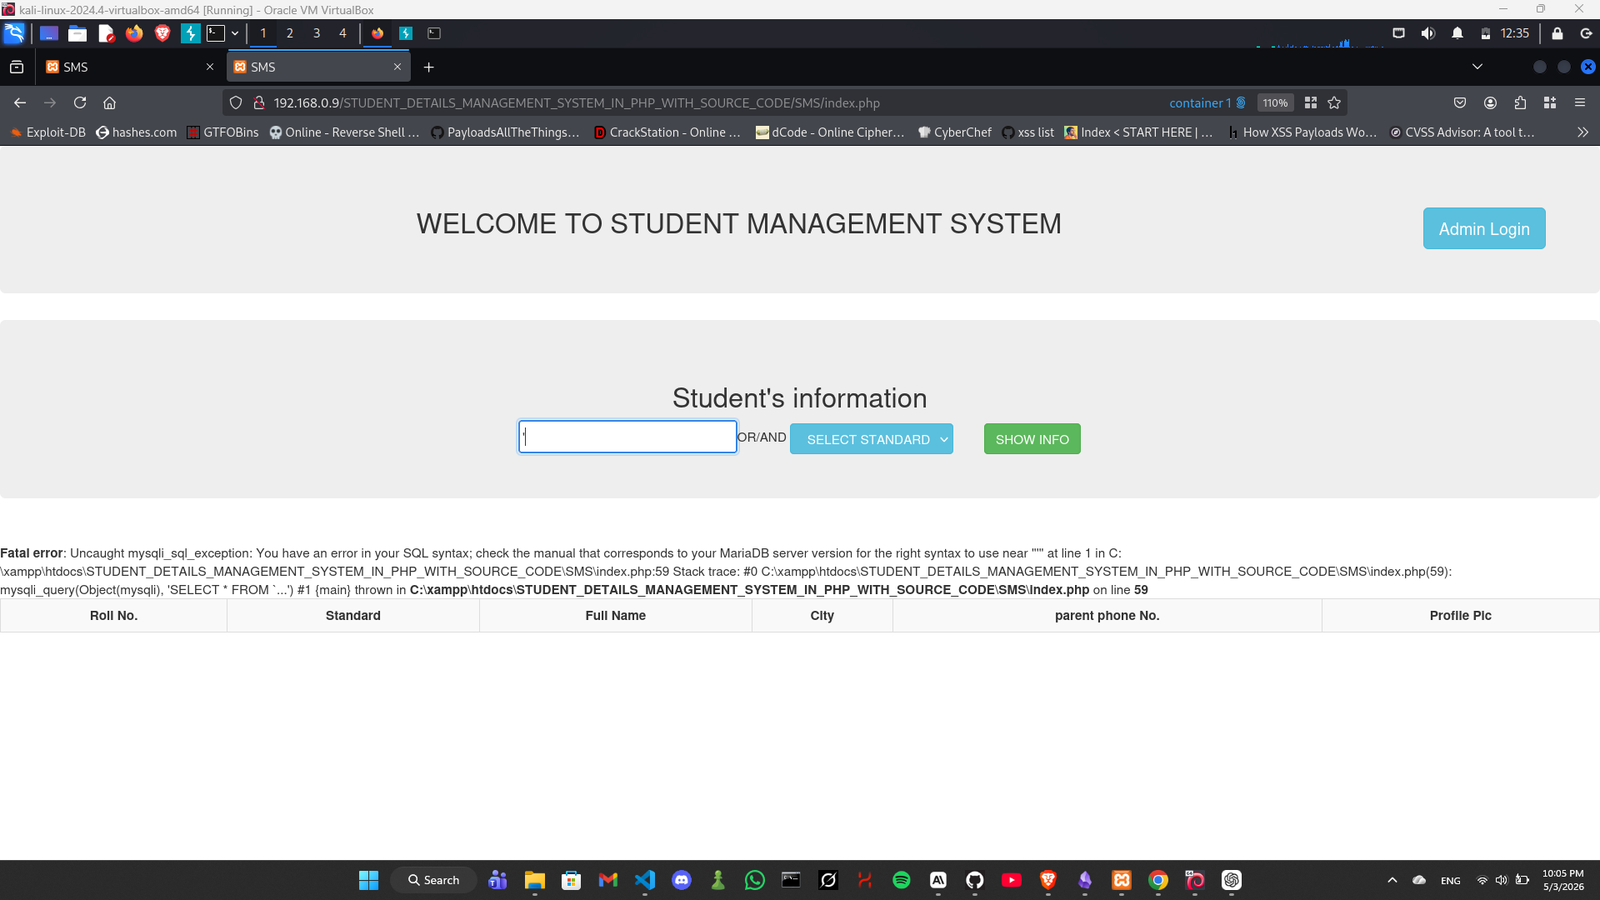 xmyronn/cve-2026-10110-sqli
Proof-of-concept for unauthenticated SQL injection in Student Details Management System 1.0, demonstrating UNION-based data extraction and credential…
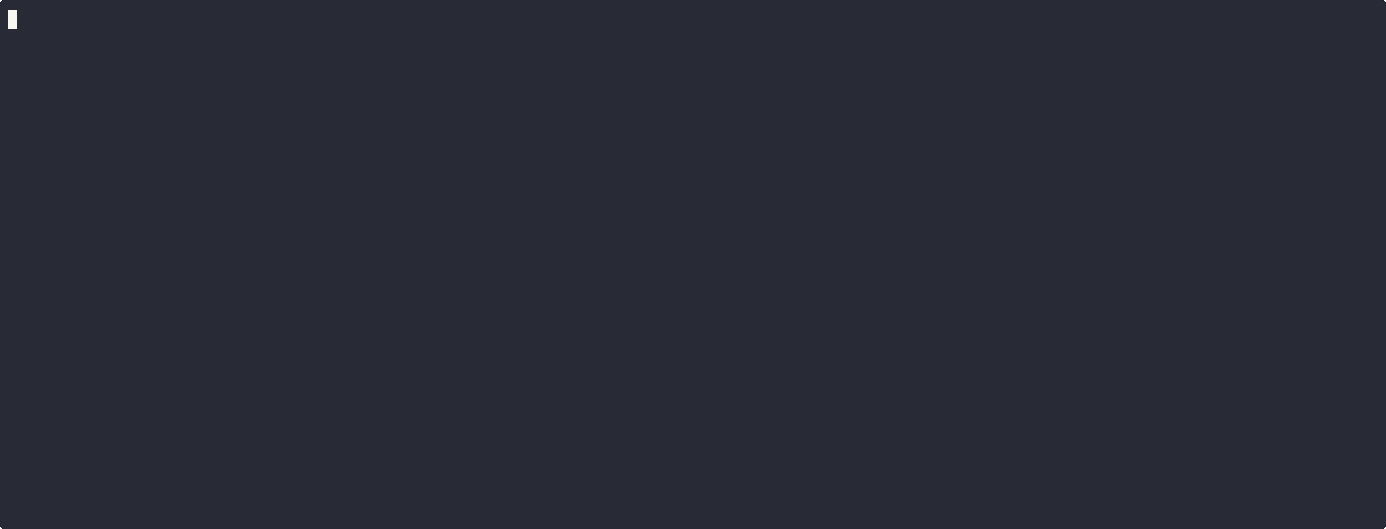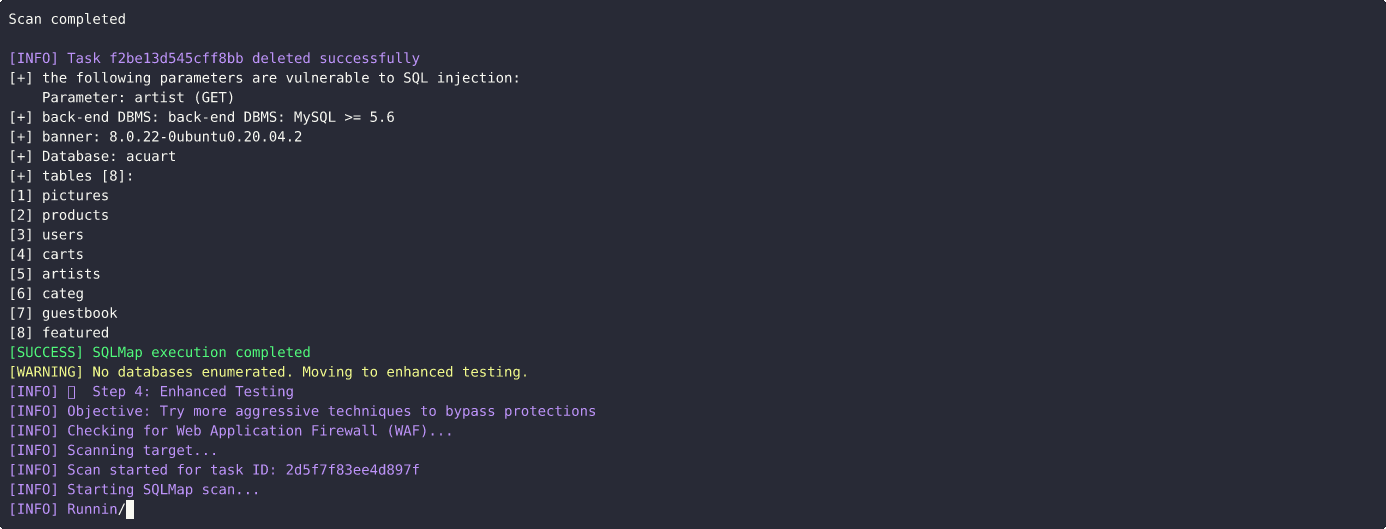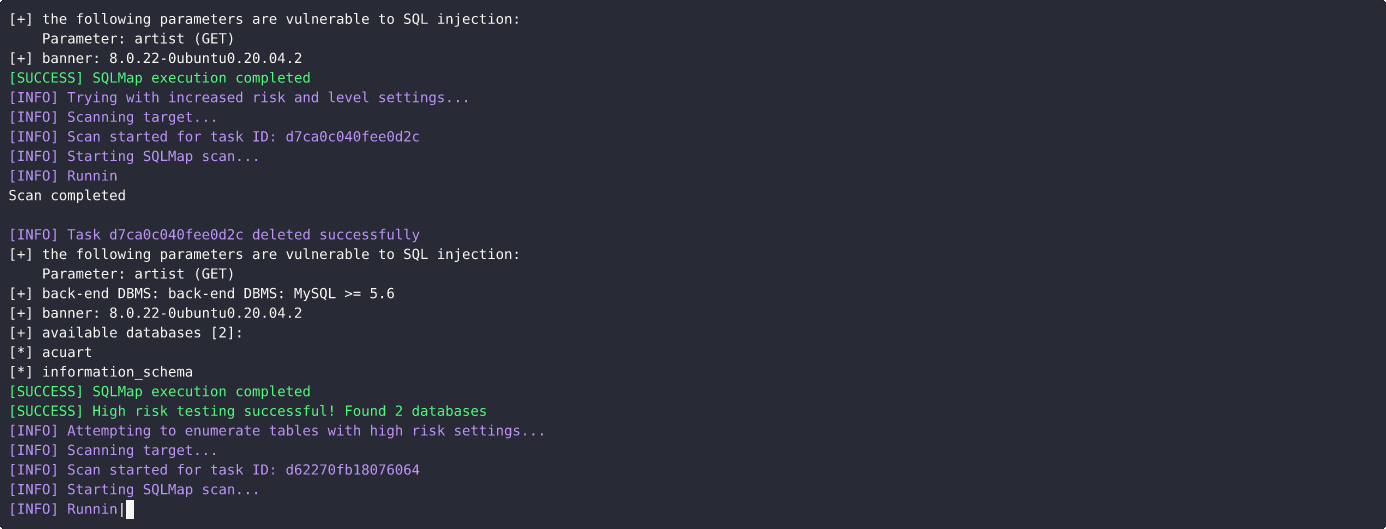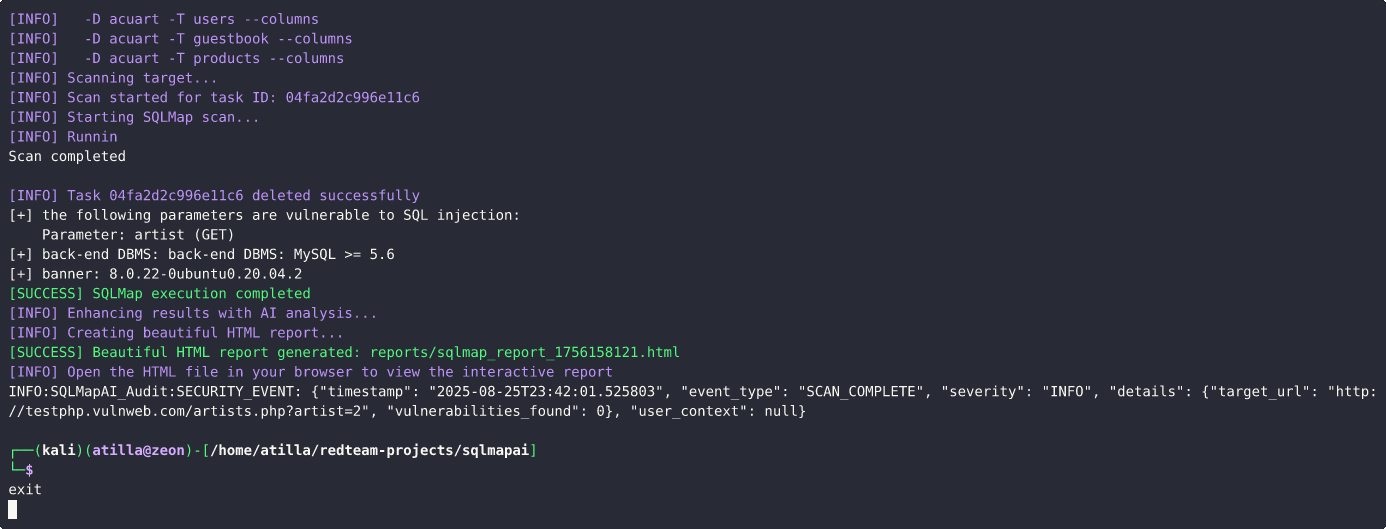 atiilla/sqlmap-ai
This script automates SQL injection testing using SQLMap with AI-powered decision making.