
caddy
 caddyserver/caddy
Fast and extensible multi-platform HTTP/1-2-3 web server with automatic HTTPS
anti-botencryption-decryption-toolsgeneral-purpose-utilities+1
74.8k4h 12m ago
caddyserver/caddyFast and extensible multi-platform HTTP/1-2-3 web server with automatic HTTPS
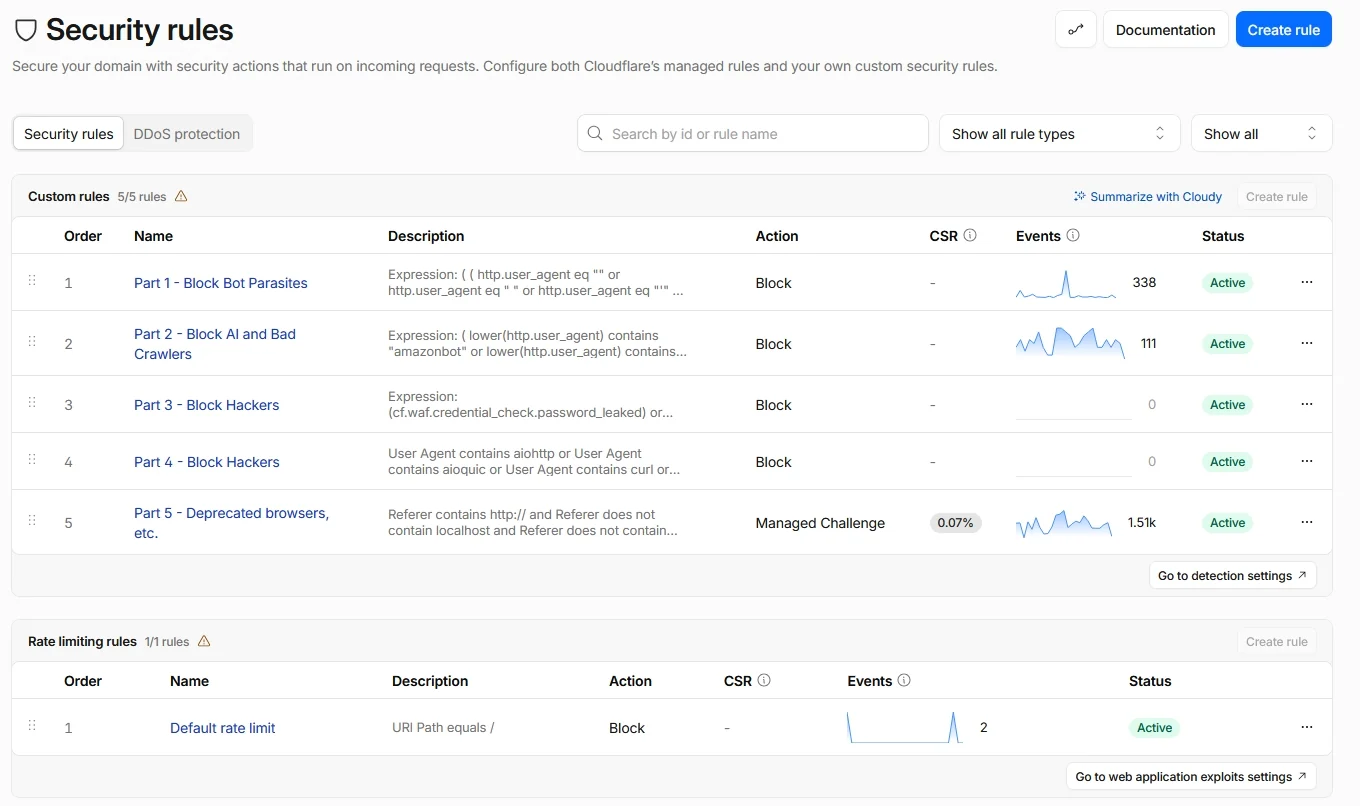 buybitart/cloudflare-security-art
Cloudflare Free Plan security rules (Zero Trust approach) for small websites
 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 chithi-dev/chithi
The next generation encrypted file sharing project
 beefproject/beef
The Browser Exploitation Framework Project
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
 horkimhab/cve-2026-wordpress
Educational CVE proof-of-concept collection targeting WordPress vulnerabilities, with setup scripts and lab guidance for authorized security research…
 efforg/https-everywhere
A browser extension that encrypts your communications with many websites that offer HTTPS but still allow unencrypted connections.
 owasp/secure-headers-project
OWASP knowledge base and validator for HTTP security response headers, providing recommendations, statistics, and automated configuration checks.
 jarryshaw/darc
Darkweb crawler that uses requests and Selenium workers to fetch pages, capture headers and cookies, extract links, and save rendered screenshots for…
 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 xkiian/awswaf
AWS WAF Solver, full reverse implemented in 100% Python & Golang.
 raghavd3v/crlfsuite
The most powerful CRLF injection (HTTP Response Splitting) scanner.
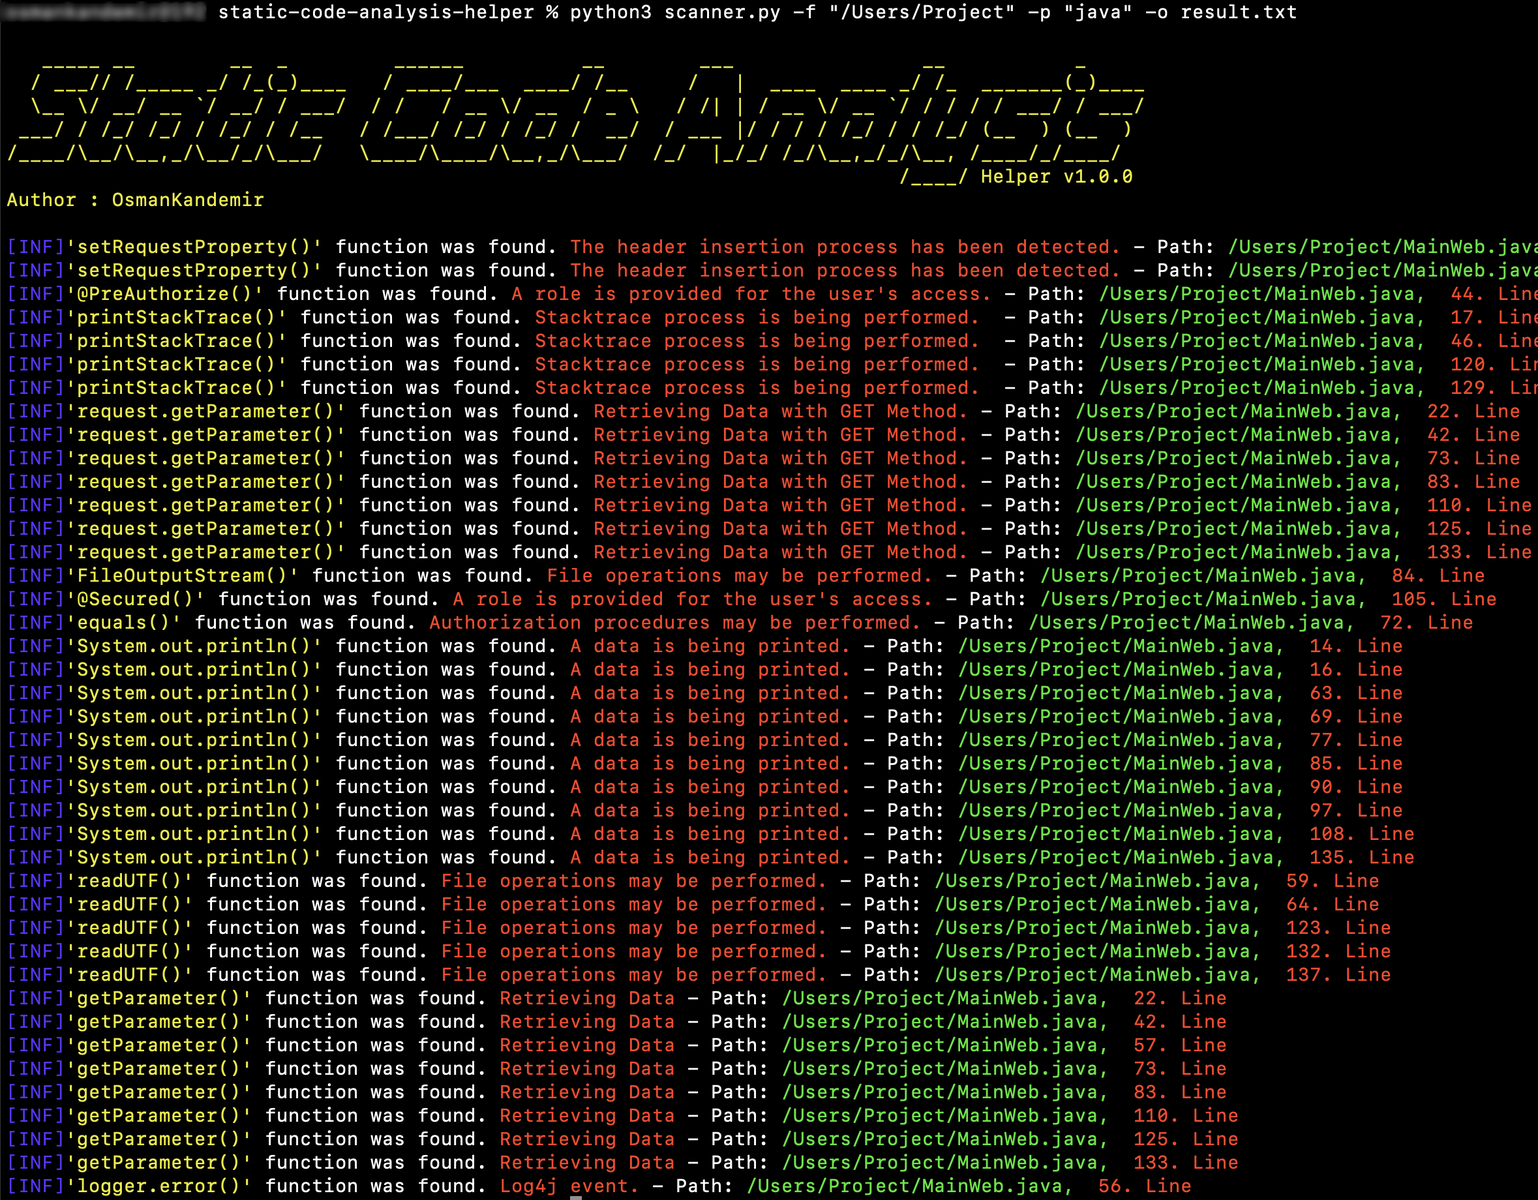 osmankandemir/static-code-analysis-helper
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…