njsscan
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
code-analysisdevsecopsstatic-analysis+3
456
ajinabraham/njsscanSemantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 open-flaw/cve-2017-11499
Documentation of CVE-2017-11499: a hash flooding remote DoS vulnerability in Node.js caused by constant HashTable seeds, with analysis of the attack…
 open-flaw/cve-2026-56848
Exploit PoC for CVE-2026-56848, a Node.js HTTP/2 heap-use-after-free that allows remote unauthenticated DoS. Includes raw-socket trigger, ASan build…
 ajinabraham/nodejsscan
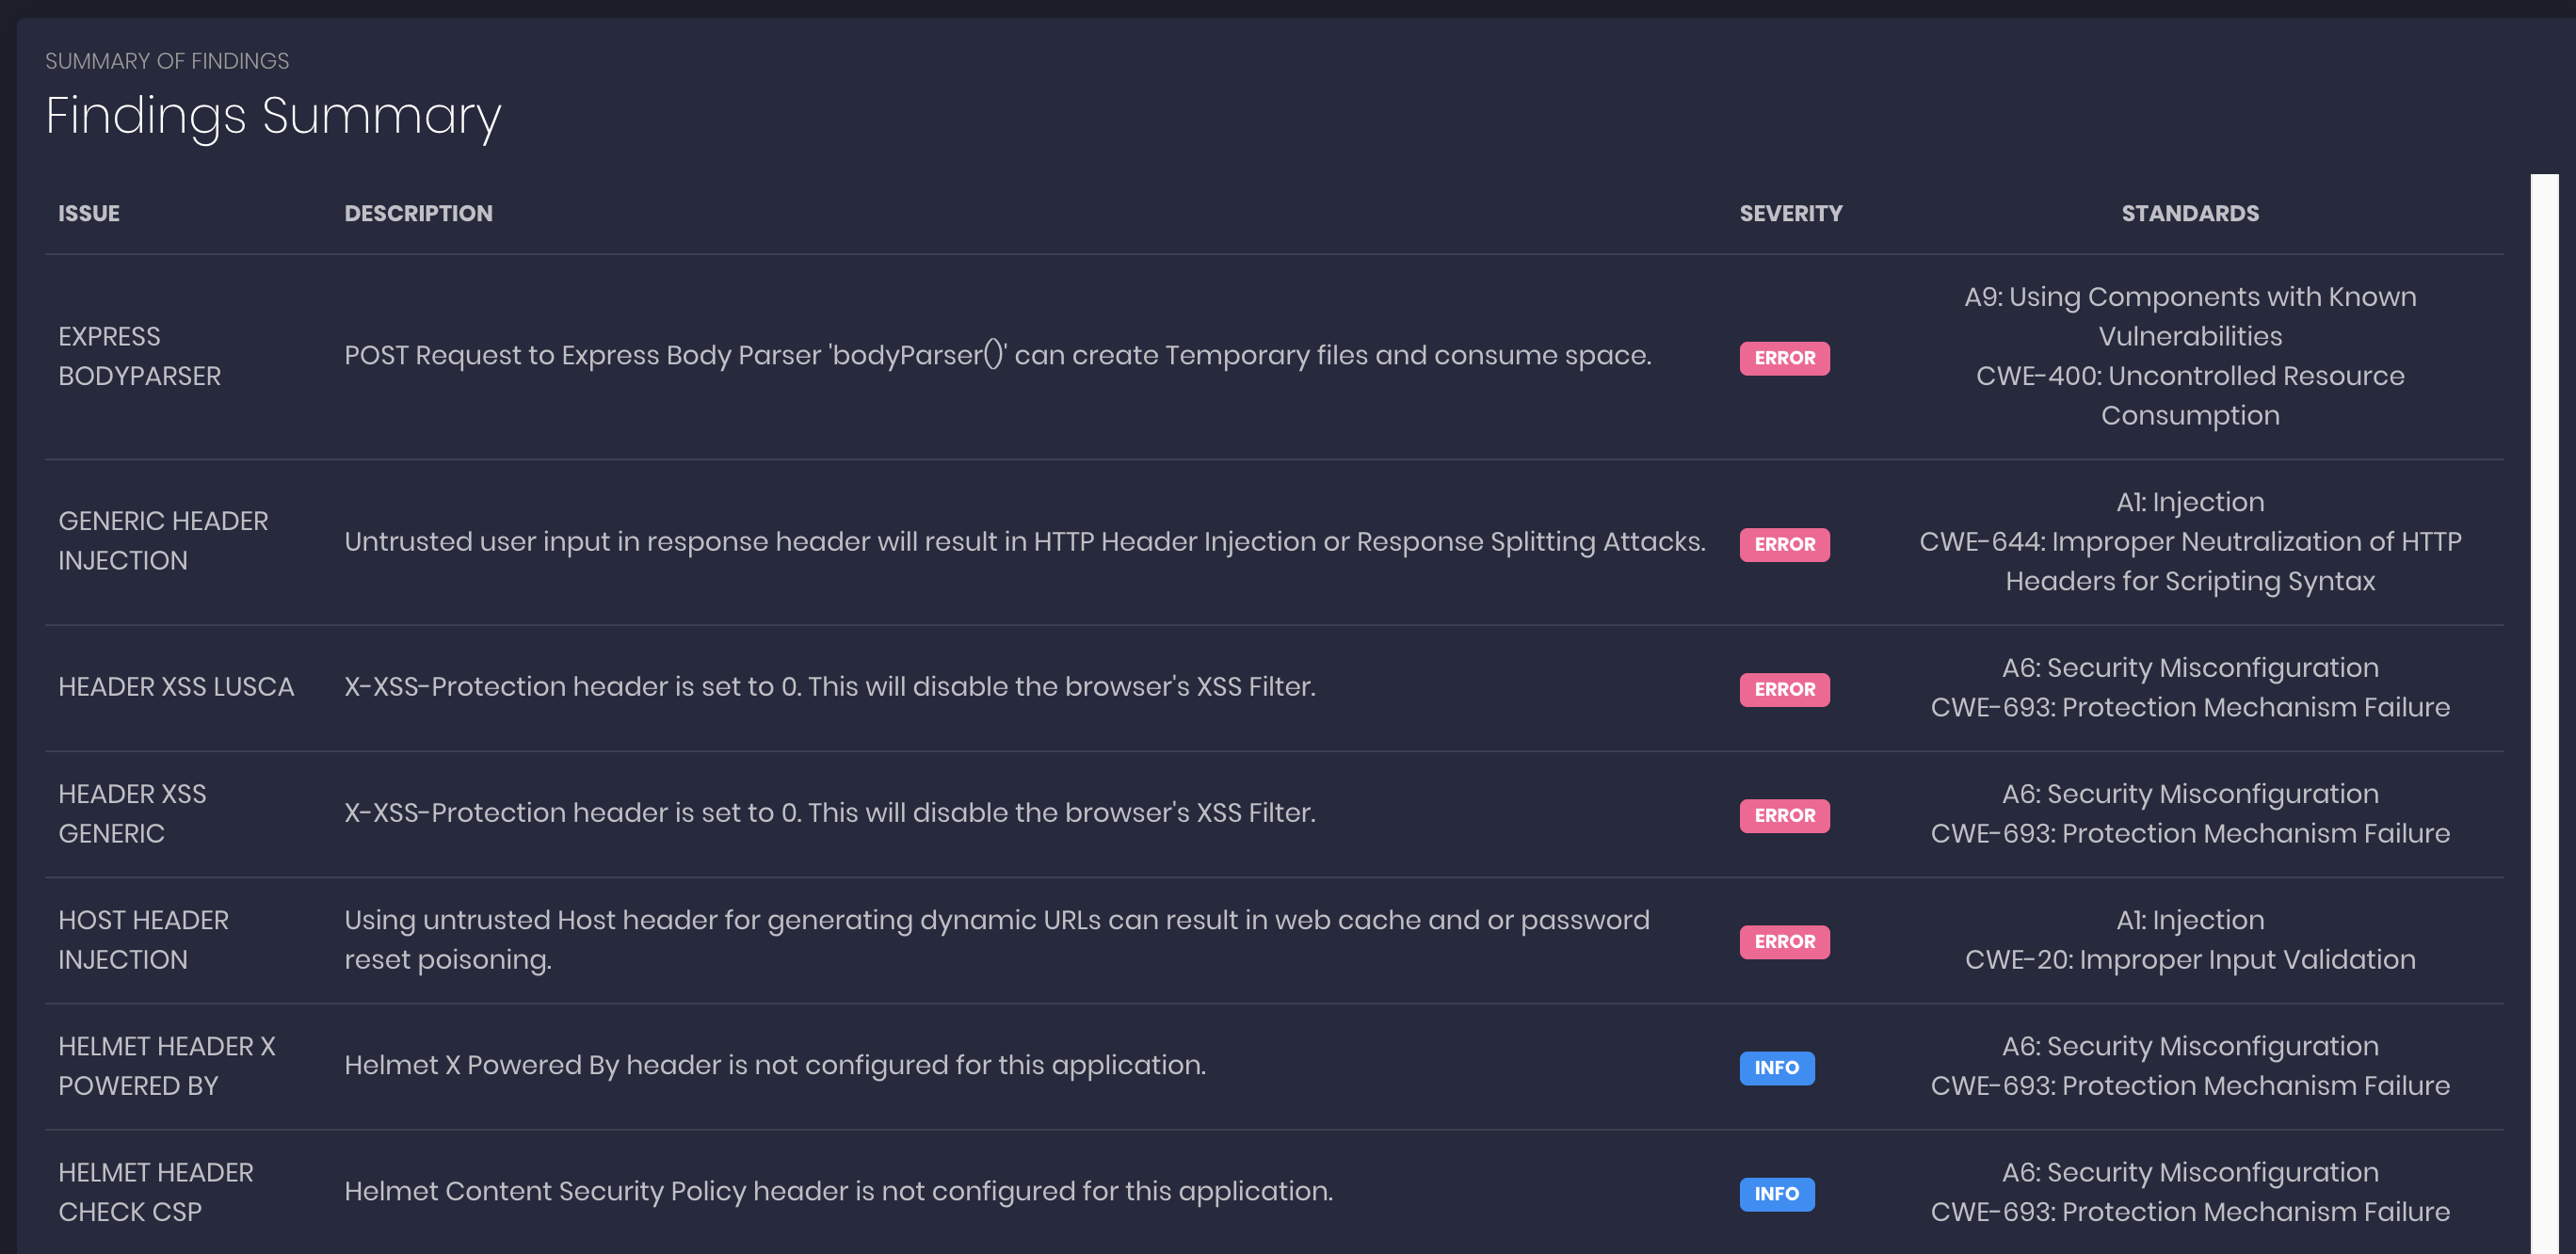
nodejsscan is a static security code scanner for Node.js applications.
 jimywork/certstreamcatcher
This tool is based on regex with effective standards for detecting phishing sites in real time using certstream and can also detect punycode (IDNA)…
 open-flaw/cve-2026-25940
Proof-of-concept for CVE-2026-25940 demonstrating embedded JavaScript execution via crafted AcroForm radio button appearances in PDF viewers, with…
 mustafabilgici/sucoshscanny
"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…
 terra-nova83/cve-2026-0915-json-patch.-v2.0
Provides a security patch for CVE-2026-0915, adding strict JSON schema validation, input sanitization, and rate limiting to prevent injection and DoS…
 scumfrog/cve-2025-55130
POC for CVE-2025-55130
 george0papasotiriou/cve-2026-3030-prototype-pollution-in-json-merge-patch
Demonstrates CVE-2026-3030 prototype pollution in a Node.js JSON merge patch REST API, including a vulnerable server and exploit script for privilege…

 fastify/send
Node.js library for streaming files as HTTP responses with support for partial content, conditional requests, and configurable caching headers.…
 nikeee/cve-2026-27607
Proof-of-concept exploit for CVE-2026-27607, a missing post-policy validation in RustFS, demonstrating the vulnerability with a Node.js script and…
 4auvar/vulnnodeapp
Deliberately vulnerable Node.js web application for practicing exploitation of SQL injection, XSS, IDOR, command injection, XXE, and deserialization…
 solidevil14/suricata-rule-for-detecting-cve-2025-55182
CVE‑2025‑55182 Detection
 polaris64/web_exploit_detector
The Web Exploit Detector is a Node.js application used to detect possible infections, malicious code and suspicious files in web hosting environments
 abhisek3122/cve-2025-23167
Working exploit for CVE-2025-23167 – HTTP request smuggling in vulnerable Node.js 20.x versions before 20.19.2