
Burp-Recordadora
Persists BurpSuite proxy history, Repeater requests, and Intruder payloads across sessions; exports and imports .log files for web pentesting context.

Persists BurpSuite proxy history, Repeater requests, and Intruder payloads across sessions; exports and imports .log files for web pentesting context.

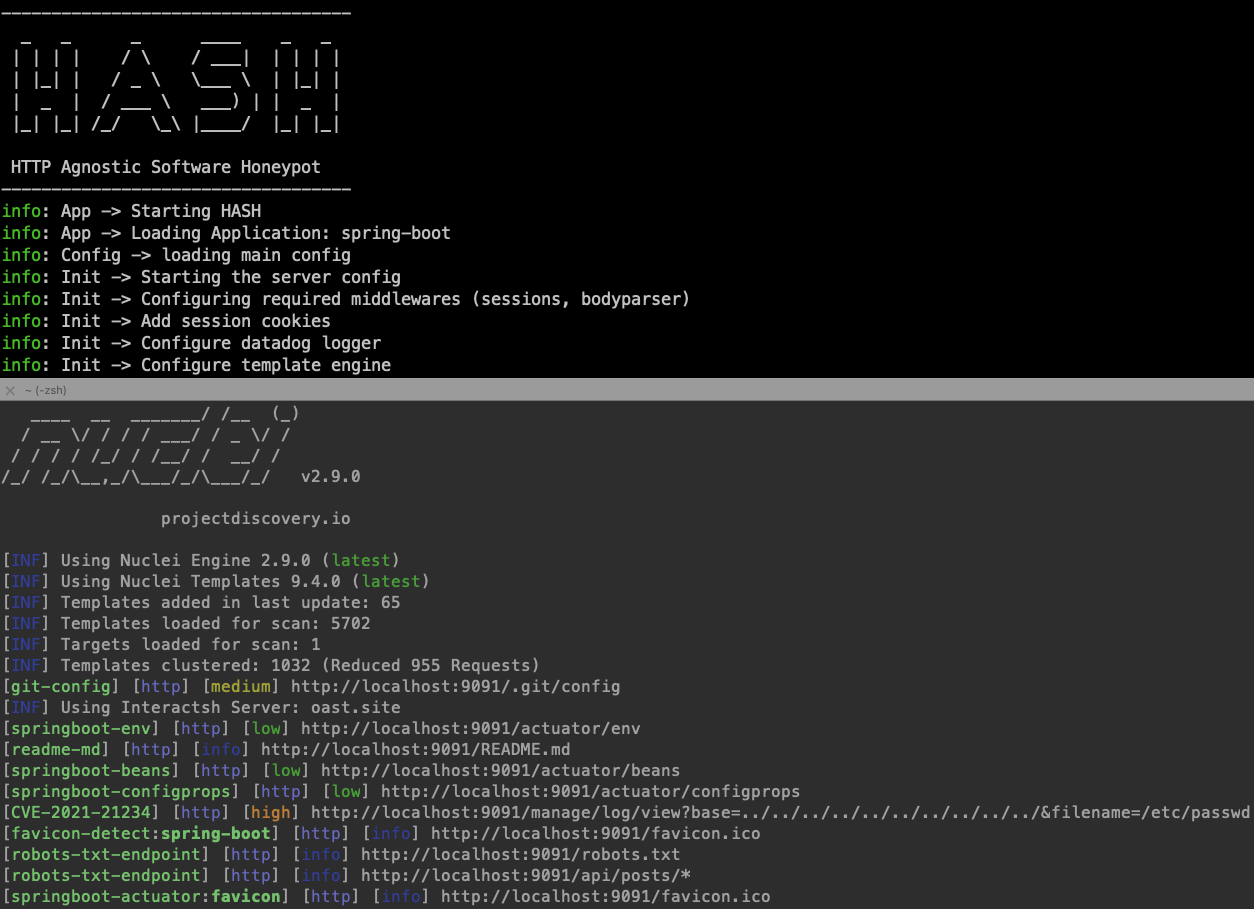
YAML-configurable low-interactive honeypot framework for deploying HTTP/HTTPS-based deception servers with built-in honeytraps and Datadog log…

Analyze and track OAuth 2.0, OIDC, and Microsoft Entra ID tokens from Burp, mitmproxy, or Chrome DevTools captures. Visualize token lifecycles,…

Scanner for the Log4j vulnerability dubbed Log4Shell (CVE-2021-44228)

Parse citrix netscaler logs to check for signs of CVE-2023-4966 exploitation

Offensive security platform that automates attack surface discovery and vulnerability management

Apache Real Time Logs Analyzer System

Add POST body excerpt to Bro's HTTP log

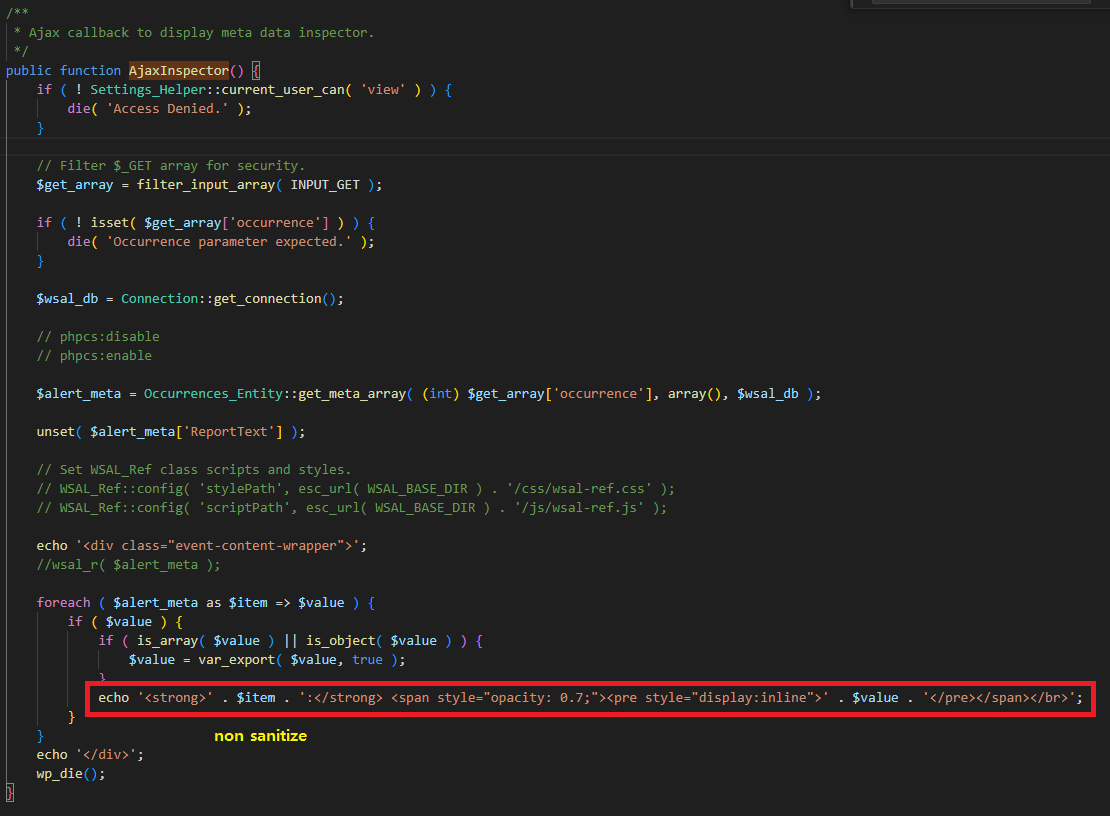
Technical analysis of CVE-2025-0924, a Stored XSS vulnerability in WP Activity Log plugin for WordPress. Includes root cause analysis, exploitation…

Passive Laravel middleware that detects and logs SQL injection, XSS, RCE, bot scanners, and 175+ attack patterns. Features a built-in dashboard,…

Proof-of-concept for CVE-2023-51214: a stored XSS vulnerability in a PHP-based activity log web application allowing remote code execution via…

Read-only IOC scanner and mitigation toolkit for cPanel & WHM EmailTrack SQL injection (CVE-2026-67401). Performs version fingerprinting, file…

Technical analysis and defensive mitigation for a WordPress Core pre-auth XSS-to-RCE chain, including sanitizer bypass, DOM clobbering, JSONP abuse,…

Temporary WordPress plugin requiring authentication for the Core REST Batch API endpoint to mitigate the wp2shell vulnerability chain…

Wazuh detection rules for CVE-2026-73570, an OS command injection in Zimbra Collaboration Suite, monitoring web access logs and zimbra.log for…

Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…

Easy automated vulnerability scanning, reporting and analysis

CVE-2026-41940 cPanel/WHM auth bypass IOC scanner — fixes false positives in upstream detection script, adds log cross-correlation