

CyberStrike
 cyberstrikeus/cyberstrike
Autonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…
ai-securitycloud-securityeducation+9
3.3k
cyberstrikeus/cyberstrikeAutonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…
 rodhnin/hephaestus-server-forger
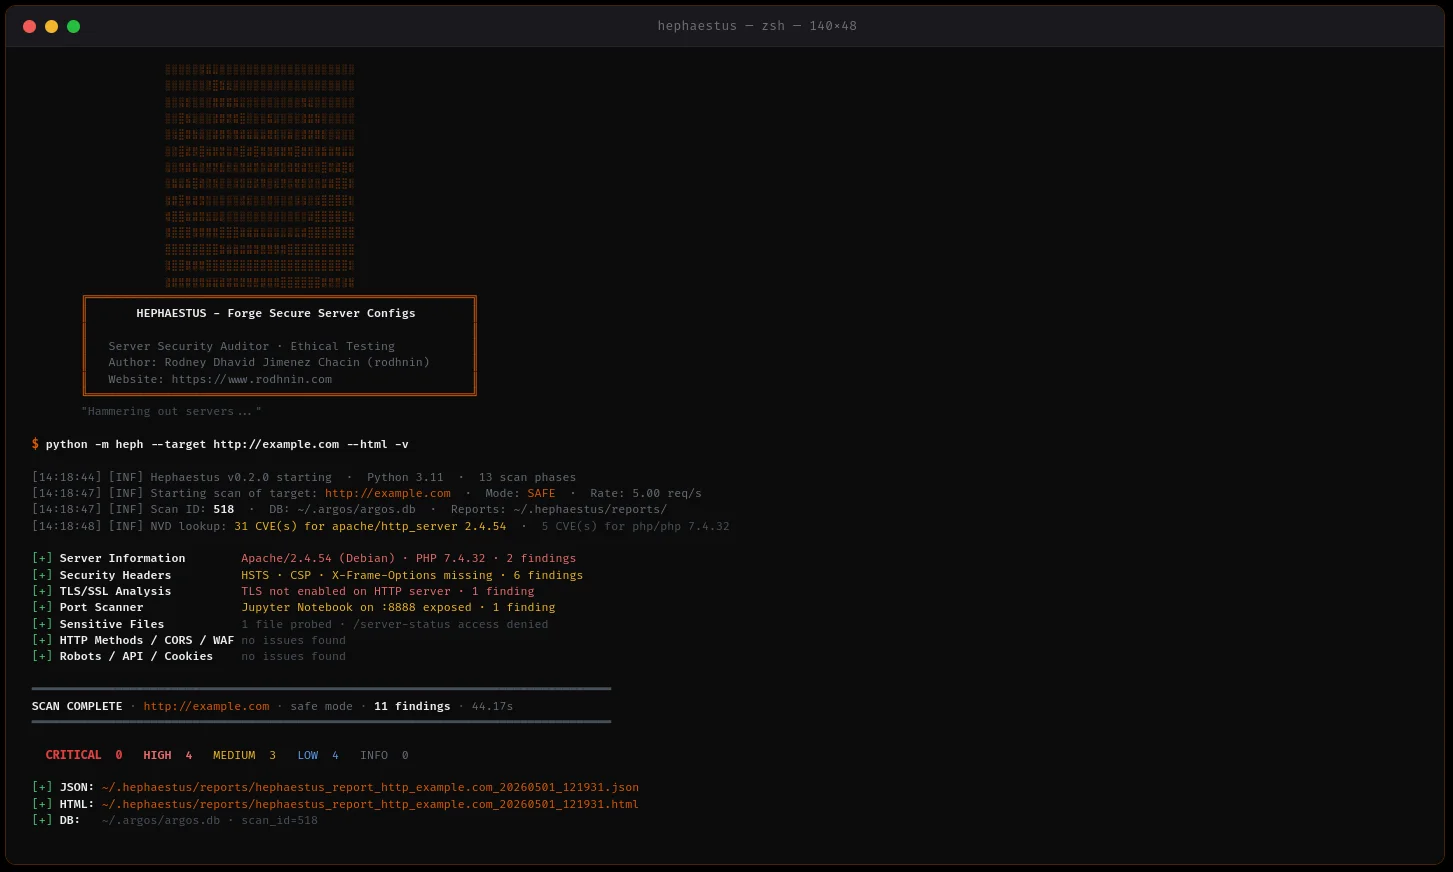
server security auditor scanning Apache, Nginx, and IIS configurations with AI-powered hardening guides and professional reporting.
 teycir/honeypotscan
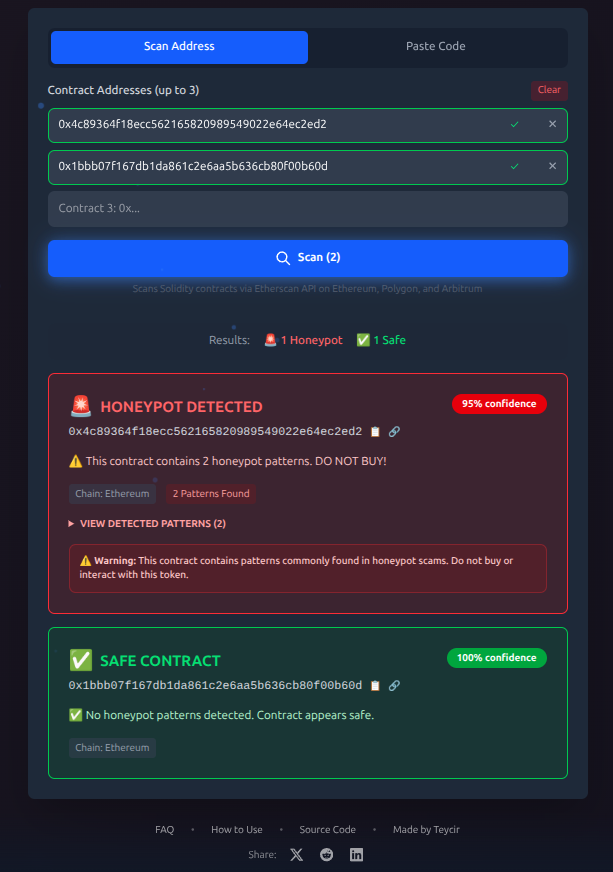
Free honeypot token scanner for Ethereum, Polygon & Arbitrum. Detect scam tokens before you buy. Instant analysis of smart contracts using 13…
 emresandikci/nextjs-cve-2026-23870-checker
Checker and fixer for all 13 vulnerabilities in the Next.js May 2026 security release (CVE-2026-23870)
 paragbagul111/cve-2024-41290
FlatPress CMS v1.3.1 1.3 was discovered to use insecure methods to > store authentication data
 sneden/zeroheight-account-verification-bypass-cve-2025-65925
Independent security finding – Zeroheight account creation bypass via missing verification enforcement (patched June 2025)
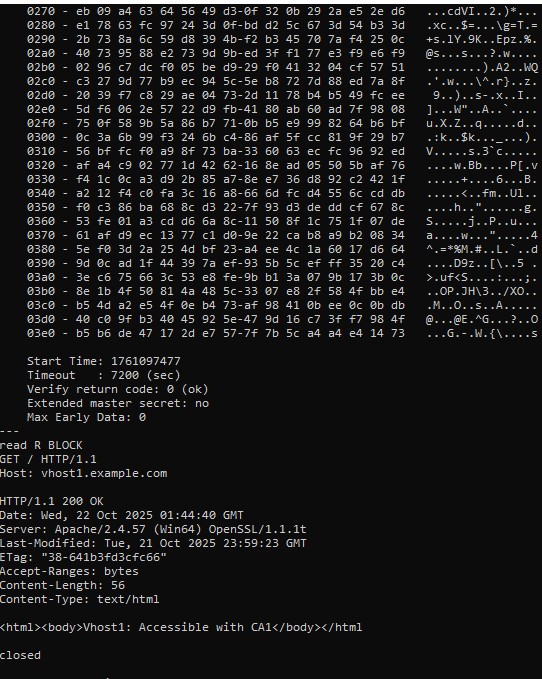 absholi7ly/cve-2025-23048-poc
Apache HTTP Server versions 2.4.35 – 2.4.63 are vulnerable to a client certificate authentication bypass when TLS 1.3 session resumption is used…
 watchtowrlabs/kentico-xperience13-authbypass-wt-2025-0011
Python script for checking authentication bypass vulnerability (WT-2025-0011) in Kentico Xperience 13 CMS Staging Service via POST request analysis.
 watchtowrlabs/kentico-xperience13-authbypass-wt-2025-0006
Authentication bypass detection script for Kentico Xperience 13 CMS Staging Service using a single POST request to verify vulnerability.
 randomrobbiebf/cve-2024-50507
DS.DownloadList <= 1.3 - Unauthenticated PHP Object Injection
 paragbagul111/cve-2024-33210
A cross-site scripting (XSS) vulnerability has been identified in Flatpress 1.3. This vulnerability allows an attacker to inject malicious scripts…
 sanupl/cve-2021-45744
CVE-2021-45744 - A Stored Cross Site Scripting (XSS) vulnerability exists in bludit 3.13.1 via the TAGS section in login panel. Application stores…
 sanupl/bludit-3.13.1-about-plugin-stored-cross-site-scripting-xss
CVE-2021-45745 - A Stored Cross Site Scripting (XSS) vulnerability exists in Bludit 3.13.1 via the About Plugin in login panel. Application stores…
 sanupl/cve-2021-45745
CVE-2021-45745 - A Stored Cross Site Scripting (XSS) vulnerability exists in Bludit 3.13.1 via the About Plugin in login panel. Application stores…
 paragbagul111/cve-2024-33209
FlatPress 1.3. is vulnerable to Cross Site Scripting (XSS). An attacker can inject malicious JavaScript code into the "Add New Entry" section, which…
 sanupl/bludit-3.13.1-tags-field-stored-cross-site-scripting-xss
CVE-2021-45744 - A Stored Cross Site Scripting (XSS) vulnerability exists in bludit 3.13.1 via the TAGS section in login panel. Application stores…