
erebus
 ethicalhackingplayground/erebus
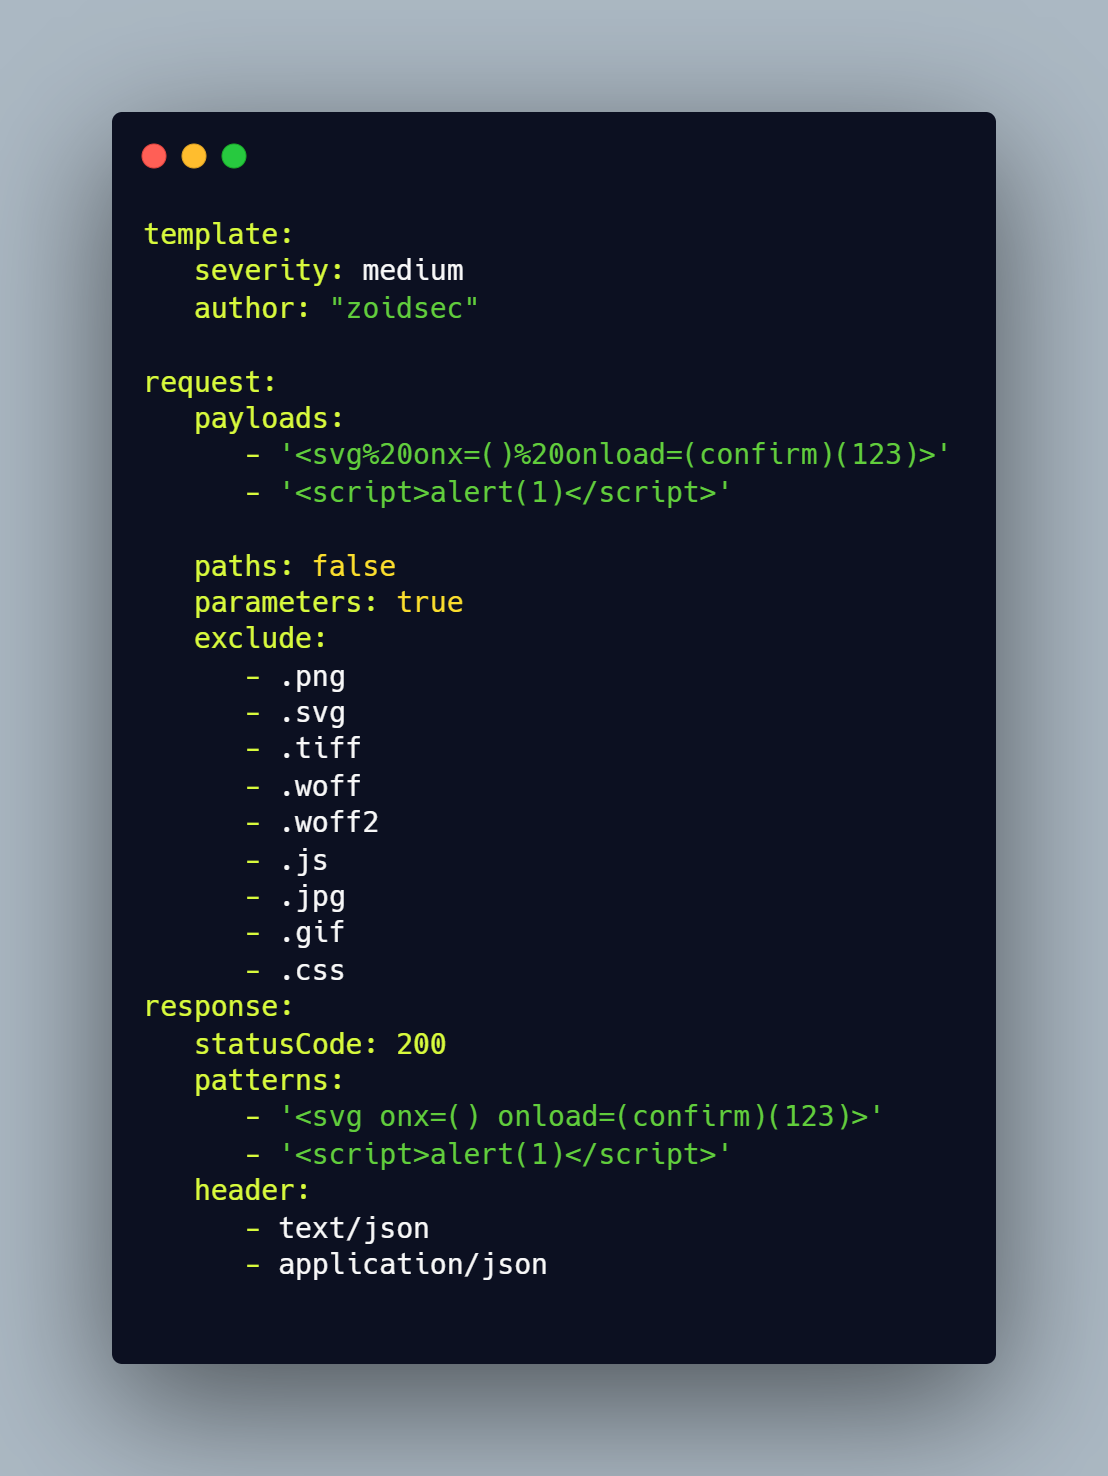
Erebus is a fast tool for parameter-based vulnerability scanning using a Yaml based template engine like nuclei.
fuzzingpenetration-testingvulnerability-scanners+4
133
ethicalhackingplayground/erebusErebus is a fast tool for parameter-based vulnerability scanning using a Yaml based template engine like nuclei.
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 ignitetechnologies/burpsuite-for-pentester
This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
 bugbasesecurity/pentest-copilot
AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…
 bugcrowd/hunt
Flags parameters commonly associated with injection, SSRF, path traversal, IDOR, and SSTI, via passive Burp/ZAP scanning; also organizes manual…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 p3n73st3r/ghazi
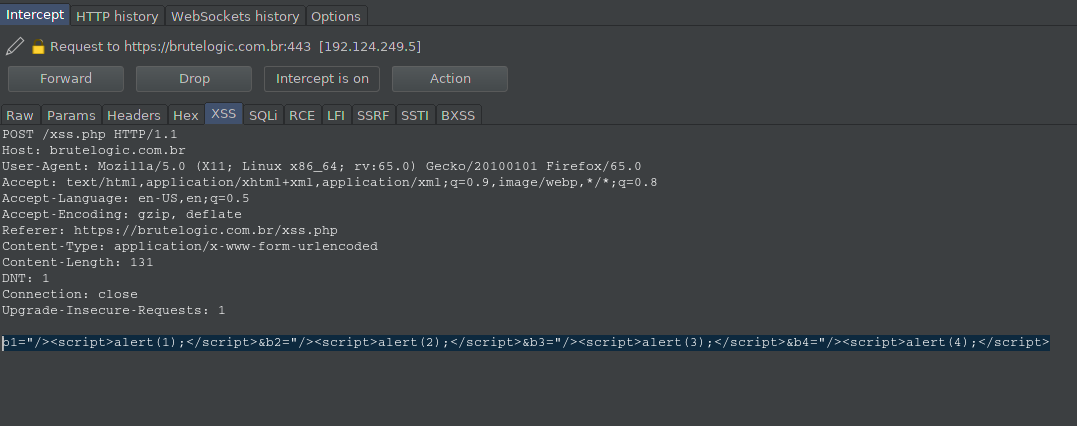
Ghazi is a BurpSuite Plugins For Testing various PayLoads Like "XSS,SQLi,SSTI,SSRF,RCE and LFI" through Different tabs , Where Each Tab Will Replace…
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 matank001/moxy
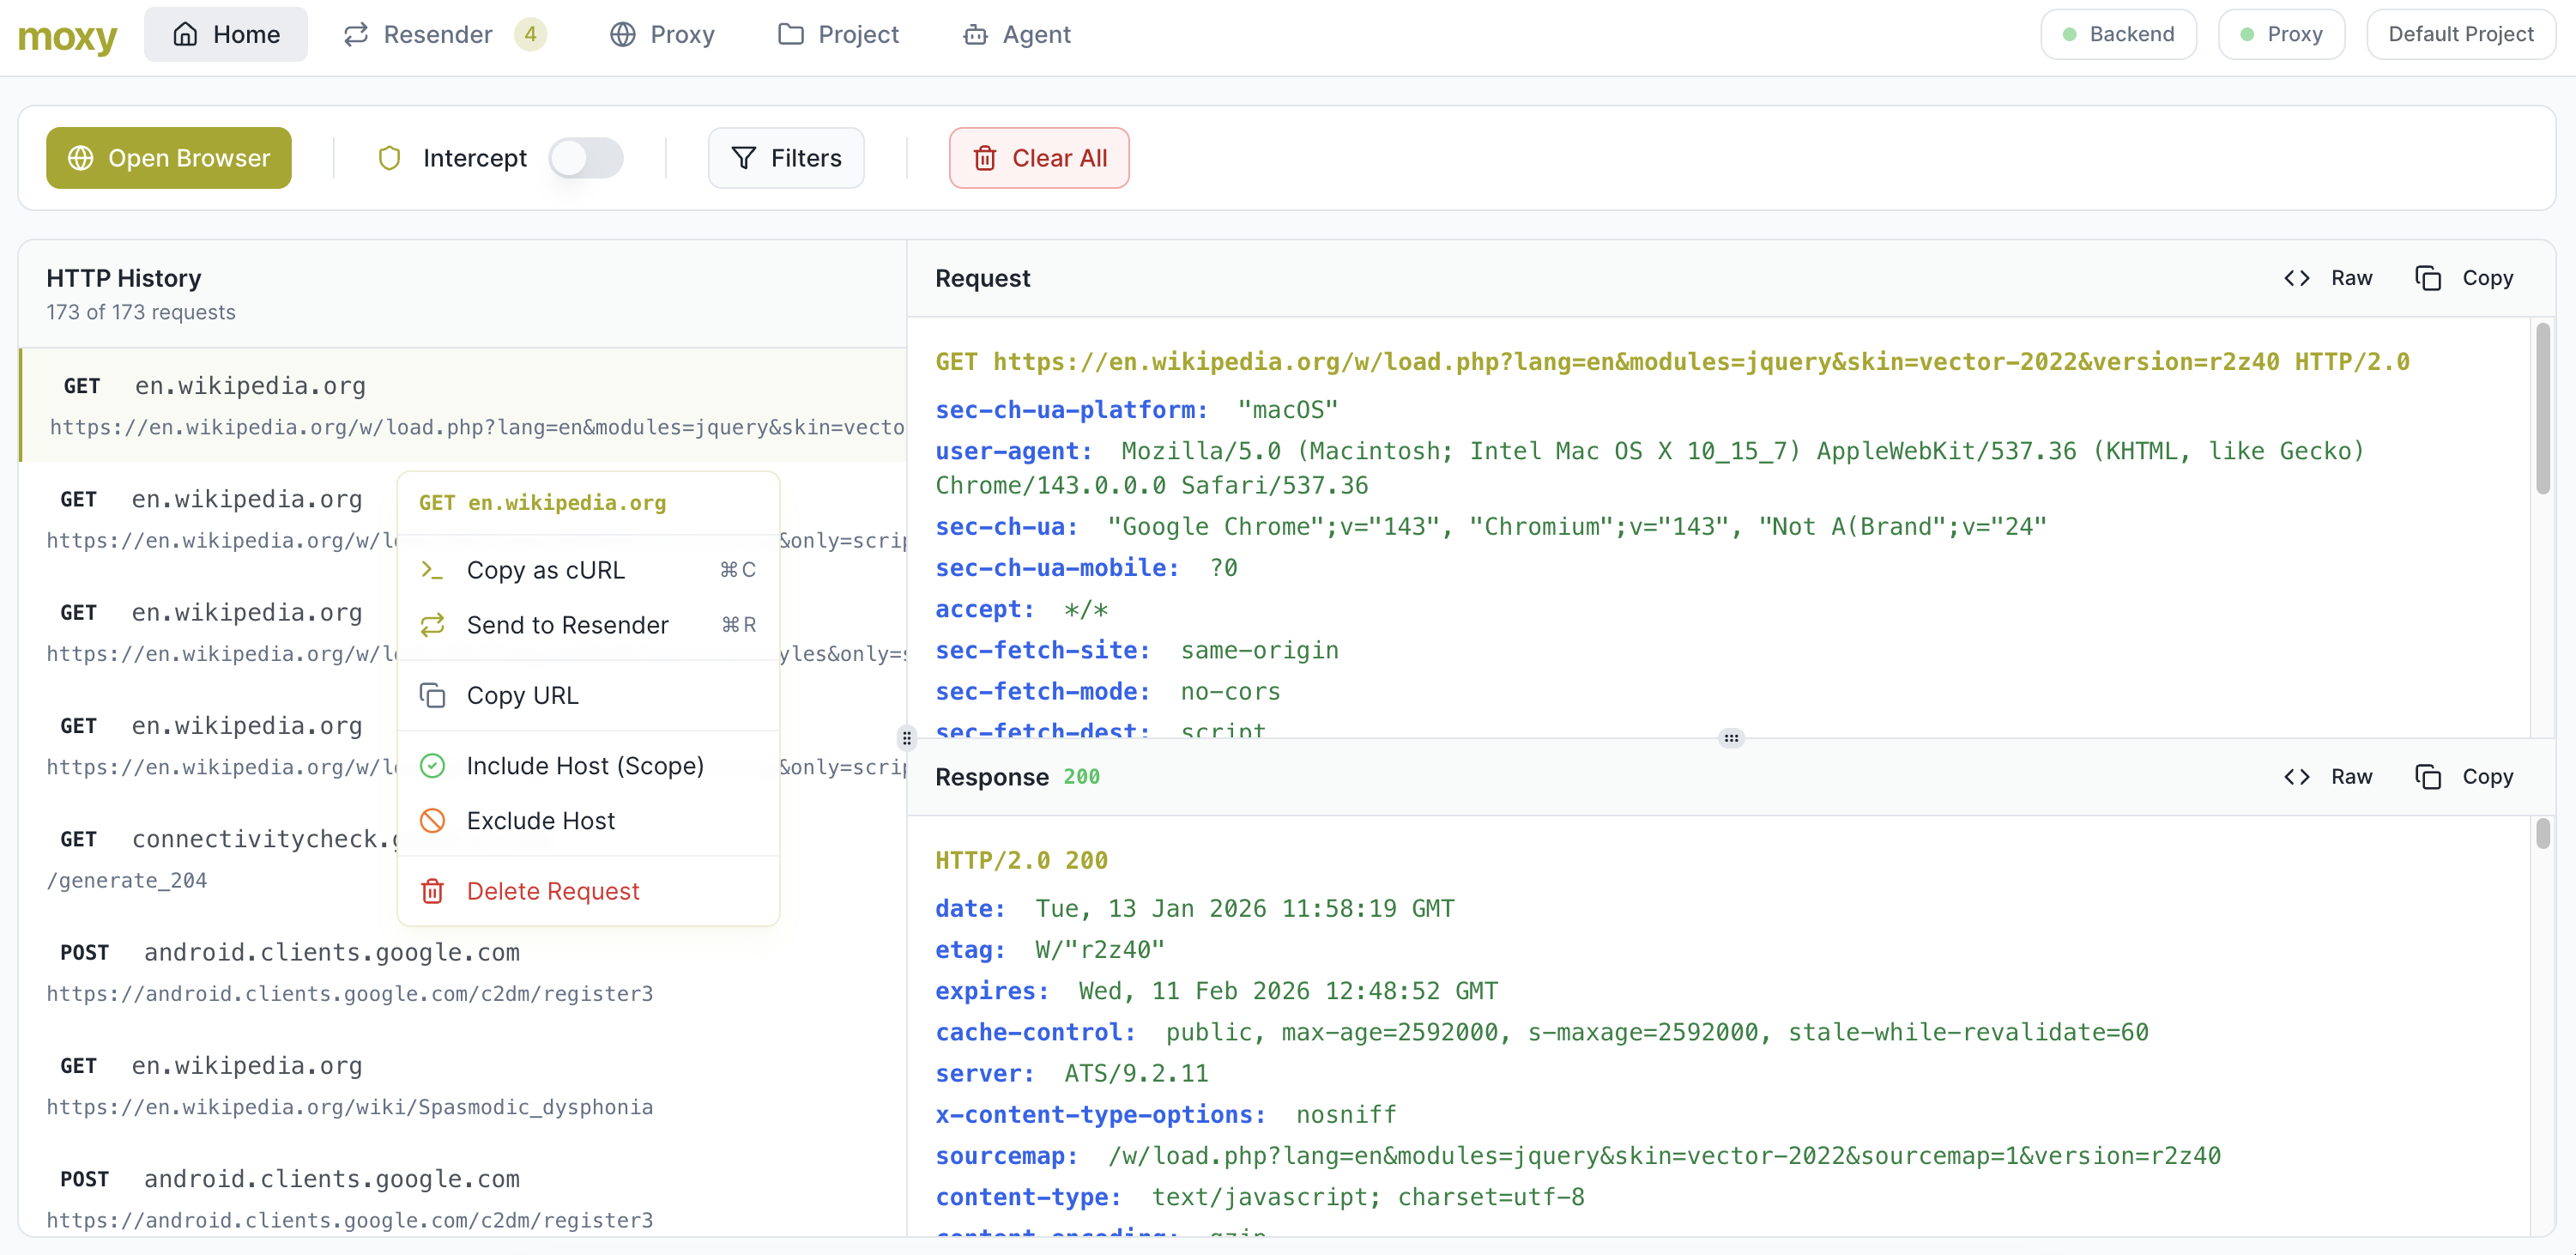
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 jas502n/burpsuite_pro_v1.7.37
Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…
 nccgroup/wcfdser-ngng
A Burp Extender plugin, that will make binary soap objects readable and modifiable.
 weirdmachine64/redom
A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…
 zaproxy/zap-api-rust
Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
 sunghoojung/reverse-engineering-browser
Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…
 imbas007/cve-2025-53770-vulnerable-scanner
Python script to scan SharePoint hosts for CVE-2025-53770 using custom payloads, with optional Burp Suite proxy interception for traffic analysis and…
 hahwul/webhackersweapons
⚔️ Web Hacker's Weapons / A collection of cool tools used by Web hackers. Happy hacking , Happy bug-hunting