reDOM
A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…

A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…

Powerful framework for rogue access point attack.

Flask-like routing framework for mitmproxy to intercept, modify, and spoof HTTP requests/responses. Enables rapid development of MITM scripts for…

Burp Extension for collaboration in Faraday

Mirror moved — see GitHub and Codeberg

An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.

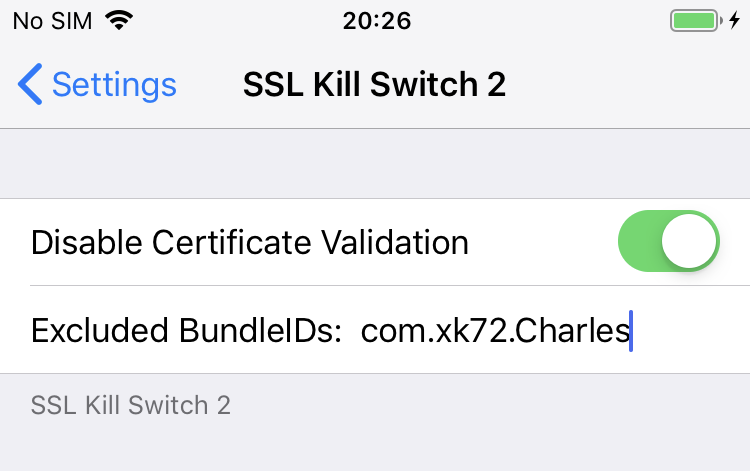
Blackbox tool to disable SSL certificate validation - including certificate pinning - within iOS and macOS applications.

Lightweight web proxy for intercepting, inspecting, and modifying HTTP traffic to audit web applications during penetration testing and bug bounty…

Tunneling data over webrtc to bypass censorship

Evilgrade is a modular framework that allows the user to take advantage of poor upgrade implementations by injecting fake updates.

Automated HTTP Request Repeating With Burp Suite

Ratched is a transparent Man-in-the-Middle TLS proxy intended for penetration testing

:package: The fastest and simplest packet manipulation lib for Python

Stop getting 403 Forbidden. A specialized httpx-like toolkit for WAF evasion.

REST API automation for Burp Suite Community Edition. Drop-in Java extension exposing send/repeat/history endpoints over a local HTTP API.

Zap Extension for collaboration in Faraday

DEPRECATED, bettercap developement moved here: https://github.com/bettercap/bettercap

Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…