

redknife
 yukibtc/redknife
A Swiss Army knife for offensive security.
command-and-controlinformation-gatheringpenetration-testing+4
yukibtc/redknifeA Swiss Army knife for offensive security.
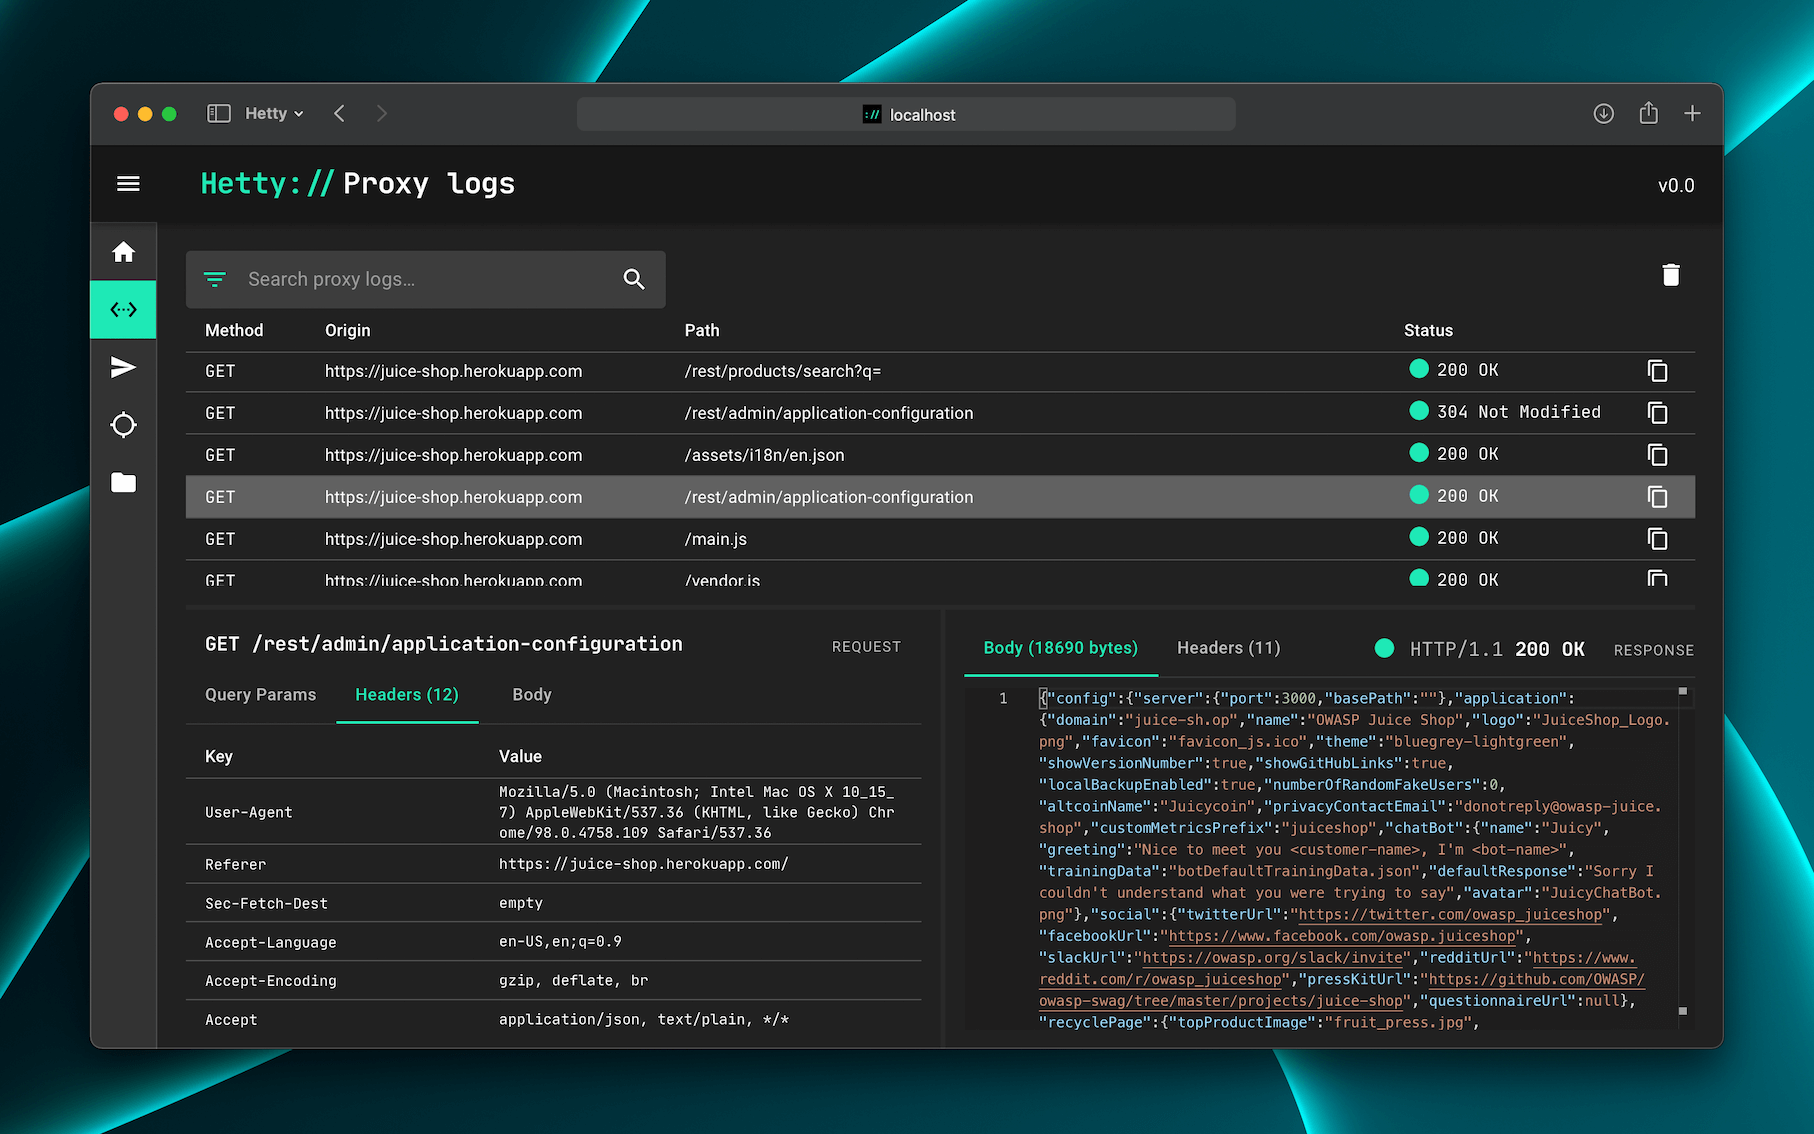
 dstotijn/hetty
An HTTP toolkit for security research.
 caido/caido
Lightweight web proxy for intercepting, inspecting, and modifying HTTP traffic to audit web applications during penetration testing and bug bounty…
 secforce/tunna
Tunna is a set of tools which will wrap and tunnel any TCP communication over HTTP. It can be used to bypass network restrictions in fully firewalled…
 t3l3machus/pentest-pivoting
A compact guide to network pivoting for penetration testings / CTF challenges.
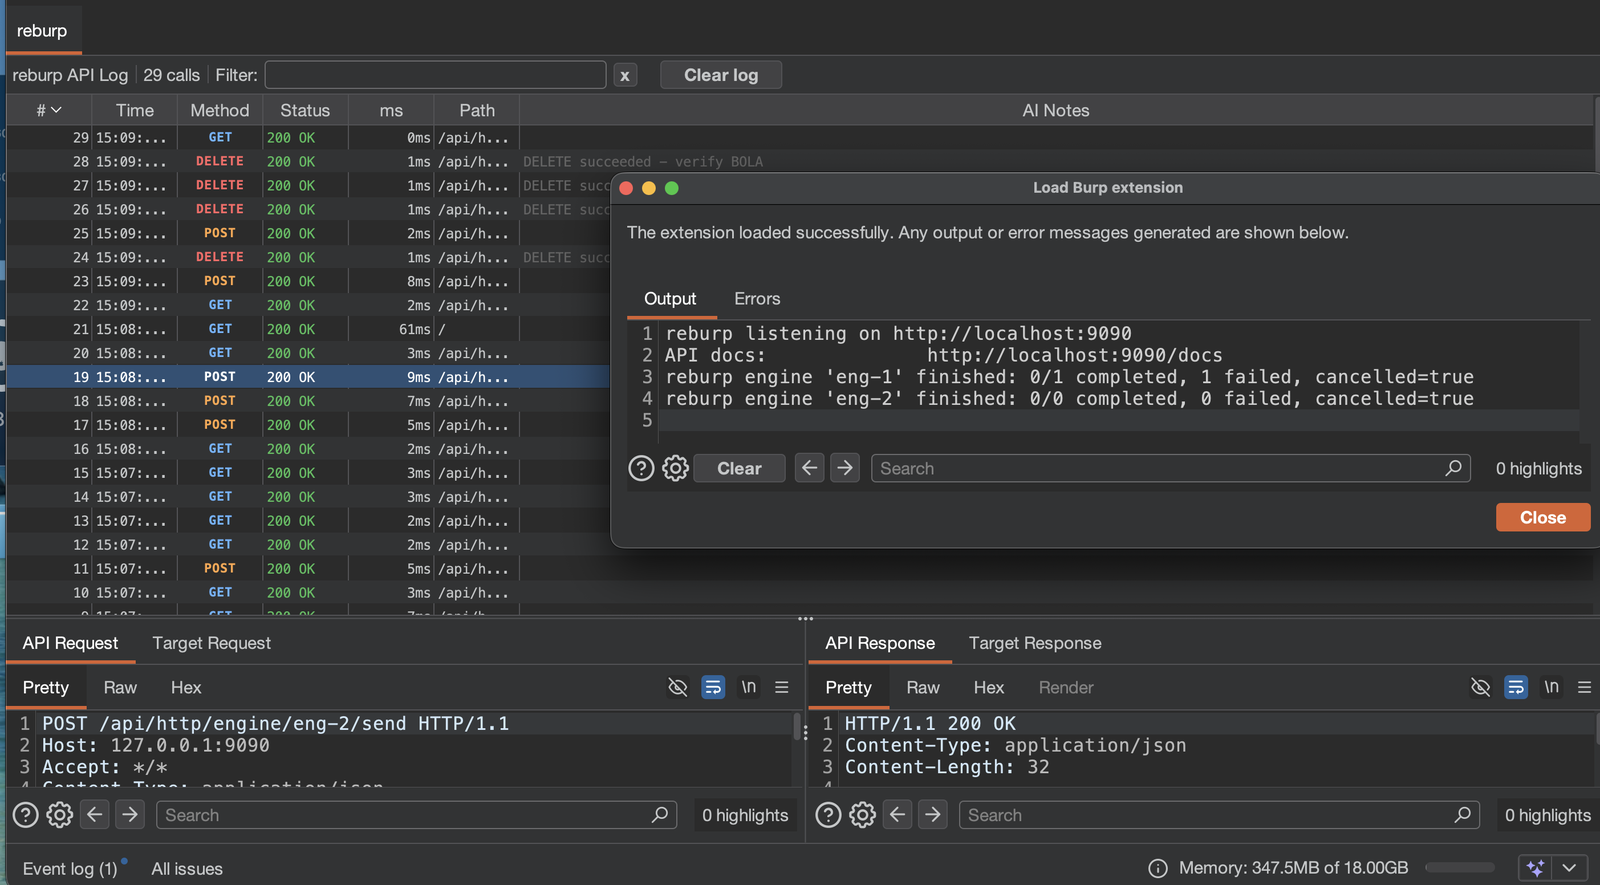 forefy/reburp
A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
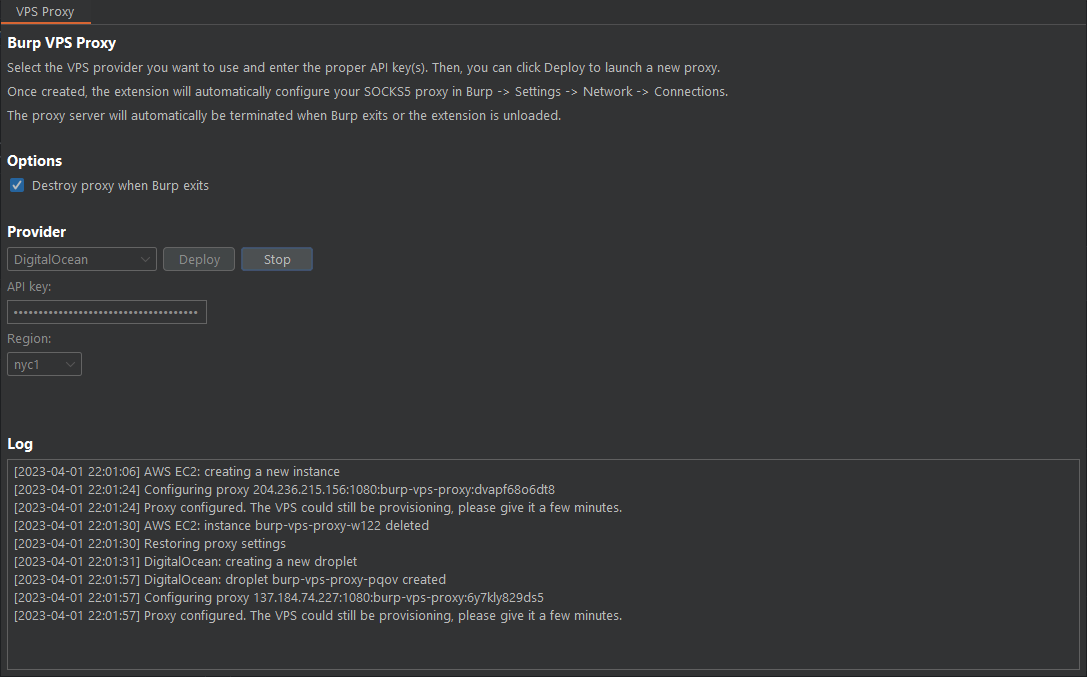 d3mondev/burp-vps-proxy
This Burp Suite extension allows for the automatic creation and deletion of an upstream SOCKS5 proxy on popular cloud services.
 v1v1/sleight
Empire HTTP(S) C2 redirector setup script
 bishopfox/ca-clone
Scripts to clone CA certificates for use in HTTPS client attacks.
 infobyte/faraday_burp
Burp Extension for collaboration in Faraday
 ericmtzmtz/pwnproxy
An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.
 infobyte/faraday_zap
Zap Extension for collaboration in Faraday
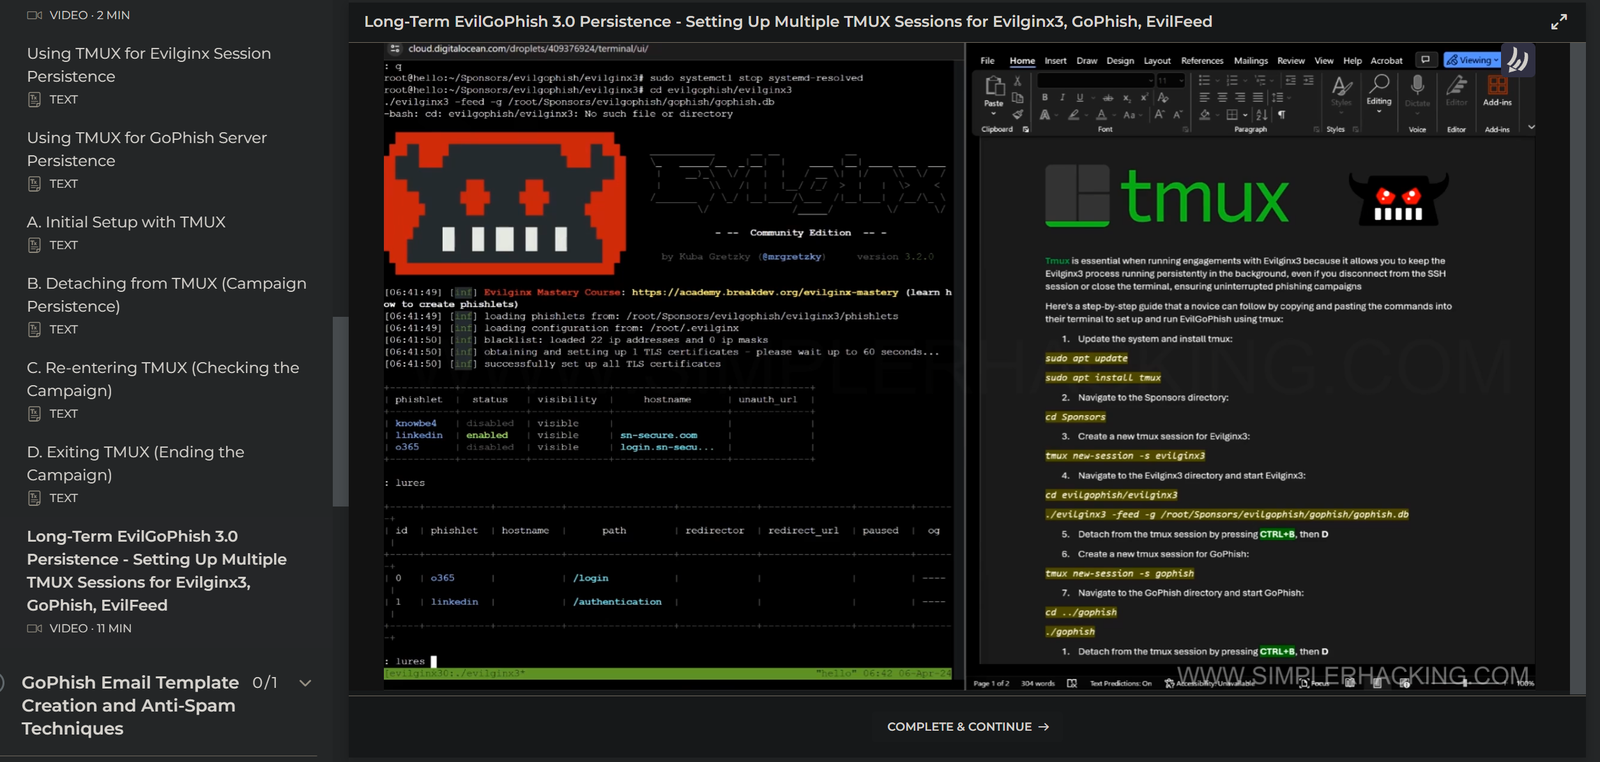 simplerhacking/evilginx3-phishlets
This repository provides penetration testers and red teams with an extensive collection of dynamic phishing templates designed specifically for use…
 1ultimat3/badintent
Intercept, modify, repeat and attack Android's Binder transactions using Burp Suite
 xdavidhu/langhost
👻 A LAN dropbox chatbot controllable via Telegram
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and pentesting toolkit for the terminal built for humans and AI agents alike.
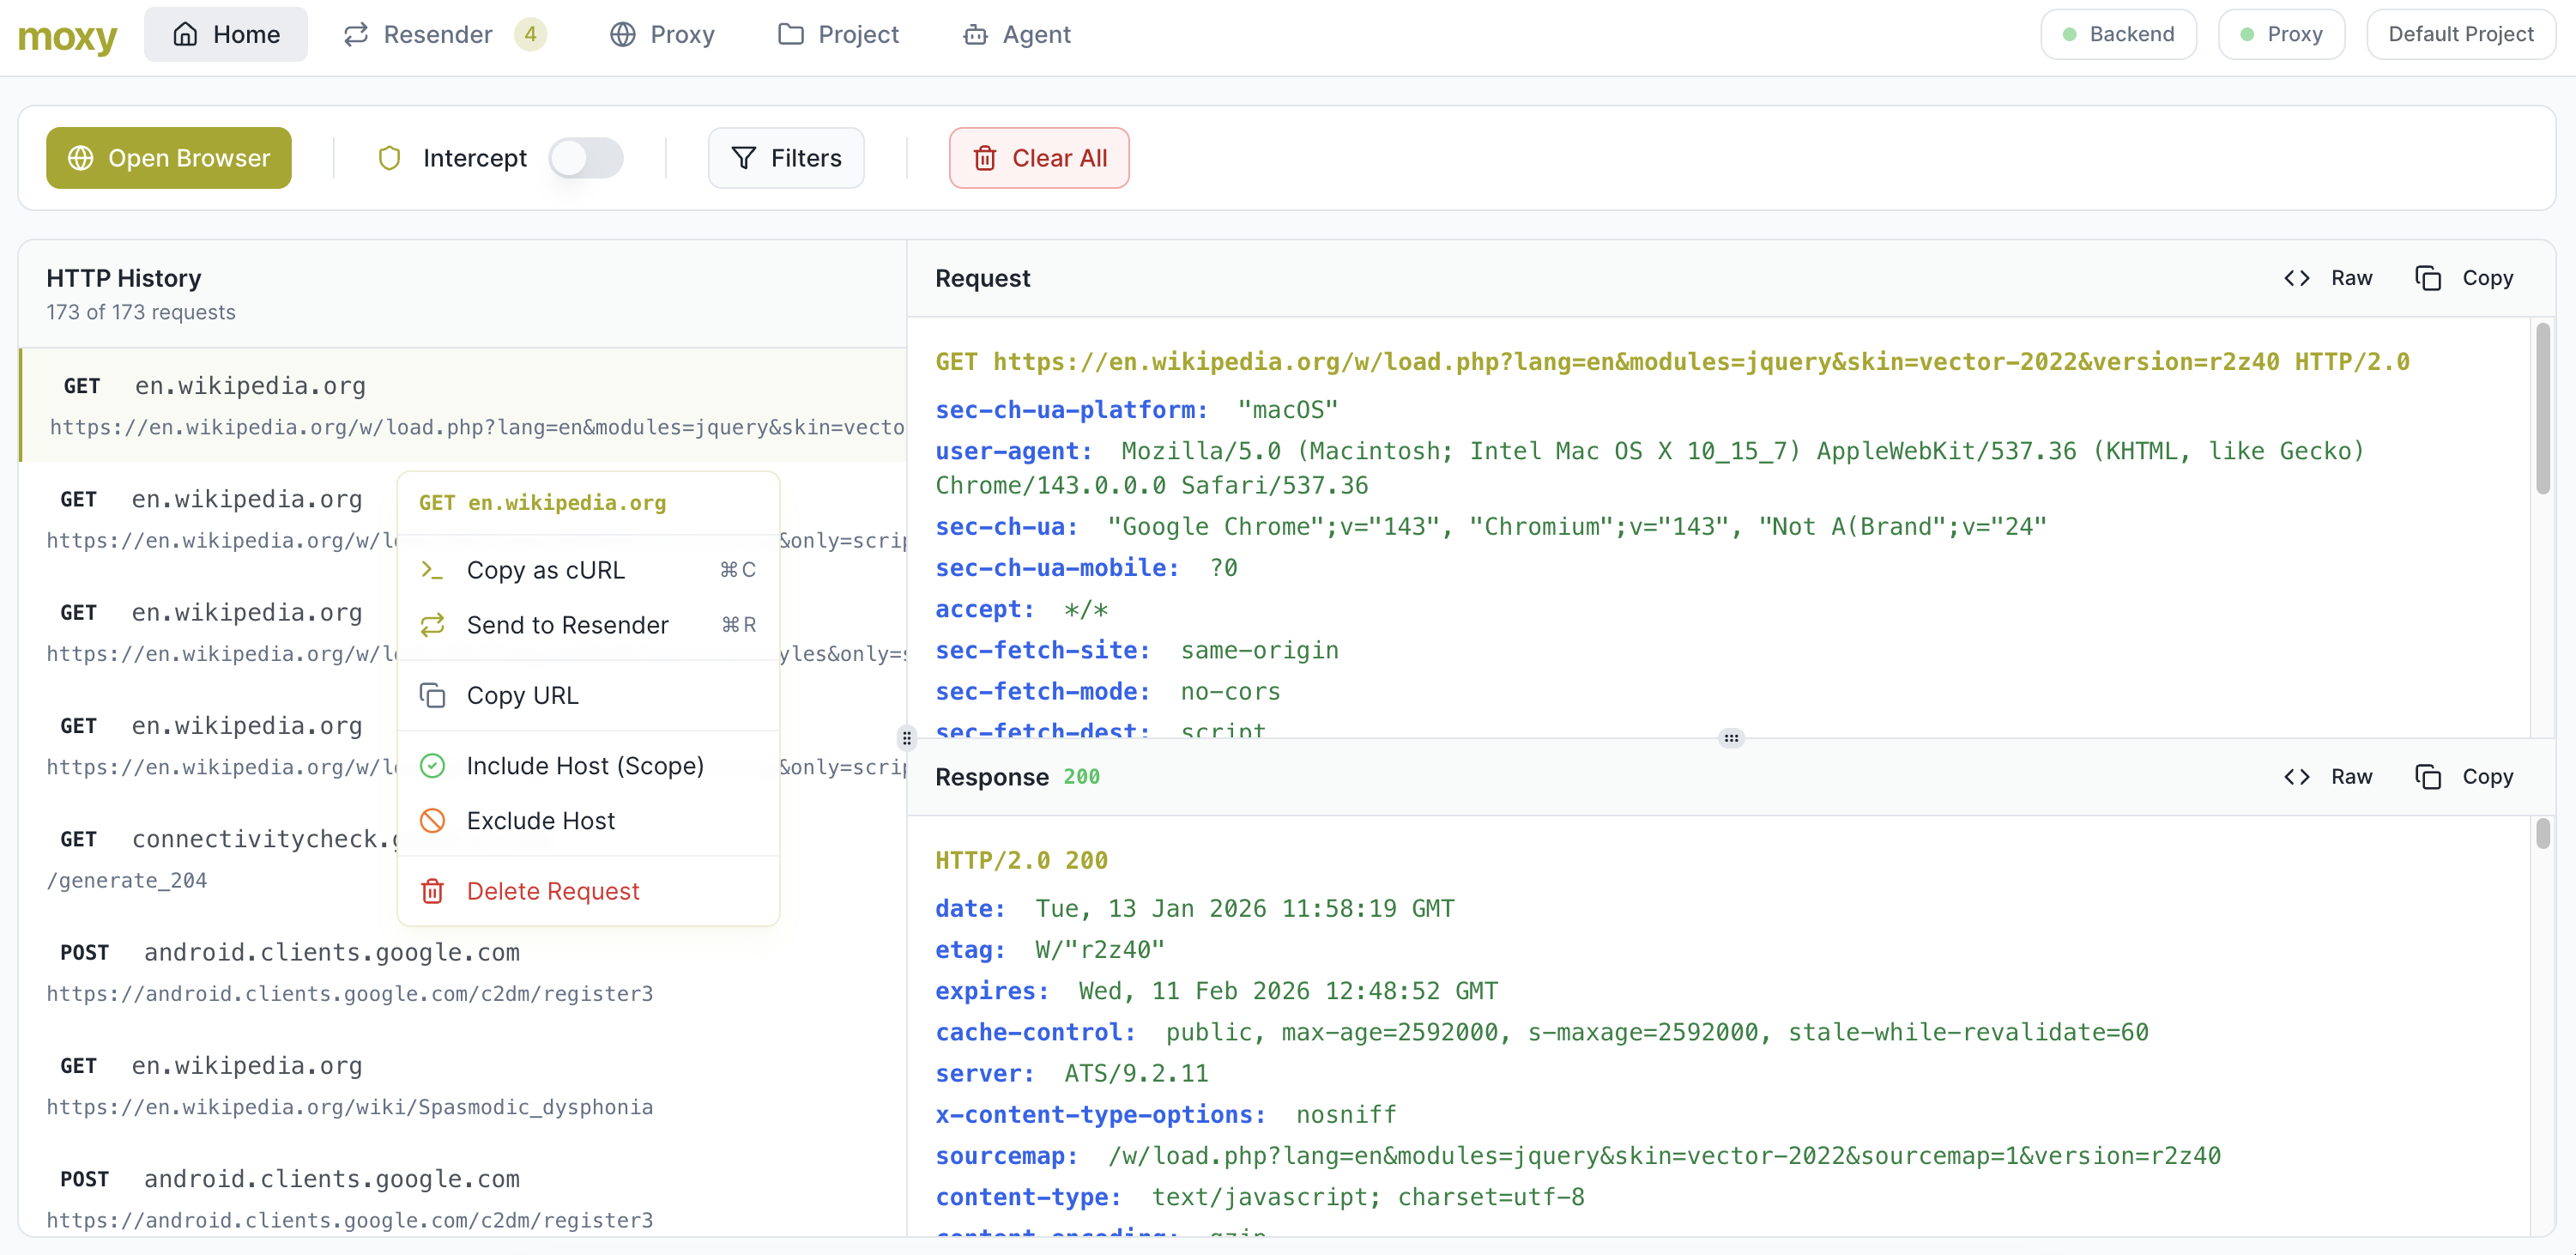 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…