
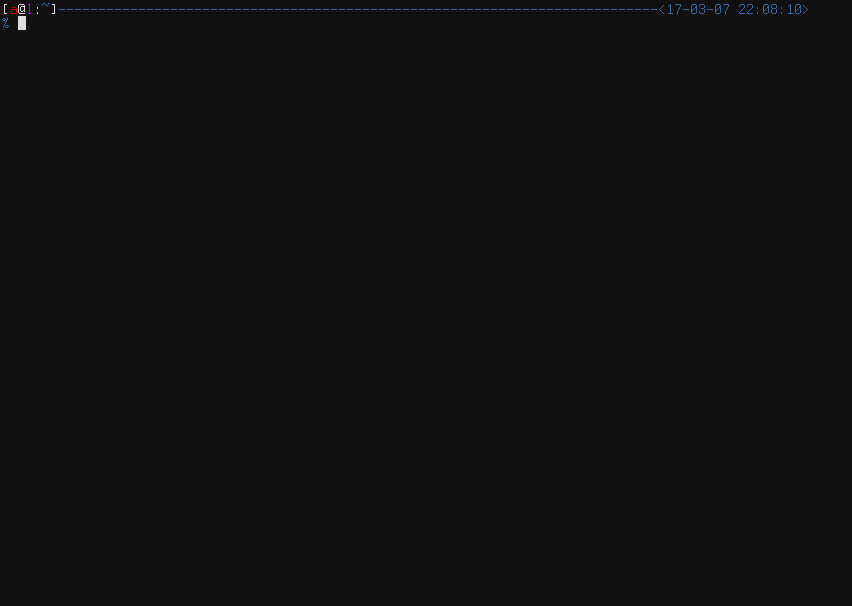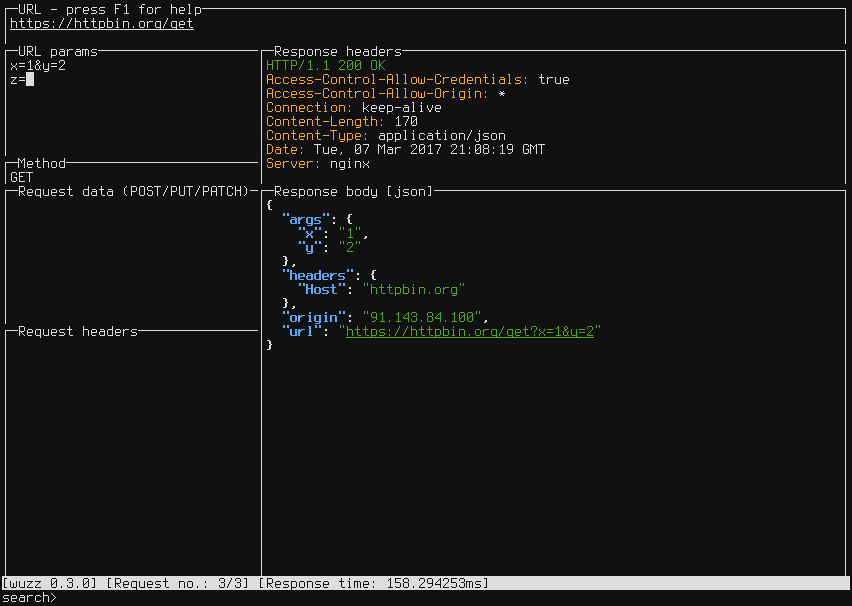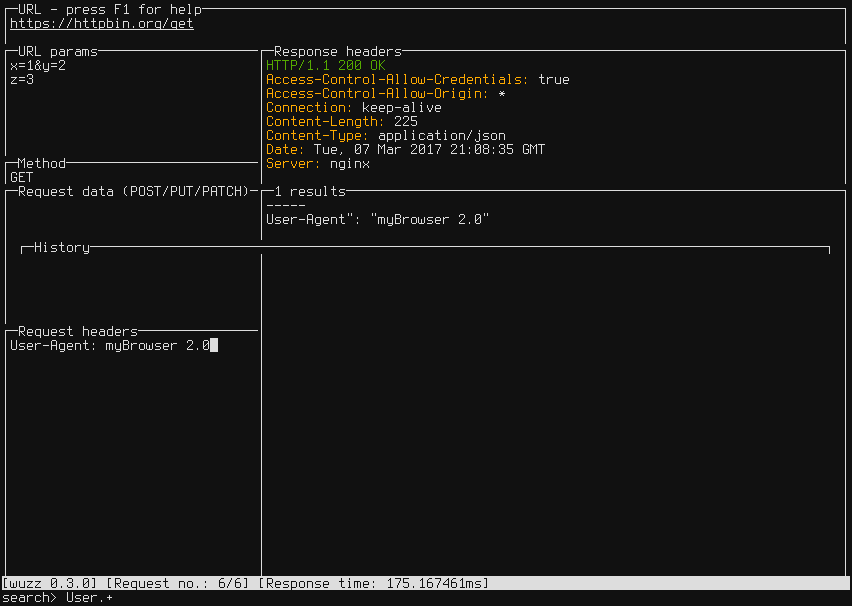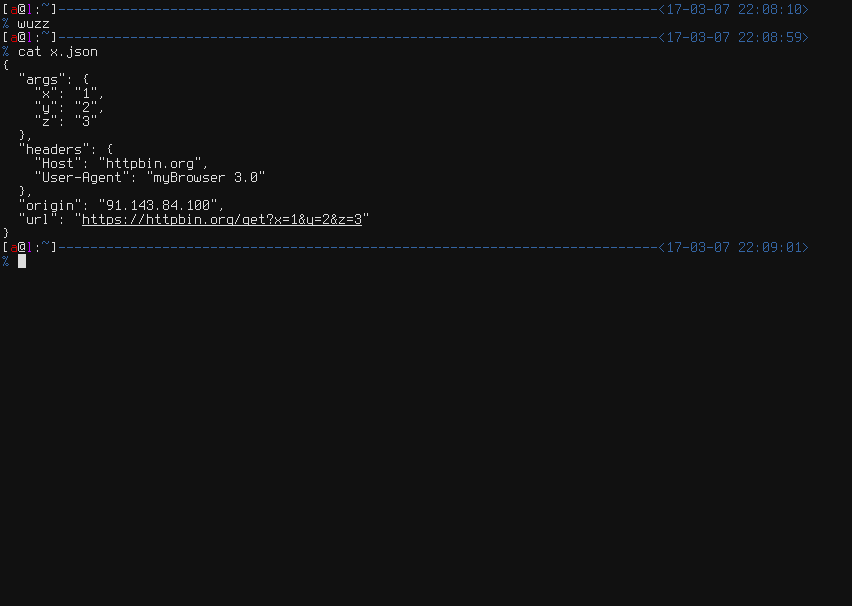
wuzz
 asciimoo/wuzz
Interactive cli tool for HTTP inspection
general-purpose-utilitiesscripting-automationweb-proxies-interception
asciimoo/wuzzInteractive cli tool for HTTP inspection
 spectolabs/hoverfly
Lightweight service virtualization/ API simulation / API mocking tool for developers and testers
 httptoolkit/httptoolkit
HTTP Toolkit is a beautiful & open-source tool for debugging, testing and building with HTTP(S) on Windows, Linux & Mac :tada: Open an issue here…
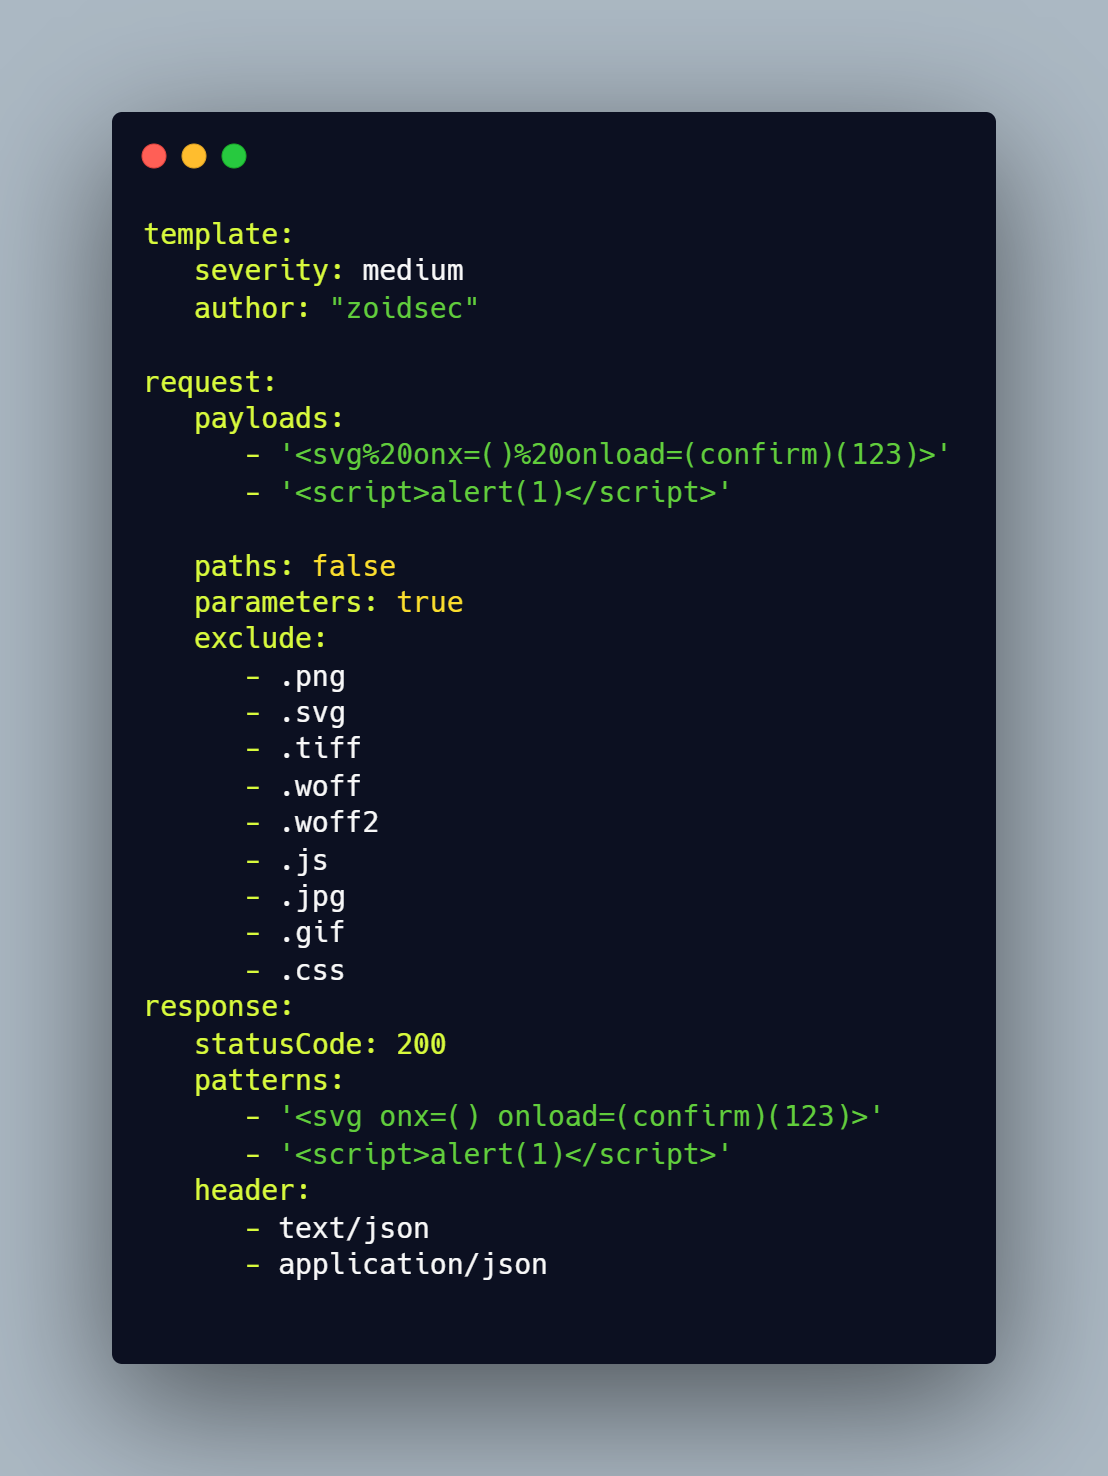 ethicalhackingplayground/erebus
Erebus is a fast tool for parameter-based vulnerability scanning using a Yaml based template engine like nuclei.
 dereeqw/web-mitm-lab
Web traffic interception simulation tool for cybersecurity research and defensive learning in isolated lab environments.
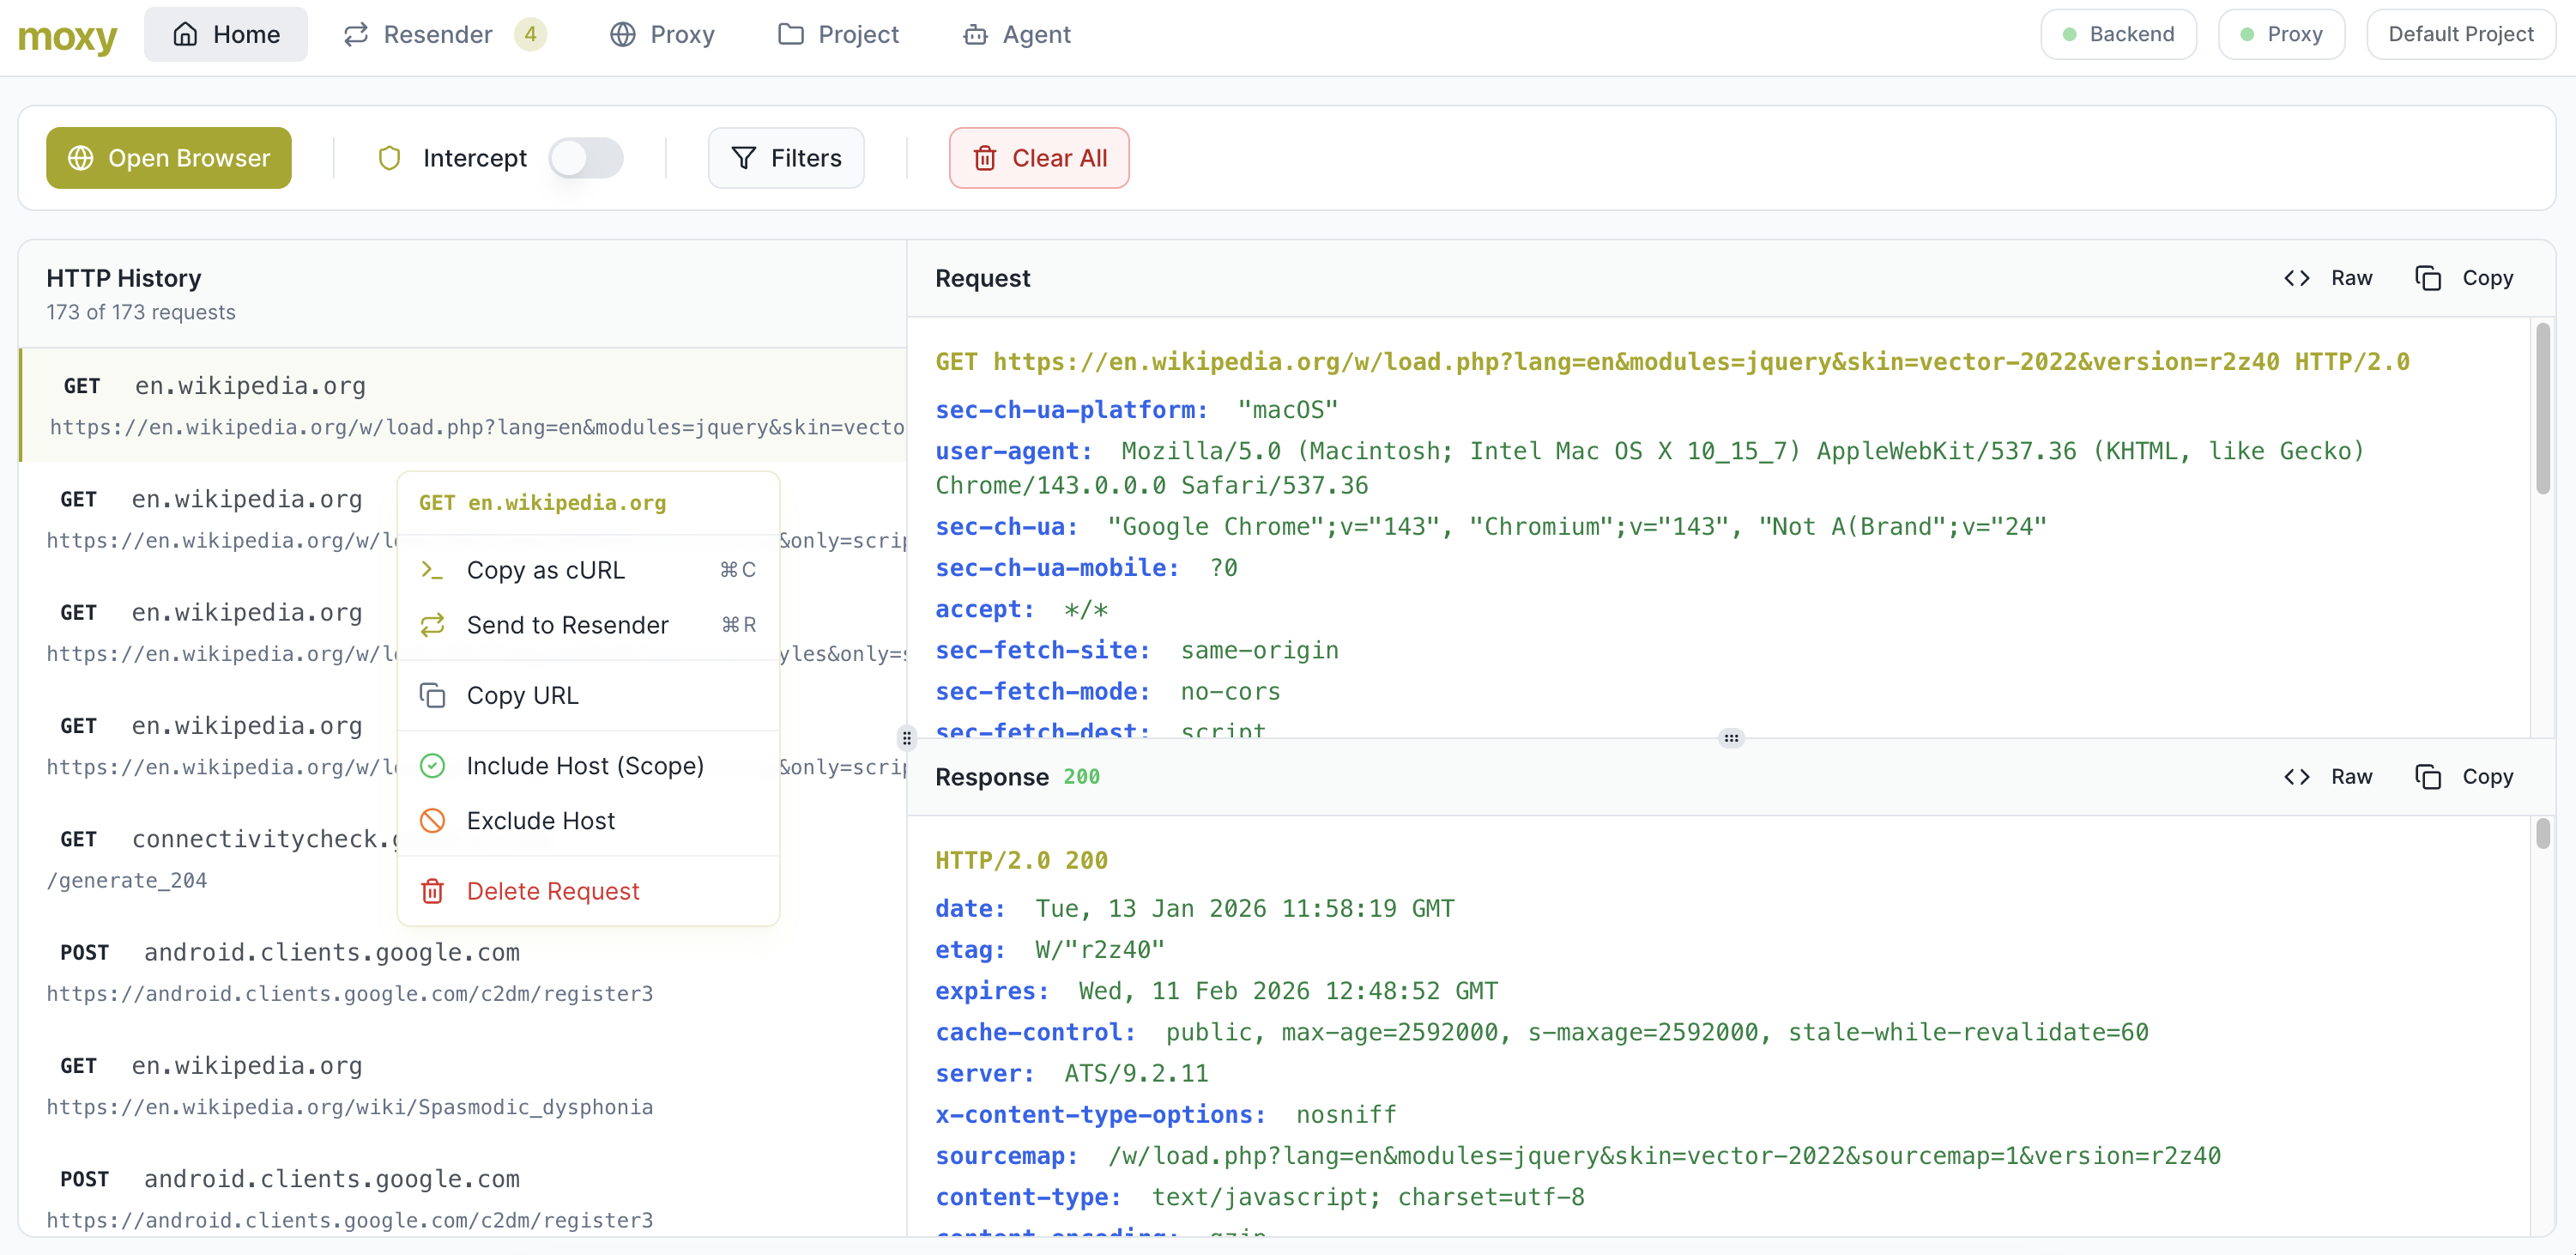 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 everywall/ladder
Selfhosted alternative to 12ft.io. and 1ft.io. Proxy to remove CORS headers and modify HTML
 nccgroup/solitude
Solitude is a privacy analysis tool that enables anyone to conduct their own privacy investigations. Whether a curious novice or a more advanced…
 zu1k/good-mitm
Rule-based MITM engine. Rewriting, redirecting and rejecting on HTTP(S) requests and responses, supports JavaScript rule.
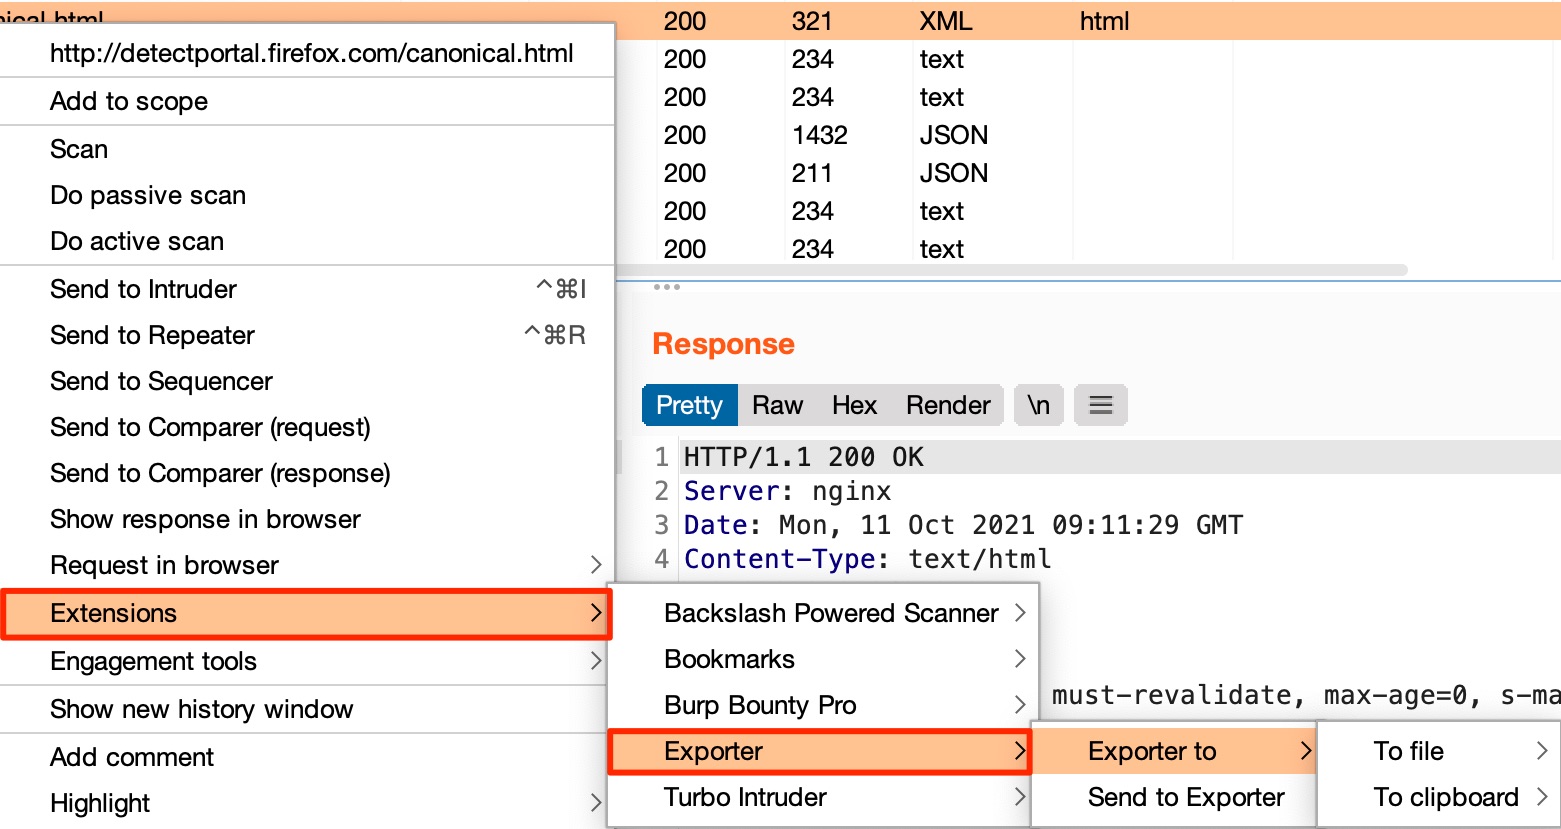 artssec/burp-exporter
Exporter is a Burp Suite extension to copy a request to a file or the clipboard as multiple programming languages functions.
 0xbartita/cookie-swapper
Burp Suite extension that auto-replaces cookies and headers in requests using configurable rules. Eliminates manual copy-pasting of session tokens…
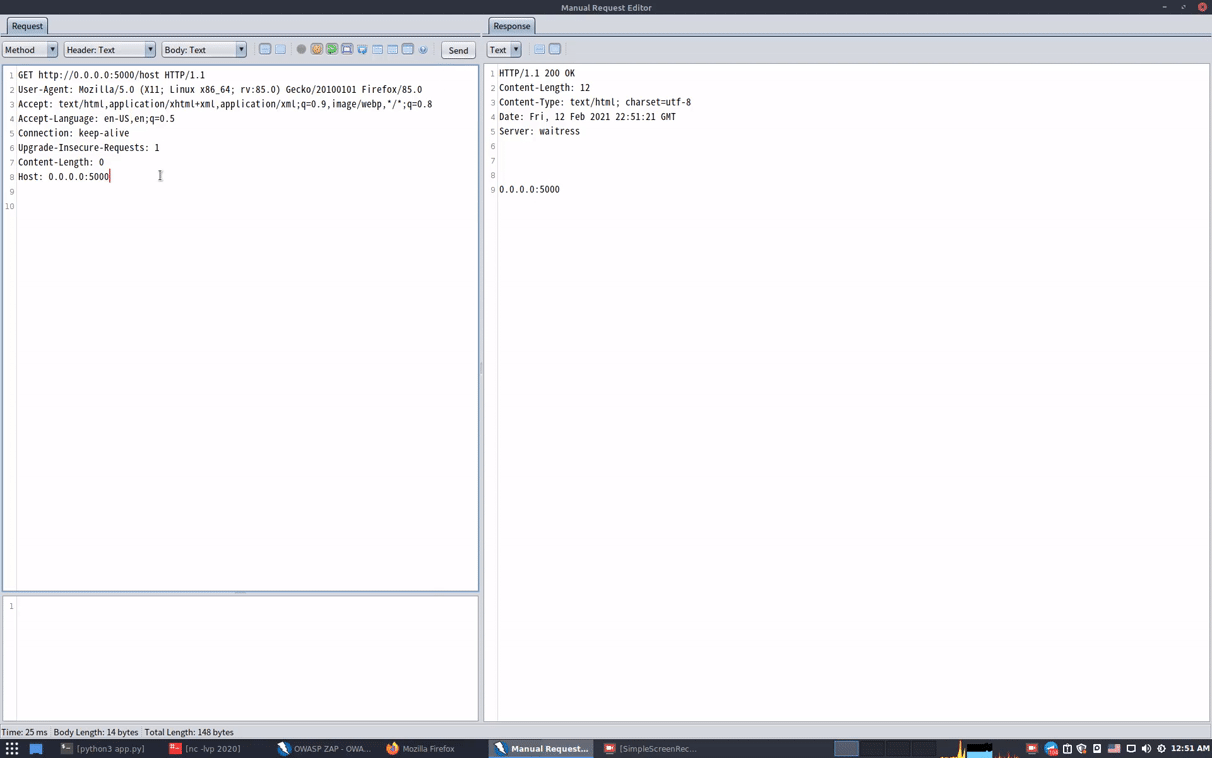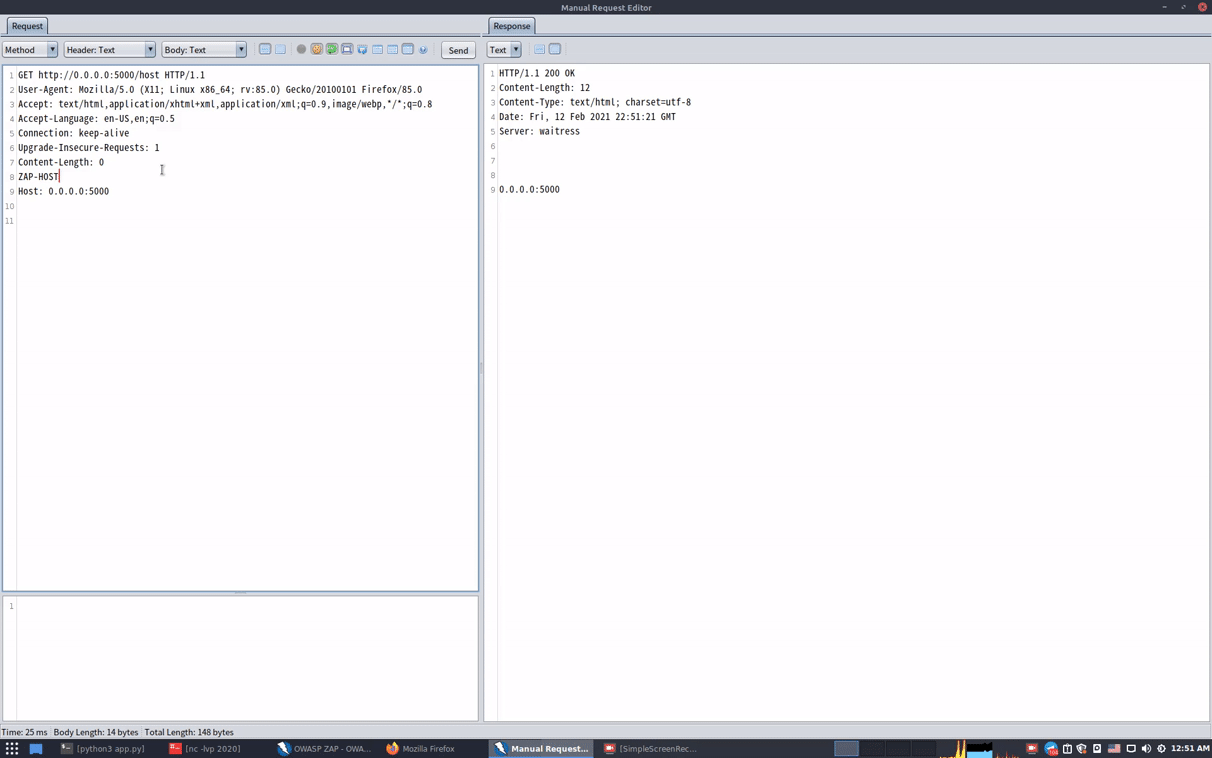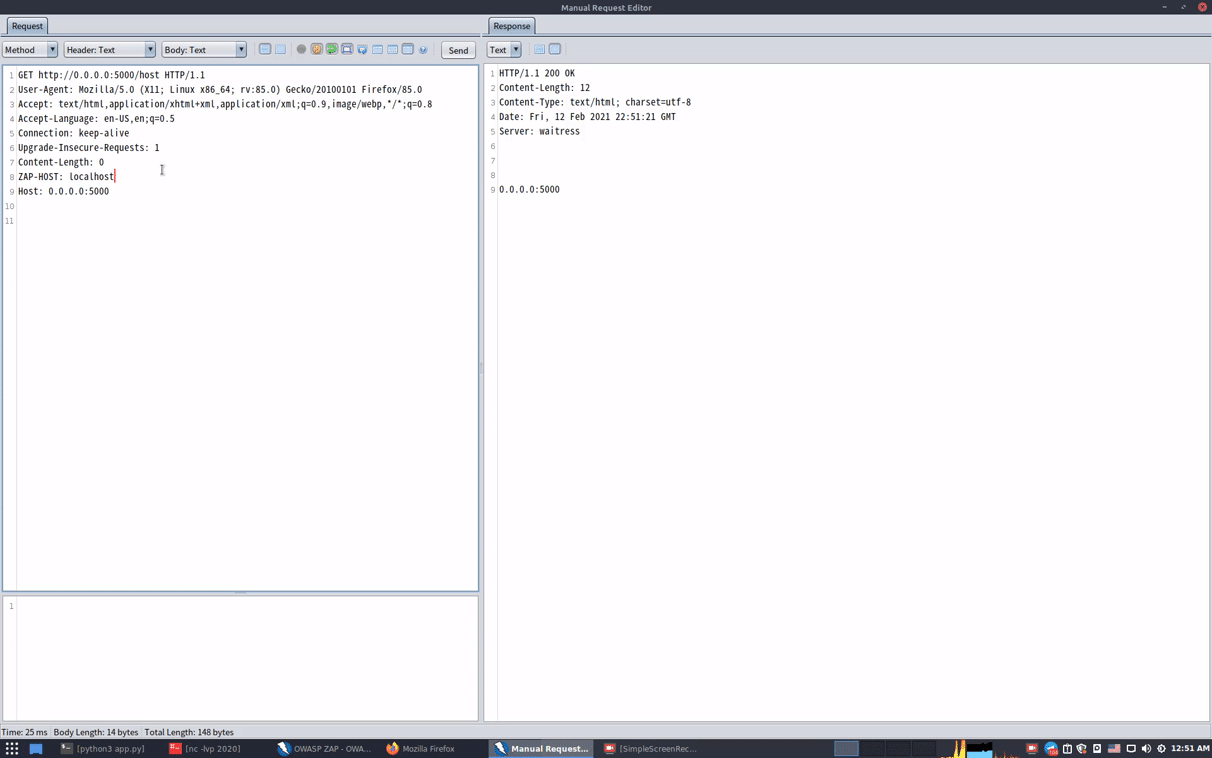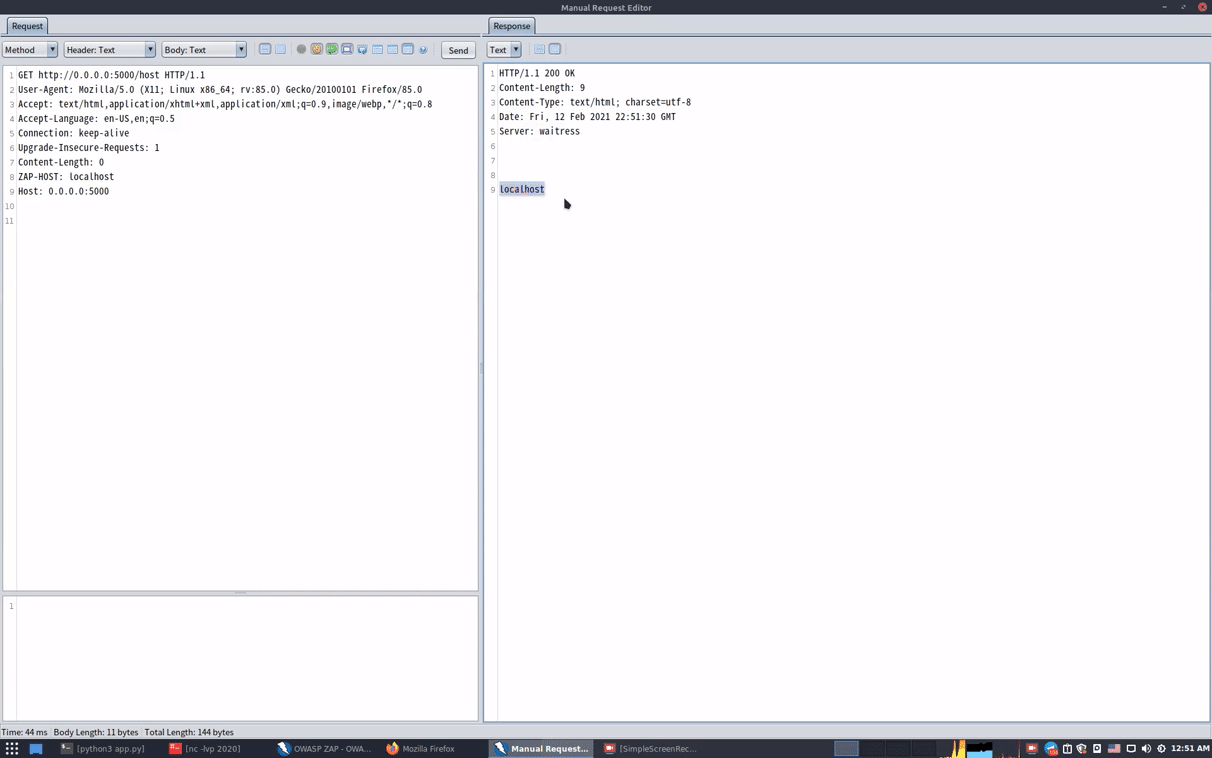 mindpatch/zaphoster
Fix host header error in zaproxy
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
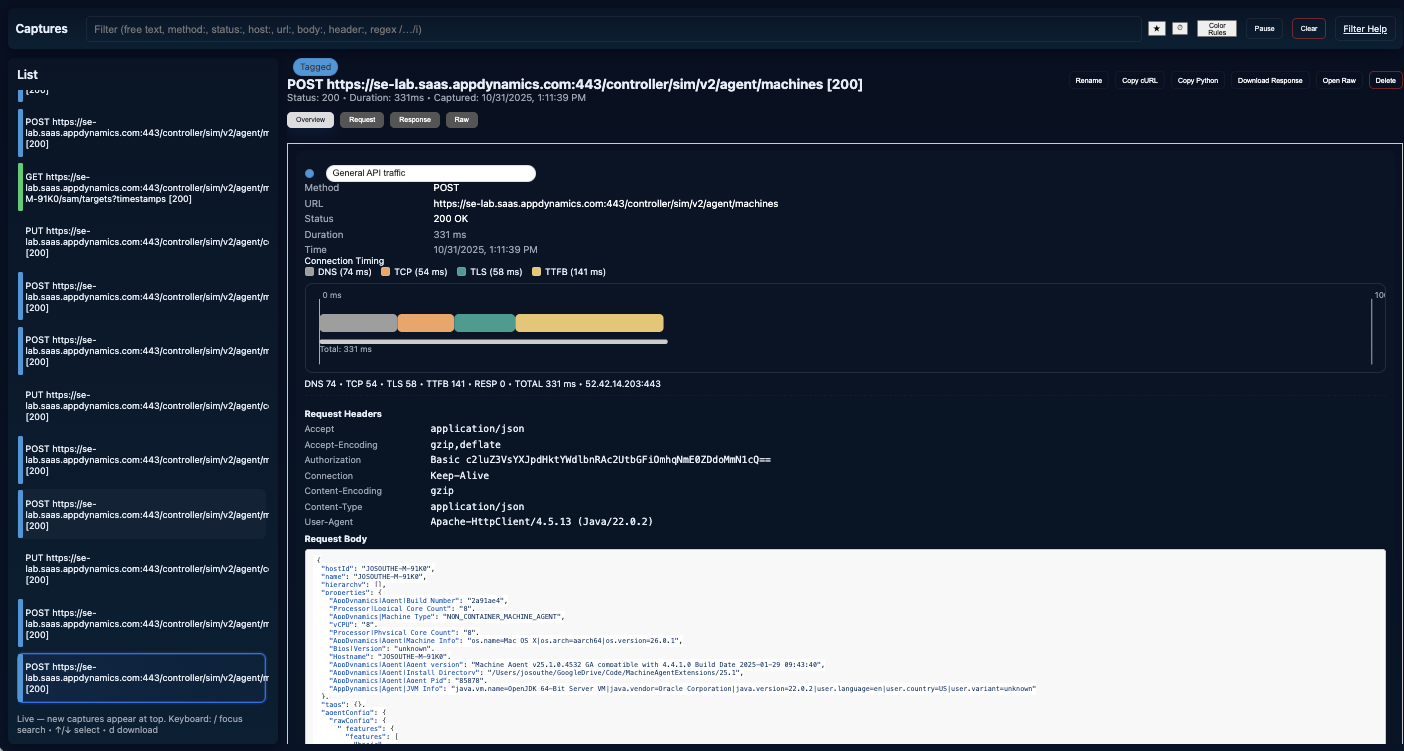 jbsouthe/http-breakout-proxy
HTTP Proxy Analysis for reverse engineering protocol communication
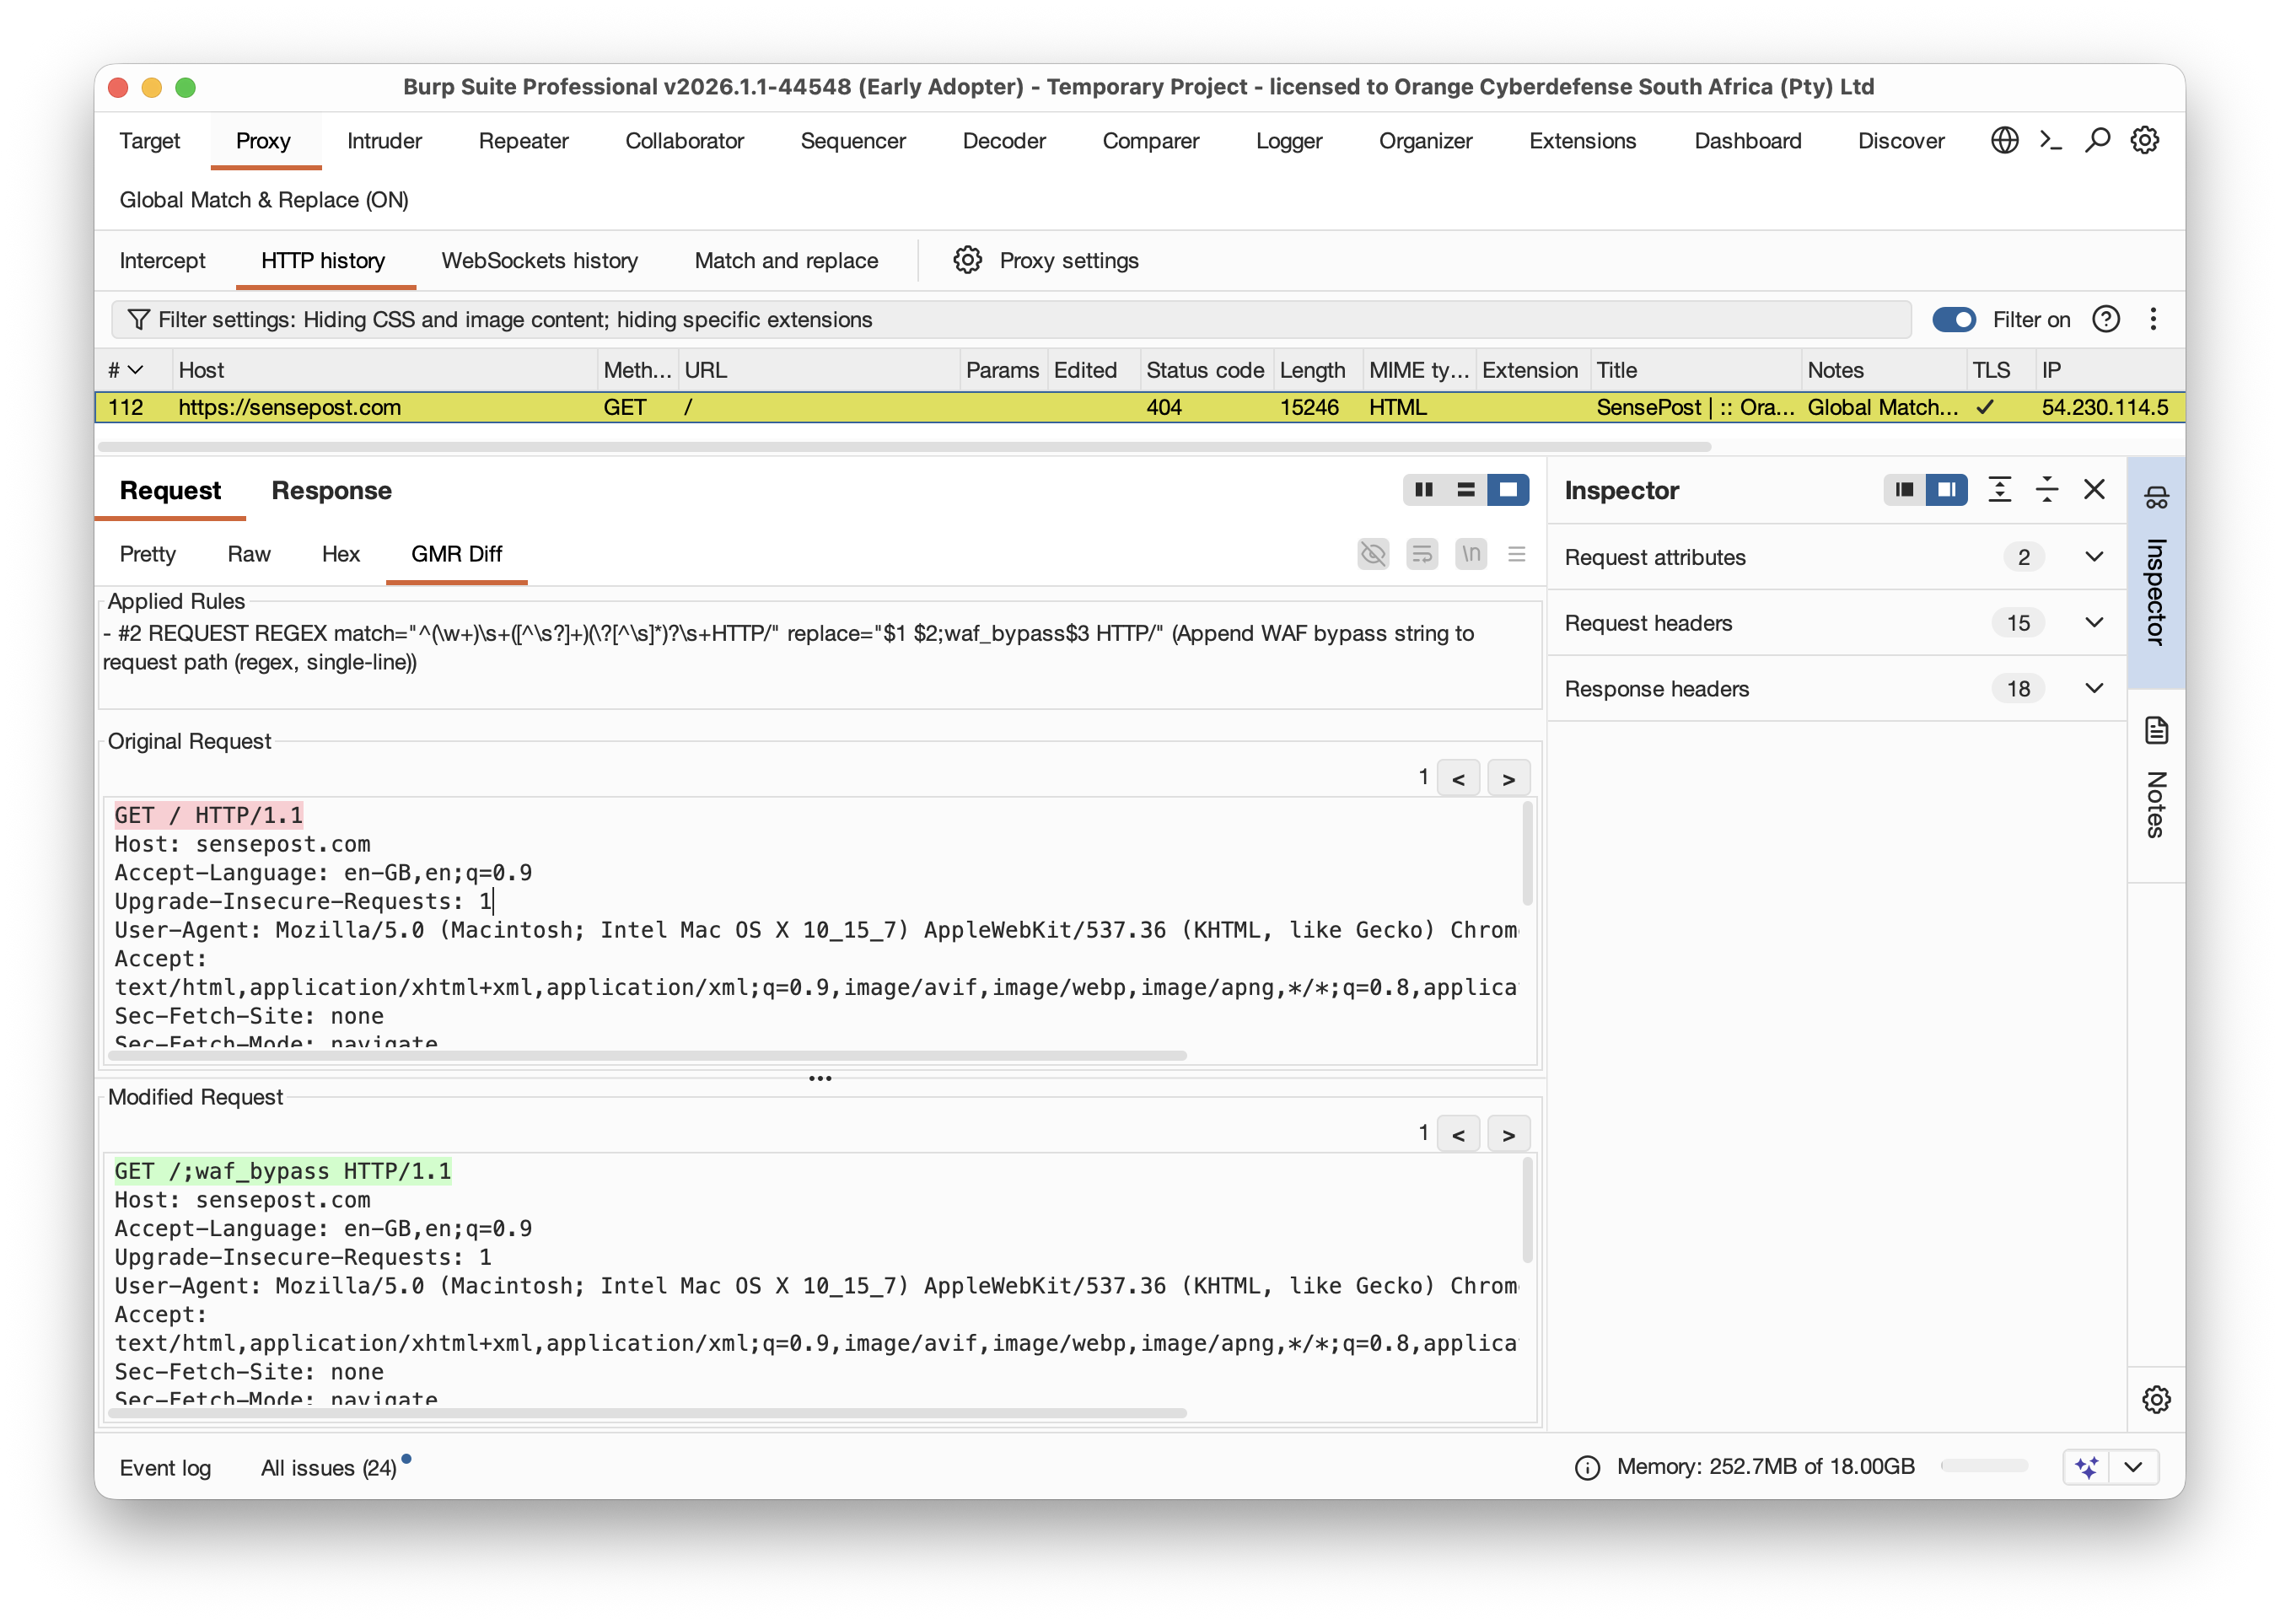 singe/burp_global_match_replace
Match & Replace rules for Portswigger's Burp that operate globally across all utilities.
 cappricio-securities/burpflow
BurpFlow is one of the best Burp Suite automation tools for bug bounty hunters and penetration testers, widely used to load recon data via proxy and…

 yukibtc/redknife
A Swiss Army knife for offensive security.
 caido/caido
Lightweight web proxy for intercepting, inspecting, and modifying HTTP traffic to audit web applications during penetration testing and bug bounty…