

faraday_burp
 infobyte/faraday_burp
Burp Extension for collaboration in Faraday
api-security-testingdevsecopspenetration-testing+3
infobyte/faraday_burpBurp Extension for collaboration in Faraday
 pentagridsec/pentagridresponseoverview
Response Overview Extension for BurpSuite - Find exotic responses by grouping response bodies
 t0xodile-swig/http3-adapter
Burp Suite extension that intercepts requests and sends them over HTTP/3, converting responses back for Burp, with support for kettled requests and…
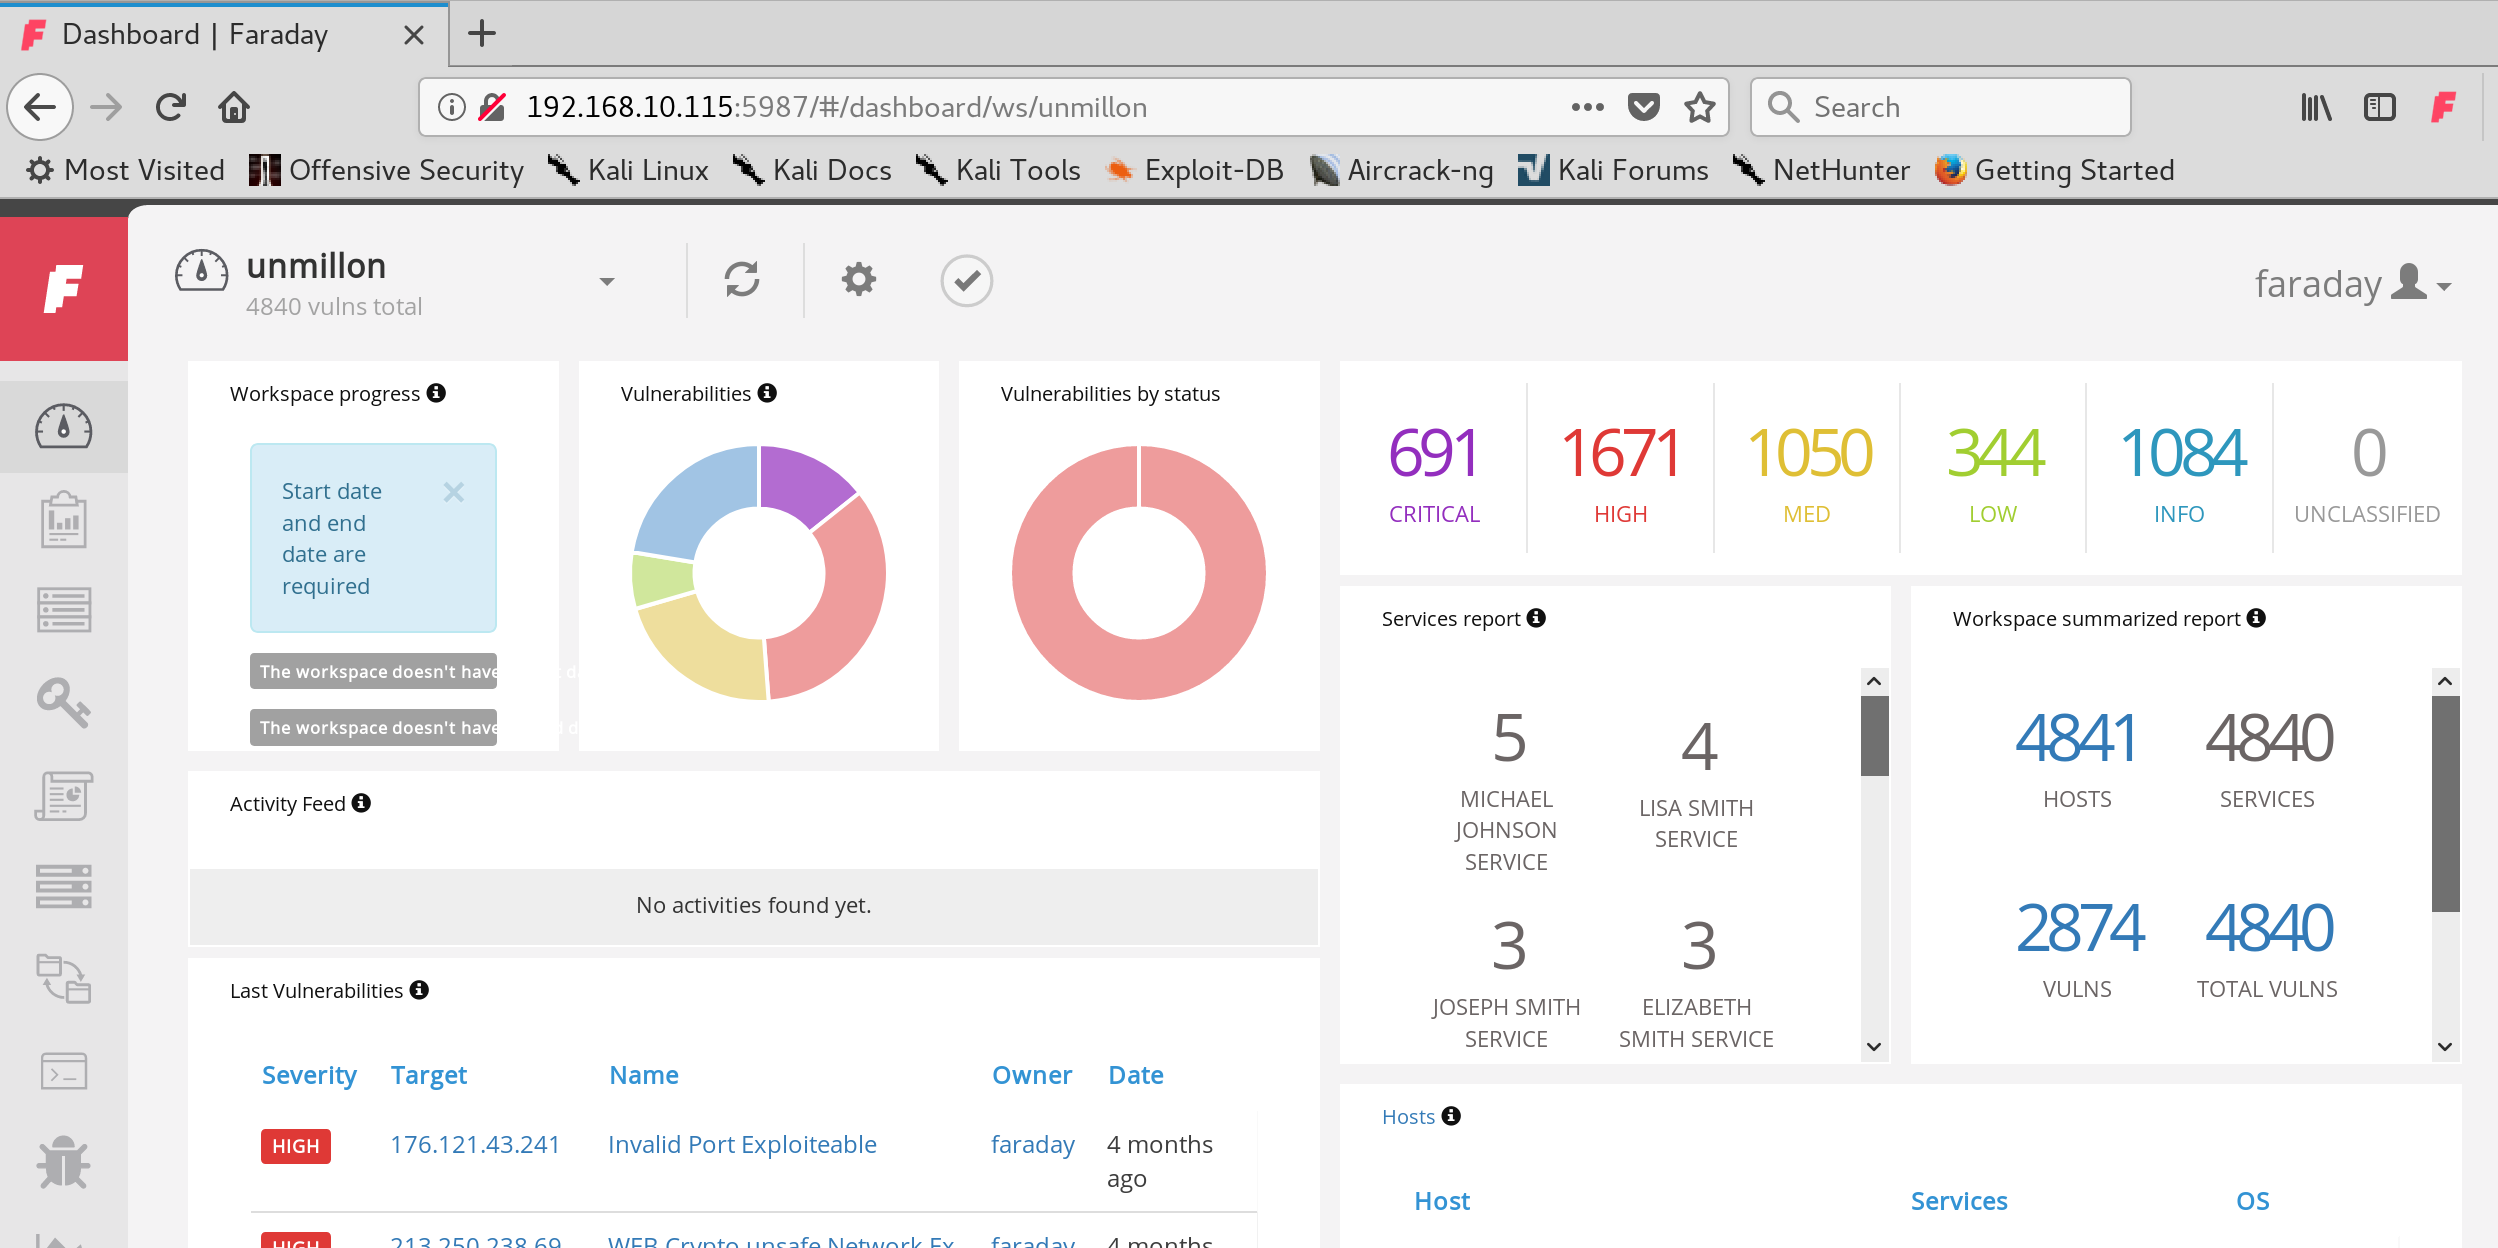 infobyte/faraday_addon
A browser extension for faradaysec platform https://faradaysec.com
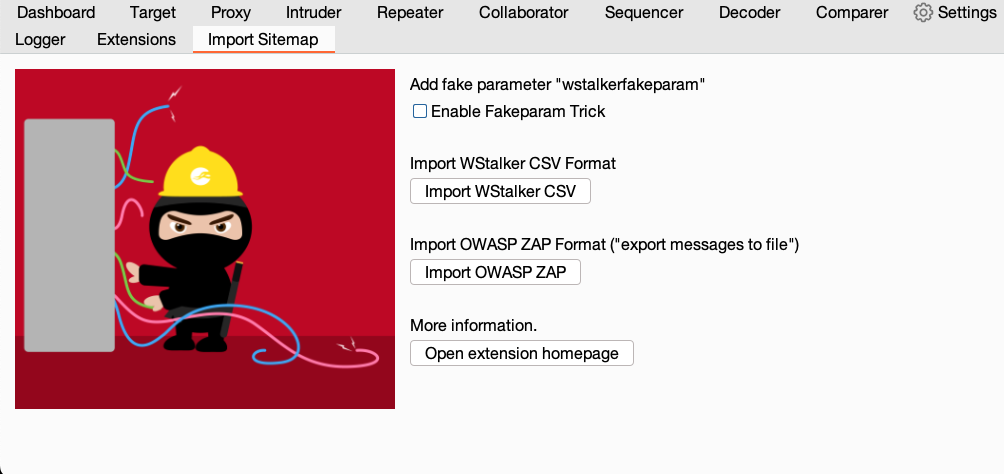 nccgroup/burpimportsitemap
Import To Sitemap is a Burp Suite Extension to import wstalker CSV file or ZAP export file into Burp Sitemap
 larrypeseckis/burp-cc-bridge
REST API automation for Burp Suite Community Edition. Drop-in Java extension exposing send/repeat/history endpoints over a local HTTP API.
 0xbartita/cookie-swapper
Burp Suite extension that auto-replaces cookies and headers in requests using configurable rules. Eliminates manual copy-pasting of session tokens…
 hemp3l/cve-2017-6640-poc
Proof of concept for CVE-2017-6640 as burp extension
 infobyte/faraday_zap
Zap Extension for collaboration in Faraday
 ottimo/burp-alfresco-referer-proxy-cve-2014-9301
Burp Suite extension exploiting CVE-2014-9301 in Alfresco Referer Proxy for targeted web application penetration testing.
 federicodotta/brida
The new bridge between Burp Suite and Frida!
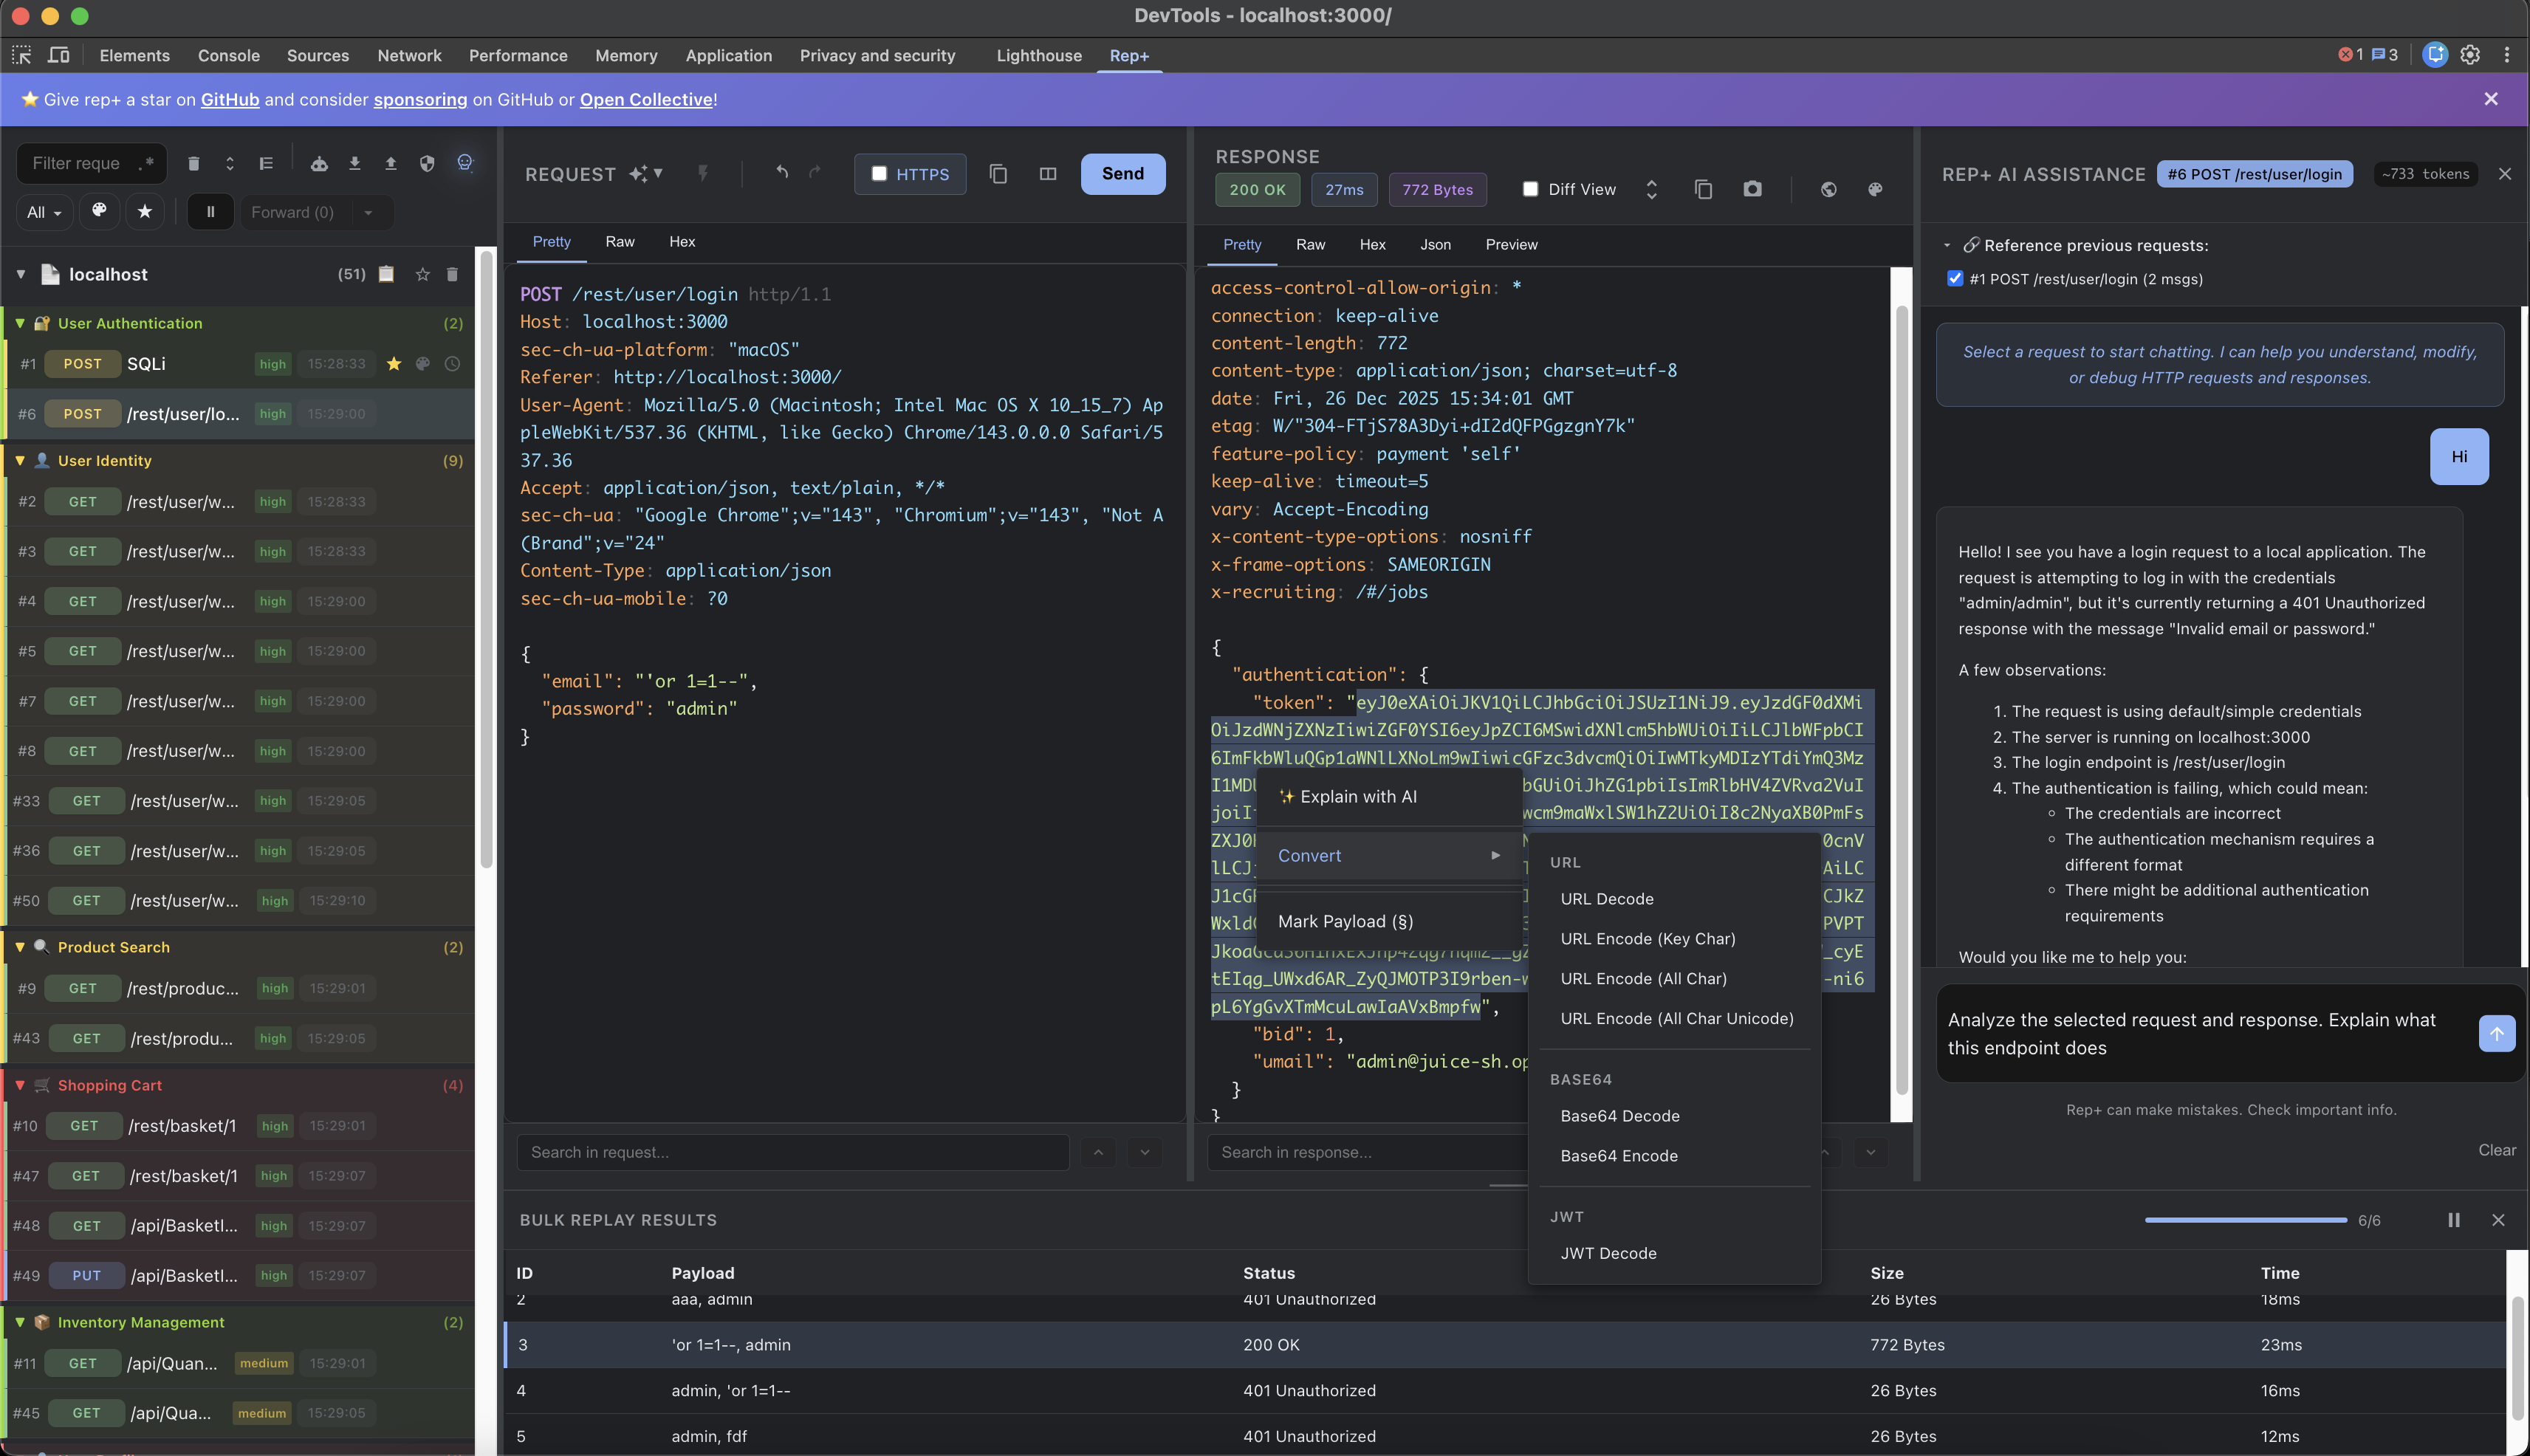 repplus/rep-chrome
rep+ — Burp-style HTTP Repeater for Chrome DevTools with built‑in AI to explain requests and suggest attacks
 portswigger/burp-extensions-montoya-api-examples
Sample Burp Suite extensions demonstrating the Montoya API, covering HTTP and proxy handlers, custom scan checks, Intruder payloads, WebSocket…
 xnl-h4ck3r/auto-repeater
Automated HTTP Request Repeating With Burp Suite
 modzero/burp-responseclusterer
Burp plugin that clusters responses to show an overview of received responses
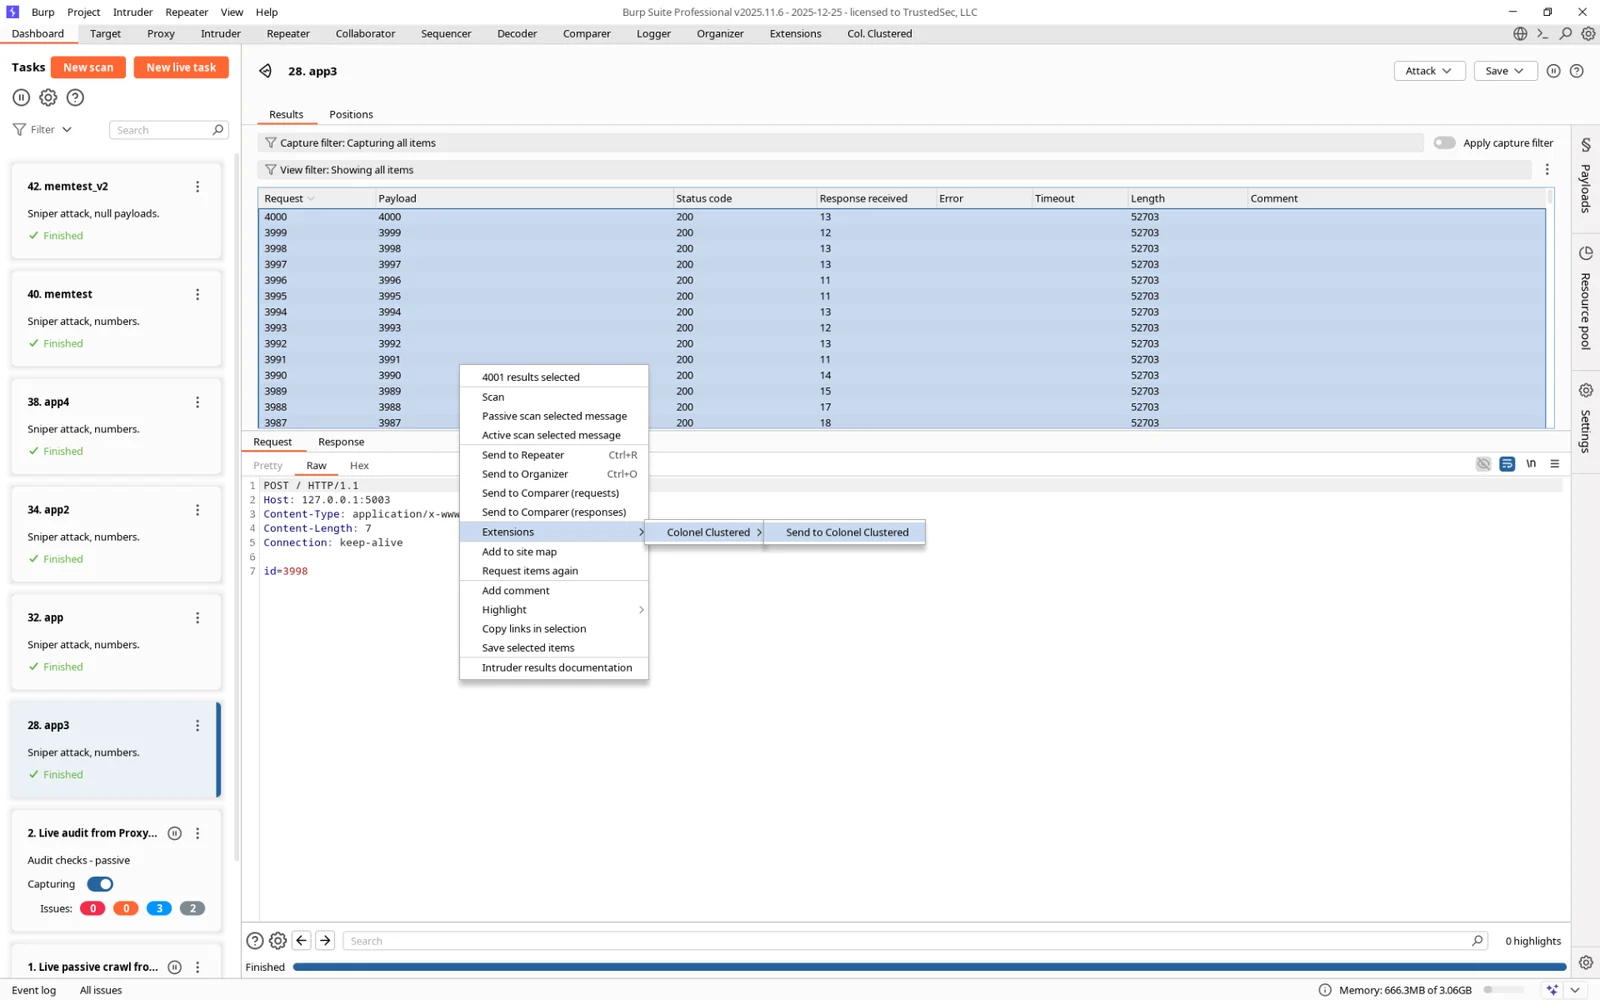 hoodoer/colonelclustered
A Java Burp Plugin that performs text clustering on responses to identify outliers/groups based on the actual content of the server responses, say…
 hackwarts12/burp-recordadora
Persists BurpSuite proxy history, Repeater requests, and Intruder payloads across sessions; exports and imports .log files for web pentesting context.
 zu1k/good-mitm
Rule-based MITM engine. Rewriting, redirecting and rejecting on HTTP(S) requests and responses, supports JavaScript rule.