CVE-2024-20767-Adobe-ColdFusion

PoC exploit for CVE-2024-20767 in Adobe ColdFusion, leveraging an improper access control flaw to read arbitrary files from affected servers.

PoC exploit for CVE-2024-20767 in Adobe ColdFusion, leveraging an improper access control flaw to read arbitrary files from affected servers.

Root-Level RCE via OS Command Injection in Ivanti Sentry

A modern vulnerable web app

Android 3.0 through 4.1.x on Disney Mobile, eAccess, KDDI, NTT DOCOMO, SoftBank, and other devices does not properly implement the WebView class,…


Proof-of-concept exploit for CVE-2020-11990 targeting Apache Cordova applications, demonstrating a remote code execution vulnerability in the mobile…

This is a Automated Generate Payload for CVE-2019-11932 (WhatsApp Remote Code Execution)

WebKit NavigateEvent.canIntercept SOP bypass via cross-port interception — iOS 26.3.1 BSI (CVE-2026-20643)

Proof of concept for CVE-2022-1364 against Alibaba's UC Browser

Local Root vulnerability- CVE-2019-13272 / Security Bypass Vulnerability – CVE-2019-14287/Google Android - 'Stagefright' Remote Code Execution -…

Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10

Proof-of-Concept exploit for CVE-2025-14174 (EUVD-2025-203113) - Memory corruption in ANGLE allowing out-of-bounds access and RCE in web browsers.…

Python script to generate a malicious MP4 file and start a CherryPy web server hosting a simple HTML page with the embedded file. Exploits another…

A deliberately vulnerable mobile banking application designed for practicing mobile security testing. Features common vulnerabilities found in…

Proof-of-concept for a stored cross-site scripting (XSS) vulnerability in the URVE Smart Office iOS app, with CVE details, impact analysis, and…

Pre-auth RCE exploit for Mobile Mouse 3.6.0.4 via TCP (port 9099) and WebSocket (port 35913) with Python scripts for unauthenticated command…

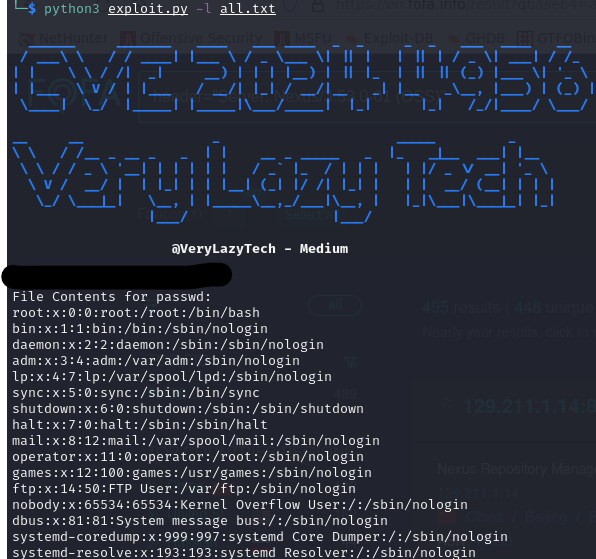
POC - CVE-2024–4956 - Nexus Repository Manager 3 Unauthenticated Path Traversal

CVE-2024-24919 Exploit and PoC - Critical LFI for Remote Access VPN or Mobile Access.