
CVE-2025-24071-POC
Proof-of-concept exploit for CVE-2025-24071, generating a malicious ZIP file that triggers NTLM hash disclosure via Windows Explorer, used with an…

Proof-of-concept exploit for CVE-2025-24071, generating a malicious ZIP file that triggers NTLM hash disclosure via Windows Explorer, used with an…

Lab environment and proof-of-concept exploit for CVE-2026-1357, a WordPress plugin vulnerability, with Docker setup and automated exploitation…

Step-by-step lab environment setup for exploiting CVE-2024-23897 in Jenkins, including Java installation, WAR file download, and execution on port…

Python-based exploit for CVE-2017-8056 targeting XML-RPC denial-of-service vulnerability in web applications.

Metasploit module exploiting InfoBlox Network Automation CVE-2014-3418 command injection to create a sudo user and deliver a reverse Meterpreter…

HTB Facts is a Easy Linux box featuring Camaleon CMS and MinIO. Gain admin access via open registration and a mass assignment vulnerability, then…

Write-up do Sudo Agent CTF (TryHackMe), com enumeração, exploração web, esteganografia, SSH e privilege escalation via CVE-2019-14287.

Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…

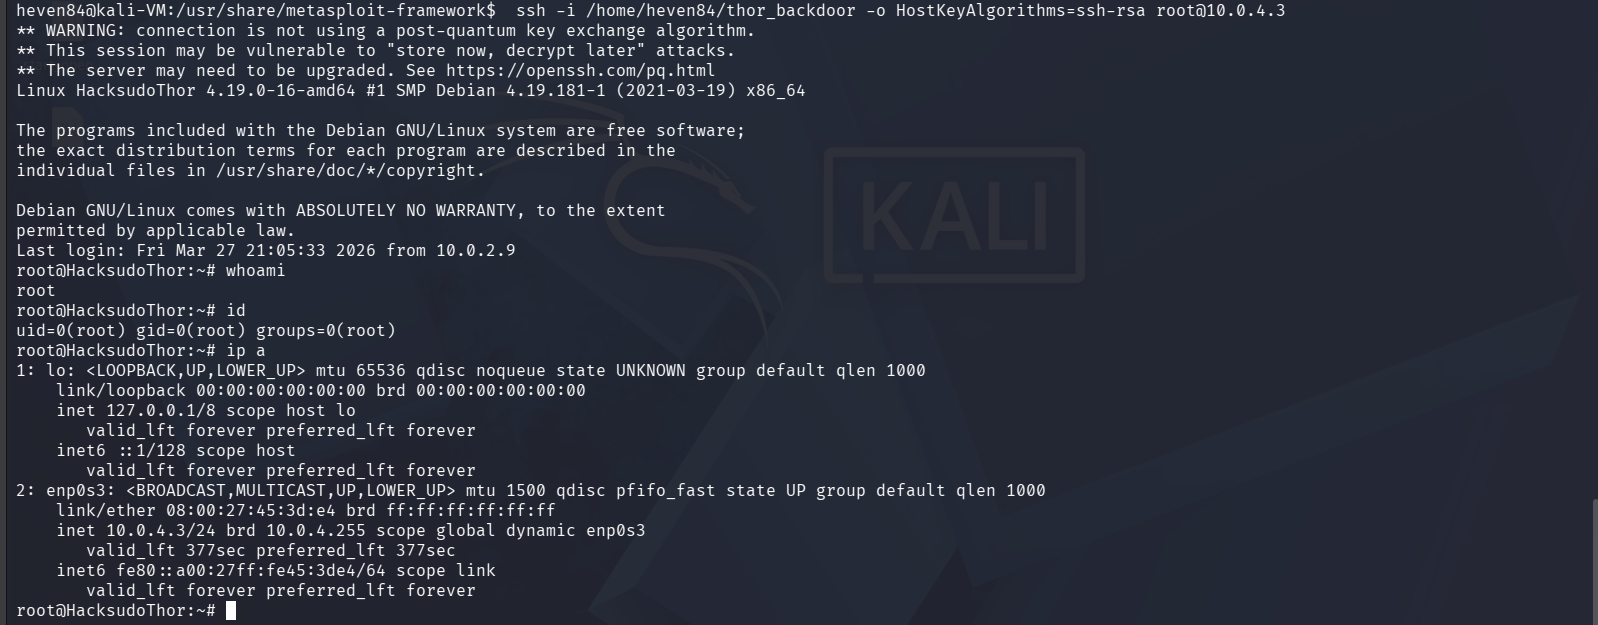
Black-box penetration test against HackSudo Thor : CVE-2014-6271 Shellshock RCE through Apache mod_cgi, chained with sudo misconfiguration and bash…

Structured HTB walkthrough demonstrating Shellshock (CVE-2014-6271) exploitation via CGI directory fuzzing and privilege escalation through…

First CTF successfully completed! This repo documents my walkthrough of TryHackMe's Simple CTF. It covers network reconnaissance (Nmap), web…

Traveller is an Easy Linux machine featuring a Joomla 4.2.7 travel booking website vulnerable to CVE-2023-23752, an unauthenticated REST API…

Authenticated command injection exploit for QuickBox Pro v2.1.8, providing remote code execution as www-data and privilege escalation to root via…

Exploit code for CVE-2019-14287 and CVE-2014-6271, targeting sudo privilege escalation and Shellshock vulnerabilities.

Privilege escalation exploit for Nagios XI 2024R1.01, enabling full root access from NAGIOS or APACHE users via malicious RSS dashlet injection and…

Exploit for Jenkins serialization vulnerability - CVE-2016-0792

Some Pentest Tools. Install and keep up to date some pentesting tools. I used this to pass my OSCP exam.

New Found 0-days!