
CVE-2018-18852
 hook-s3c/cve-2018-18852
Authenticated remote code execution exploit for CERIO routers (DT300N, DT100G, AMR-3204, WMR-200N) using vendor default credentials. Python PoC…
embedded-systems-securityexploitationiot-security+4
45
hook-s3c/cve-2018-18852Authenticated remote code execution exploit for CERIO routers (DT300N, DT100G, AMR-3204, WMR-200N) using vendor default credentials. Python PoC…
 orf53975/rig-exploit-for-cve-2018-8174
Rig Exploit for CVE-2018-8174 As with its previous campaigns, Rig’s Seamless campaign uses malvertising. In this case, the malvertisements have a…
 nsflabs/cve-2020-5902
Python scanner to detect CVE-2020-5902 RCE vulnerability in F5 BIG-IP TMUI. Tests unauthenticated remote systems for arbitrary command execution via…
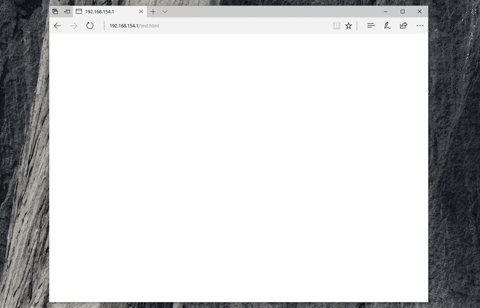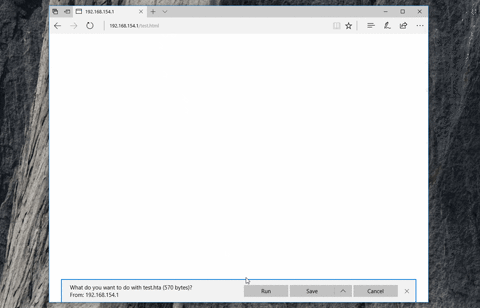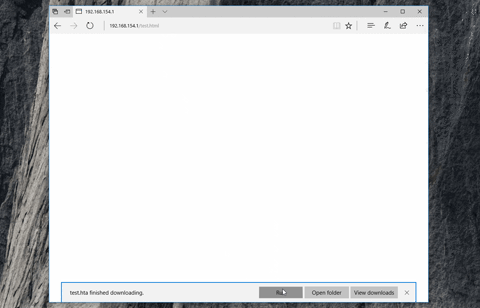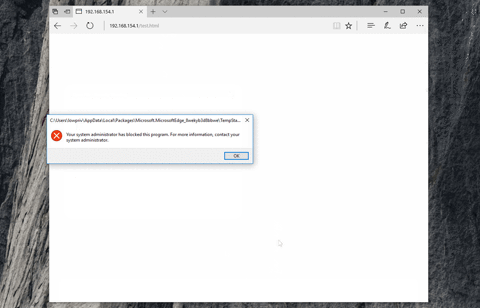 nccgroup/demiguise
HTA encryption tool for RedTeams
 rip1s/cve-2017-11882
CVE-2017-11882 Exploit accepts over 17k bytes long command/code in maximum.
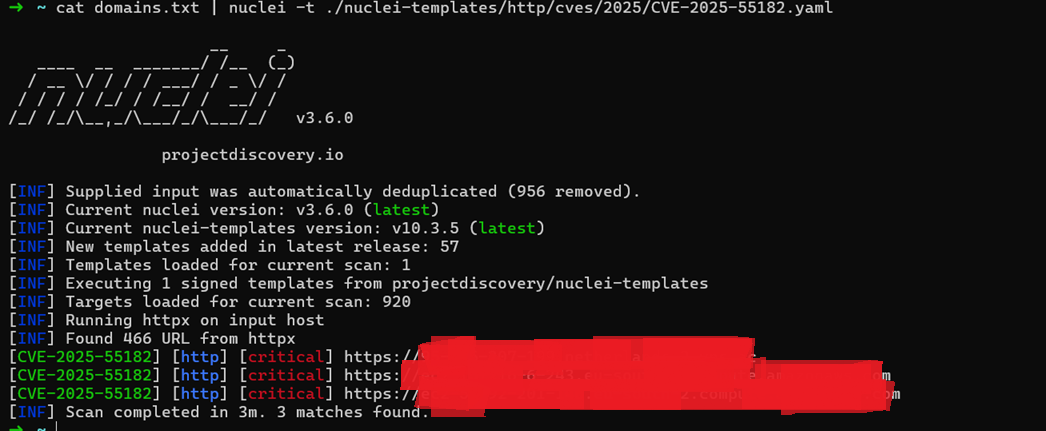 jaycelation/cve-2025-55182
PoC, Hunting React2Shell about CVE-2025-55182
 sk1dish/ilo4-rce-vuln-scanner
Scan a list of given IP's for CVE-2017-12542
 hudi233/cve-2022-1388
Shell-based scanner for CVE-2022-1388 (F5 BIG-IP iControl REST unauthenticated RCE). Checks target IPs for the vulnerability and reports exploitable…
 xhendos/cve-2017-5638
Proof-of-concept exploit for Apache Struts vulnerability CVE-2017-5638, with scripts to scan random IPs, check for the vulnerability, and execute…
 zhusx110/cve-2019-2725
Automated scanner and exploit for CVE-2019-2725 (Oracle WebLogic RCE). Reads target IPs from ip.txt, checks for vulnerability, and saves exploitable…
 abrewer251/cve-2025-1974_ingressnightmare_poc
Automates sending JSON payloads to multiple IPs via curl to test for CVE-2025-1974 (IngressNightmare), classifying responses and generating XML…
 givemefivw/cve-2021-3019
Automated exploitation tool for CVE-2021-3019 that reads target IPs from a text file and executes the exploit against HTTP endpoints.
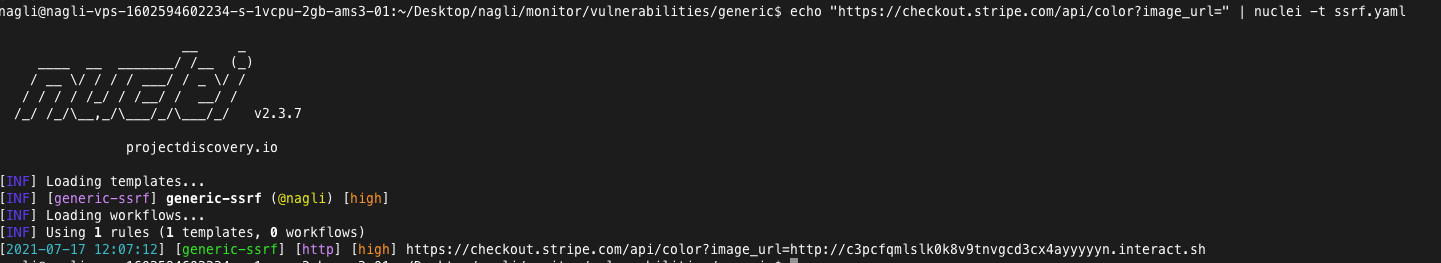 gal-nagli/shockwave-oss
Curated collection of bug bounty tips, one-liners, and automation workflows for recon, fuzzing, and web exploitation, with private nuclei templates…
 itres-labs/cve-2023-3350
Exploit for cryptographic Issue vulnerability on IBERMATICA RPS [CVE-2023-3350]
 ak-cybe/cve-2025-68613-n8n-rce-analysis
CVE-2025-68613 (n8n) Critical RCE analysis + defensive recommendations (patch validation, detection ideas, and hardening tips)
 cycraft-corp/cve-2019-7192-check
Checker for QNAP pre-auth root RCE (CVE-2019-7192 ~ CVE-2019-7195)
 abhishekmorla/cve-2022-26134
Exploit scanner for CVE-2022-26134 in Atlassian Confluence. Uses Shodan to find vulnerable hosts, then executes commands via the OGNL injection…
 zadewg/rius
CVE-2020-20093; 20094; 20095; 20096, 2022-28345 RTLO Injection URI Spoofing