
WebGoat
 webgoat/webgoat
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
ctfeducationlabs-practice+4
9.4k4 days ago
webgoat/webgoatDeliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
 timothyjxhn/deliberatelyvulnerablewebapp
A Deliberately Vulnerable Web Application built on Struts 2 (CVE-2017-5638) and Log4J (CVE-2021-44228) for testing and demonstration of OWASP Top 10…
 owasp/dvsa
a Damn Vulnerable Serverless Application
 mindpatch/simple-maven
Deliberately vulnerable C# API application for practicing web application exploitation and security testing. Includes Docker setup and documentation…
 appsecco/dvcsharp-api
Damn Vulnerable C# Application (API)
 owasp/offat
Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 yeswehack/vulnerable-code-snippets
Twitter vulnerable snippets
 moeinfatehi/xss_vulnerability_challenges
Dockerized PHP application providing hands-on XSS vulnerability challenges and bypass examples, including WAF, blacklist, and JavaScript validation…
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 owasp/vbscan
OWASP VBScan is a Black Box vBulletin Vulnerability Scanner
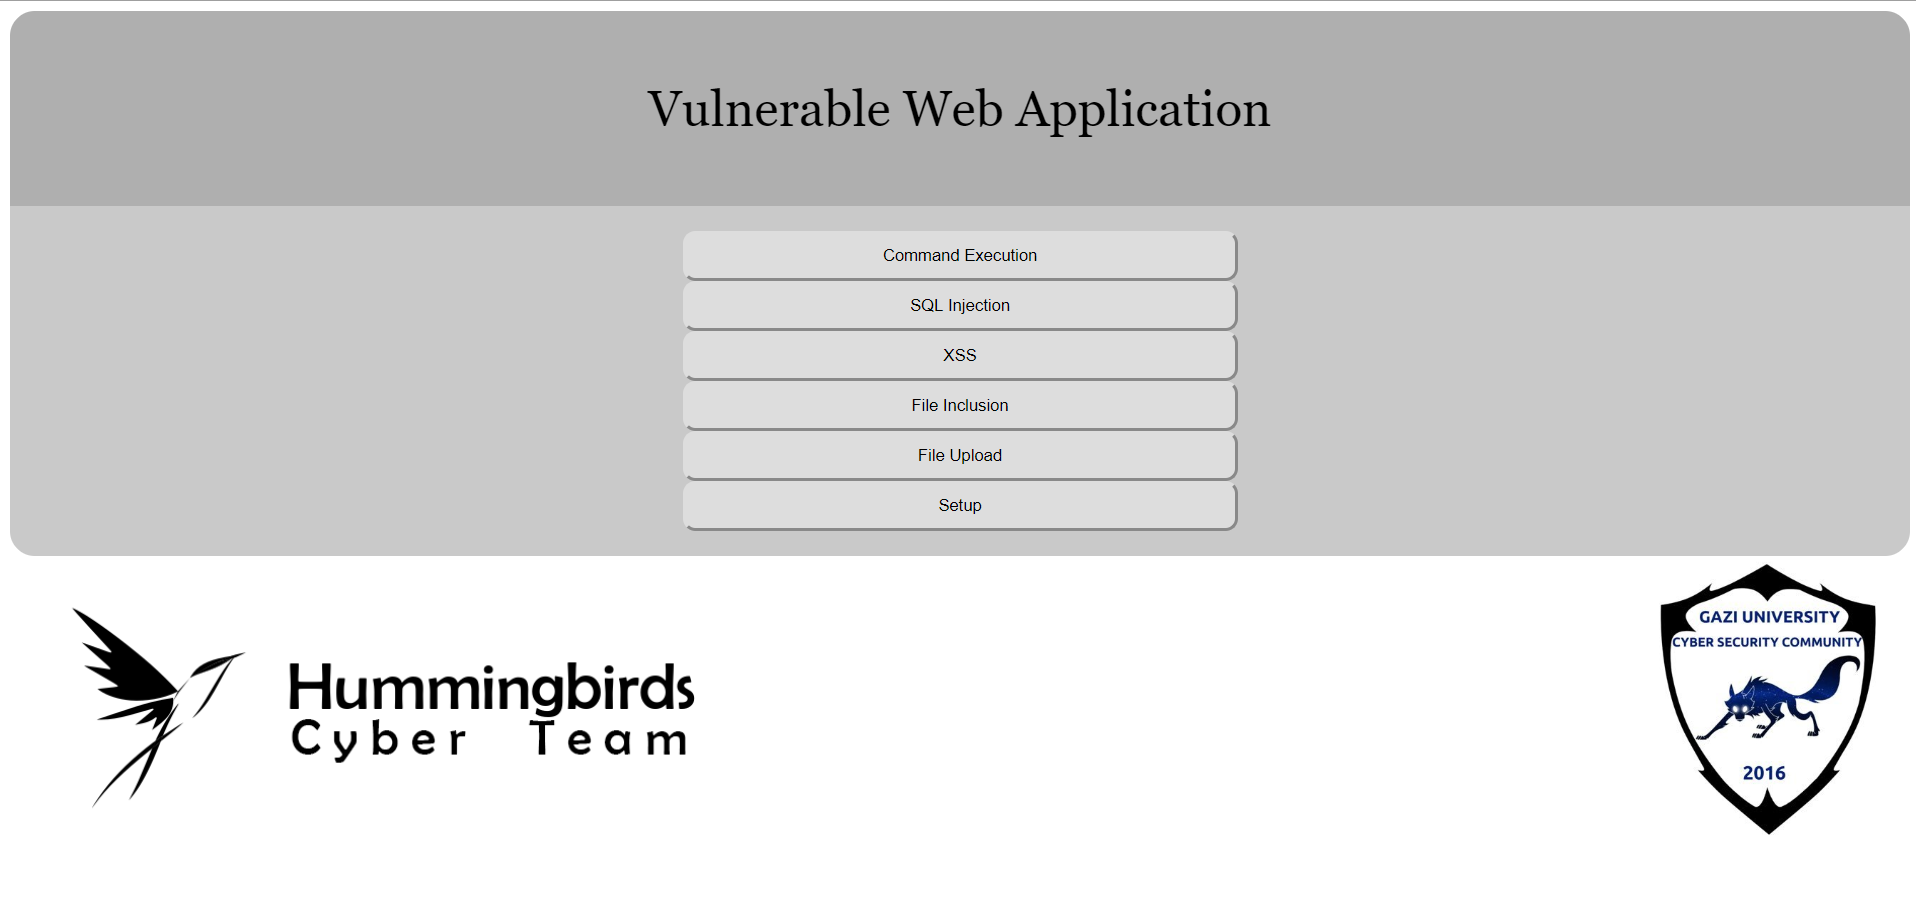 owasp/vulnerable-web-application
OWASP Vulnerable Web Application Project https://github.com/hummingbirdscyber
 owasp/joomscan
Perl-based Joomla CMS vulnerability scanner automating version enumeration, component detection, exploit matching, firewall identification, and…
 owasp/webgoat
This is a defunct code base. The project is located at: https://github.com/WebGoat
 owasp/qrljacking
Social engineering attack vector and exploitation framework for hijacking user sessions via QR code login, targeting web applications like WhatsApp,…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…