
CVE-2025-44203
 ivant7d3/cve-2025-44203
Exploit for CVE-2025-44203 targeting a race condition in HotelDruid 3.0.0/3.0.7 that leaks admin credentials and causes denial of service. Includes a…
exploitationinformation-gatheringpassword-cracking+2
ivant7d3/cve-2025-44203Exploit for CVE-2025-44203 targeting a race condition in HotelDruid 3.0.0/3.0.7 that leaks admin credentials and causes denial of service. Includes a…
 spyx/cve-2019-17240
Go-based brute-force tool exploiting Bludit bruteforce mitigation bypass (CVE-2019-17240) for automated password cracking against admin login pages.
 boreas37/cve-2026-43914-poc
PoC for CVE-2026-43914: Vaultwarden <1.35.4 email-2FA brute-force bypass password oracle. Stdlib-only Python.
 leekenghwa/cve-2023-37756-cwe-521-lead-to-malicious-plugin-upload-in-the-i-doit-pro-25-and-below
Proof-of-concept for CVE-2023-37756: weak password requirements in i-doit Pro admin-center enabling brute-force login and malicious plugin upload…
 pocpioneer/cve-2025-4094-poc
WordPress Plugin Digits < 8.4.6.1 - OTP Auth Bypass via Bruteforce (CVE-2025-4094)
 david-botelho-mariano/exploit-cve-2024-25723
Educational Proof of Concept exploit for CVE-2024-25723, demonstrating unauthorized account takeover in ZenML via API password reset, with version…
 saykino/cve-2023-34732
Proof-of-concept exploit for CVE-2023-34732 demonstrating authenticated function abuse in Flytxt NEON-dX to brute-force and reset user passwords,…
 c1ph3rx13/cve-2023-42820
Exploit script for JumpServer password reset vulnerability CVE-2023-42820, with automatic verification code calculation and password modification.
 n4nj0/cve-2020-35590
Brute-force tool for WordPress Plugin Limit Login Attempts Reloaded >=2.13.0 - Login Limit Bypass (CVE-2020-35590)
 jfriedli/cve-2025-10658
Python exploit script for CVE-2025-10658: brute-forces 6-digit OTP in WordPress SupportCandy guest login to achieve full account takeover via…
 inflixim4be/cve-2020-15367
Exploit for CVE-2020-15367: brute-force authentication attack against Venki Supravizio BPM 10.1.2 login page, leveraging user enumeration to gain…
 tieulong21prosper/detect_bruteforce
detect bruteforce using for cve-2021-34527
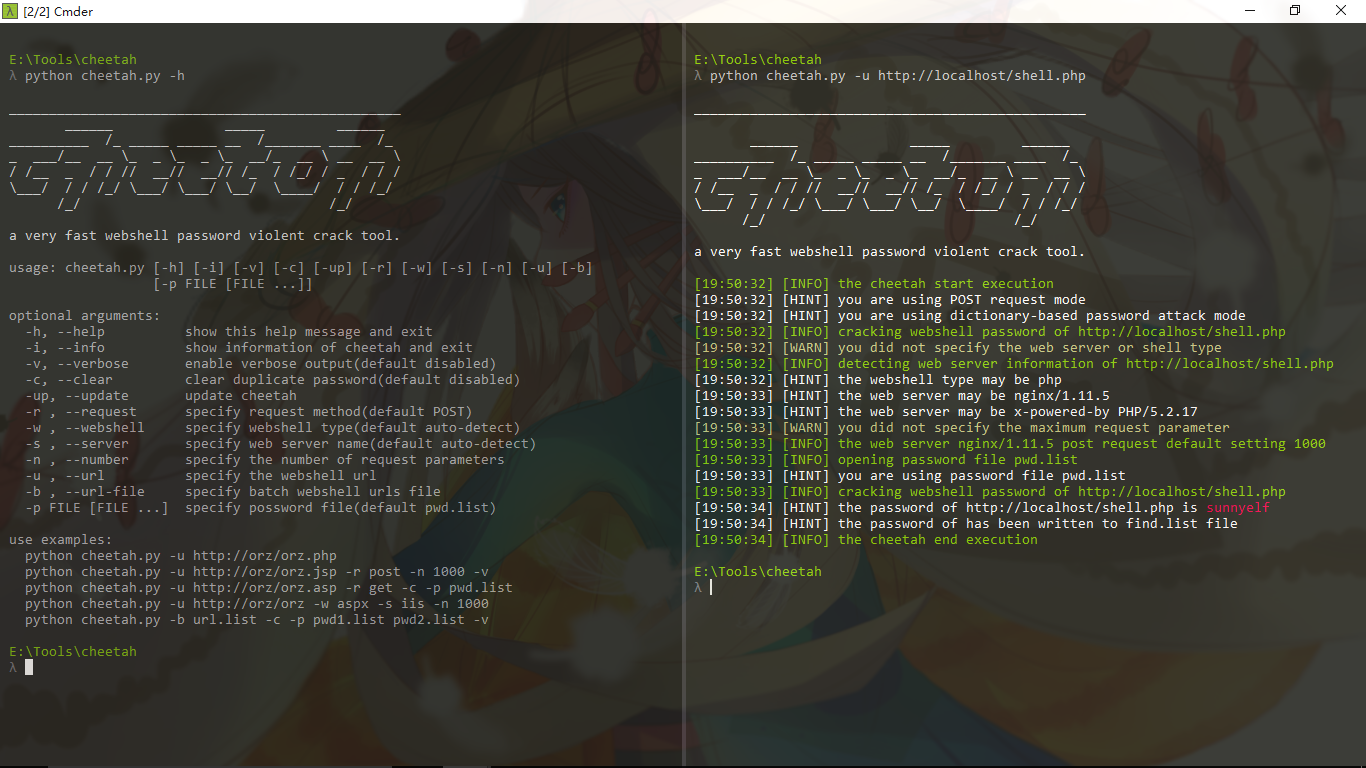 shmilylty/cheetah
a very fast brute force webshell password tool
 karma-syndicate/xcrack-python-tools-for-hackers
Python Hacking Tool for Hackers And Spammers
 pr0x13/idict
PHP-based iCloud Apple ID dictionary attack tool that bypasses account lockout and secondary authentication to brute-force credentials.
 ajnik/joomla-bruteforce
Python script that brute-forces Joomla administrator login credentials using wordlists, with proxy and verbose options for penetration testing.
 randomrobbiebf/cve-2023-32243
CVE-2023-32243 - Essential Addons for Elementor 5.4.0-5.7.1 - Unauthenticated Privilege Escalation
 cyberheartmi9/cve-2017-8295
Proof-of-concept exploit for CVE-2017-8295, a WordPress password reset vulnerability allowing attackers to obtain reset links without authentication,…