
CVE-2026-34990-poc
Proof-of-concept exploit for CVE-2026-34990, a CUPS 2.4.16 local privilege escalation via arbitrary file write through CUPS_CREATE_LOCAL_PRINTER and…

Proof-of-concept exploit for CVE-2026-34990, a CUPS 2.4.16 local privilege escalation via arbitrary file write through CUPS_CREATE_LOCAL_PRINTER and…

Exploit for CVE-2013-2842, a kernel privilege escalation vulnerability, providing local privilege escalation on affected Linux systems.

Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…

Proof-of-concept exploit for CVE-2025-8110 in Gogs <=0.13.x, enabling authenticated symlink bypass to arbitrary file write as the Gogs process user,…

Proof-of-concept exploit for CVE-2017-0106, a Win32k elevation of privilege vulnerability in Windows, enabling local privilege escalation.

Comprehensive penetration testing write-up and exploit details for Hack The Box - Enigma machine, covering local enumeration, OliveTin CVE-2026-27626…

Vulnerability disclosure with PoCs for three critical Termius macOS flaws: Remote Code Execution via exposed Node modules, Local Privilege Escalation…

CVE-2026-102282: Local Privilege Escalation via SUID/SGID preservation during archive extraction

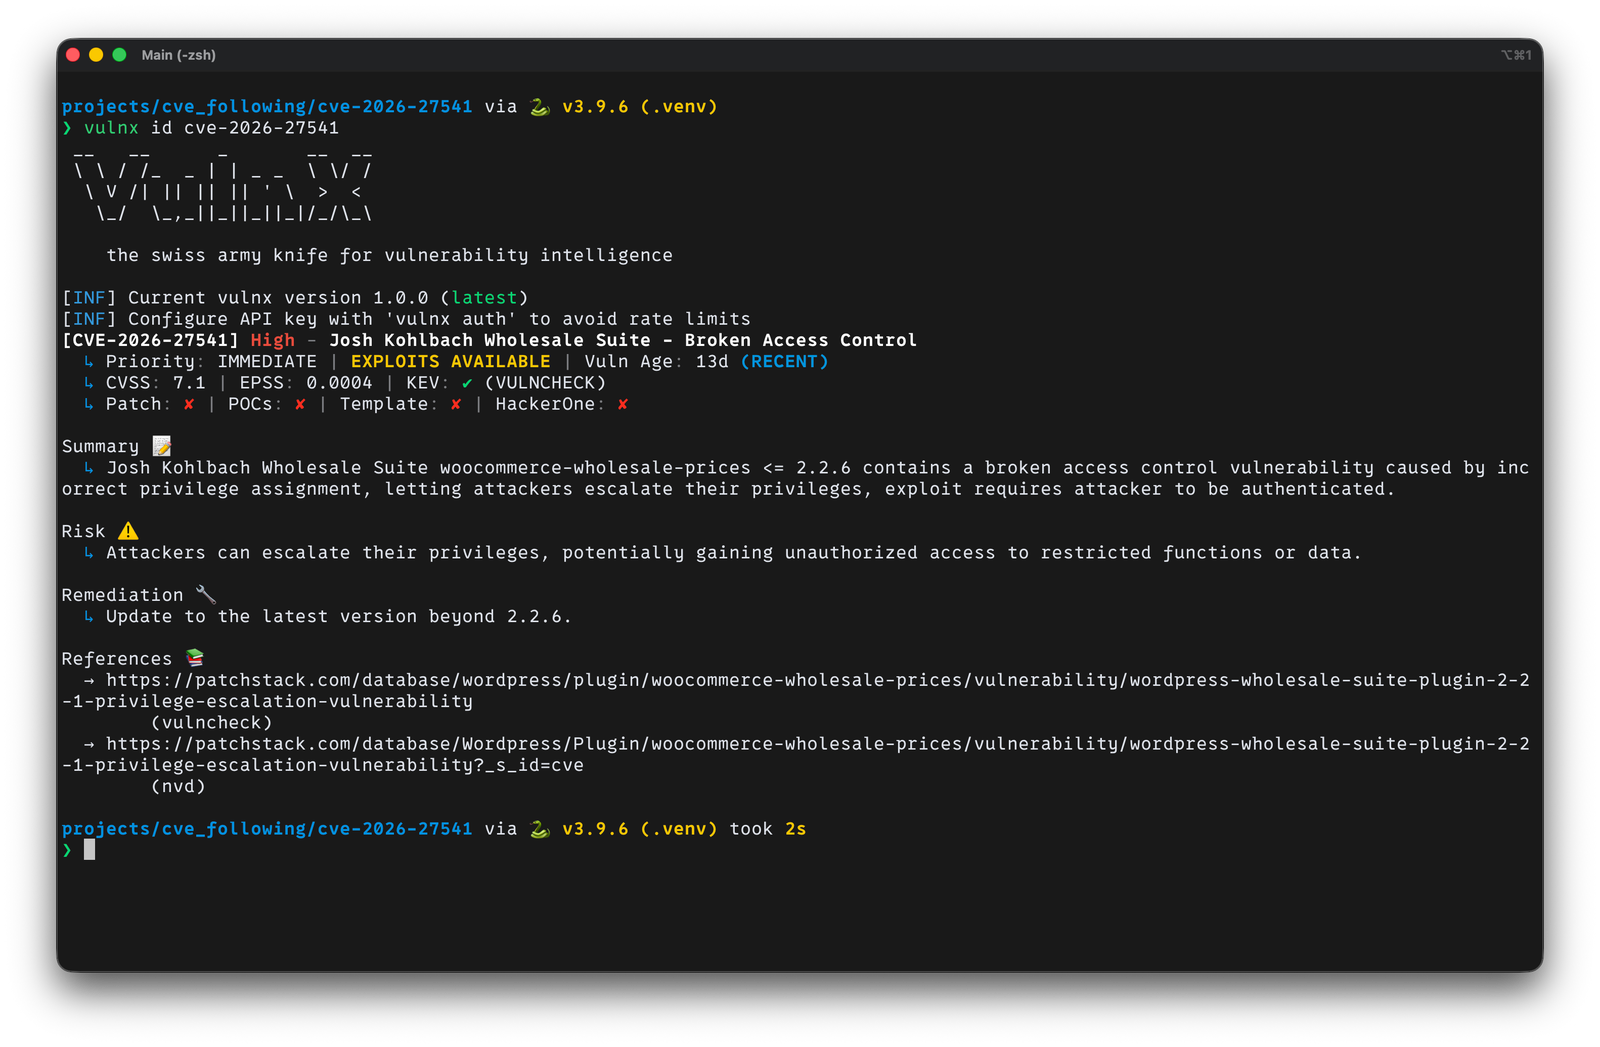
Docker lab for reproducing CVE-2026-27541, an authenticated privilege escalation in WooCommerce Wholesale Prices. Compares vulnerable and patched…

Local privilege escalation against a root `cupsd`.

CUPS 2.4.16 Local Privilege Escalation via Local Admin Token Leak and file:// Arbitrary File Write (CVE-2026-34990)

CVE-2020-11107-Local-Privilege-Escalation-XAMPP-7.2.29-7.3.x-7.3.16-7.4.x-7.4.4

[PoC] Privilege escalation & code execution via LFI in PwnDoC

Improper Symbolic link handling in the PutContents API in Gogs allows Local Execution of Code.

A "Mishandling of Input to API" or "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure…

Acunetix 0day RCE

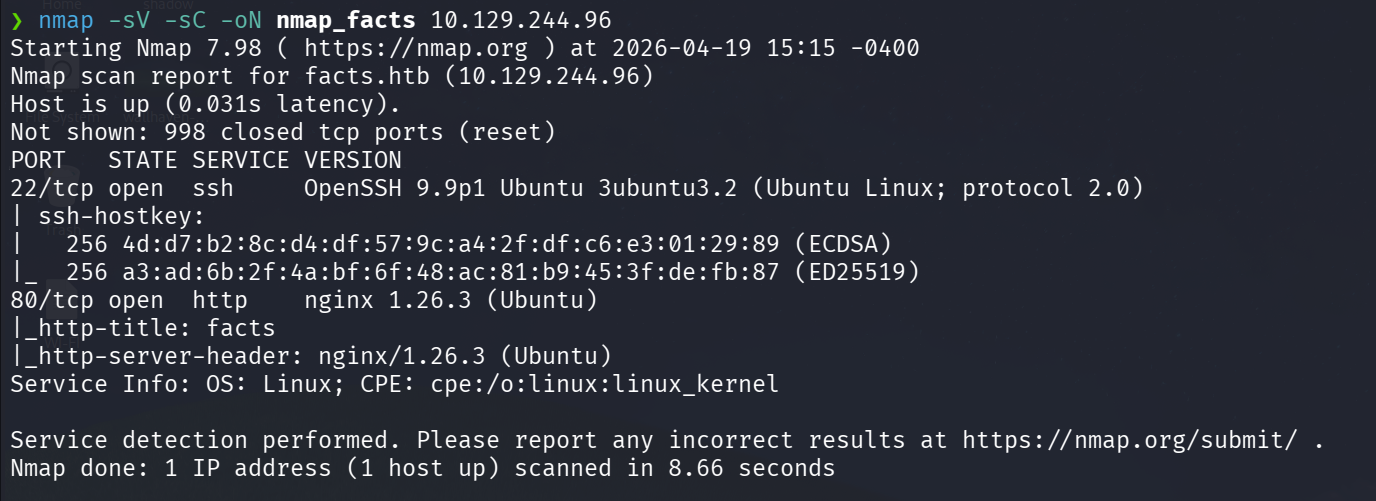
HackTheBox — Facts (Easy/Linux) | CVE-2025-2304 + AWS S3 + SSH Key + Facter PrivEsc