
CVE-List
 cylock11/cve-list
A collection of CVE exploits, including Python PoCs and README files with instructions for reproducing and exploiting each vulnerability.
curated-resourceseducationexploitation+4
cylock11/cve-listA collection of CVE exploits, including Python PoCs and README files with instructions for reproducing and exploiting each vulnerability.
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node
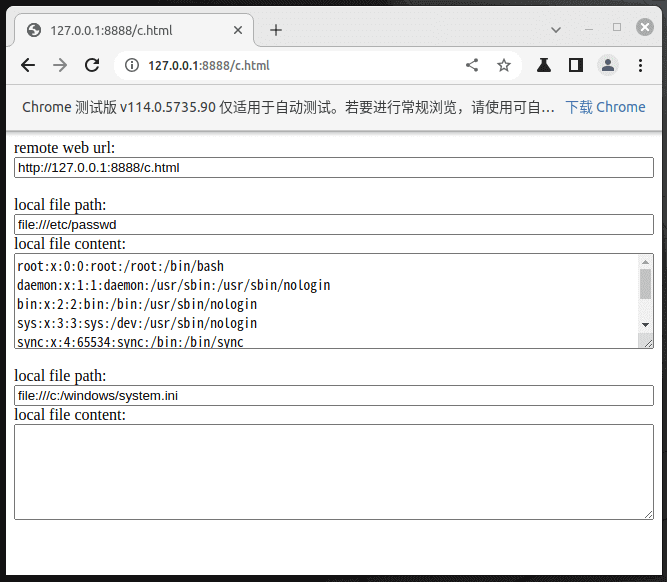 xcanwin/cve-2023-4357-chrome-xxe
[漏洞复现] 全球首款单文件利用 CVE-2023-4357 Chrome XXE 漏洞 EXP, 实现对访客者本地文件窃取. Chrome XXE vulnerability EXP, allowing attackers to obtain local files of visitors.
 vulnmachines/grafana-unauth-file-read
Exploit for Grafana LFI vulnerability CVE-2021-43798 enabling unauthorized file reading via path traversal in plugin endpoints.
 trackflaw/cve-2023-25202
CVE-2023-25202: Insecure file upload mechanism
 yahiahamza/cve-2026-25099
Python exploit for Bludit CMS API unrestricted file upload leading to remote code execution, providing command execution and interactive shell for…
 binganao/cve-2024-23897
Proof-of-concept exploit for CVE-2024-23897, a Jenkins arbitrary file read vulnerability, allowing retrieval of sensitive files via crafted HTTP…
 imjdl/cve-2019-11510-poc
Proof-of-concept exploit for CVE-2019-11510 targeting pre-authentication arbitrary file read in Pulse Secure SSL VPN. Enables extraction of sensitive…
 maddsec/cve-2023-34598
Gibbon v25.0.0 is vulnerable to a Local File Inclusion (LFI) vulnerability where it's possible to include the content of several files present in the…
 jpiechowka/zip-shotgun
Utility script to test zip file upload functionality (and possible extraction of zip files) for vulnerabilities (aka Zip Slip)
 entr0pie/cve-2022-44268
Proof-of-concept exploit for ImageMagick arbitrary file read vulnerability (CVE-2022-44268) via crafted PNG textual chunks, enabling extraction of…
 chiefyoru/cve-2026-48939_poc
iCagenda extension for Joomla allows the upload of arbitrary files in the file attachment feature, ultimately resulting in PHP code upload and…
 abokormahammadmousse/cve-2025-25279-mattermost-path-traversal
Proof-of-concept exploit for CVE-2025-25279, a Mattermost Focalboard path traversal enabling authenticated arbitrary file read and exfiltration of…
 abrewer251/cve-2020-3452_cisco_asa_pathtraversal
Proof-of-concept exploit for CVE-2020-3452, a path traversal in Cisco ASA/FTD, enabling unauthenticated file disclosure. Automates extraction of…
 icmpoff/apache-2.4.49-2.4.50-traversal-remote-code-execution-exploit
This Metasploit module exploits an unauthenticated remote code execution vulnerability which exists in Apache version 2.4.49 (CVE-2021-41773). If…
 pwn3z/cve-2021-41773-apache-rce
A flaw was found in a change made to path normalization in Apache HTTP Server 2.4.49. An attacker could use a path traversal attack to map URLs to…
 mksundaram69/cve-2024-34102
Proof-of-concept exploit for CVE-2024-34102, a critical XML entity injection in Magento, enabling exfiltration of sensitive files and unauthorized…
 mbadanoiu/wso2-2021-1260
WSO2-2021-1260: Deletion of Arbitrary files via Path Traversal in Artifact Name in WSO2 ESB