

strix
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
ai-securityapi-security-testingcode-analysis+9
usestrix/strixOpen-source AI penetration testing tool to find and fix your app’s vulnerabilities.
 in3tinct/see-surf
Security tool to find potential vulnerable Server Side Request Forgery (SSRF) parameters.
 whxitte/white-deface
This is a simple python tool to automatically deface webdav vulnerable websites.
 dwisiswant0/proxylogscan
A fast tool to mass scan for a vulnerability on Microsoft Exchange Server that allows an attacker bypassing the authentication and impersonating as…
 cyb0r9/config-exploiter
Automated tool to dump config.php files from vulnerable Joomla and WordPress websites using known exploit modules (com_joomanager, revslider).
 randomrobbiebf/phpunit-brute
Tool to try multiple paths for PHPunit RCE CVE-2017-9841
 revoltsecurities/cve-2023-22518
An Exploitation tool to exploit the confluence server that are vulnerable to CVE-2023-22518 Improper Authorization
 mbrg/dontgo403
Tool to bypass 40X response codes.
 mr-xn/cve-2021-26855-d
Python tool to exploit CVE-2021-26855 (ProxyLogon) for downloading Exchange mailbox emails via EWS, supporting user enumeration and bulk target…
 samh4cks/cve-2023-27163-internalprober
A tool to perform port scanning using vulnerable Request-Baskets
 00xcanelo/cve-2025-32778
PoC exploit for CVE-2025-32778: command injection in Web-Check OSINT tool
 sl4cky/cve-2018-7600-masschecker
Tool to check for CVE-2018-7600 vulnerability on several URLS
 caybermods/cve-2026-22812-poc
Python tool to check and exploit CVE-2026-22812 in OpenCode, supporting command execution, file read, and multi-target scanning on ports 4095-4100.
 nebian/cve-2024-23897
Scraping tool to ennumerate directories or files with the CVE-2024-23897 vulnerability in Jenkins.
 amirqusairy99/wordpress-file-upload-4.24.11---unauthenticated-path-traversal
Python-based tool to detect and exploit arbitrary file read vulnerability in WordPress WP File Upload plugin (<=4.24.11), enabling unauthenticated…
 0x6b7966/cve-2019-13063-poc
Proof of concept tool to exploit the directory traversal and local file inclusion vulnerability that resides in the Sahi-pro web application…
 adel-hx0d/cve-2006-3392
It is a simple tool to exploit local file include . vulnerabilities
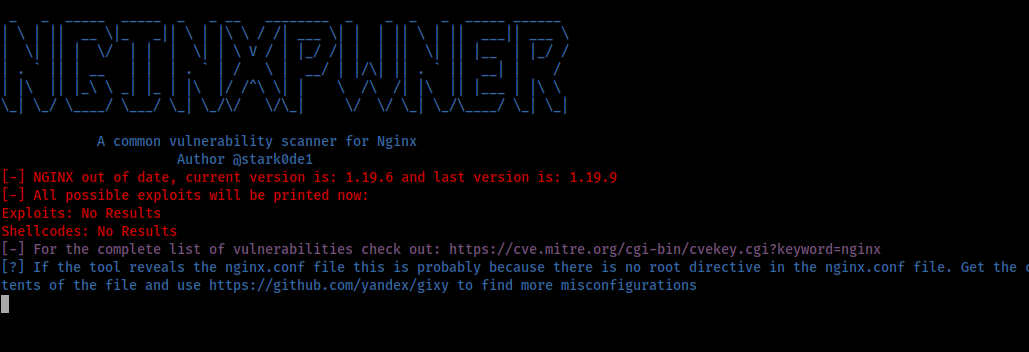 stark0de/nginxpwner
Nginxpwner is a simple tool to look for common Nginx misconfigurations and vulnerabilities.