Exploit-CSRF-on-SCOPIA-XT-Desktop-version-8.3.915.4

Proof of concept demonstrating Cross-Site Request Forgery (CSRF) on Avaya SCOPIA XT Desktop, allowing admin password change without anti-CSRF token.

Proof of concept demonstrating Cross-Site Request Forgery (CSRF) on Avaya SCOPIA XT Desktop, allowing admin password change without anti-CSRF token.

fsociety Hacking Tools Pack – A Penetration Testing Framework

JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…

Git-lfs RCE exploit CVE-2020-27955 - tested on Windows on: git, gh cli, GitHub Desktop, Visual Studio, SourceTree etc.

Exploit tool targeting CVE-2019-0708 in Remote Desktop Services, enabling remote code execution on vulnerable Windows systems for penetration testing…

Go-based exploit for CVE-2020-27955, achieving remote code execution via Git LFS on Windows across multiple development tools including Git, VS Code,…

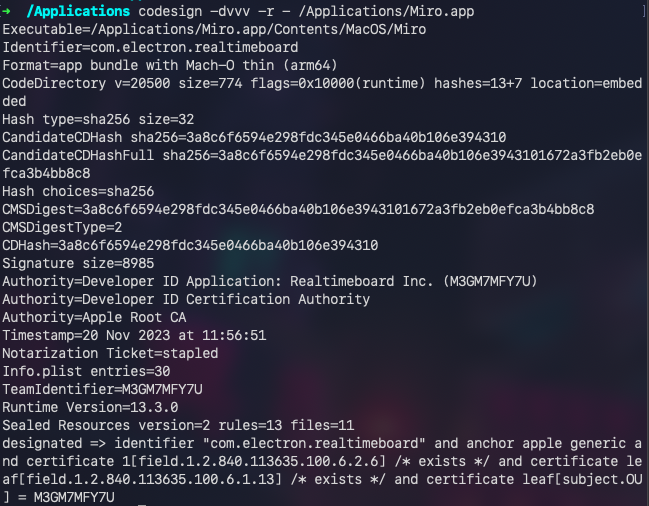
Miro Desktop 0.8.18 on macOS allows Electron code injection.

A remote code execution vulnerability exists in Remote Desktop Services – formerly known as Terminal Services – when an unauthenticated attacker…

Python exploit for CVE-2020-10189 targeting ManageEngine Desktop Central, enabling unauthenticated remote code execution via file upload…

A remote code execution vulnerability exists in Remote Desktop Services – formerly known as Terminal Services – when an unauthenticated attacker…

CVE-2024-38077 vulnerability checker with proof-of-concept exploit targeting Windows Remote Desktop Licensing Service. Validates by connecting to a…

OS Command Injection Vulnerability via Cache Clearing Scheduler in Reolink Desktop Application

Checks Remote Desktop Gateway servers for CVE-2019-1006 by sending crafted requests to a user-supplied URL and reporting whether the target is…

Proof-of-concept exploit demonstrating unauthorized microphone recording and desktop notification abuse via embedded web pages in Obsidian Canvas,…

Local Authentication Bypass Vulnerability in Reolink Desktop Application

CVE-2025-34324, CVE-2025-34327: GoSign Desktop TLS Bypass & Insecure Update Exploit Proof of Concept

OS Command Injection Vulnerability via Plugin Execution in Figma Desktop Application

Proof-of-concept exploit code for CVE-2024-38077, a remote code execution vulnerability in Windows Remote Desktop Licensing Service. Backup copy, not…