

Docx-Exploit-2021
 lazarusreborn/docx-exploit-2021
This docx exploit uses res files inside Microsoft .docx file to execute malicious files. This exploit is related to CVE-2021-40444
command-and-controlexploitationmalware-analysis+3
5
lazarusreborn/docx-exploit-2021This docx exploit uses res files inside Microsoft .docx file to execute malicious files. This exploit is related to CVE-2021-40444
 lockedbyte/cve-2021-40444
Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office RCE) with a hosted server for DLL payload delivery, based on…
 abelche/evil_minio
EXP for CVE-2023-28434 MinIO unauthorized to RCE
 fengjixuchui/cve-2021-40444-docx-generate
Generates .docx files exploiting CVE-2021-40444 for Microsoft Office Word Remote Code Execution via malicious bitmap image objects.
 knooow/cve-2021-40444-docx-generate
Generates malicious .docx files exploiting CVE-2021-40444 (Microsoft Office Word RCE) with embedded HTML and CAB payloads for penetration testing.
 hqdat809/cve-2021-40444
Malicious DOCX generator exploiting CVE-2021-40444 for remote code execution via crafted Office documents, with integrated hosting server for payload…
 w1kyri3/exploit-poc-cve-2021-40444-inject-ma-doc-vao-docx
Generates malicious DOCX files exploiting CVE-2021-40444 to achieve remote code execution via crafted Office documents, with an integrated hosting…
 alexcot25051999/cve-2021-40444
Generates malicious DOCX files exploiting CVE-2021-40444 to achieve remote code execution via crafted CAB and HTML payloads, with a built-in hosting…
 lisinan988/cve-2021-40444-exp
Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office Word RCE) with a built-in HTTP server for payload delivery and…
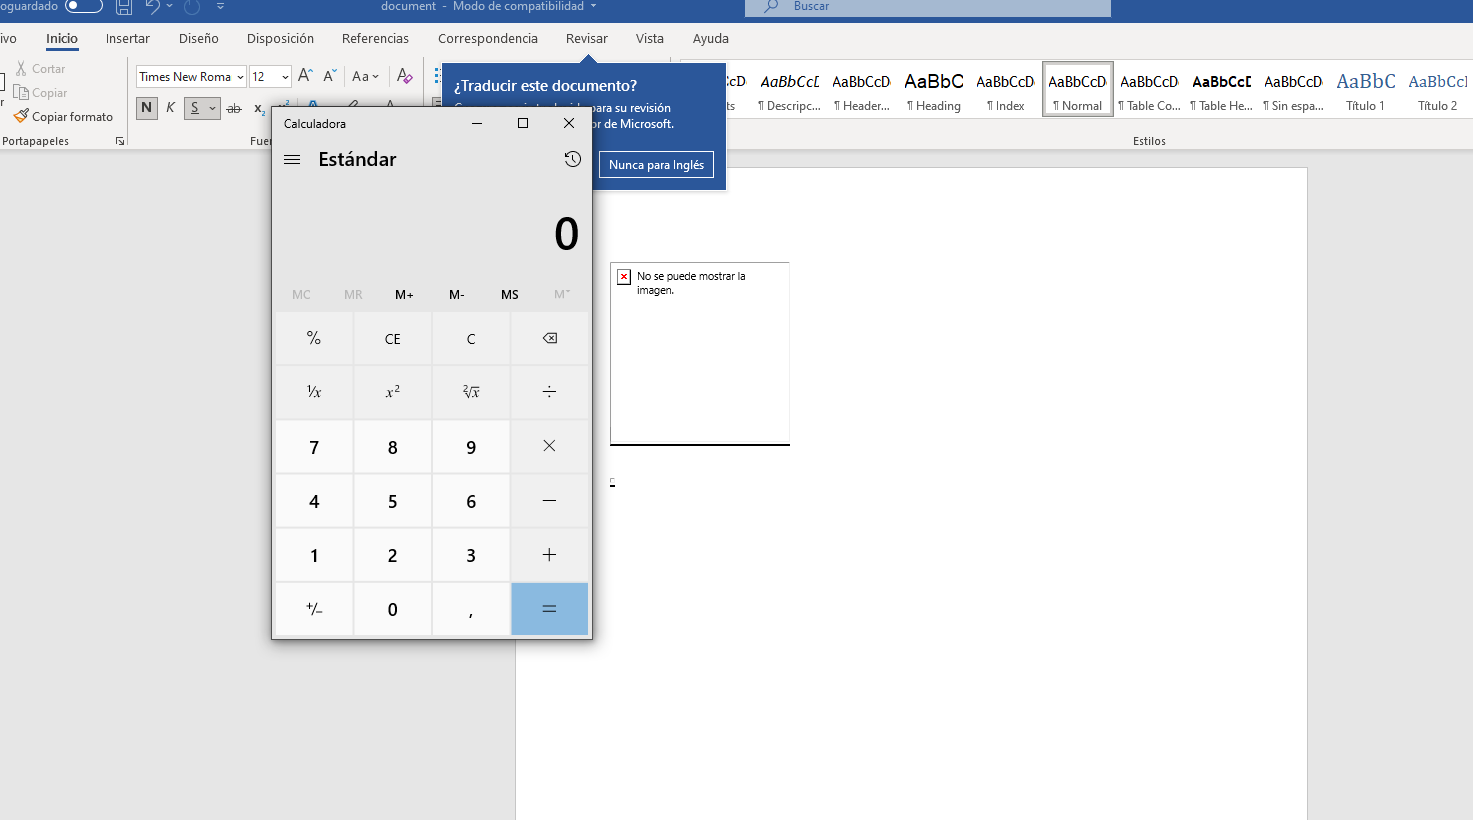 sudoaza/cve-2022-30190
MS-MSDT Follina CVE-2022-30190 PoC document generator
 drgreenthumb93/cve-2022-30190-follina
Proof-of-concept exploit for CVE-2022-30190 (Follina MSDT vulnerability). Generates a malicious Word document that executes a remote script via the…
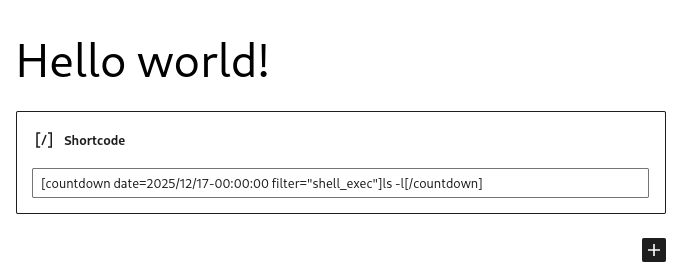 nimisha17/poc-cve-2025-9519
Proof-of-concept exploit for CVE-2025-9519, demonstrating remote code execution in WordPress Easy Timer plugin via a crafted shortcode filter, with…
 kimstars/ashwesker-cve-2026-21509
Proof-of-concept exploit for Microsoft Office security feature bypass (CVE-2026-21509). Generates malicious DOCX files with embedded OLE objects to…
 febinrev/deepin-linux_reader_rce-exploit
CVE-2023-50254: PoC Exploit for Deepin-reader RCE that affects unpatched Deepin Linux Desktops. Deepin Linux's default document reader…
 hscorpion/cve-2022-30190
Proof-of-concept exploit for CVE-2022-30190 (Follina). Generates malicious docx files and hosts a server to trigger remote code execution via…
 walidriouah/cve-2026-30691
CVE-2026-30691: Stored Cross-Site Scripting (XSS) in @cyntler/react-doc-viewer
 tiagob0b/cve-2021-40444
Malicious DOCX generator exploiting CVE-2021-40444 (Microsoft Office Word RCE) with CAB-based DLL side-loading and CAB-less RAR/WSF attack chains for…
 komomon/cve-2022-30190-follina-office-msdt-fixed
Modified CVE-2022-30190 exploit tool for MS-MSDT Office RCE with custom docx template support, binary/command execution modes, and embedded HTTP…