
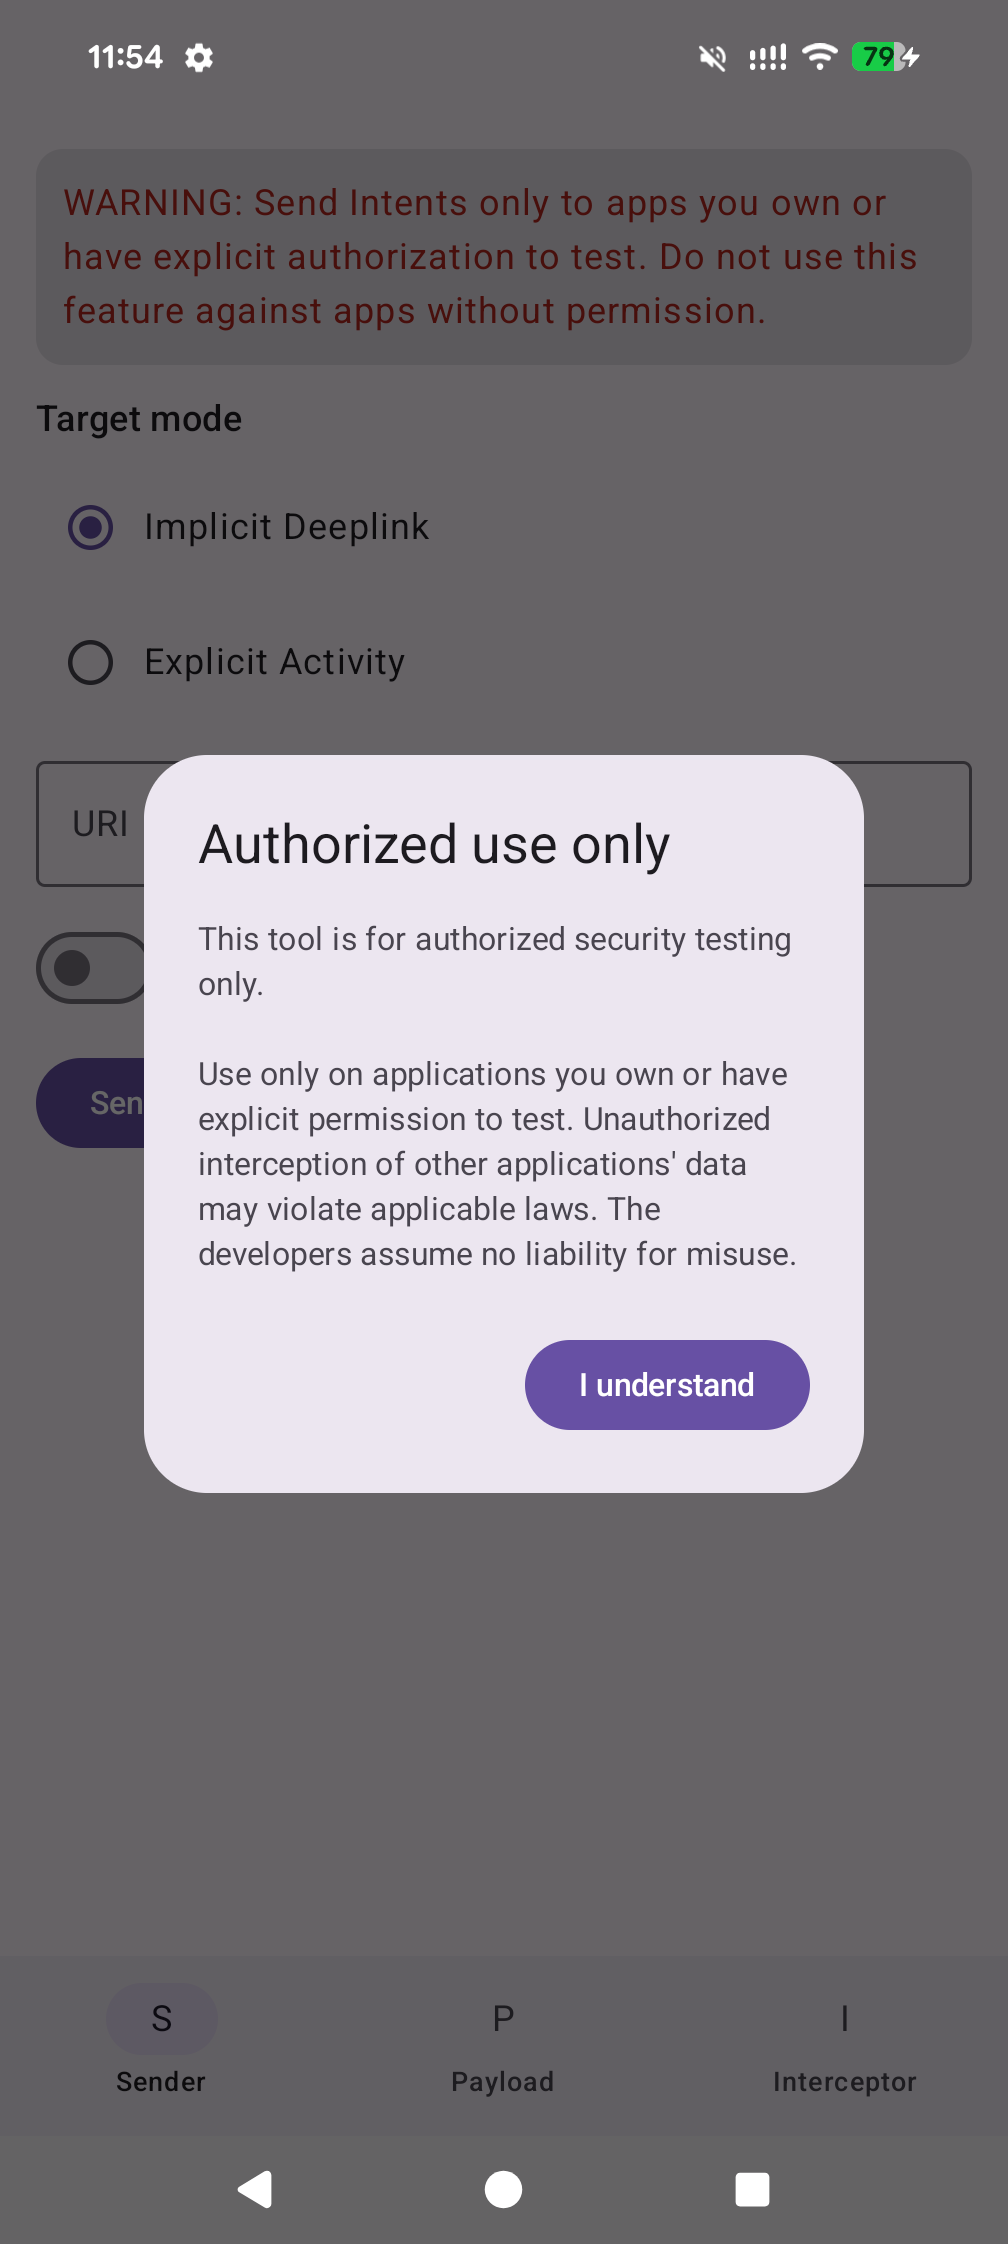
apk-interceptor
 sterrasec/apk-interceptor
Android deeplink, Intent, and WebView bridge assessment helper for ethical hacking
android-securityinformation-gatheringmobile-app-pentesting+3
8
sterrasec/apk-interceptorAndroid deeplink, Intent, and WebView bridge assessment helper for ethical hacking
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 mozilla/firefox-devtools-mcp
Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi
 census/whatsapp-mitd-mitm
PoC and tools for exploiting CVE-2020-6516 (Chrome) and CVE-2021-24027 (WhatsApp)
 nccgroup/conscrypttrustusercerts
Magisk module for Android 14 that adds user-installed CA certificates to the system's Conscrypt trust store, enabling HTTPS interception with proxy…
 adityatelange/poc-cve-2026-0073
CVE-2026-0073 - ADB Wireless Mutual Authentication Bypass PoC
 commando-x/vuln-bank-mobile
A deliberately vulnerable mobile banking application designed for practicing mobile security testing. Features common vulnerabilities found in…
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
 isec-tugraz/file-notification-attacks
Research artifacts for file-notification side-channel attacks on Linux, Windows, and macOS, demonstrating inotify/FSEvents leakage, keystroke timing,…
 absholi7ly/poc-for-cve-2024-7014-exploit
Proof of Concept (PoC) for CVE-2024-7014 (EvilVideo) Exploit
 jaf0rk/cve-2026-14382
Proof-of-concept exploit for CVE-2026-14382, a high-severity ANGLE vulnerability in Chromium, with 32-bit and AArch64 PoCs achieving program counter…
 satirush/cve-2025-14174-poc
Proof-of-Concept exploit for CVE-2025-14174 (EUVD-2025-203113) - Memory corruption in ANGLE allowing out-of-bounds access and RCE in web browsers.…
 hasan-khalil/cve-2020-6514
Exploit for CVE-2020-6514 targeting WebRTC SCTP memory corruption in Android applications. Uses Frida to hook native functions and alter SCTP packets…
 hfh86/cve-2021-43530-uxss-on-qrcode-reader-
Proof-of-concept for CVE-2021-43530, a Universal XSS vulnerability in Firefox for Android caused by improper URL sanitization when processing QR code…
 hunt-benito/the-callback-that-outlived-the-page-cve-2026-78997-uc-browser-android-universal-xss
PoC for CVE-2026-78997, a Universal XSS in UC Browser for Android. Includes a crafted URL builder, a callback-dispatch oracle, and Frida hooks to…
 hunt-benito/two-dots-and-a-slash-cve-2026-18907-tecno-hi-browser-download-path-traversal
Python PoC for CVE-2026-18907 path traversal in TECNO Hi Browser's download handler. Includes malicious HTTP server and naive downloader to…
 jaf0rk/cve-2026-5281-cve-2026-11057-fullchain
Full-chain exploit for Android Chromium combining CVE-2026-11057 info leak and CVE-2026-5281 use-after-free to achieve vtable hijack and arbitrary…
 iwallplace/cve-2026-26897-ecoonline-deeplink
Public advisory & PoC for CVE-2026-26897 — Deep Link Bypass in EcoOnline EHS Android (com.airsweb.v10), fixed in 0.2.500