
Tenda-F3-V4
 4d000/tenda-f3-v4
Python script to exploit CVE-2020-35391 on Tenda F3 V3/V4 routers, enabling unauthorized download of configuration, flash, and syslog files.
embedded-systems-securityexploitationfirmware-analysis+4
3
4d000/tenda-f3-v4Python script to exploit CVE-2020-35391 on Tenda F3 V3/V4 routers, enabling unauthorized download of configuration, flash, and syslog files.
 haingn/hik-cve-2021-36260-exploit
Go-based brute-force exploit tool targeting Hikvision cameras vulnerable to CVE-2021-36260, with multi-threaded scanning and configurable…
 leonardobg/cve-2023-36143
Proof-of-concept exploit for CVE-2023-36143 demonstrating command injection in Maxprint Maxlink 1200G v3.4.11E via the diagnostic tool web interface.
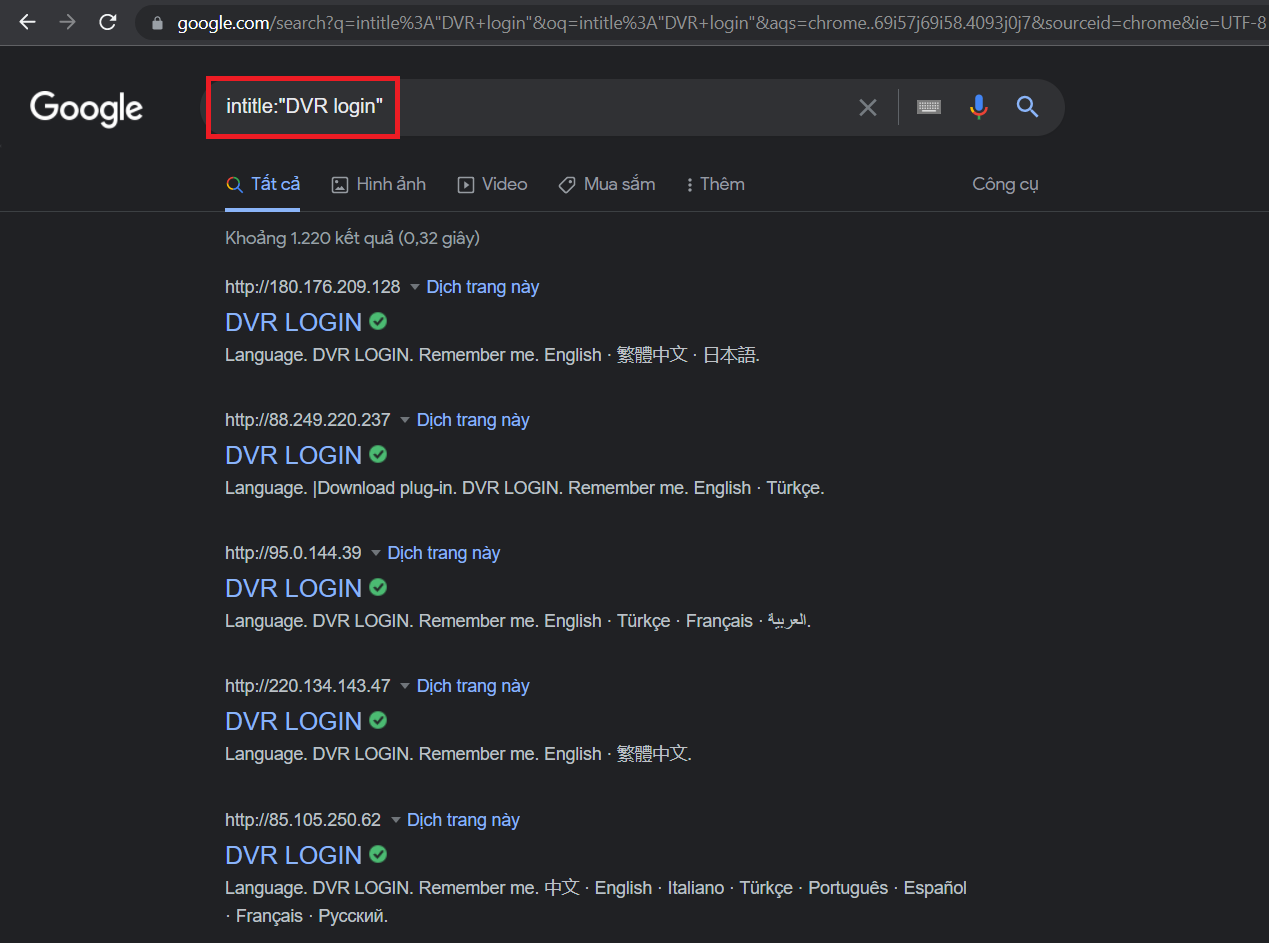 lequockhanh2k/tool_exploit_password_camera_cve-2018-9995
Exploit tool for CVE-2018-9995 that extracts credentials from vulnerable DVR devices via Google dorking and direct IP access.
 rajchowdhury240/cve-2018-13341
This Tool Aims to Exploit the CVE-2018-13341
 robintrigon/cve-2023-36143
Maxprint Maxlink 1200G v3.4.11E has an OS command injection vulnerability in the "Diagnostic tool" functionality of the device.
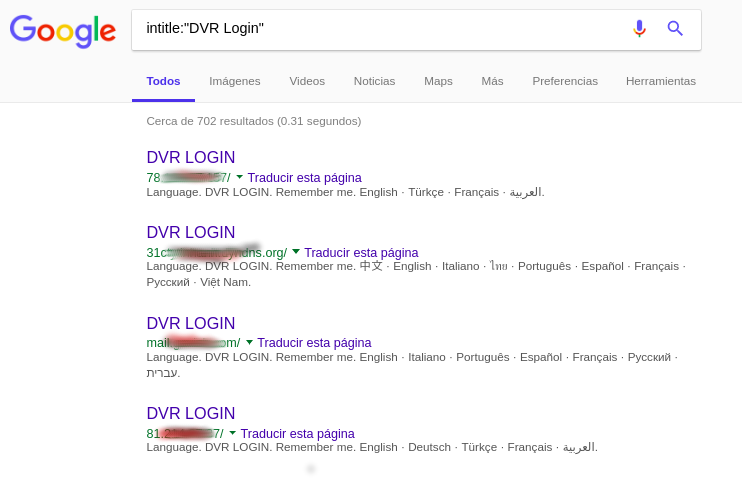 f7p-h4nn1b4l/cve-2018-9995-dvr-credentials-extractor
This project demonstrates the publicly disclosed CVE-2018-9995 vulnerability found in multiple embedded DVR devices.
 d6fault/cve-2026-95675
Python PoC exploiting CVE-2026-95675, an unauthenticated root command injection in D-Link DAP-1360 RevB firmware via a hardcoded auth-bypass and the…
 tothi/pwn-hisilicon-dvr
Proof-of-concept exploit and vulnerability disclosure for HiSilicon hi3520d DVR/NVR devices. Demonstrates RCE via web interface, backdoor…
 duality084/cve-2023-33381-mitrastar-gpt-2741gnac
Proof-of-concept exploit for OS command injection (CVE-2023-33381) in MitraStar GPT-2741GNAC routers. Demonstrates bypass of restricted shell via…
 badnack/d_link_880_bug
CVE-2017-14948 for D-Link 880 Firmware
 murrez/cve-2026-13249
Unauthenticated arbitrary file upload on Honeywell PD45 web admin (firmware F10.19.010040–before F10.22.030745) leading to RCE. Python check/exploit…
 hellkkid/cve-2026-56718
AJCloud AJY IPC Firmware Path Traversal via jdbhttpd
 kemrec/cve-2025-11142-axis-mediaclip-rce
Proof-of-concept and technical analysis for CVE-2025-11142, an authenticated OS command injection in AXIS VAPIX mediaclip.cgi, with time-based and…
 hackspeak/cve-2026-94095
PoC for CVE-2026-94095, a traceroute command injection in Netcore NBR200V2 firmware via ubus JSON-RPC, enabling root RCE for authorized testing.
 varangamin/cve-2017-6206
The DGS-1510 Websmart switch series firmware has been found to have security vulneratiblies. The vulnerabilities include unauthenticated command…
 leonardobg/cve-2022-24654
Proof-of-concept exploit for authenticated stored cross-site scripting (XSS) vulnerability in INTELBRAS ATA 200 firmware 74.19.10.21, targeting the…
 234329a423853/cve-2021-4045
CVE-2021-4045 CVE-2021-4045 is a Command Injection vulnerability that allows Remote Code Execution in the TP-Link Tapo c200 IP camera. It affects all…