
CVE-2024-4157-SSRF-RCE-Reverse-Shell
 ch4os1/cve-2024-4157-ssrf-rce-reverse-shell
Chaining Havoc C2 SSRF with RCE to get reverse shell on Havoc C2 Server.
command-and-controlexploitationpayload-development+3
ch4os1/cve-2024-4157-ssrf-rce-reverse-shellChaining Havoc C2 SSRF with RCE to get reverse shell on Havoc C2 Server.
 jarm222/cve-2025-26244
The graph functionality of DeimosC2 v1.1.0-Beta is vulnerable to Stored Cross-Site Scripting (XSS), allowing the theft of session cookie and…
 azefzafyoussef/cve-2026-34621
Research PoC demonstrating a prototype pollution and JavaScript injection chain in Adobe Acrobat Reader, enabling privileged JavaScript execution and…
 yrkuo/cve-2022-30190
Step-by-step reproduction guide for CVE-2022-30190 (Follina) MSDT remote code execution vulnerability, including malicious document creation and C2…
 cerberusmrxi/cerberus-react2shell-scanner-exploit
Elite exploitation toolkit for CVE-2025-55182 (React Server Components RCE). Async polymorphic payloads, advanced WAF/CDN bypass, proxy rotation,…
 felisha-elmer/sandbox-challenge-spring4shell-cve-2022-22965-
Step-by-step walkthrough of exploiting CVE-2022-22965 (Spring4Shell) with Metasploit, deploying a C2 listener, and mitigating the vulnerability by…
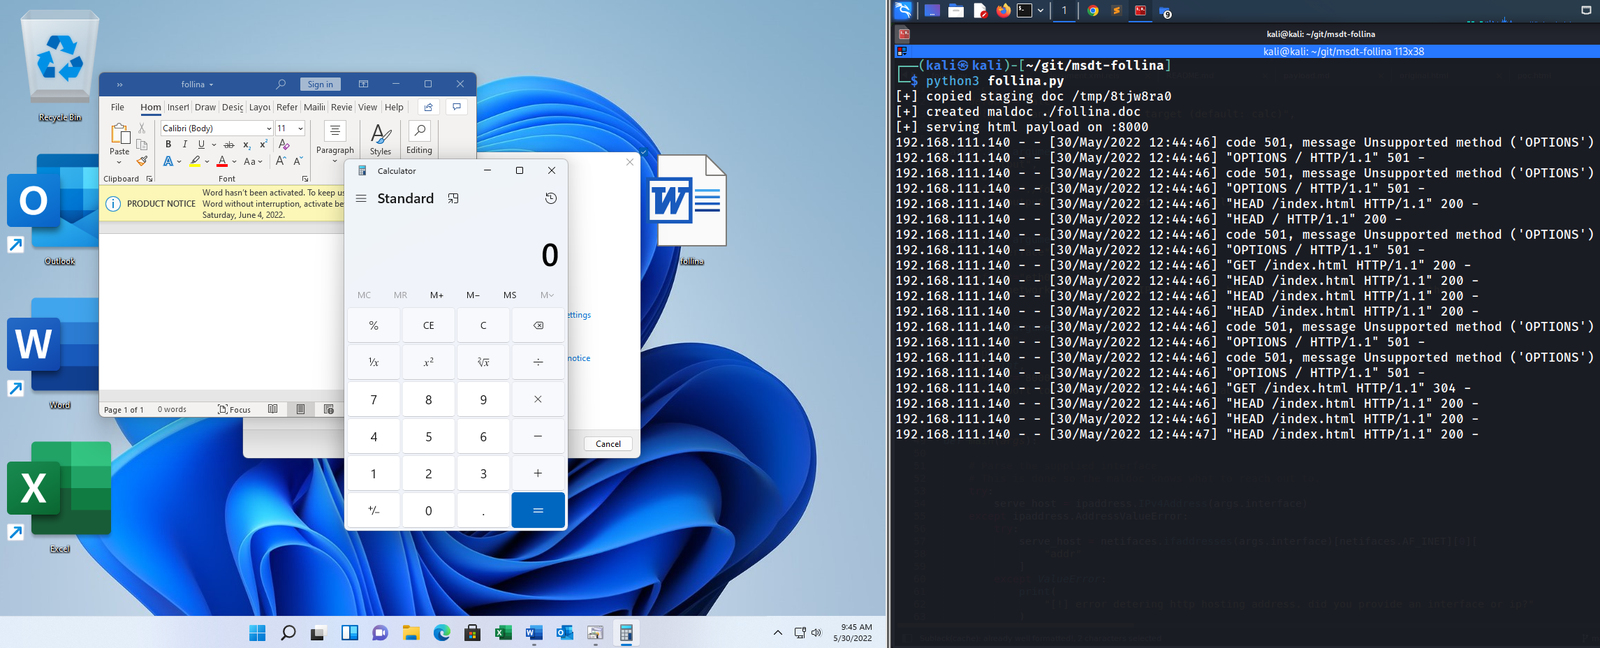 johnhammond/msdt-follina
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…
 komomon/cve-2022-30190-follina-office-msdt-fixed
Modified CVE-2022-30190 exploit tool for MS-MSDT Office RCE with custom docx template support, binary/command execution modes, and embedded HTTP…
 aiminsun/cve-2021-36260
command injection vulnerability in the web server of some Hikvision product. Due to the insufficient input validation, attacker can exploit the…
 absholi7ly/poc-cve-2025-24813
his repository contains an automated Proof of Concept (PoC) script for exploiting **CVE-2025-24813**, a Remote Code Execution (RCE) vulnerability in…
 lnxg33k/webhandler
Bash simulator to control a server using PHP system functions.
 n1k0la-t/cve-2023-36745
Proof-of-concept exploit for Microsoft Exchange Server RCE vulnerability CVE-2023-36745, enabling remote code execution via authenticated PowerShell…
 jas502n/cve-2018-3191
Exploit for CVE-2018-3191 targeting Oracle WebLogic Server via T3 protocol, enabling unauthenticated remote code execution with JNDI payload…
 w01fh4cker/cve-2024-22120-rce
Time Based SQL Injection in Zabbix Server Audit Log --> RCE
 jas502n/cve-2020-2551
Proof-of-concept exploit for CVE-2020-2551, demonstrating remote code execution in Oracle WebLogic Server via the IIOP protocol. Includes default…
 dinhbaouit/cve-2021-26084
Exploit for CVE-2021-26084 targeting Confluence Server OGNL injection vulnerability for unauthenticated remote code execution.
 zeyad-azima/cve-2024-27348
Apache HugeGraph Server RCE Scanner ( CVE-2024-27348 )
 fatguru/cve-2025-55182-scanner
A non-intrusive surface scanner for CVE-2025-55182 (React Server Components RCE). Detects exposed RSC endpoints in React 19 and Next.js applications