cve-2022-42889-text4shell-docker

Dockerized vulnerable Java application demonstrating CVE-2022-42889 (Text4Shell) remote code execution via Apache Commons Text string lookups, for…

Dockerized vulnerable Java application demonstrating CVE-2022-42889 (Text4Shell) remote code execution via Apache Commons Text string lookups, for…

Deliberately vulnerable Apache Solr application (CVE-2021-44228) for practicing Log4Shell exploitation via User-Agent, POST, and admin endpoints.…

Automated SQL injection detection and exploitation tool for extracting database information from web applications, supporting multiple injection…

Security research & exploitation analysis of CVE-2025-55182 (React) — CVSS + OWASP Top 10 mapping

A Remote Code Execution PoC for Log4Shell (CVE-2021-44228)

CVE Description

Command line tool to fetch, decode, brute-force and craft session cookies of a Flask application by guessing secret keys.

一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

WARNING: This is a vulnerable application to test the exploit for the Spring Break vulnerability (CVE-2017-8046). Run it at your own risk!

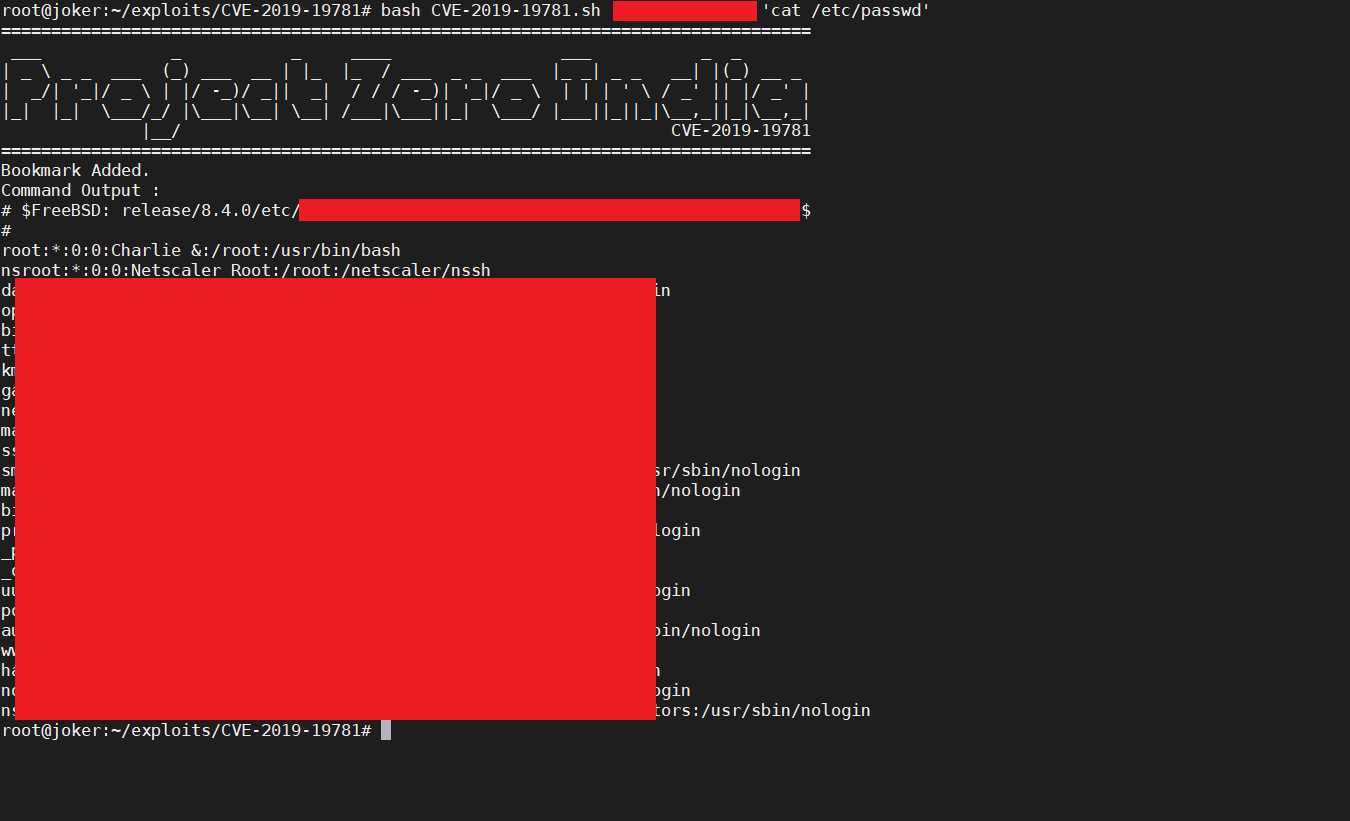
Remote Code Execution Exploit for Citrix Application Delivery Controller and Citrix Gateway [ CVE-2019-19781 ]

Damn Vulnerable C# Application (API)

A purposely vulnerable application in order to demonstrate PHP payload smuggling techniques for PNG files.

Exploit a vulnerable Spring application with the Spring4Shell (CVE-2022-22965) Vulnerability.

Vulnerable demo application for the race condition

PoC for CVE-2016-1000027

Spring Cloud Function Vulnerable Application / CVE-2022-22963

[CVE-2019-8389] An exploit code for exploiting a local file read vulnerability in Musicloud v1.6 iOS Application

A simple application that shows how to exploit the CVE-2022-42889 vulnerability