
CVE-2020-9496
 ambalabanov/cve-2020-9496
XML-RPC request are vulnerable to unsafe deserialization and Cross-Site Scripting issues in Apache OFBiz 17.12.03
exploitationpayload-generationpenetration-testing+3
ambalabanov/cve-2020-9496XML-RPC request are vulnerable to unsafe deserialization and Cross-Site Scripting issues in Apache OFBiz 17.12.03
 mbanyamer/cve-2026-26335-calero-verasmart-rce
Automated exploit for CVE-2026-26335, a critical unauthenticated RCE in Calero VeraSMART via forged ASP.NET ViewState using static machine keys.…
 p4x1s/cve-2023-23638-tools
Exploit tool for CVE-2023-23638, providing automated exploitation and payload generation for targeted vulnerability assessment and penetration…
 4nuxd/cve-2023-43208
Unauthenticated RCE exploit for CVE-2023-43208 in Mirth Connect via XML deserialization, with version detection, bulk scanning, and interactive PTY…
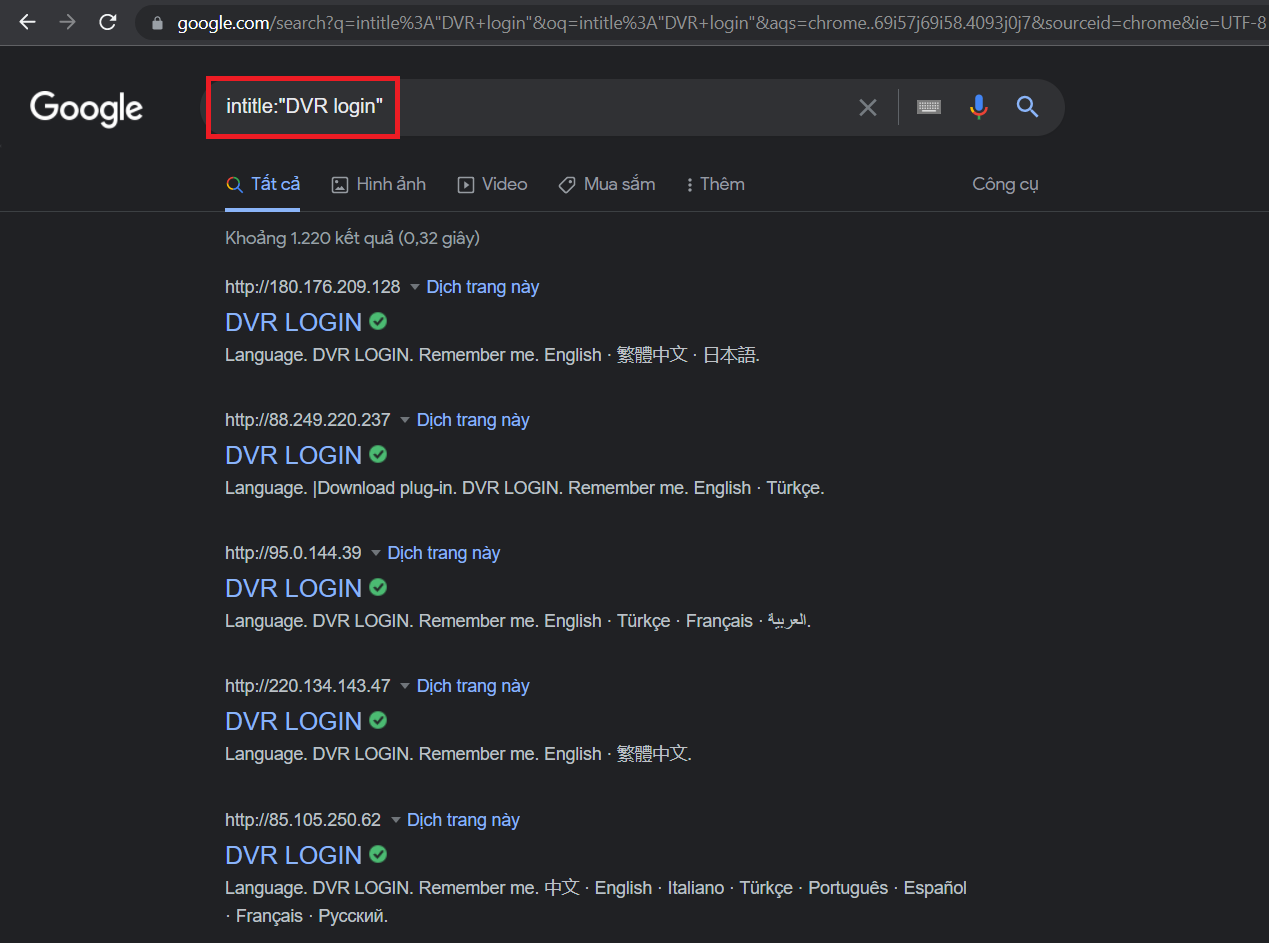 lequockhanh2k/tool_exploit_password_camera_cve-2018-9995
Exploit tool for CVE-2018-9995 that extracts credentials from vulnerable DVR devices via Google dorking and direct IP access.
 zerbaliy3v/cve-2018-6574-exploit
CVE-2018-6574 this vulnerability impacts Golang go get command and allows an attacker to gain code execution on a system by installing a malicious…
 mohandacherir/cve-2021-23639
Exploit of CVE-2021-23639 for the vulnerable library 'md-to-pdf' in JS
 leonardobg/cve-2023-36143
Proof-of-concept exploit for CVE-2023-36143 demonstrating command injection in Maxprint Maxlink 1200G v3.4.11E via the diagnostic tool web interface.
 f01965/cve-2018-5146
Proof-of-concept exploit and custom payload generator for CVE-2018-5146, including crafted OGG POC file and HTML-based exploit with CRC32 calculation…
 0x13-bytezer0/cve-2024-21762
Detects and exploits CVE-2024-21762 pre-authentication RCE in FortiGate SSL VPN, featuring baseline validation, automatic exploitation, ROP…
 ubaydev/cve-2024-10508
Proof-of-concept exploit for CVE-2024-10508: unauthenticated privilege escalation via password recovery bypass in RegistrationMagic WordPress plugin…
 hqdat809/cve-2021-40444
Malicious DOCX generator exploiting CVE-2021-40444 for remote code execution via crafted Office documents, with integrated hosting server for payload…
 d34dun1c02n/cve-2023-31704
Proof-of-concept exploit for CVE-2023-31704: Incorrect access control in Sourcecodester Online Computer and Laptop Store 1.0 allows remote privilege…
 lekosbelas/pdfkit-cmd-injection
Proof-of-concept exploit for CVE-2022-25765 demonstrating command injection in pdfkit 0.8.6 via unsanitized URL parameter, enabling remote code…
 fredbrave/cve-2017-5638-apachestruts2.3.5
A exploit for CVE-2017-5638. This exploit works on versions 2.3.5-2.3.31 and 2.5 – 2.5.10
 fredbrave/cve-2015-6967
An exploit for the Nibbles manager version 4.0.3. This exploit allows RCE to be performed.
 alexfrancow/cve-2020-14882
Proof-of-concept exploit for CVE-2020-14882 in Oracle WebLogic Server, demonstrating remote code execution via crafted HTTP requests to the console…
 rampanic/cve-2019-19609-exploit
Exploit for CVE-2019-19609, a remote code execution vulnerability in a web application, providing proof-of-concept code for security testing.