
CVE-2025-68664-LangGrinch-PoC
 ak-cybe/cve-2025-68664-langgrinch-poc
A testing framework to identify and demonstrate deserialization vulnerabilities in LangChain Core (<0.3.81). Educational use only
ai-securitycode-analysiseducation+6
3
ak-cybe/cve-2025-68664-langgrinch-pocA testing framework to identify and demonstrate deserialization vulnerabilities in LangChain Core (<0.3.81). Educational use only
 ludy-dev/phpunit_eval-stdin_rce
(CVE-2017-9841) PHPUnit_eval-stdin_php Remote Code Execution
 hackersatyamrastogi/n8n-exploit-cve-2025-68613-n8n-god-mode-ultimate
n8n God Mode Ultimate - CVE-2025-68613 Scanner v1.0.0 ║ ║ Workflow Automation Remote Code Execution
 drackyjr/cve-2025-3248-exploit
A comprehensive Python exploitation framework for testing and demonstrating CVE-2025-3248, a critical unauthenticated remote code execution…
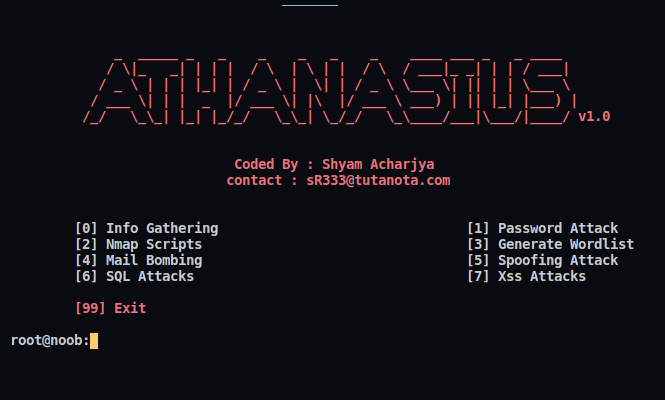 shyam999/athanasius
Framework for penetration testing. The software can identify everything from cross-site scripting to SQL injection. Developers can also use this…
 cved-sources/cve-2015-8103
Docker container for CVE-2015-8103 exploitation targeting JBoss, part of a vulnerable container management framework for security testing.
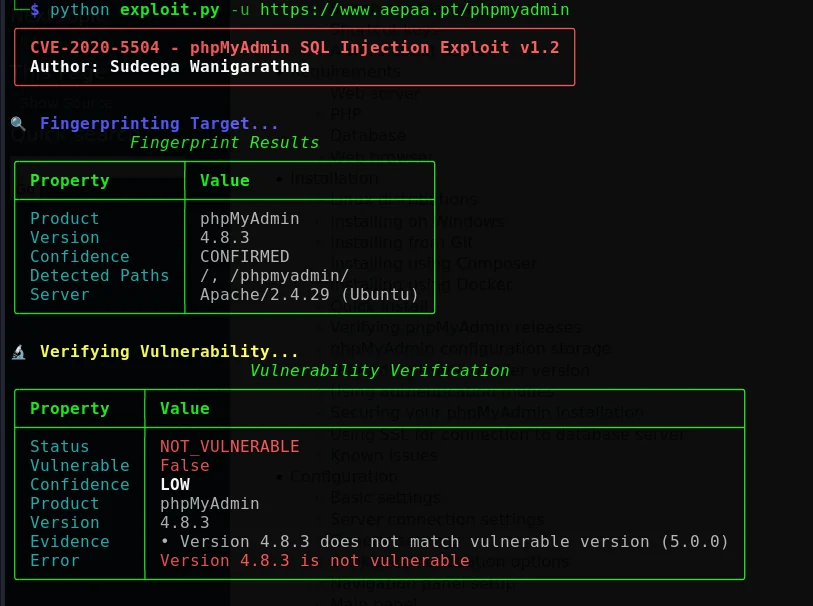 cerberusmrxi/phpmyadmin-cve-2020-5504-exploit
Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…
 alienwithin/owasp-mth3l3m3nt-framework
OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…
 cj-0107/cve-2022-26134
PoC for CVE-2022-26134, a Confluence Server OGNL injection vulnerability, built on the pocsuite3 framework for authorized security testing.
 xmohamed0/cve-2021-21315-poc
Proof-of-concept exploit for CVE-2021-21315, demonstrating remote code execution in a web application framework. Intended for security testing and…
 visionspacetec/offsec-osgi-exploits
Collection of exploits targeting OSGi Java framework versions 3.1.1–3.20 for penetration testing and vulnerability exploitation.
 cved-sources/cve-2018-1273
Docker container for CVE-2018-1273 exploitation lab, part of the Cved vulnerable environment management framework for security training and testing.
 cved-sources/cve-2019-6340
Docker container for CVE-2019-6340 exploitation lab, part of the Cved vulnerable container management framework for practicing Drupal security…
 fairyming/cve-2019-11043
Proof-of-concept exploit for CVE-2019-11043, a PHP-FPM underflow vulnerability, built on the pocsuite framework for automated web application…
 kadamnayan/poc-cve-2024-38820
Proof-of-concept exploit for CVE-2024-38820, demonstrating locale-dependent case conversion bypass of Spring Framework DataBinder disallowedFields…
 lionsec/xerosploit
Efficient and advanced man in the middle framework
 ghostlyrootb2h/cve-2026-82222
Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…
 osungjinwoo/cve-2022-22965
Proof-of-concept exploit and testing scripts for Spring4Shell (CVE-2022-22965), a Spring Framework remote code execution vulnerability, with bash and…