
WordPressMassExploiter
 dmonst3r/wordpressmassexploiter
[discontinued] Mass exploiter of CVE-2015-1579 for WordPress CMS
exploitationinformation-gatheringreconnaissance+3
31
dmonst3r/wordpressmassexploiter[discontinued] Mass exploiter of CVE-2015-1579 for WordPress CMS
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 juanschallibaum/cve-2024-38473-nuclei-template
Nuclei template to detect Apache servers vulnerable to CVE-2024-38473
 ryandamour/crlfmap
CRLFMap is a tool to find HTTP Splitting vulnerabilities
 tin-z/cve-2023-35086-poc
POC of CVE-2023-35086 only DoS
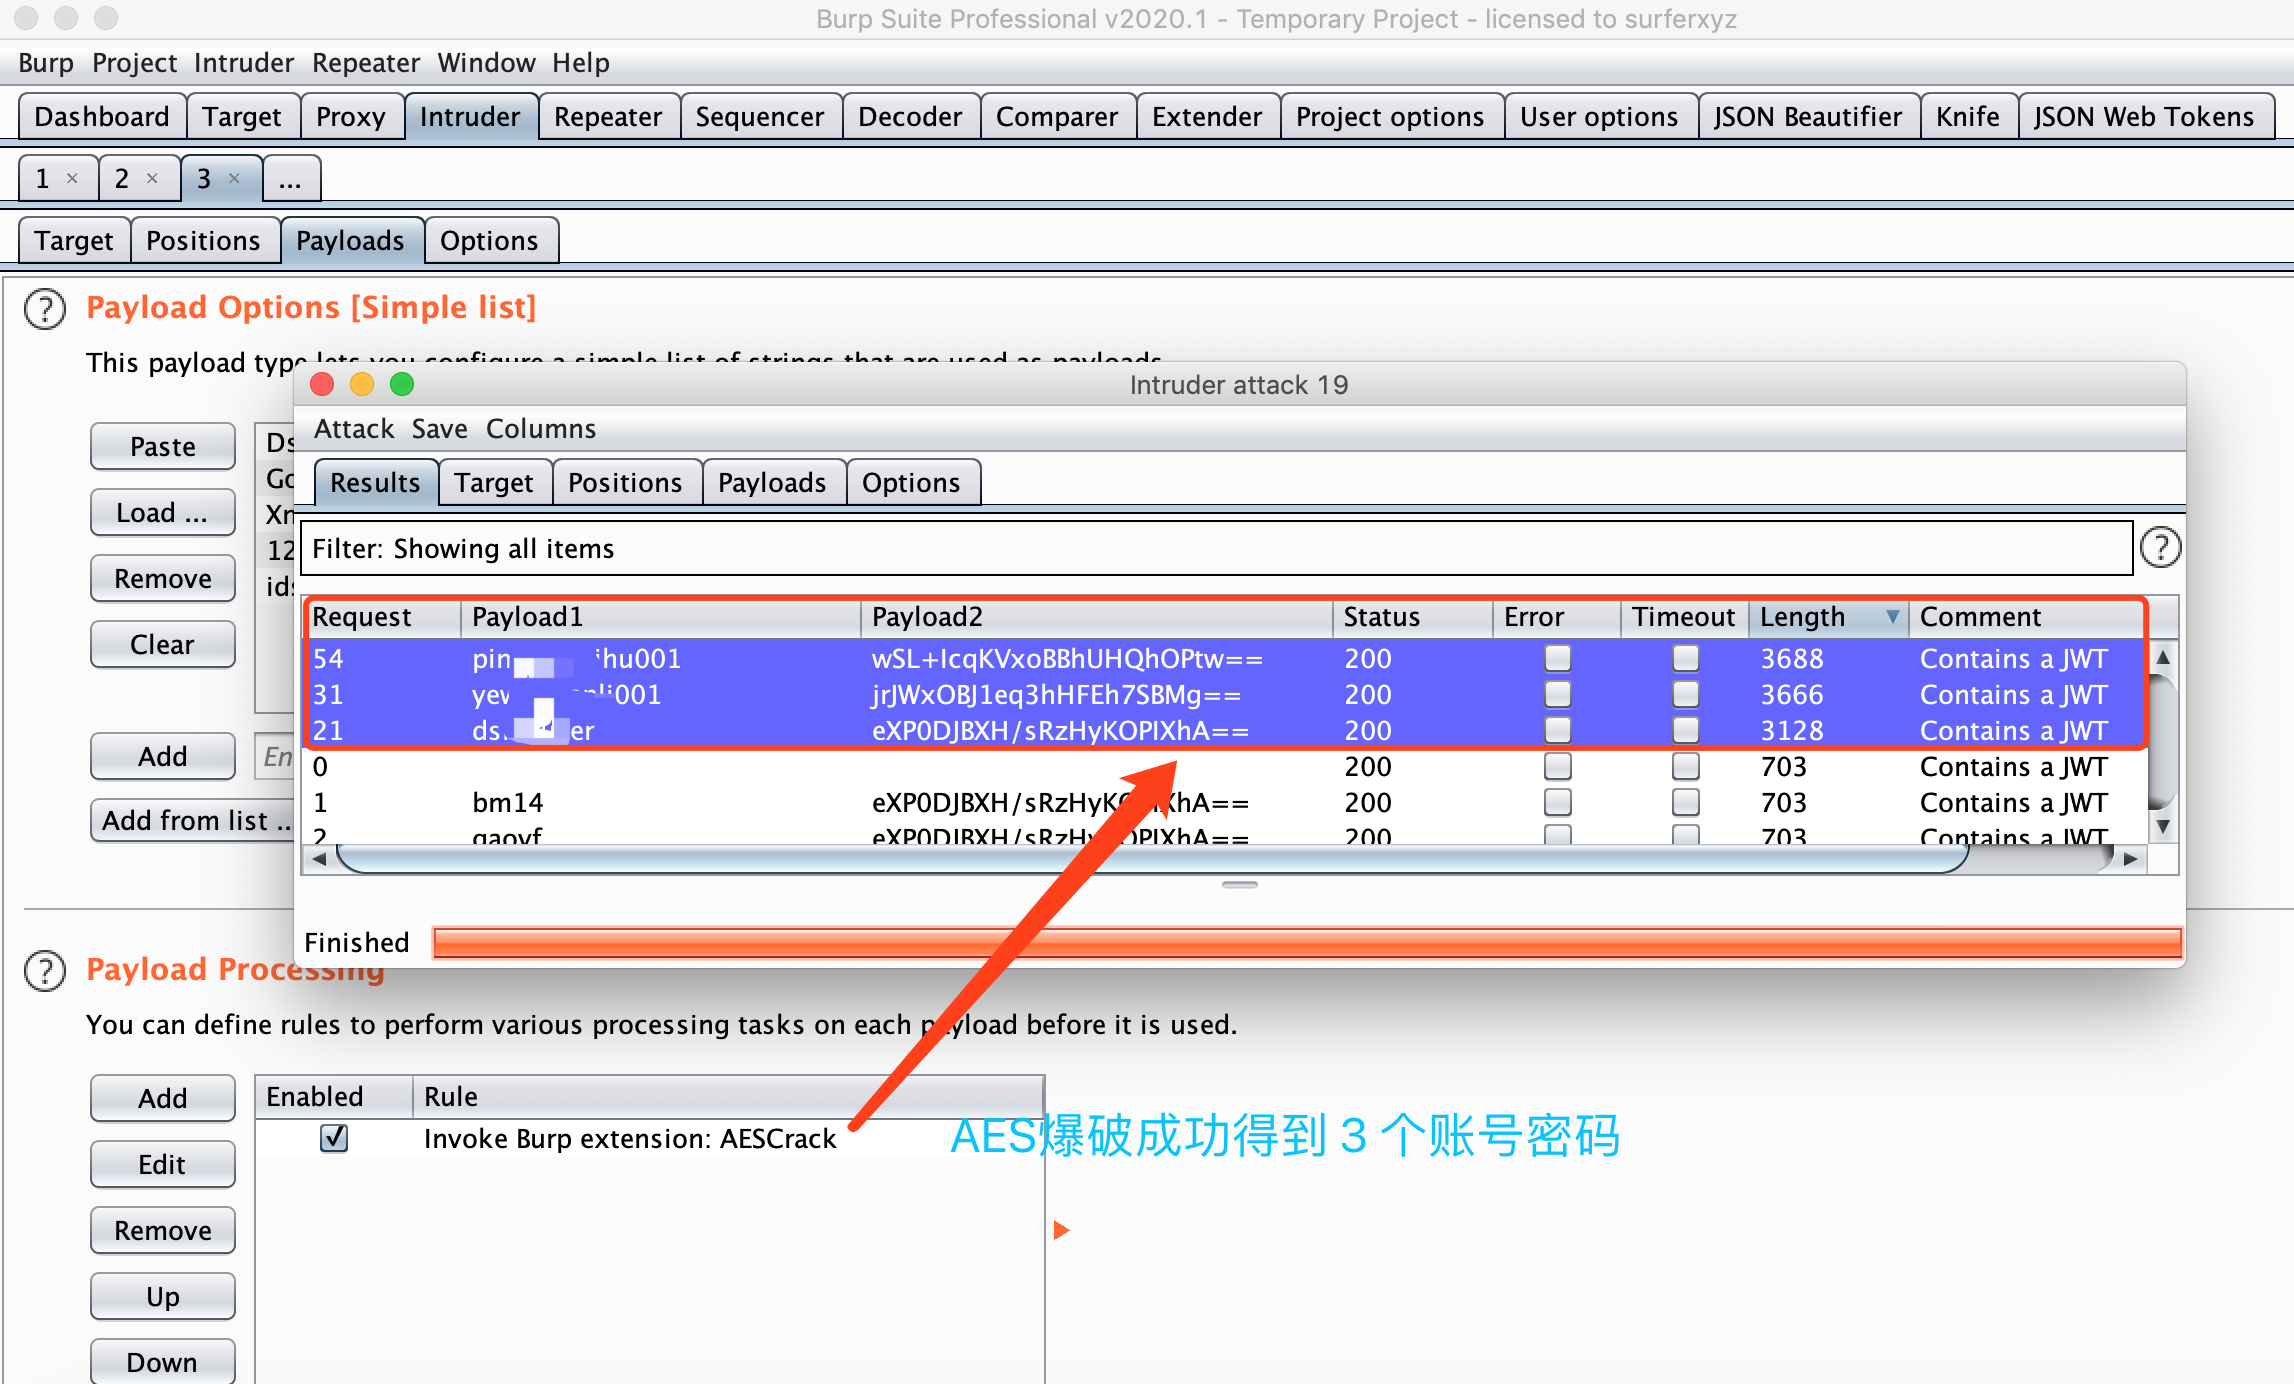 jas502n/burp_aes_plugin
Burpsuite Plugin For AES Crack
 alchemist3dot14/cve-2025-2783
Simulated PoC for CVE-2025-2783 — a sandbox escape vulnerability in Chrome's Mojo IPC. Includes phishing delivery, memory fuzzing, IPC simulation,…
 teycir/apihunter
Async API security scanner in Rust for CORS, CSP, GraphQL, JWT, OpenAPI, and active API posture checks.
 turtlesec-software/crlf-desyncs
Nuclei templates and exploit resources for CRLF based desync attacks
 davkharrr/cve-2026-19478-poc
Proof-of-concept exploit for unauthenticated remote code injection in GitLab's GraphQL API, using crafted queries to modify or delete public projects…
 bountyyfi/azure-apim-cross-tenant-signup-bypass
Security advisory: Azure APIM Developer Portal allows cross-tenant account registration by bypassing UI signup restrictions. Reported to MSRC twice -…
 ut-security/cve-2023-5217-poc
A PoC to trigger CVE-2023-5217 from the Browser WebCodecs or MediaRecorder interface.
 xvnpw/k8s-cve-2021-43557-poc
PoC for CVE-2021-43557
 bishopfox/cve-2022-22274_cve-2023-0656
Proof-of-concept exploit for SonicWall SonicOS stack-based buffer overflows (CVE-2022-22274, CVE-2023-0656) that tests and triggers crashes via…
 m4xsec/apache-apisix-cve-2022-24112
Apache APISIX Remote Code Execution (CVE-2022-24112) proof of concept exploit
 jakabakos/cve-2017-9096-itext-xxe
Proof-of-concept exploit for CVE-2017-9096 demonstrating XML External Entity (XXE) injection in iText PDF library via malicious XMP metadata and form…
 sunn1day/cve-2020-36109-poc
CVE-2020-36109 PoC causing DoS