param-miner
Burp Suite extension that discovers hidden, unlinked parameters using advanced diffing and binary search, enabling detection of web cache poisoning…

Burp Suite extension that discovers hidden, unlinked parameters using advanced diffing and binary search, enabling detection of web cache poisoning…

Efficient and advanced man in the middle framework

40X/HTTP bypasser in Go. Features: Verb tampering, headers, #bugbountytips, User-Agents, extensions, default credentials...


:new: The Multi-Tool Web Vulnerability Scanner.

The Offensive Manual Web Application Penetration Testing Framework.

Vulnerability-specific PoC scripts for discovering and exploiting RCE, SQLi, XXE, SSRF, and unauthorized-access flaws in enterprise web apps and…

An XSS exploitation command-line interface and payload generator.

Self contained htaccess shells and attacks

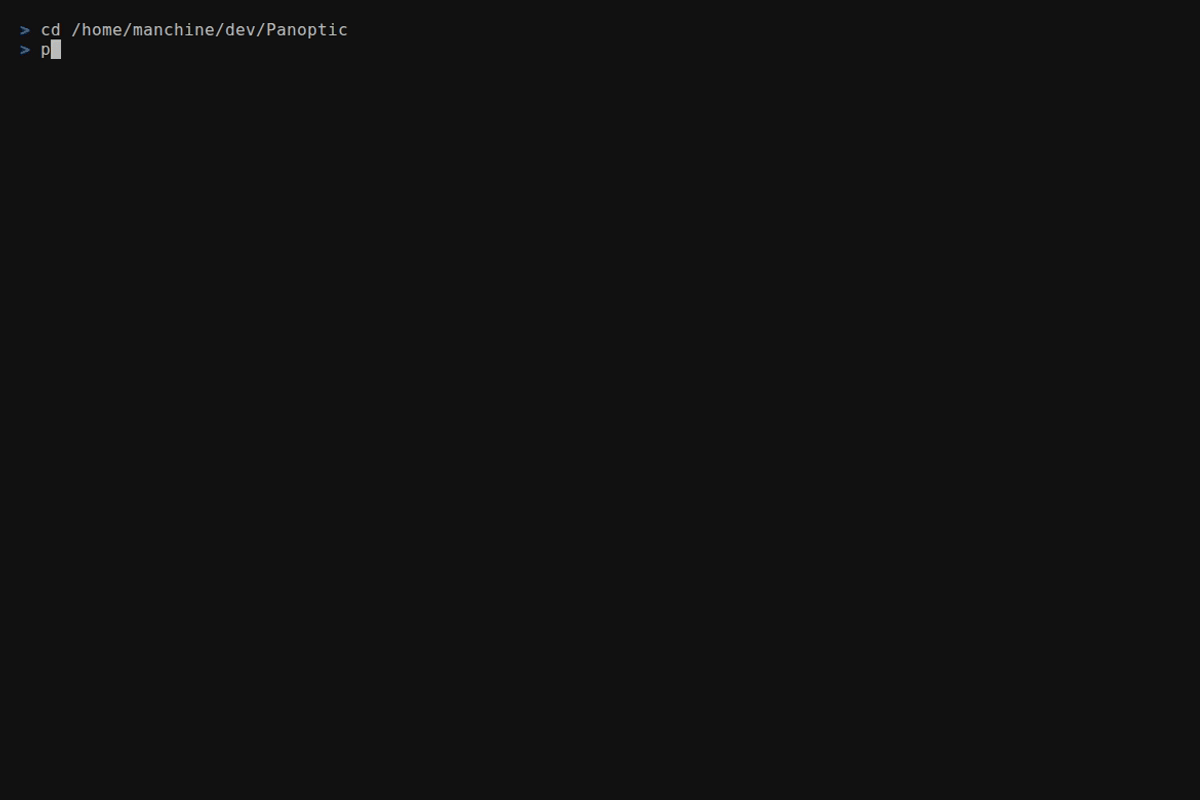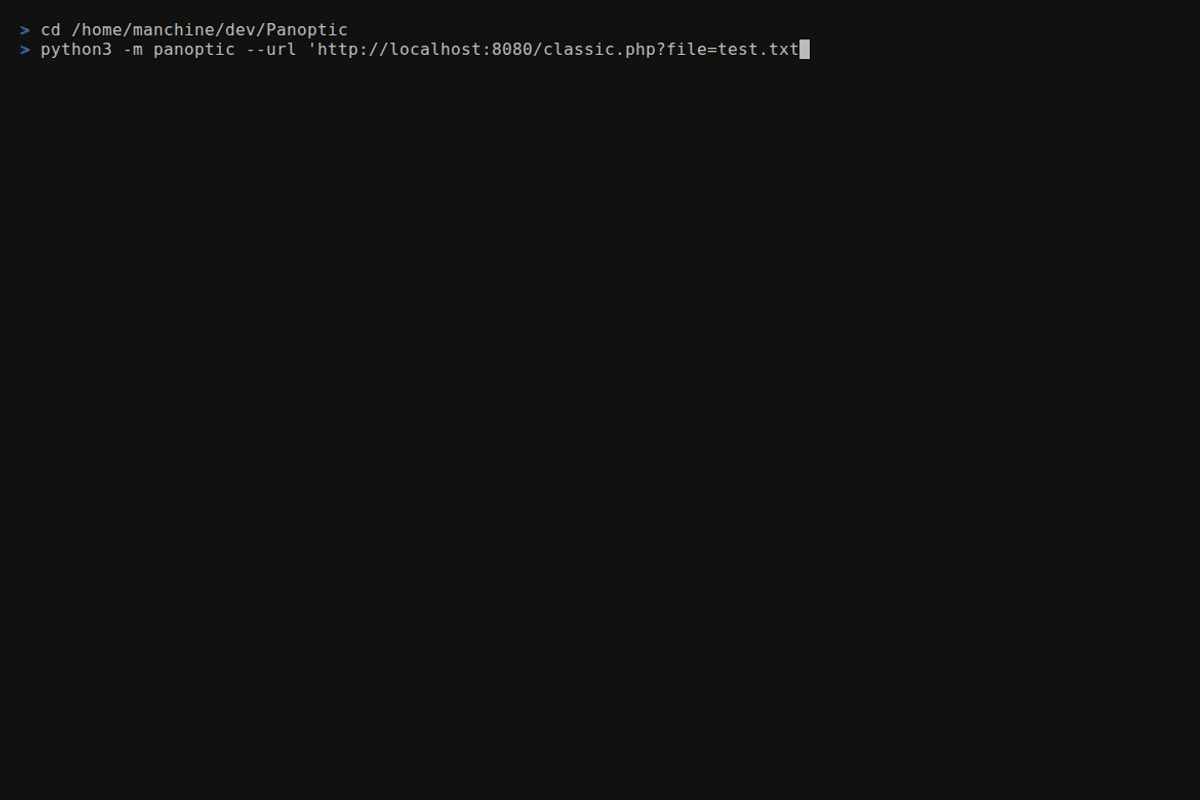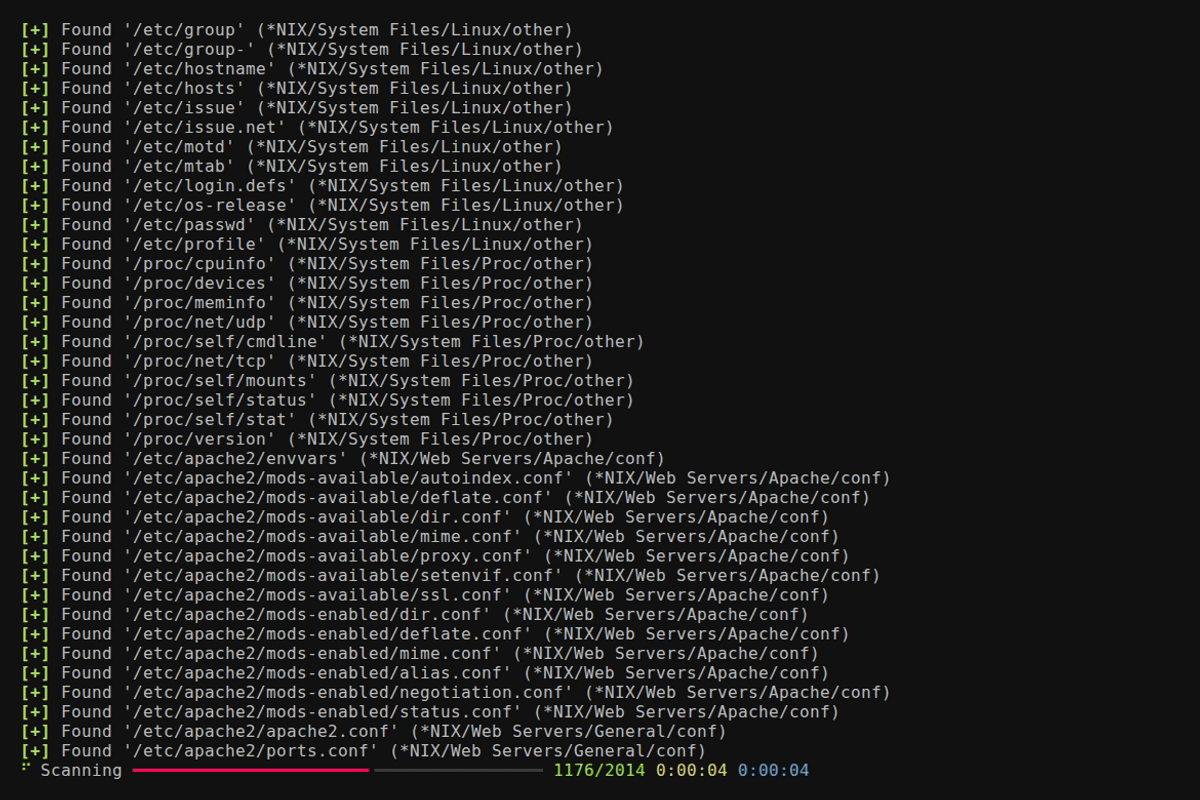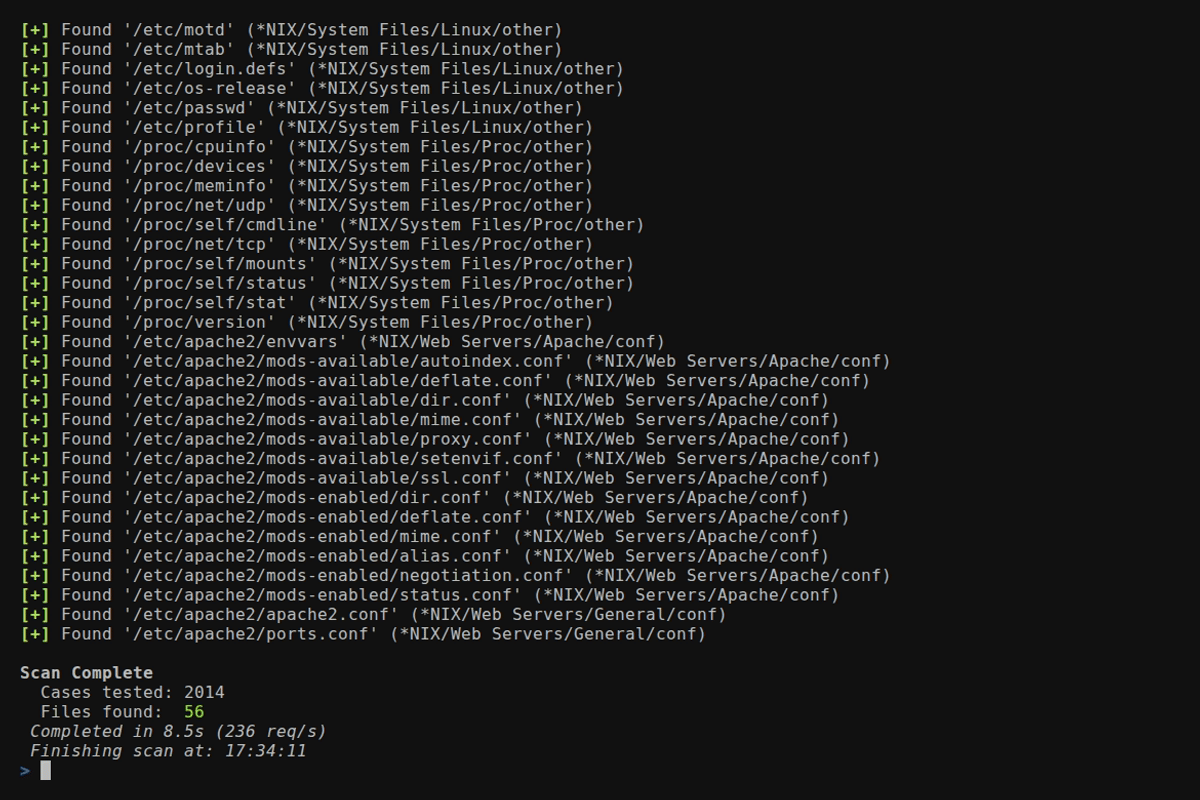
Panoptic is an open source penetration testing tool that automates the process of search and retrieval of content for common log and config files…

Web Application Security Scanner

An automated SSRF finder. Just give the domain name and your server and chill! ;) Also has options to find XSS and open redirects

Perl-based Joomla CMS vulnerability scanner automating version enumeration, component detection, exploit matching, firewall identification, and…

Microsoft-Outlook-Remote-Code-Execution-Vulnerability

DotDotPwn - The Directory Traversal Fuzzer

Wordpress XMLRPC System Multicall Brute Force Exploit (0day) by 1N3 @ CrowdShield

Grafana Unauthorized arbitrary file reading vulnerability

This is a tool published for the Citrix ADC (NetScaler) vulnerability. We are only disclosing this due to others publishing the exploit code first.