
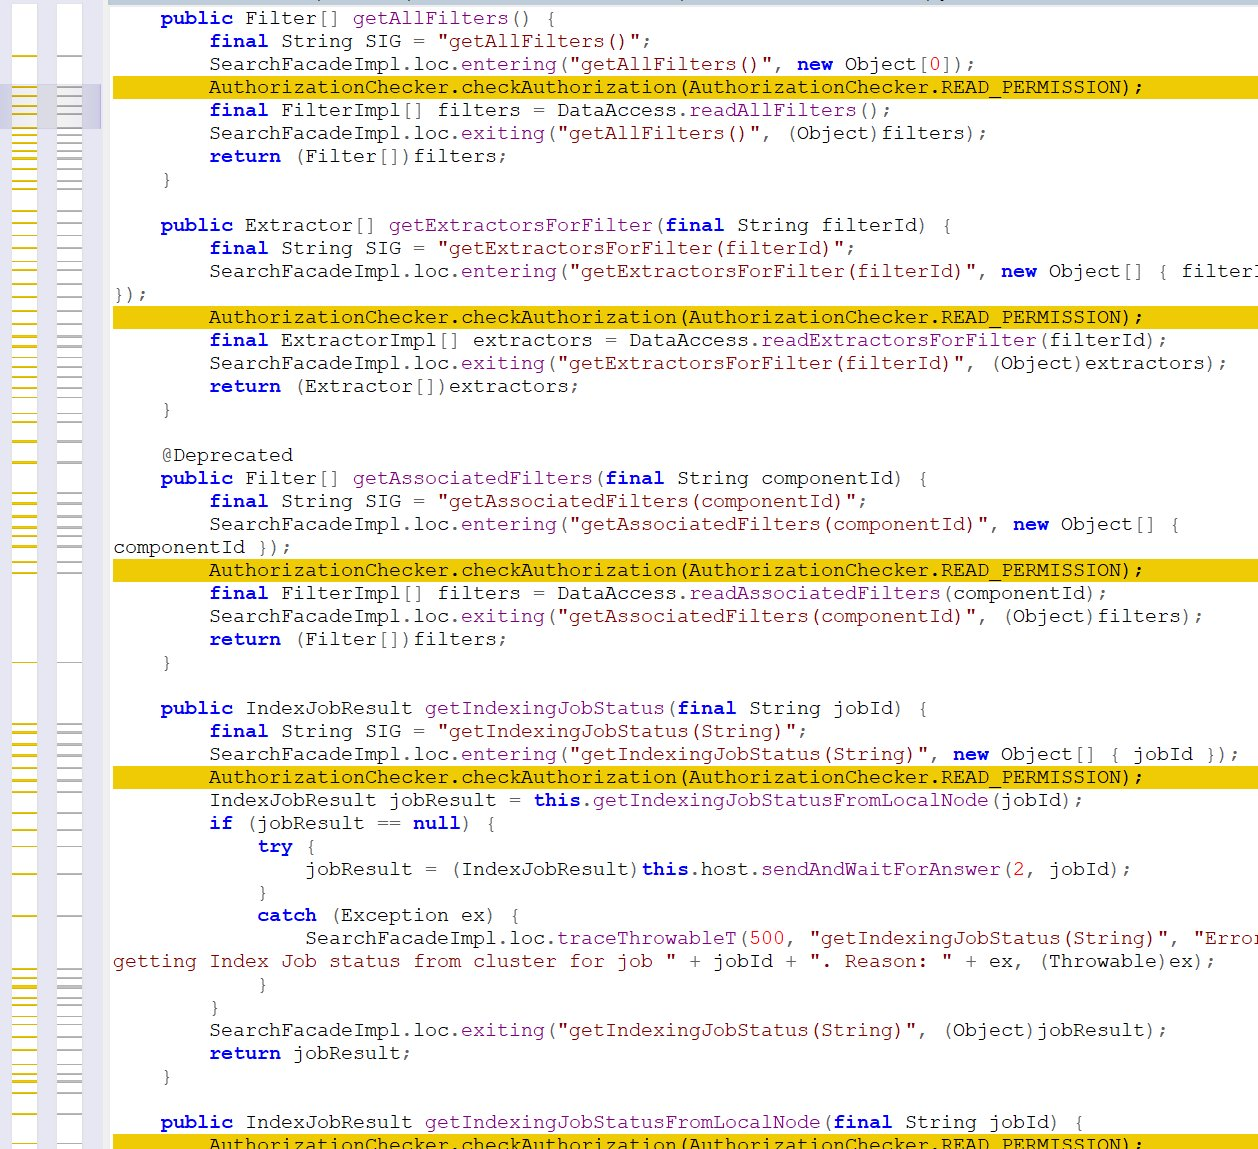
CVE-2022-41272
 redrays-io/cve-2022-41272
Improper access control in SAP NetWeaver Process Integration
exploitationinformation-gatheringpenetration-testing+2
3
redrays-io/cve-2022-41272Improper access control in SAP NetWeaver Process Integration
 chocapikk/cve-2026-39912
Xboard / V2Board Unauth Account Takeover - Magic Link Token Leak (CVE-2026-39912)
 redrays-io/cve-2022-39802
[CVE-2022-39802] File path traversal vulnerability in SAP Manufacturing Execution
 halencarjunior/f5scan
CVE-2020-5902 scanner for F5 BIG-IP with Shodan host discovery, LFI file reading, and remote command execution capabilities.
 pushkarup/cve-2023-23752
Exploit for CVE-2023-23752 (4.0.0 <= Joomla <= 4.2.7).
 halencarjunior/cve-2023-36845
Scanner for CVE-2023-36845 with Shodan and Censys integration for automated host discovery and exploitation of Juniper devices.
 tarantula-team/cve-2019-12543
Proof-of-concept XSS exploit for Zoho ManageEngine ServiceDesk Plus 9.3 via the PurchaseRequest.do serviceRequestId parameter, demonstrating…
 tarantula-team/cve-2019-12542
Proof-of-concept for CVE-2019-12542: XSS vulnerability in Zoho ManageEngine ServiceDesk Plus 9.3 via SearchN.do userConfigID parameter, with a…
 randomrobbiebf/ninja-forms-brute
Exploit for Ninja Forms plugin vulnerability allowing unauthenticated download of submission CSVs to disclose email addresses.
 huyvo2910/cve-2025-25747-hoteldruid-3-0-7-reflected-xss
Reflected XSS vulnerability proof-of-concept for HotelDruid 3.0.7, demonstrating arbitrary JavaScript execution via the ripristina_backup parameter…
 bytereaper77/cve-2025-11077
Exploit blind SQL Injection in (Online Learning Management System)
 manisso/fsociety
fsociety Hacking Tools Pack – A Penetration Testing Framework
 danmcinerney/lans.py
Inject code and spy on wifi users
 tomnomnom/waybackurls
Fetch all the URLs that the Wayback Machine knows about for a domain
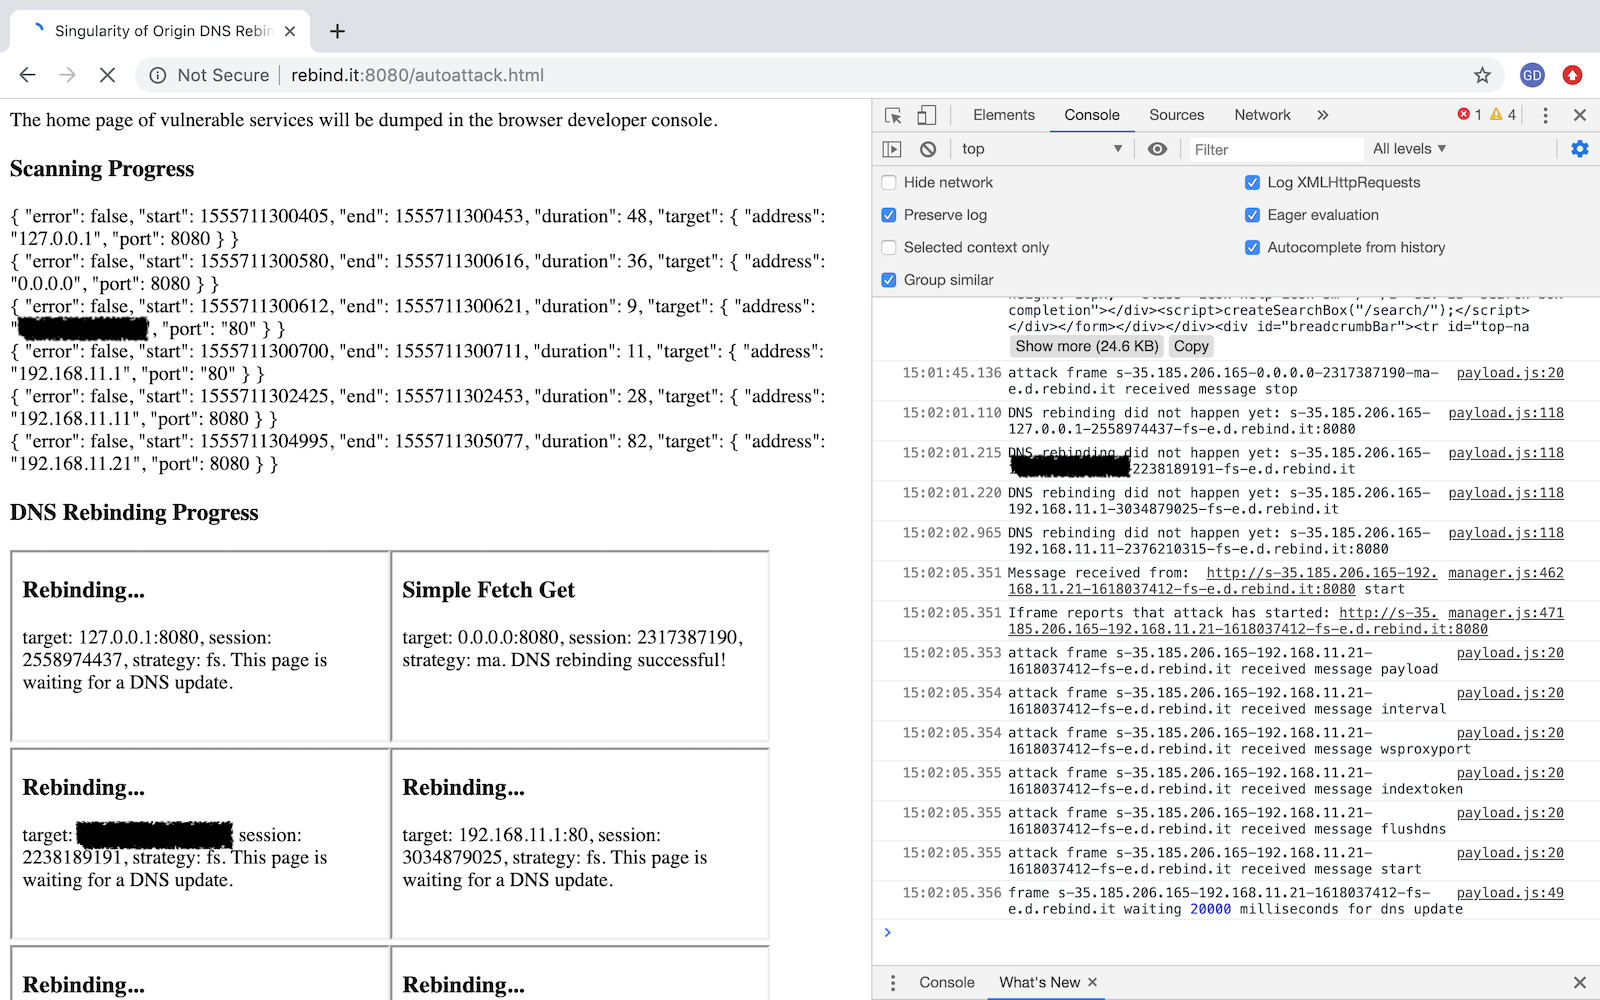 nccgroup/singularity
A DNS rebinding attack framework.
 codingo/nosqlmap
Automated NoSQL database enumeration and web application exploitation tool.
 gquere/pwn_jenkins
Notes about attacking Jenkins servers
 0xn0ne/weblogicscanner
weblogic 漏洞扫描工具。目前包含对以下漏洞的检测能力:CVE-2014-4210、CVE-2016-0638、CVE-2016-3510、CVE-2017-3248、CVE-2017-3506、CVE-2017-10271、CVE-2018-2628、CVE-2018-2893、CVE-20…