
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2022-41272 — Improper access control in SAP NetWeaver Process Integration | Kitploit
Tools/GitHubGitHub/redrays-io/cve-2022-41272
Vulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration Testing
GitHubredrays-io/cve-2022-41272

CVE-2022-41272

Improper access control in SAP NetWeaver Process Integration

View Repository
3103 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2022-41272

On this repository, we will briefly write information about the CVE-2022-41272 vulnerability.

The vulnerability exists on the SAP P4 service that runs on the 5NN04 port. Where NN is an instance number, that can be from 00-99.

There are remote call functions that an attacker can call without any authentication.

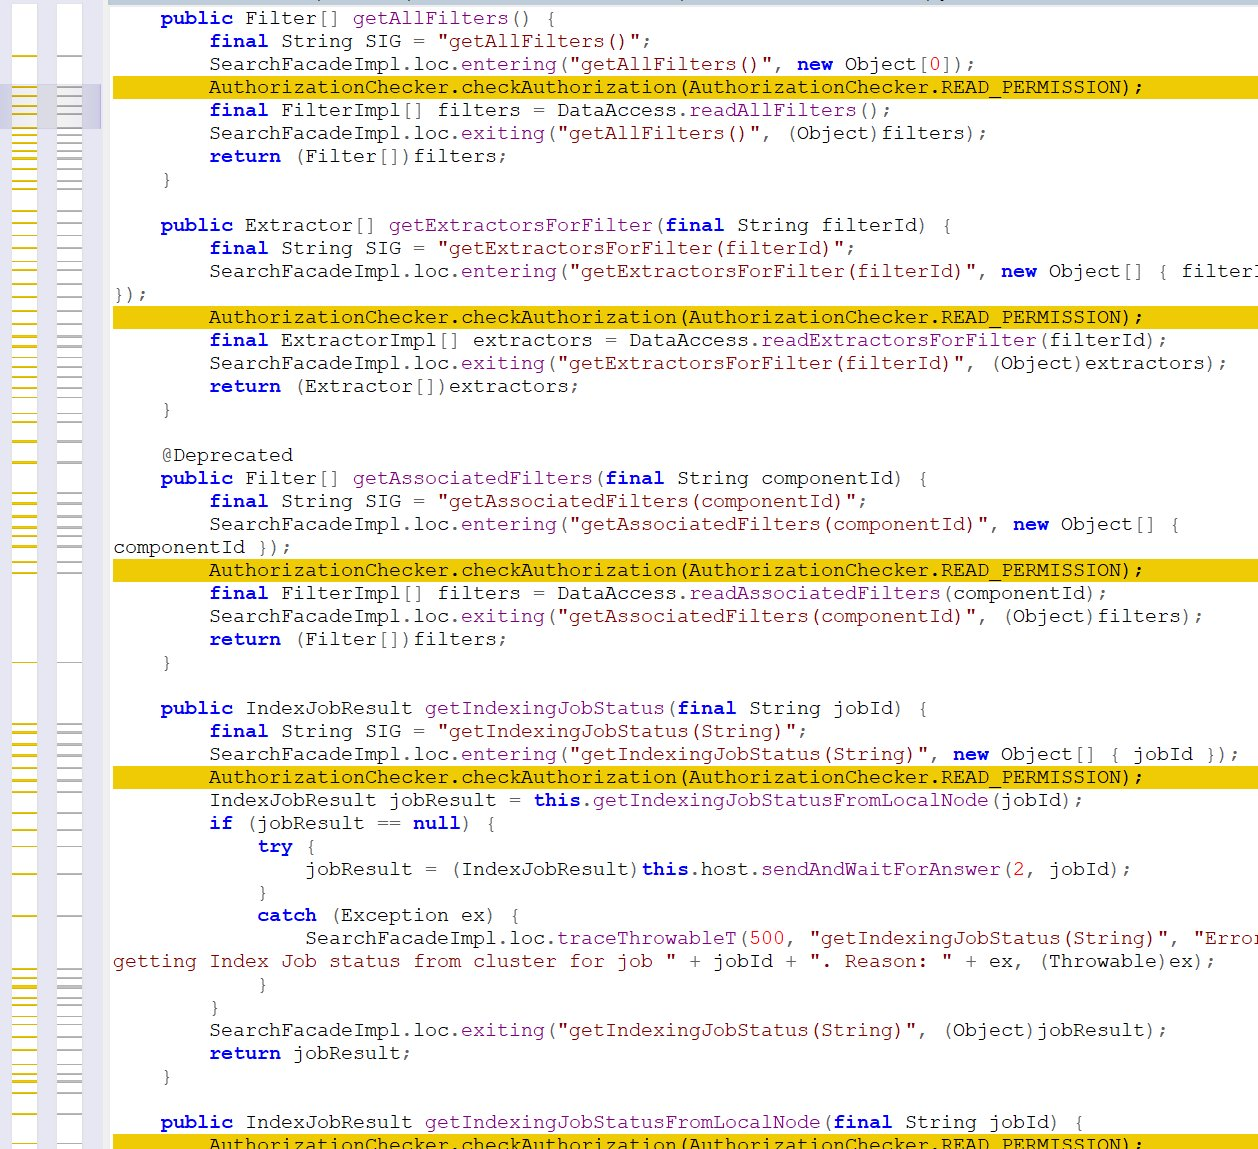
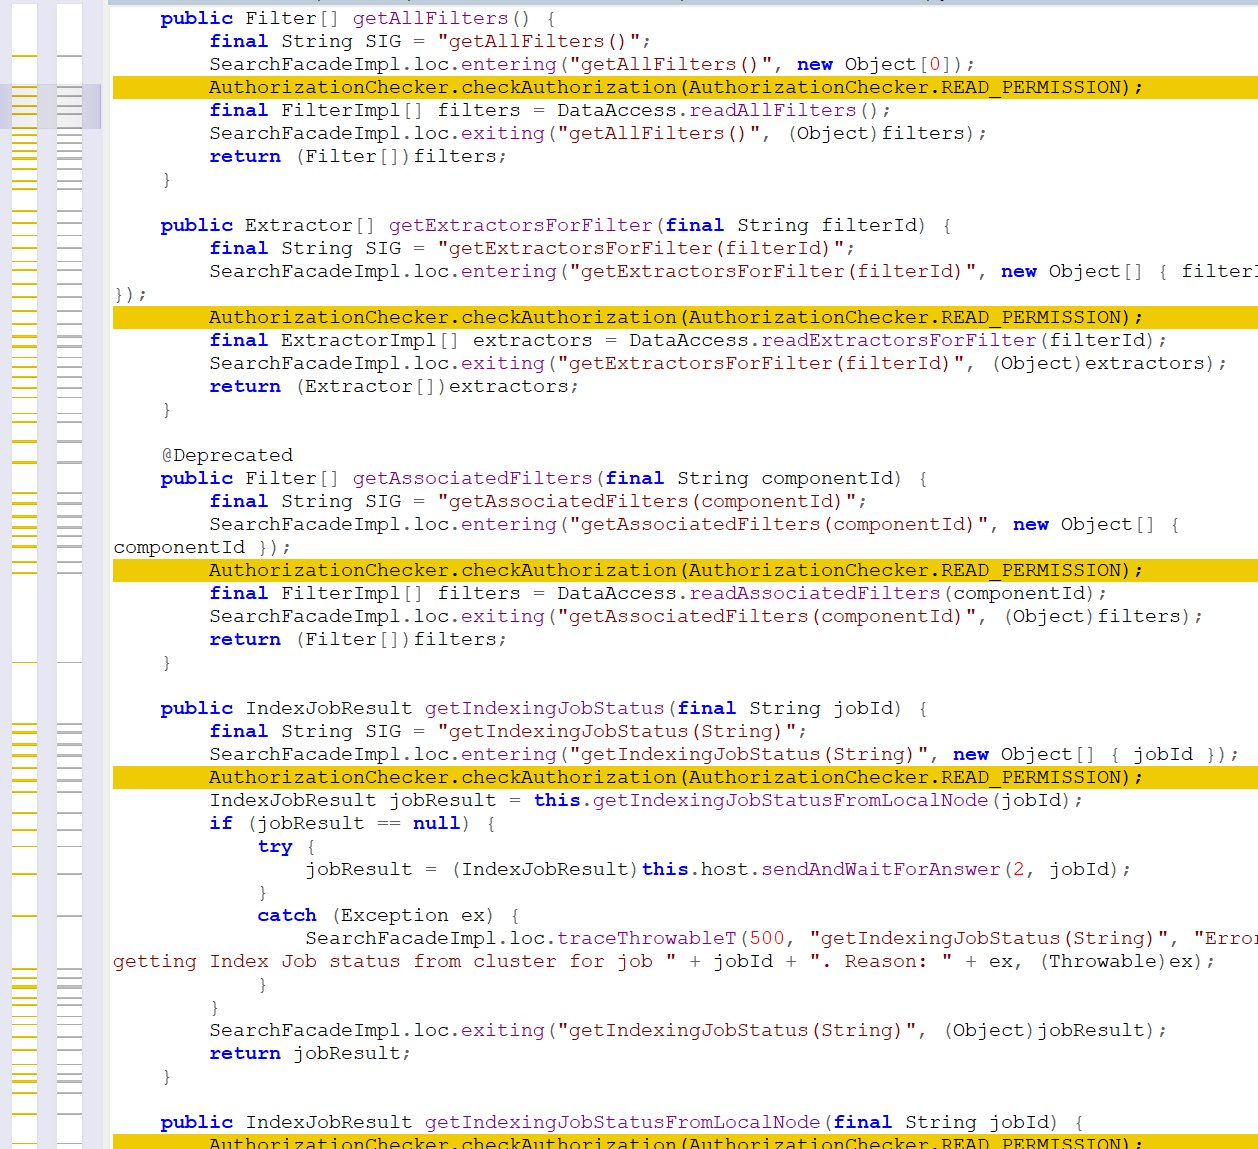
In the following image, you can see the patch released by SAP. image
The PoC is ready and deployed to the RedRays Security Platform.

PS. You can star and start watching the repository, and when we open the PoC, you will receive the notification.

link to original twitt

Download Tool