

LFITester
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
crawlerexploitationfuzzing+7
112
kostas-pa/lfitesterPython3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
 abraxas/cve-2026-19089-woocommerce-tyche
Research repository for CVE-2026-19089, a remote command execution vulnerability in WooCommerce Product Input Fields by Tyche Softwares. Contains…
 schn1tzelme1ster/cve-2025-6002
Python exploit for CVE-2025-6002 targeting authenticated arbitrary file upload in VirtueMart < 4.4.10. Logs in, uploads a PHP webshell, and triggers…
 vozec/cve-2023-22527
Proof-of-concept exploit for CVE-2023-22527, a server-side template injection in Confluence that enables remote code execution. Includes a Python…
 hhesenjan/cve-2023-422-chamilo-lms-rce
Python exploit for CVE-2023-4220 in Chamilo LMS that uploads a file and delivers an unauthenticated reverse shell to a netcat listener.
 motikan2010/cve-2017-8809_mediawiki_rfd
CVE-2017-8809 Docker - RFD(Reflected File Download) for MediaWiki
 dragonked2/cve-2024-50379-poc
This repository contains a Python script designed to exploit CVE-2024-50379, a vulnerability that allows attackers to upload a JSP shell to a…
 krill-x7/cve-2022-25226
Python exploit script for ThinVNC 1.0b1 authentication bypass (CVE-2022-25226) that chains unauthenticated /cmd endpoint access with AMSI bypass and…
 nxploited/cve-2024-50498
Exploit script for CVE-2024-50498 code injection in WordPress WP Query Console that checks vulnerability and delivers a reverse shell.
 minhluannguyen/cve-2020-7247-reproducer
Docker-based environment to reproduce CVE-2020-7247 (OpenSMTPD) with a Python exploit script for arbitrary command execution and reverse shell via…
 y1s4s/cve-2024-36401-poc
Proof-of-concept exploit for CVE-2024-36401 enabling remote code execution via HTTP requests with reverse shell payload generation and Base64…
 wooluo/cve-2022-25581
Python exploit script for CVE-2022-25581 (ClassCMS 2.4 arbitrary file download) that automates login, CSRF token extraction, malicious zip upload…
 arunhatter/cve-2022-31814
This script is a proof-of-concept exploit for pfBlockerNG <= 2.1.4_26 that allows for remote code execution. It takes a single target URL or a list…
 groppoxx/cve-2020-25042-poc
PoC for CVE-2020-25042: automated Mara CMS 7.5 authenticated PHP upload to RCE, with login hash handling, shell reuse, custom payload support, and…
 pwnvader/cve-2026-87902-poc-pwnvader
Shell PoC for CVE-2026-87902, an unauthenticated WordPress core LFI via page-template resolution that chains to RCE through pearcmd.php.
 g01d3nw01f/cve-2015-8351
this script is exploit for wordpress old plugin gwolle
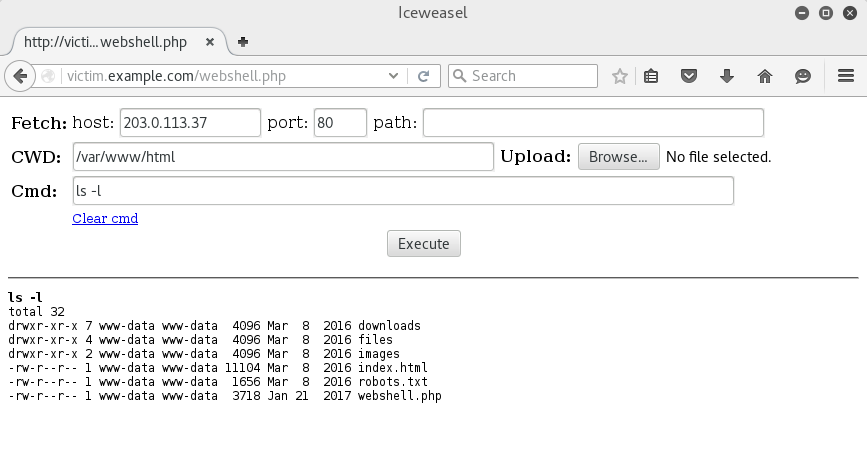 whitewinterwolf/wwwolf-php-webshell
WhiteWinterWolf's PHP web shell
 spidermate/jatayu
Stealthy standalone PHP web shell with HTTP header-based authentication, exec function switching, and undetectable design for remote command…