

SAMLRaider
 compasssecurity/samlraider
SAML2 Burp Extension
api-security-testingauthenticationcryptography+6
compasssecurity/samlraiderSAML2 Burp Extension
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 hackmanit/tinja
TInjA is a CLI tool for testing web pages for template injection vulnerabilities and supports 44 of the most relevant template engines for eight…
 palindromelabs/awesome-websocket-security
Awesome information for WebSockets security research
 lwzsoviet/noxss
Faster xss scanner,support reflected-xss and dom-xss
 lucksec/spring-cloud-gateway-cve-2022-22947
Exploit for CVE-2022-22947: remote code execution in Spring Cloud Gateway via crafted requests to the Actuator endpoint. Includes Python script and…
 dobin/burpsentinel
GUI Burp Plugin to ease discovering of security holes in web applications
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
 moopinger/smugglefuzz
A rapid HTTP downgrade smuggling scanner written in Go.
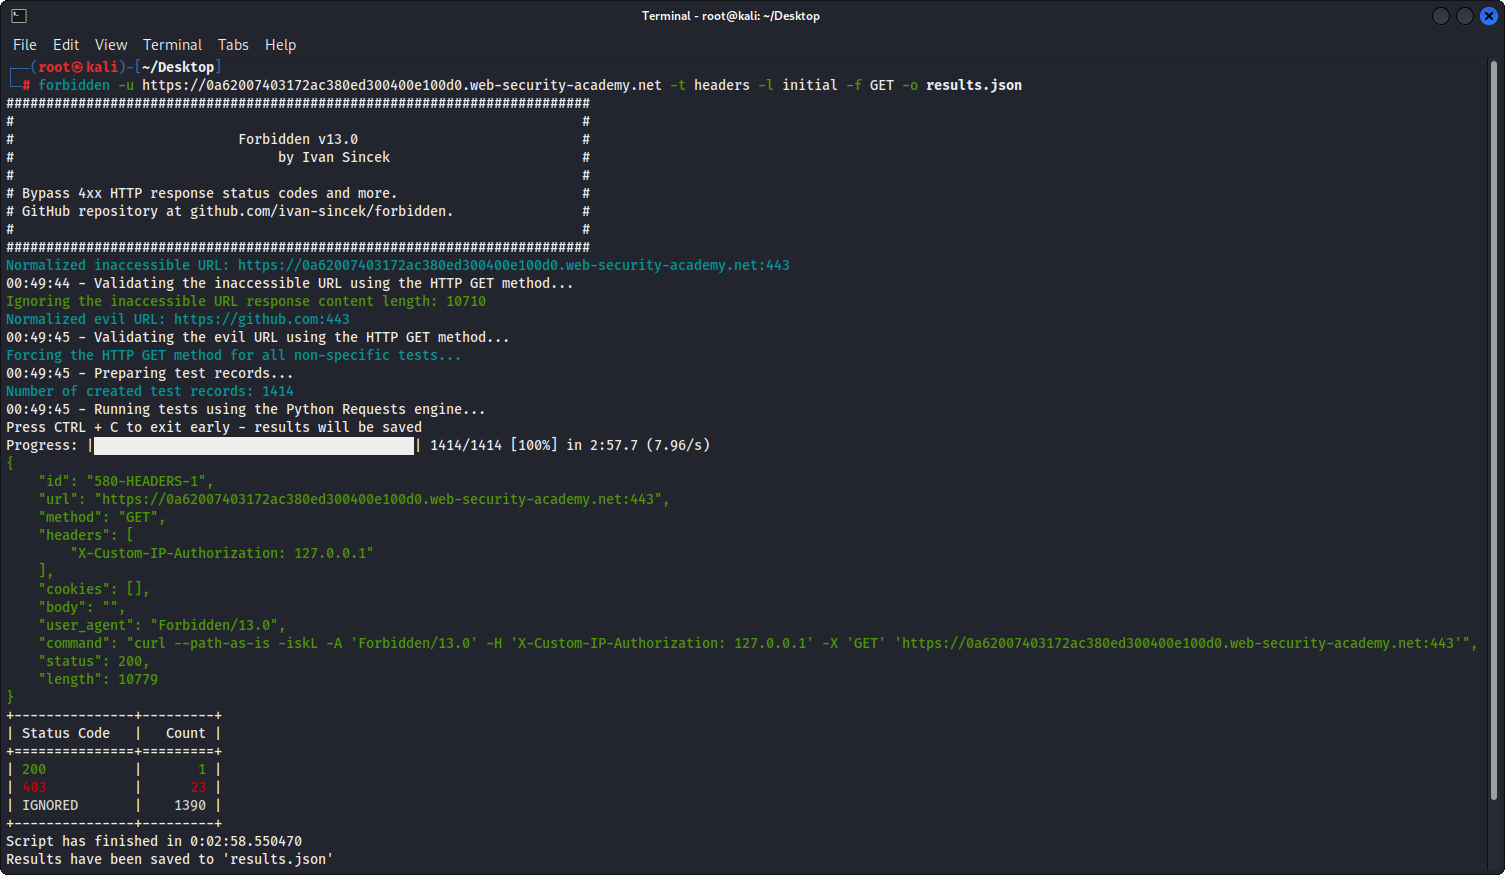 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
 thumpbo/cve-2025-30208-exp
CVE-2025-30208-EXP
 nicholasaleks/crackql
GraphQL penetration testing tool that exploits weak rate limits and cost analysis to brute-force credentials, bypass 2FA, enumerate users, and fuzz…
 ryandamour/ssrfuzz
SSRFuzz is a tool to find Server Side Request Forgery vulnerabilities, with CRLF chaining capabilities
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 takito1812/web-hacking-playground
Web application with vulnerabilities found in real cases, both in pentests and in Bug Bounty programs.
 dmontgomery40/pentest-mcp
NOT for educational purposes: An MCP server for professional penetration testers including STDIO/HTTP/SSE support, nmap, go/dirbuster, nikto, JtR,…
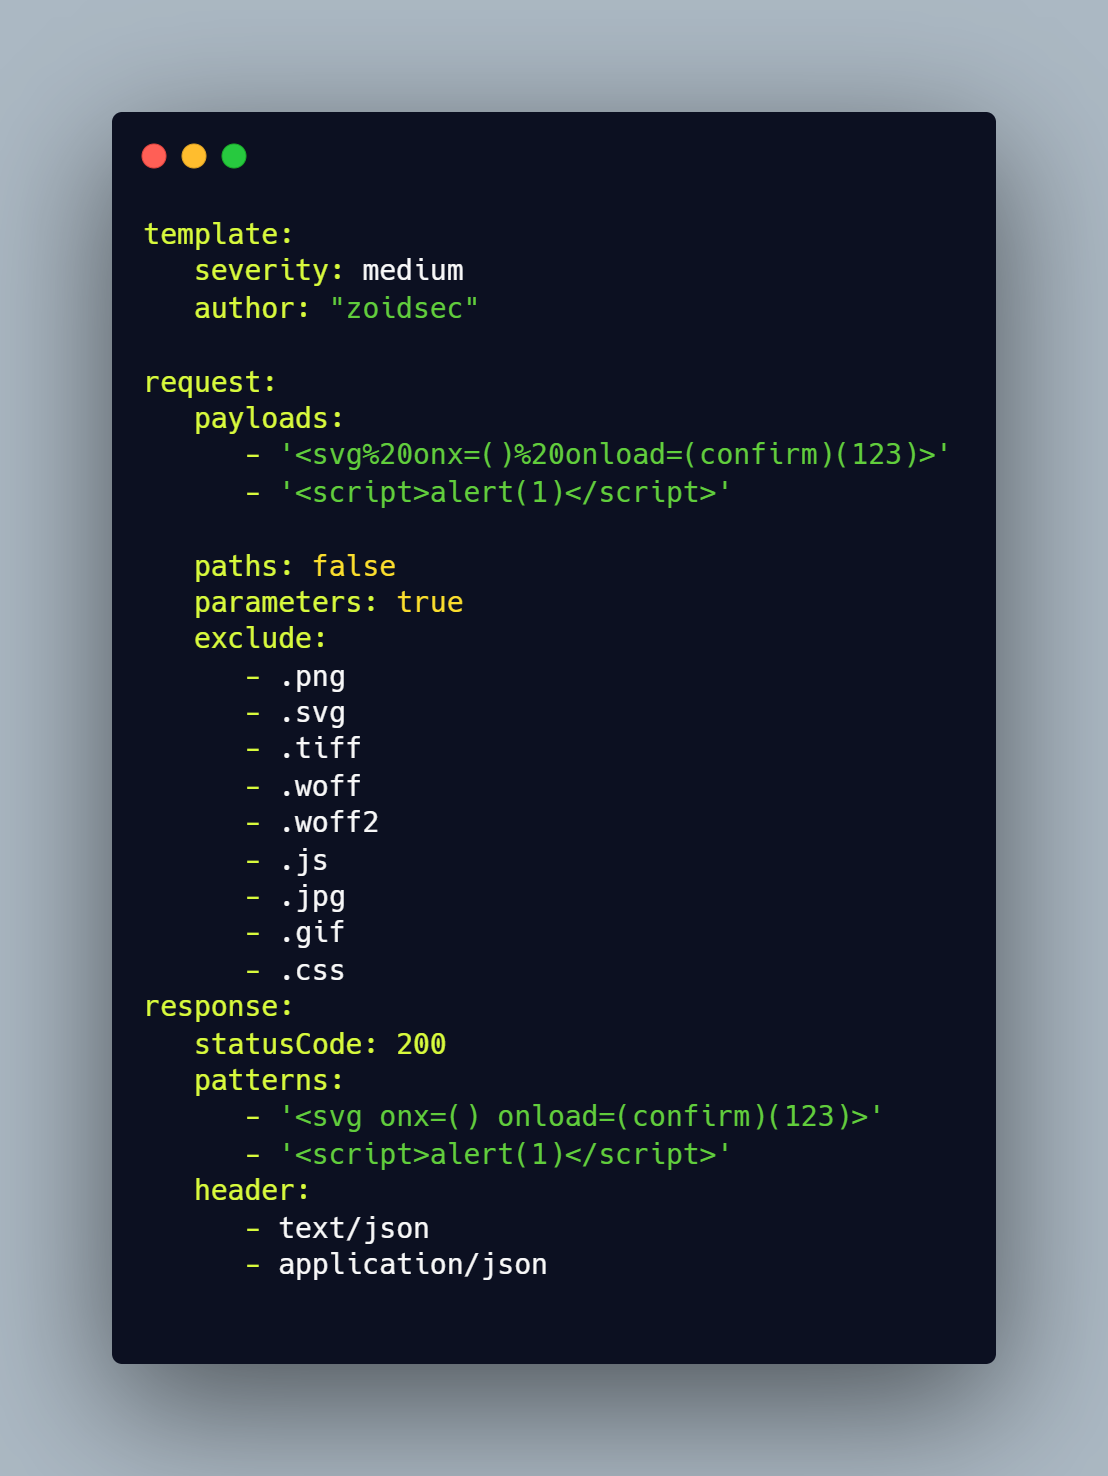 ethicalhackingplayground/erebus
Erebus is a fast tool for parameter-based vulnerability scanning using a Yaml based template engine like nuclei.
 bitthebyte/eagle
Multithreaded Plugin based vulnerability scanner for mass detection of web-based applications vulnerabilities