
 lobuhi/byp4xx
40X/HTTP bypasser in Go. Features: Verb tampering, headers, #bugbountytips, User-Agents, extensions, default credentials...
 ssl/ezxss
Blind XSS detection and exploitation platform with persistent sessions, reverse proxy, and automated information gathering for penetration testers…
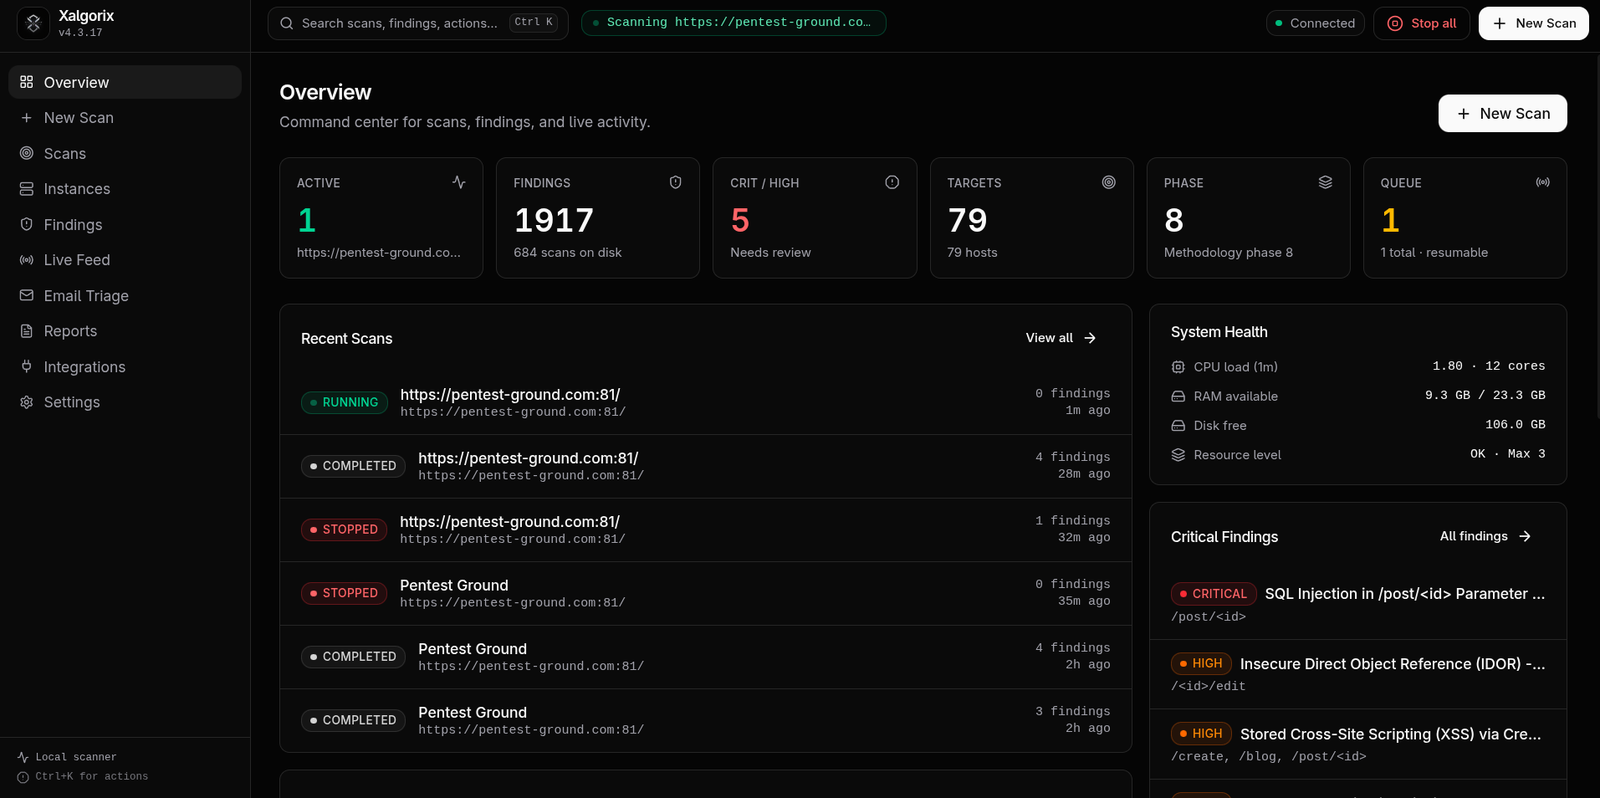 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
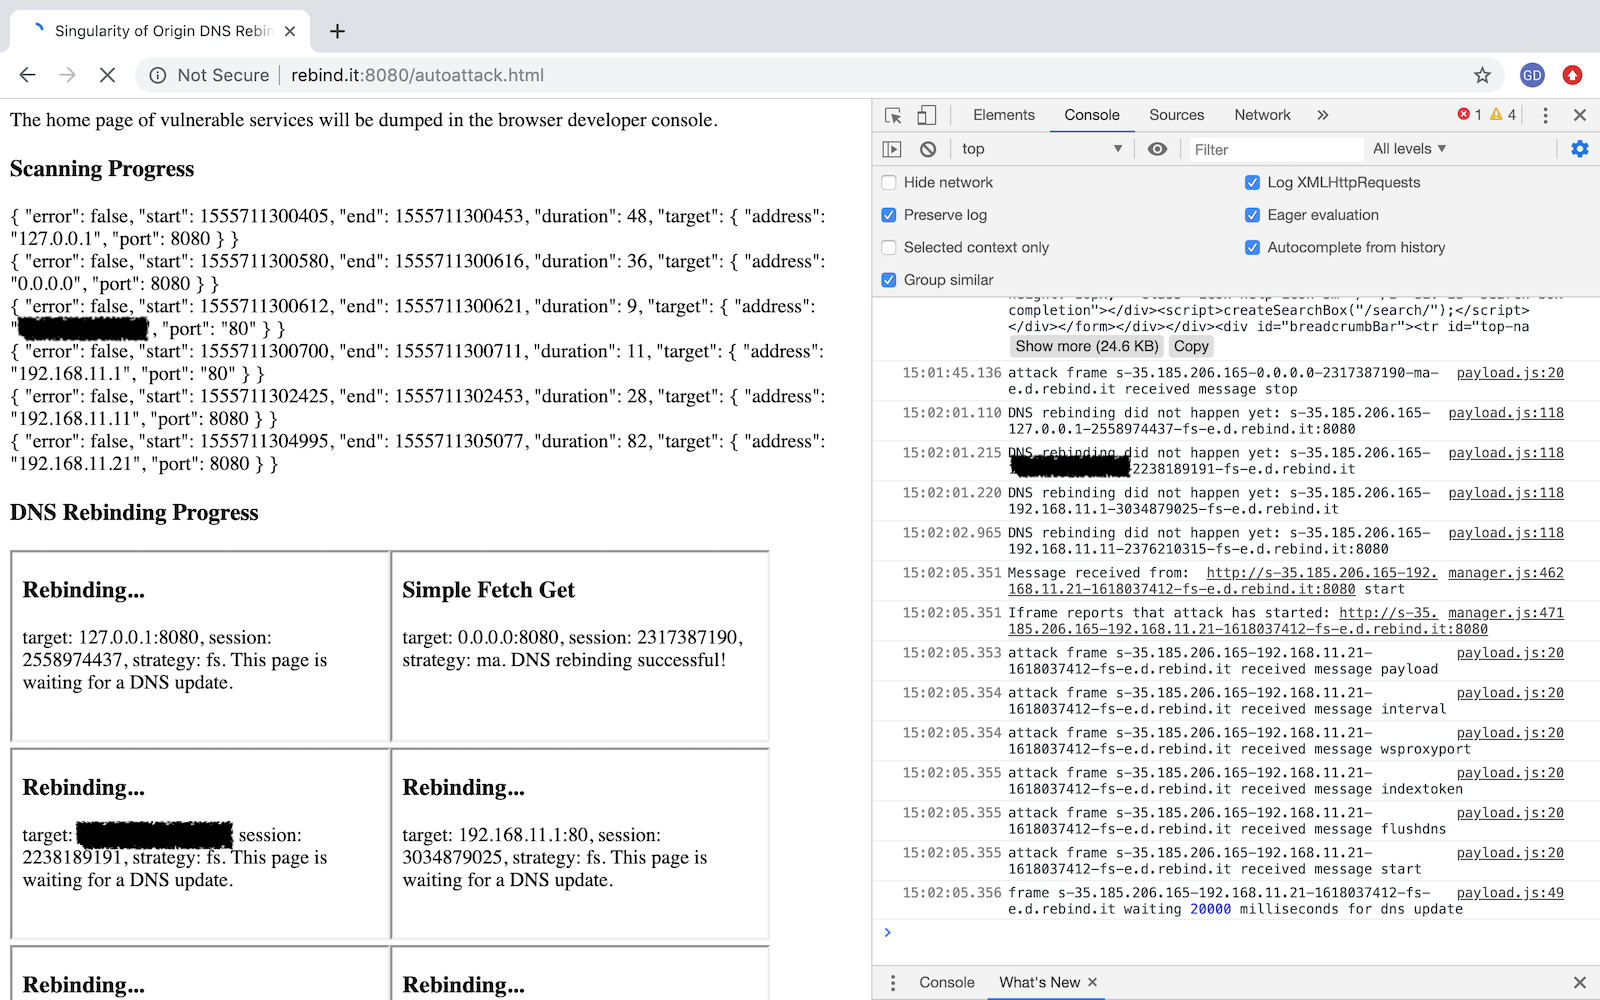 nccgroup/singularity
A DNS rebinding attack framework.
 skavngr/rapidscan
:new: The Multi-Tool Web Vulnerability Scanner.
 0xinfection/tidos-framework
The Offensive Manual Web Application Penetration Testing Framework.
 portswigger/param-miner
Burp Suite extension that discovers hidden, unlinked parameters using advanced diffing and binary search, enabling detection of web cache poisoning…
 t3l3machus/toxssin
An XSS exploitation command-line interface and payload generator.
 1n7erface/poclist
Vulnerability-specific PoC scripts for discovering and exploiting RCE, SQLi, XXE, SSRF, and unauthorized-access flaws in enterprise web apps and…
 wireghoul/htshells
Self contained htaccess shells and attacks
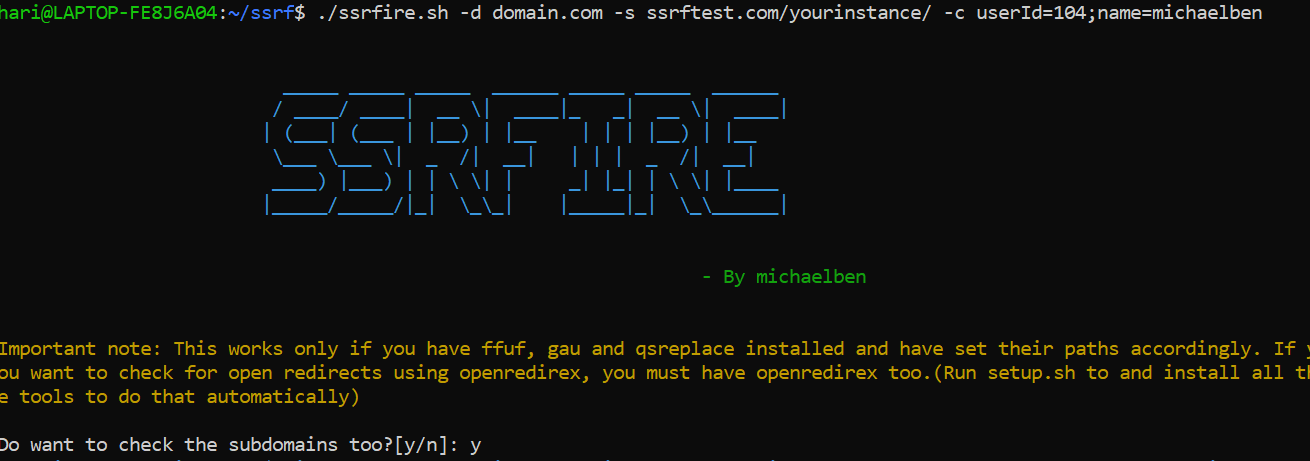 ksharinarayanan/ssrfire
An automated SSRF finder. Just give the domain name and your server and chill! ;) Also has options to find XSS and open redirects
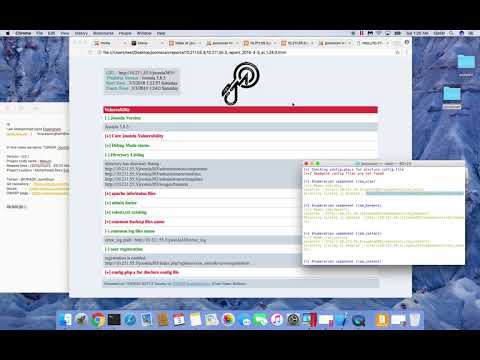 owasp/joomscan
Perl-based Joomla CMS vulnerability scanner automating version enumeration, component detection, exploit matching, firewall identification, and…
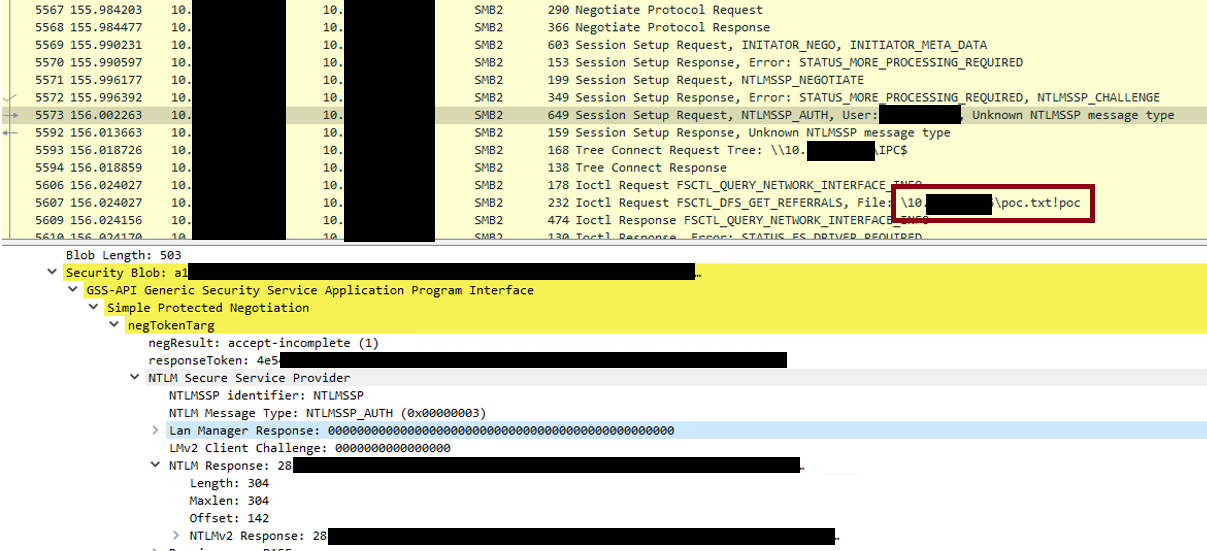 xaitax/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Microsoft-Outlook-Remote-Code-Execution-Vulnerability
 wireghoul/dotdotpwn
DotDotPwn - The Directory Traversal Fuzzer
 1n3/wordpress-xmlrpc-brute-force-exploit
Wordpress XMLRPC System Multicall Brute Force Exploit (0day) by 1N3 @ CrowdShield
 trustedsec/cve-2019-19781
This is a tool published for the Citrix ADC (NetScaler) vulnerability. We are only disclosing this due to others publishing the exploit code first.
 zigoo0/webpwn3r
WebPwn3r - Web Applications Security Scanner.