

CVE-2020-36708
 b1g-b33f/cve-2020-36708
Proof of concept for CVE-2020-36708
educationexploitationpenetration-testing+2
b1g-b33f/cve-2020-36708Proof of concept for CVE-2020-36708
 exdev994/cve-2026-49049
CVE-2026-49049 Helix3 (JoomShaper) Joomla Unauthenticated AJAX RCE Scanner
 r00t4dm/cve-2018-14667
about CVE-2018-14667 from RichFaces Framework 3.3.4
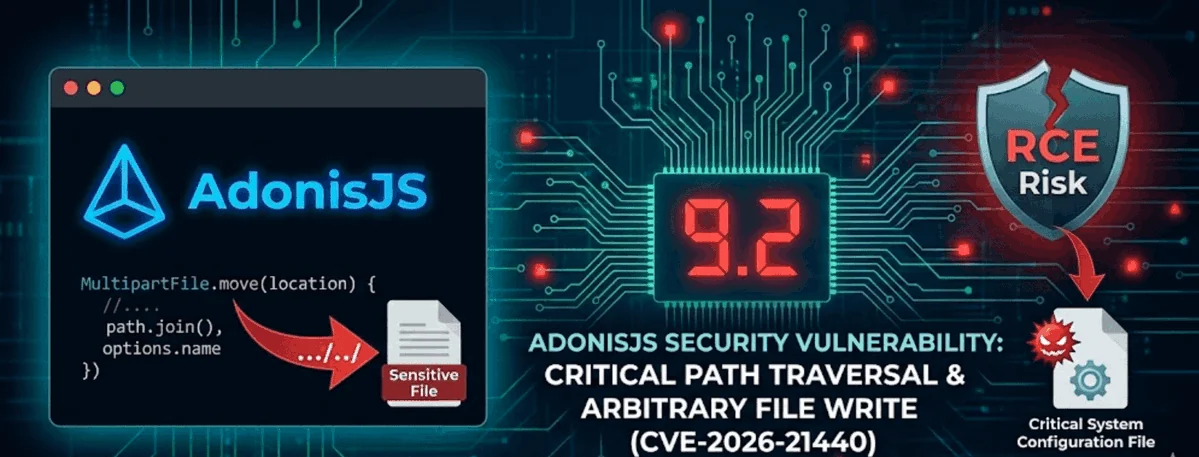 redpack-kr/ashwesker-cve-2026-21440
Proof-of-concept exploit for CVE-2026-21440, a critical path traversal in AdonisJS multipart uploads enabling arbitrary file write and remote code…
 sk4la/cve_2011_3556
Python 3 implementation of an existing CVE-2011-3556 proof of concept (PoC).
 yallasec/cve-2026-21627---tassos-novarain-framework-plg_system_nrframework-exploit---joomla
Python exploit for CVE-2026-21627, an unauthenticated arbitrary PHP file inclusion in Joomla's Novarain Framework, enabling file upload, delete, and…
 ethan-repo-lab4b6/cve-2022-36537
Python exploit for CVE-2022-36537, an authentication bypass in ZK Framework affecting R1Soft Server Backup Manager, allowing retrieval of web context…
 cr4zyd14m0nd137/lab-for-cve-2018-15133
Ejecución de exploit de deserialización con CVE-2017-5941
 n000xy/cve-2019-19609-poc-python
Strapi Framework, 3.0.0-beta.17.4
 redteamsecurity2023/cve-2022-26265
The first proof of concept of the Contao CMS RCE
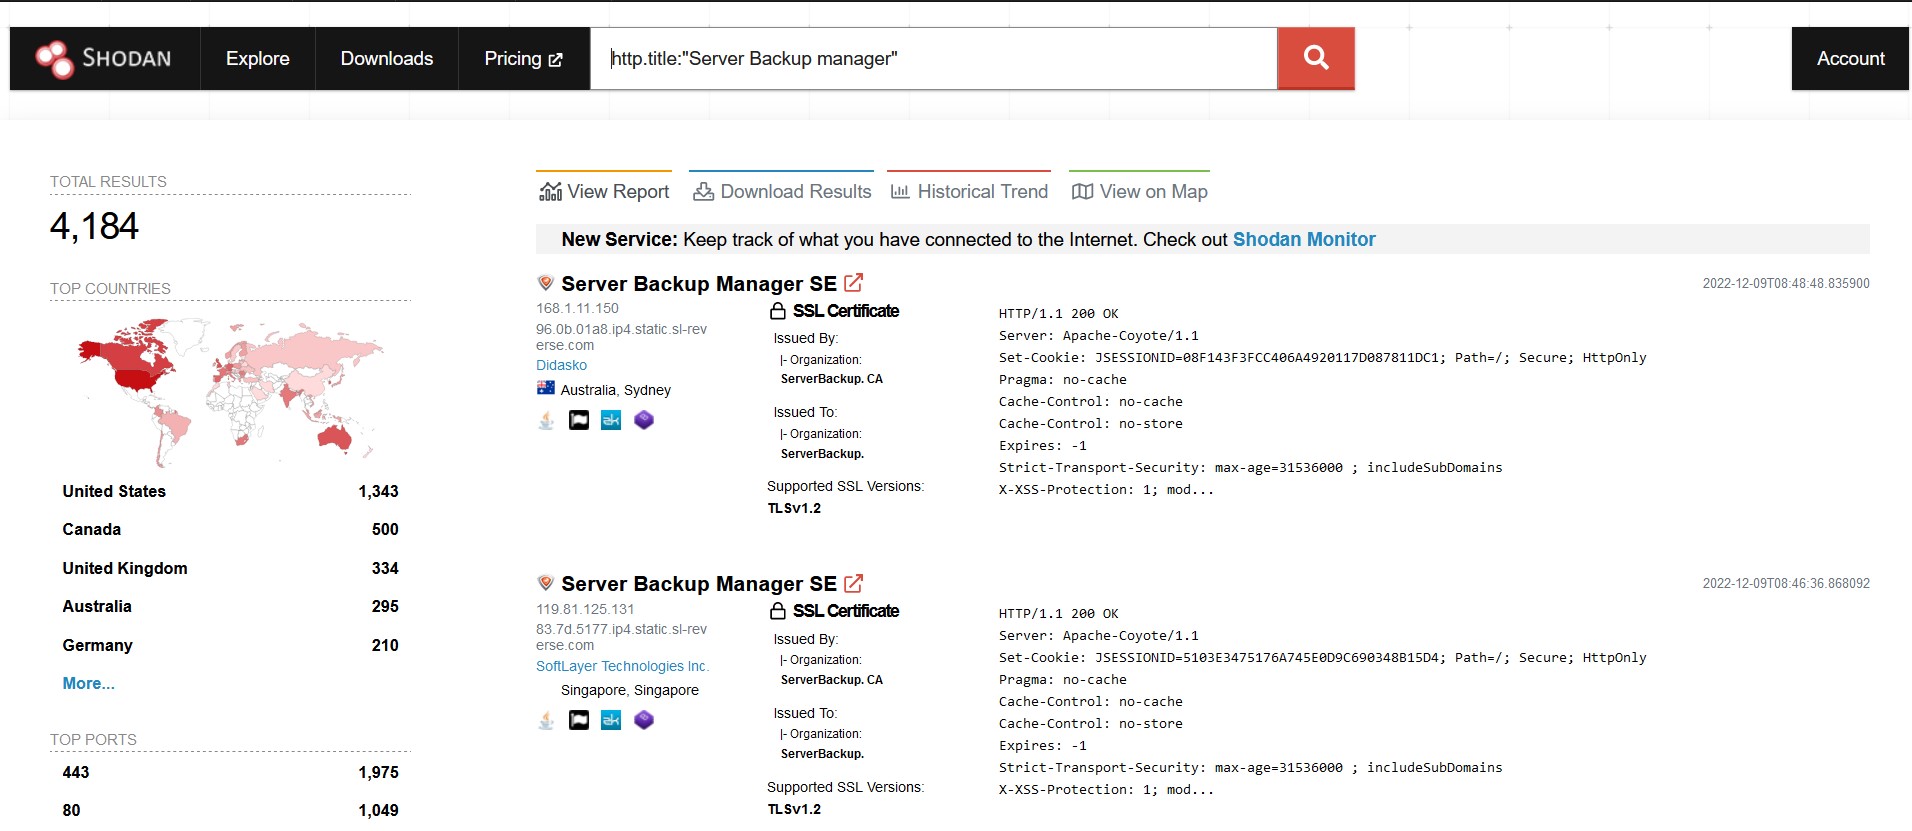 malwareman007/cve-2022-36537
POC of CVE-2022-36537
 sh4den/cve-2022-36804
A loader for bitbucket 2022 rce (cve-2022-36804)
 agnihackers/cve-2022-36537-exploit
CVE-2022-36537
 madexploits/phpunit-exploit
PHPunit Checker CVE-2017-9841 By MrMad
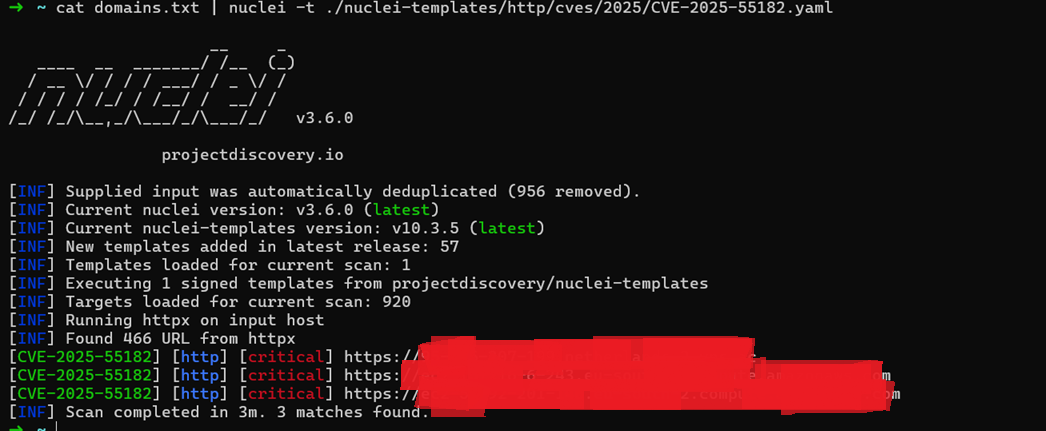 jaycelation/cve-2025-55182
PoC, Hunting React2Shell about CVE-2025-55182
 puneetbehl/grails3-cve-2022-27772
Proof-of-concept exploit for CVE-2022-27772 targeting Grails 3.3 framework's custom TomcatEmbeddedServletContainerFactory, demonstrating insecure…
 tankirat/cve-2017-5638
Educational analysis of Apache Struts 2 RCE vulnerability CVE-2017-5638, including exploit details, Equifax case study, and prevention measures.
 beefproject/beef
The Browser Exploitation Framework Project