CVE-2018-9995-DVR-Credentials-Extractor

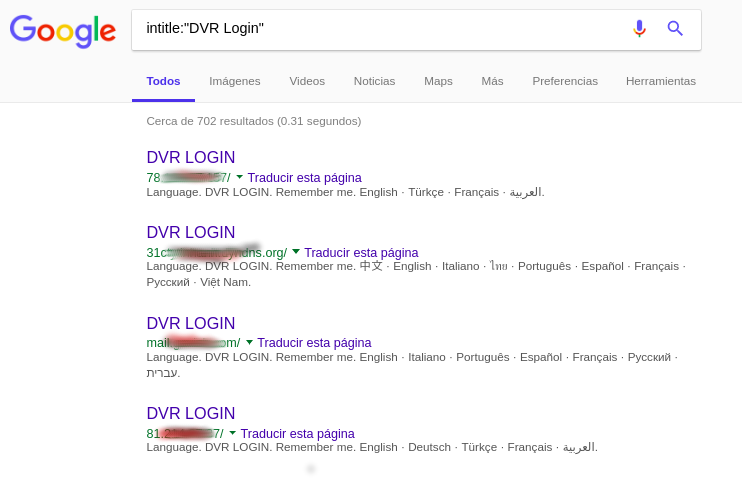
This project demonstrates the publicly disclosed CVE-2018-9995 vulnerability found in multiple embedded DVR devices.

This project demonstrates the publicly disclosed CVE-2018-9995 vulnerability found in multiple embedded DVR devices.

Python tool for analyzing CVE-2018-16763 in FUEL CMS with cleaner response parsing and interactive vulnerability checking.

We hope to reproduce CVE-2021-41773 to deepen our understanding of real-world cybersecurity vulnerabilities so that we can be knowledgeable about…

Go-based brute-force tool exploiting Bludit bruteforce mitigation bypass (CVE-2019-17240) for automated password cracking against admin login pages.

CVE-2022-39197 RCE POC

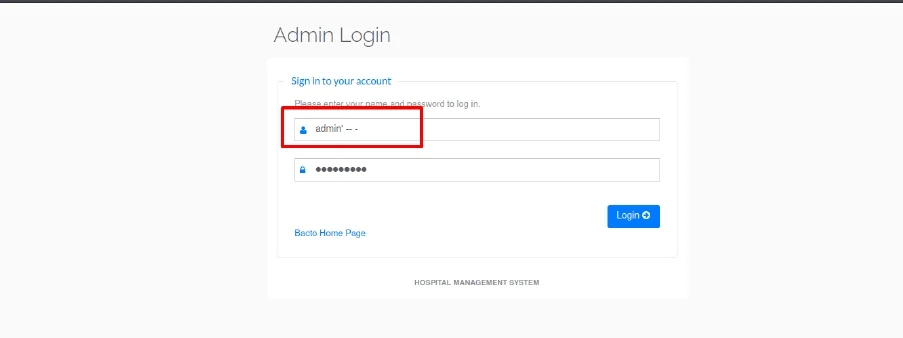
Intentionally vulnerable Hospital Management System demonstrating SQL injection (CVE-2023-7172) with Docker setup and PoC for educational security…

Apache Struts2 CVE-2017-5638 (Safe Educational Demo)

Proof of Concept (POC) for the CVE-2025-25296 vulnerability affecting Label Studio versions prior to 1.16.0

HTTP Request Smuggling

Proof-of-concept exploit for CVE-2024-38820, demonstrating locale-dependent case conversion bypass of Spring Framework DataBinder disallowedFields…

CVE-2024-4367

Buildpack providing a workaround for CVE-2021-44228 (Log4j RCE exploit)

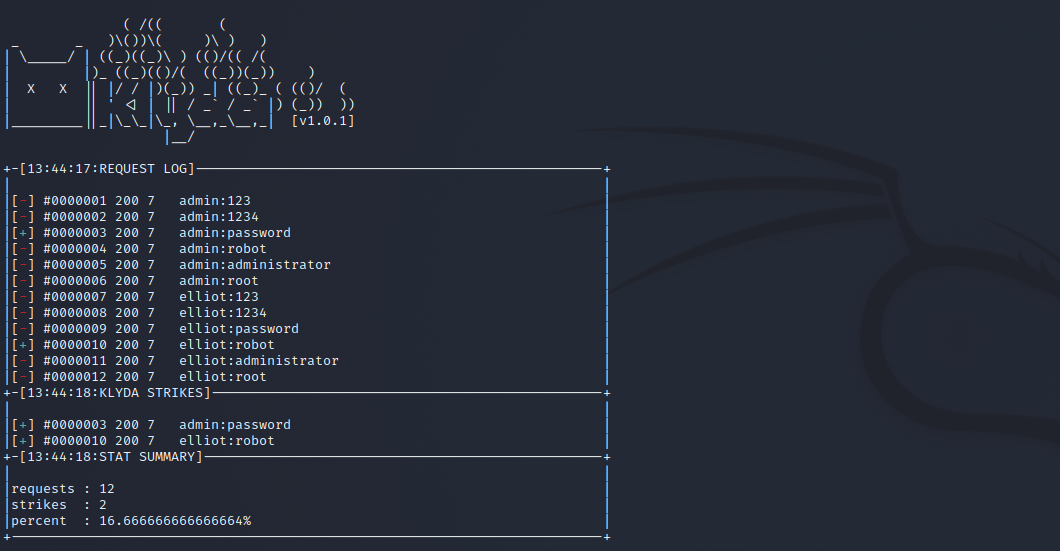
Highly configurable script for dictionary/spray attacks against online web applications.

CVE-2022-22978 POC Project

This project for CVE-2019-18935

Veno File Manager Project Veno File Manager Project 4.4.9 is vulnerable to Incorrect Access Control in admin-head-updates.php

Exploit for CVE-2021-43857 in Gerapy v0.9.7, providing a reverse shell via authenticated project creation and command injection.

This is a simple Shiro-basic project .Just for pentest env